Beef
Independent verification, backed by open-source code.


 Passed
audit and dataset.
- Live Bets Verified
- 6,450
- Parity Rate
- 100%
- Simulated Rounds
- 4M
- Proven RTP
- 99.2%
Verification pipeline
Real bets. Independently reproduced.
Placed anonymously at Duel.com. We rebuilt the game logic from scratch and matched all 6,450 recorded outcomes.
Positions 0–19 · Cashed out after the recorded step
The casino result, reproduced.
- Casino outcome
- 5 safe steps · Cashed out
- Our reproduction
- 5 safe steps · Cashed out
- Recorded payout
- $0.0512


- Seed Hash IntegrityPass
- Commitment LinkagePass
- Hash ConsistencyPass
- Nonce AuditPass
- Death-Point RecomputationPass
- Client Seed InfluencePass
- Payout MathPass
- Multiplier FormulaPass
- Win ConditionPass
- Phase C Bet-Size InvariancePass
- Config CompletenessPass
- House Edge AuditPass
- Phase LabelsPass
- Dataset HashPass
- Epoch SizePass
- Anti-CircularityPass
- Phase D Client-Seed VariationPass
- Simulation Pass 1Pass
- Cherry-Pick DetectionPass
- Multi-Step Multiplier ChainPass
- Phase E Death-Point RecomputePass
- Cash-Out Payout CorrectnessPass


The repo is the credential. You don't have to trust us — every finding ships as code. Run npm test to re-run the full audit: 22 verification steps, 4M simulated rounds, 6,450 live bets re-verified.

This audit independently validates the Beef game operated by Duel.com across five domains: deterministic outcome generation, entropy integrity, live-to-verifier parity, RTP mathematical accuracy, and fairness integrity testing. We placed 6,450 real bets across 139 seed entries and independently verified every single outcome using our own implementation of the algorithm.

Audit Verdict
| Check | Result | Evidence |
|---|---|---|
| Overall Status | Pass | |
| RTP Verified | Pass | 99.2% proven · 99.1468% simulated (4M) · flat 0.8% house edge across all 4 difficulty levels |
| Live ↔︎ Verifier Parity | Pass | 100% — 6,450 / 6,450 bets matched |
| Commit-Reveal System | Pass | SHA-256 verified, 139 seed entries — commitment intact across all rotations |
| Client Seed | Pass | Browser-generated + player customizable — server commits before client seed is known |
| RNG Analysis | Pass | HMAC-SHA256 backward Fisher-Yates on a 20-tile grid — bias-free rejection sampling, no hidden inputs |
| Payout Logic | Pass | All 6,450 payouts verified — single-step and multi-step cash-out chains, exact to 8 decimal places |
| Anti-Circularity | Pass | Algebraic identity: winChance × payoutMult = 0.992 for all 4 difficulty levels — proven from first principles |
| Fairness Integrity | Pass | 16 fairness integrity tests — all 16 pass (includes one Beef-specific multi-step state test) |
| Determinism | Pass | Full reproducibility confirmed |
Overall StatusPass
RTP VerifiedPass
Live ↔︎ Verifier ParityPass
Commit-Reveal SystemPass
Client SeedPass
RNG AnalysisPass
Payout LogicPass
Anti-CircularityPass
Fairness IntegrityPass
DeterminismPass

What Was Audited
✓ Audited
- The RNG algorithm is deterministic and verifiable
- Server seeds are cryptographically committed via SHA-256 before play
- Client seed is browser-generated and players can customize it
- Nonces increment correctly and are never reused within a seed pair
- Death-point positions are computed via HMAC-SHA256 backward Fisher-Yates with bias-free rejection sampling
- Outcomes are reproducible from server seed, client seed, and nonce
- Single-step and multi-step cash-out payouts match the hypergeometric formula C(20,k) / C(20−m,k) × 0.992 across all 4 difficulty levels
- The death-point set is fixed at round start and unchanged by step sequence or cash-out timing
- Theoretical RTP is 99.2% across all 4 difficulty levels (flat 0.8% house edge)
- Bet amount does not influence death-point placement or outcome
- Players can independently verify every bet

What Audit Excludes
- Infrastructure or server security
- Wallet, payments, or operational systems outside game logic
- Rakeback layer — 99.2% is the certified RTP; rakeback is operator-side
- Cross-account sampling
- Max win cap enforcement — not embedded in game logic
What Audit Covers

| Area | Description |
|---|---|
| Commit-Reveal System | SHA-256 server seed hashing, pre-bet commitment, reveal on rotation |
| Client Seed Origin | Player-controlled seed, browser-generated — server commits before your seed is known |
| Seed Handling | Client seed control, nonce lifecycle, seed pair rotation |
| RNG Analysis | HMAC-SHA256 backward Fisher-Yates verification, rejection sampling, bias analysis |
| Payout Logic | Hypergeometric multiplier formula, single-step and multi-step cash-out chains, bet-size invariance (Phase C), multiplier chain integrity across k=2, 3, 5 cash-outs |
| Live Parity | Independent death-point recomputation vs live game results across all capture phases |
| RTP Validation | Anti-circularity proof, simulated RTP (4M rounds), cherry-pick detection (Pass 2) |
| Fairness Integrity | Standard integrity matrix — tests across commit-reveal, determinism, payout, isolation, and parameter enforcement |
What Audit Guarantees

- Outcomes are deterministic and reproducible from the recorded inputs
- Live game results match independent recomputation for the verified sample (6,450 / 6,450)
- Death-point positions follow the uniform distribution expected from the backward Fisher-Yates shuffle across all 4 difficulty levels
- RTP is proven analytically: winChance × payoutMult = 0.992 for all 4 difficulty levels by combinatorial cancellation (max algebraic deviation 2.22e-16)
- Simulated RTP of 99.1468% across 4 million rounds (1M per difficulty) — matches the theoretical 99.2% within expected variance
- The death-point set is fixed at round start and independent of which tile the player steps on
- Client seed is a genuine, browser-generated input that materially influences results
- The house edge is a flat 0.8% across all 4 difficulty levels — no scaling edge
- Multi-step cash-out payouts at k=2, 3, and 5 match the hypergeometric formula exactly (202 winning multi-step bets verified, 0 errors)
- All 16 fairness integrity tests passed at audit time, including the Beef-specific multi-step state integrity test
References
Beef — Game Rules6 sections▶

Beef is a step-by-step survival game (commonly called Cross the Road). You choose a difficulty level — EASY, MEDIUM, HARD, or EXPERT — which sets how many hidden death points lie on the path ahead (1, 3, 5, or 10 respectively). Each safe step grows your multiplier; step on a death point and the round ends. You can cash out after any safe step. You'll only ever *see* one death point — the one that ends your round — but the others were always there, hidden along the path. That's why higher difficulty is harder: more hidden death points means a bigger chance any given step lands on one, even though you only ever see one of them.
How to Play
1. Choose difficulty — Select EASY (1 death point), MEDIUM (3), HARD (5), or EXPERT (10). More death points means higher reward per safe step but a higher chance of hitting one.
2. Enter bet amount — Choose how much to wager.
3. Step onto tiles — Click tiles one at a time. Each safe step grows the running multiplier.
4. Cash out or continue — After any safe step, choose to cash out at the current multiplier or push on for more.
5. Outcome — If you step onto a death point, the round ends and the bet is lost. If you cash out, payout = bet × multiplier at the current step count.
Win Conditions
The win condition in Beef depends on whether every stepped tile avoided the death-point set.
| Outcome | Condition | Example (difficulty=MEDIUM, k=3) |
|---|---|---|
| Safe step | Stepped tile is not in death-point set | Multiplier grows; player may cash out or continue |
| Cash out | Player stops after k safe steps | k=3 → payout × 1.6631× |
| Loss | Stepped tile is in death-point set | Round ends, bet is lost |
Risk vs Reward
The core mechanic of Beef is the tradeoff between difficulty level and safe-step risk.
- Difficulty controls risk per step — more death points means fewer safe tiles, higher multiplier growth per step, and a higher chance the next step ends the round
- Step count controls total multiplier — each additional safe step multiplies your running payout by the ratio
(20−k) / (20−m−k) - RTP is constant — all 4 difficulty levels have the same theoretical RTP (99.2%) regardless of how many steps you take
Parameters
| Parameter | Value | Notes |
|---|---|---|
| Grid Size | 20 tiles | Fixed; all difficulty levels use this layout |
| Difficulty Levels | 4 (EASY, MEDIUM, HARD, EXPERT) | Player-selected; sets death-point count |
| Death Points by Difficulty | EASY=1, MEDIUM=3, HARD=5, EXPERT=10 | Determines risk and multiplier curve |
| House Edge | 0.8% flat | No scaling — same edge for all difficulty levels and all bet sizes |
| Theoretical RTP | 99.2% | Verified across all 4 difficulty levels |
| RNG Algorithm | HMAC-SHA256 | Backward Fisher-Yates with bias-free rejection sampling; key = hex-decoded server seed |
Seed Formats
Every Beef bet uses three cryptographic inputs to generate the death-point layout.
| Seed Type | Format | Example | Purpose |
|---|---|---|---|
| Server Seed | 64-char hex (32 bytes) | fcf0584a… | Casino-provided randomness |
| Client Seed | Alphanumeric string | 8AgNlaGR1fxeiy93 | Player-contributed entropy |
| Nonce | Integer ≥ 0 | 0 | Per-round counter within the active seed pair |
serverSeedHashed (SHA-256 of the raw hex bytes) before play and revealed only on seed rotation. The HMAC key is the hex-decoded bytes of the server seed, not its UTF-8 text.Multiplier & Payout
The payout multiplier after k safe steps with m death points on a 20-tile grid is the combinatorial ratio of unrevealed configurations multiplied by the house-edge factor.
multiplier(k, m) = C(20, k) / C(20−m, k) × 0.992| Steps (k) | Death Points (m) | Raw multiplier | With 0.8% edge |
|---|---|---|---|
| 1 | 1 | 1.0526× | 1.0442× |
| 1 | 3 | 1.1765× | 1.1671× |
| 1 | 5 | 1.3333× | 1.3227× |
| 1 | 10 | 2.0000× | 1.9840× |
| 5 | 3 | 2.5055× | 2.4855× |
| 10 | 3 | 9.5000× | 9.4240× |
| 5 | 5 | 5.1628× | 5.1215× |
multiplier as the raw combinatorial ratio C(20,k)/C(20−m,k) without the edge applied, and no_house_edge_multiplier as the actual payout multiplier with the 0.992 edge factor applied. Payout is computed as amount_won = amount × no_house_edge_multiplier. The naming is counter-intuitive — the field labelled no_house_edge_multiplier is the one that includes the house edge. We verify against the correct field throughout. Duel's /api/v2/cross-road/config endpoint also publishes a pre-computed payout_tables lookup (61 entries across the 4 difficulties); every entry matches the closed-form hypergeometric formula exactly (max observed deviation 4.55 × 10⁻¹³).Why Provably Fair Matters▶

Traditional online casinos ask you to trust them. Provably fair cryptography replaces that trust with independently verifiable proof. Every bet you place can be reconstructed from three public inputs — the server seed, your client seed, and the nonce — and the result you see should match the result anyone else can compute from those inputs.
- No outcome manipulation — the server seed is committed (SHA-256 hashed) and published before you play. The casino cannot change the outcome based on your bet size or history without breaking the commitment.
- Your seed matters — the client seed is controlled by your browser, not the casino. Changing it produces a different outcome for the same server seed and nonce, which proves your input is genuinely part of the computation.
- Verifiable by anyone — once the server seed is revealed on rotation, anyone with the seed triple can recompute the result with a few lines of code. The casino has no way to hide a tampered outcome.
- Mathematically bounded — the published multiplier formula determines payouts. We prove from first principles that win-chance × payout-multiplier equals 99.2% for every configuration, so the house edge cannot be inflated silently.
High-Level Overview7 sections▶

This section walks through how a Beef bet moves through the system end-to-end — from the server seed commitment, through the bet and step flow, to the post-rotation verification step that closes the loop.
Checklist Reference
Commit-Reveal
| Check | What it proves |
|---|---|
| Server seed committed before play | Casino cannot change outcome post-bet |
| SHA-256 of revealed seed matches committed hash | Revealed seed is the one that was actually committed |
| Hash identical across all bets in an epoch | All bets within a seed pair share the same commitment |
Seed System
| Check | What it proves |
|---|---|
| Nonces are sequential within an epoch | No nonce skipping or reuse |
| Single client seed per epoch | Client seed cannot be silently rotated mid-epoch |
| Next-seed pre-committed before rotation | Future commitment chain is locked in before reveal |
RNG & Parity
| Check | What it proves |
|---|---|
| Death-point positions recompute from seeds + nonce | Outcome is deterministic and verifiable |
| Independent verifier matches live API for every bet | No hidden inputs to the RNG |
| Death-point set invariant across step sequence | Layout fixed at round start, not rewritten per step |
Payout & RTP
| Check | What it proves |
|---|---|
| Multiplier matches C(20,k)/C(20−m,k) × 0.992 | Payout formula matches published rules |
| amount_won = amount × no_house_edge_multiplier | Payout arithmetic is exact to 1e-8 |
| winChance × payoutMult = 0.992 for all m | RTP is fixed at 99.2% by construction, not observation |
Integrity
| Check | What it proves |
|---|---|
| Wrong client seed produces different death points | Client seed genuinely influences outcome |
| Bet size does not influence outcome | Phase C $10 bets match Phase A/B $0.01 bets |
| No cherry-picking in seed selection (Pass 2) | Casino is not curating favourable seeds |
High-Level Flow
A Beef round runs through five stages — from the casino committing to a server seed before you play, through the bet and steps, to the post-rotation verification that anyone can run.
1. Commit — Server generates server seed, publishes SHA-256 hash as `serverSeedHashed`. Player sees only the hash.
2. Seed pair activated — Client seed is browser-generated (or player-set). Nonce starts at 0. Next server seed is pre-committed.
3. Bet — Player selects difficulty and bet amount. Platform computes death-point positions via HMAC-SHA256 backward Fisher-Yates using the active seed pair + nonce.
4. Steps — Player steps onto tiles one at a time. Multiplier grows per safe step. Player may cash out at any point.
5. Rotate — On client-seed change or manual rotation, the active server seed is revealed. The next-committed seed becomes active.
6. Verify — Anyone with serverSeed, clientSeed, nonce, and difficulty level can recompute the exact death-point set.
Provably Fair Model
Beef is a commit-reveal provably fair game. The casino commits to a server seed by publishing its SHA-256 hash before any bet is placed. Once play on that seed is complete and the seed is rotated, the casino reveals the raw server seed. Anyone can then verify two things: (1) that the revealed seed hashes to the previously-published commitment, and (2) that the death-point positions for every bet in that epoch recompute correctly from the seed triple. The model does not require trust in the casino — only that SHA-256 and HMAC-SHA256 are cryptographically sound, which is a well-established assumption.
Commit-Reveal Model
Beef uses a four-phase commit-reveal cycle. Each phase has a single, well-defined purpose, and every phase produces artefacts that can be verified after the fact.
Commit phase
Server generates a 32-byte random server seed, computes `SHA-256(hex_bytes(serverSeed))`, and publishes the hash as `serverSeedHashed`. The raw seed is kept secret. A next-seed hash is also pre-committed.
Bet phase
Player places bets against the active seed pair. For each bet, death-point positions are computed via `HMAC-SHA256(key=hex_bytes(serverSeed), msg=clientSeed:nonce:cursor)` followed by backward Fisher-Yates on the 20-tile grid. Nonce increments per bet.
Reveal phase
Player (or system) rotates the seed pair — typically by changing the client seed. The previously-active server seed is now revealed in the API. The pre-committed next-seed hash becomes the active `serverSeedHashed`.
Verify phase
Anyone with the seed triple can run HMAC-SHA256 + Fisher-Yates independently and confirm that death-point positions match the values returned by the live API. The commitment chain is preserved: revealed hash = prior commitment.
Player-Controlled Client Seed
The client seed is the player's lever into the RNG. It is generated in the browser (not the server) and can be replaced at any time, which forces a seed rotation.
- Browser-generated — a fresh 16-character alphanumeric string is produced client-side on first load
- Player-editable — the player can overwrite it with any value they choose; changing the client seed triggers a seed rotation and reveals the active server seed
- Materially influences outcome — we verified that changing
clientSeedto a random alternative produces different death-point positions in 597 / 601 tests (99.3%); the remaining 4 collisions are expected at low death-point counts where the sample space is small - Not known to the server at commit time — the server publishes
serverSeedHashedbefore your client seed is known, so it cannot cherry-pick a commitment that favours the casino against your specific seed
Nonce Lifecycle
The nonce is a per-round counter within the active seed pair. It starts at 0, increments by 1 per bet, and resets only on seed rotation. The nonce is reused across all steps in a single round — the death-point set is computed once, at bet time, and is unchanged by subsequent steps.
- Starts at 0 on every new seed pair
- Increments sequentially — no skipping, no reuse within an epoch
- Resets on rotation — every rotation produces a fresh nonce=0 sequence
- Shared across steps — all steps in a round use the same nonce; the death-point set is fixed at
noncetime
// Per seed pair, nonce sequence:// bet 1 → nonce=0// bet 2 → nonce=1// bet 3 → nonce=2// ...// On client seed change:// serverSeed revealed, new pair activated, nonce resets to 0Determinism Guarantee
Given serverSeed, clientSeed, nonce, and deathPointsCount (set by difficulty level), the death-point set is fully determined — there is no randomness, no hidden input, and no dependence on bet amount, timestamp, or any other variable. The pipeline is:
// Inputs: serverSeed (hex), clientSeed (string), nonce (int), deathPointsCount (1, 3, 5, or 10) key = Buffer.from(serverSeed, 'hex') // hex-decoded bytes, NOT utf-8grid = [0, 1, 2, ..., 19]cursor = 0 for i from 19 down to 1: range = i + 1 maxFair = 0xFFFFFFFF - (0xFFFFFFFF % range) loop: hash = HMAC-SHA256(key, `${clientSeed}:${nonce}:${cursor}`) scan 4-byte chunks of hash: if chunk < maxFair: j = chunk % range swap grid[i] ↔ grid[j] break out of loop cursor++ // only if no chunk passed rejection death_points = grid[0 .. deathPointsCount-1] // sorted ascendingTechnical Glossary7 categories▶

Terms and definitions used throughout this audit report, grouped by category.
Core Concepts
| Term | Definition |
|---|---|
| Provably Fair | A system where every game outcome can be independently verified from public cryptographic inputs, without trusting the operator. |
| Commit-Reveal | A two-phase protocol where a party publishes a hash of a secret before play (commit), then reveals the secret afterward (reveal). The hash proves the secret was fixed in advance. |
| Determinism | A property where the same inputs always produce the same output. Beef is deterministic: (serverSeed, clientSeed, nonce, deathPointsCount) uniquely determines the death-point set. |
| Epoch | The set of bets placed under a single active seed pair, from activation to rotation. Also called a seed pair lifecycle. |
Seed System
| Term | Definition |
|---|---|
| Server Seed | A 32-byte random value generated by the casino. Represented as a 64-character hex string. Used as the HMAC key (hex-decoded). |
| Server Seed Hashed | SHA-256(hex_bytes(serverSeed)). The commitment published before play. |
| Client Seed | A player-controlled alphanumeric string, browser-generated by default. Part of the HMAC message. |
| Nonce | A per-round counter within the active seed pair. Starts at 0, increments per bet, shared across all steps in a single round, resets on seed rotation. |
| Cursor | A rejection-sampling retry counter appended to the HMAC message. Increments only when every 4-byte chunk of the previous hash exceeded the fairness threshold. |
| Seed Pair | The combination of one server seed and one client seed. A seed pair defines an epoch. |
| Next Server Seed Hash | A pre-commitment to the server seed that will become active after the current one is rotated. Locks the future chain in advance. |
| Phase-Boundary Marker | A seed-rotation entry that carries a valid commitment but no bets. Created by the capture script forcing a clean seed rotation at each phase transition. The 139-entry seed set contains 8 such markers (4 in the primary dataset, 4 in Phase E); the remaining 131 entries are bet-bearing epochs. |
Cryptographic Functions
| Term | Definition |
|---|---|
| SHA-256 | A 256-bit cryptographic hash function. Used here for server seed commitment: SHA-256(hex_bytes(serverSeed)) = serverSeedHashed. |
| HMAC-SHA256 | Hash-based message authentication code built on SHA-256. Takes a key and a message, returns a 256-bit (64-hex-char) digest. Used here for death-point position generation. |
| HMAC-SHA256 Backward Fisher-Yates | The full RNG pipeline: HMAC-SHA256 produces the 4-byte random chunks; backward Fisher-Yates uses those chunks to shuffle the 20-tile grid. Beef-specific implementation. |
| Rejection Sampling | A technique for bias-free uniform sampling. A 4-byte chunk is accepted only if it falls below maxFair = 0xFFFFFFFF − (0xFFFFFFFF mod range). Guarantees every position in range is equally likely. |
Verification Terms
| Term | Definition |
|---|---|
| Parity | Agreement between the live game's reported outcome and an independent recomputation from the same inputs. 100% parity means zero mismatches. |
| Recomputation | Running the audit's standalone RNG implementation on captured seed triples and comparing the output to the live API response. |
| Anti-Circularity Proof | A proof that RTP is not an empirical observation but a mathematical identity — winChance × payoutMult = 0.992 by algebraic cancellation, independent of any simulation. |
| Hypergeometric Distribution | The probability distribution describing sampling without replacement. For Beef, the survival probability after k safe steps with m death points on a 20-tile grid is C(20−m, k) / C(20, k) — the ratio of safe-tile combinations to total combinations. Combining with the multiplier C(20, k) / C(20−m, k) × 0.992 yields the fixed RTP identity. |
| Cherry-Pick Detection (Pass 2) | A statistical test over revealed casino seeds that checks whether early-epoch win rates systematically exceed later-epoch win rates — the signature of seed pre-selection. |
Game Mechanics
| Term | Definition |
|---|---|
| Grid Size | The total number of tiles on the Beef board. Fixed at 20 for all difficulty levels. |
| Difficulty Level | One of four settings (EASY, MEDIUM, HARD, EXPERT) that determines how many of the 20 tiles are death points (1, 3, 5, 10 respectively). |
| Death Point | A tile position that ends the round on contact. Placed by the Fisher-Yates shuffle; count determined by difficulty level. |
| Step | The act of clicking a tile. A safe step grows the multiplier; a death-point step ends the round. |
| Multiplier Chain | The sequence of running multipliers as a player steps through tiles: m₁, m₂, ..., mₖ. Each step satisfies mₖ = C(20,k) / C(20−m,k) × 0.992. |
| Cash-Out | Stopping after k safe steps and collecting amount × mₖ. Only available after at least one safe step. |
| Death-Point Set Invariance | The property that the death-point set is fixed at round start and does not change based on which tiles the player steps on, or in what order. |
Audit Terms
| Term | Definition |
|---|---|
| Fairness Integrity (FI) Matrix | The standard test matrix applied to every audit, covering commit-reveal, determinism, payout, isolation, and parameter enforcement. Documented in S5. |
| Chi-Squared Test | A goodness-of-fit test comparing observed distributions (e.g., death-point positions, win counts) to theoretical expectations. Used with Bonferroni correction where multiple configurations are tested. |
| Bonferroni Correction | A multiple-comparison adjustment: when testing N hypotheses at significance α, the per-test threshold is α/N. Prevents false positives from mass testing. |
| Point-in-Time Audit | An audit verdict that applies to the code and configuration in force at the audit date. Subsequent changes are outside scope unless re-certified. |
Data Formats
| Term | Definition |
|---|---|
| beef-master-6000bets.json | Primary capture dataset. 6,000 rounds across Phases A–D: baseline difficulty coverage, high-variance EXPERT sampling, $10 bet-size invariance, and custom client seed variation. All single-step (k=1) outcomes. SHA-256 pinned in S1. |
| beef-phaseE-450bets.json | Multi-step cash-out capture dataset. 450 rounds across 4 sub-phases (E1–E4) covering k=2, 3, 5 cash-outs on all 4 difficulty levels. SHA-256 pinned in S1. |
| verification-results.json | Output of the 22-step verification pipeline. Contains per-step pass/fail status and per-step detail strings. |
| simulation-results.json | Output of the 4-configuration × 1M-round simulation. Contains Pass 1 (fresh seeds, RTP + chi²) and Pass 2 (casino seeds, cherry-pick detection). |
Seed, Nonce & Determinism
Can the casino change your outcome after you bet?
Every Beef round on Duel.com is generated from three inputs: server seed, client seed, and nonce. The casino commits to its server seed by publishing a SHA-256 hash before you place any bets. After you rotate your seed, the server reveals the actual seed — and anyone can verify that the hash matches. This cryptographic commitment makes it impossible for the casino to secretly change your outcome after you bet.

Commit-Reveal Cryptographic Guarantee
What we verified
- Casino commits to the server seed hash before any bet is placed
- Client seed is browser-generated — server cannot know it at commitment time (Full Pass origin)
- Players can set or change their client seed at any time via the rotation UI
- Nonce increments by 1 per bet with no gaps or duplicates across 131 bet-bearing epochs
- Death-point positions are fully determined by the seed inputs before any tile is stepped on
- Identical inputs always produce the same death-point set — confirmed across all 6,450 bets
- Your client seed is a genuine input — changing it changes the death-point layout
What this means for you
- The casino cannot change where the death points are after you bet
- You contribute randomness the server cannot predict or pre-select against
- Every bet is unique — the nonce ensures no two bets share an outcome
- Any result can be independently verified using the public tools and repo
- Outcomes are tamper-proof and verifiable even months later
- Cherry-picking favourable seeds is structurally impossible


- Casino commits to the server seed hash before any bet is placed
- Client seed is browser-generated — server cannot know it at commitment time (Full Pass origin)
- Players can set or change their client seed at any time via the rotation UI
- Nonce increments by 1 per bet with no gaps or duplicates across 131 bet-bearing epochs
- Death-point positions are fully determined by the seed inputs before any tile is stepped on
- Identical inputs always produce the same death-point set — confirmed across all 6,450 bets
- Your client seed is a genuine input — changing it changes the death-point layout
- The casino cannot change where the death points are after you bet
- You contribute randomness the server cannot predict or pre-select against
- Every bet is unique — the nonce ensures no two bets share an outcome
- Any result can be independently verified using the public tools and repo
- Outcomes are tamper-proof and verifiable even months later
- Cherry-picking favourable seeds is structurally impossible
Server seed committed before betPass
Client seed originPass
Client seed controlPass
Nonce sequencingPass
Hash consistency within epochPass
Seed hash integrityPass
Deterministic outputPass
Client seed participationPass
All 131 revealed seeds hash-verified (121 primary + 10 Phase E). Every seed rotation was verified — the next seed the casino pre-committed always matched what was actually used. Outcomes are fully deterministic — the same server seed, client seed, and nonce always produce the same death-point layout. The casino cannot change your result after you bet.
| Check | Result | Evidence |
|---|---|---|
| Server seed committed before bet | Pass | SHA-256 hash of server seed published before play — casino cannot change death-point layout after betting |
| Client seed origin | Pass | Browser-generated (Full Pass) — server commits before client seed is known |
| Client seed control | Pass | Player can set/change client seed via rotation UI at any time |
| Nonce sequencing | Pass | Sequential within each epoch, 0 gaps, 0 duplicates across 131 epochs |
| Hash consistency within epoch | Pass | serverSeedHashed constant across all bets within each of 131 epochs |
| Seed hash integrity | Pass | 131 / 131 revealed seeds hash-verified — commitment chain intact |
| Deterministic output | Pass | Same (serverSeed, clientSeed, nonce, difficultyLevel) always produces same death-point SET — 6,450 / 6,450 confirmed |
| Client seed participation | Pass | Client seed is a genuine input — changing it changes the death-point positions |
Server seed committed before betPass
Client seed originPass
Client seed controlPass
Nonce sequencingPass
Hash consistency within epochPass
Seed hash integrityPass
Deterministic outputPass
Client seed participationPass
All 131 revealed seeds hash-verified (121 primary + 10 Phase E). Every seed rotation was verified — the next seed the casino pre-committed always matched what was actually used. Outcomes are fully deterministic — the same server seed, client seed, and nonce always produce the same death-point layout. The casino cannot change your result after you bet.
How It Works — Seed, Nonce & Determinism7 sections
1.1Server Seed Commitment
Before any bet is placed, the casino generates a secret server seed and publicly commits to it by displaying its SHA-256 hash. The server seed is a 64-character hex string (32 bytes), and the commitment hash is computed as SHA-256(hexDecode(serverSeed)). This cryptographic commitment locks the server's randomness before the player acts. After the epoch ends, the actual server seed is revealed — and anyone can verify that the hash matches.
export function verifyHash(serverSeed: string, serverSeedHashed: string): boolean { const seedBytes = Buffer.from(serverSeed, 'hex'); const computed = crypto.createHash('sha256').update(seedBytes).digest('hex'); return computed === serverSeedHashed;}Real Example from Live Data:
// Seed block captured at bet time (round 7722773, Phase A, MEDIUM, nonce=1){ "serverSeedHashed": "b86763e0dc0f362d83e9bf1e6466f9be05434a502b7ea5fd1f96c2873b2bbcfe", "clientSeed": "8AgNlaGR1fxeiy93", "nonce": 1} // After seed rotation, the plaintext was revealed as:// serverSeed = "fcf0584ae26b61deecc138adfc788ef039d69814c172a7d71667b5c9cdc661fb"//// SHA-256 of the revealed seed equals the committed hash above — verified below.Verification:
const crypto = require('crypto'); const serverSeed = "fcf0584ae26b61deecc138adfc788ef039d69814c172a7d71667b5c9cdc661fb"; const hashedServerSeed = crypto .createHash("sha256") .update(Buffer.from(serverSeed, 'hex')) .digest("hex"); console.log(hashedServerSeed);// Output: b86763e0dc0f362d83e9bf1e6466f9be05434a502b7ea5fd1f96c2873b2bbcfe ✅1.2Commitment Linkage (Next-Seed Promotion)
At every seed rotation, the nextServerSeedHash pre-committed before rotation must match the serverSeedHashed that becomes active after rotation. This chain ensures the server cannot generate seeds at rotation time after seeing the player's client seed — the next seed was already locked before the previous epoch began.
// Step 2: Next-Seed Promotion (Commitment Linkage)for (const s of seeds) { if (!s.nextSeedPromotion) continue; promoChecked++; // recompute linkage — don't trust a captured flag: const ok = s.nextSeedPromotion.previousNextHash === s.nextSeedPromotion.newActiveHash; if (!ok) promoFails++;}1.3Hash Consistency Within Epoch
For each of the 131 bet-bearing epochs (121 primary + 10 Phase E), the serverSeedHashed field was extracted from every bet response and checked for uniqueness. More than one distinct hash within a single epoch would indicate a mid-epoch seed substitution — a critical commit-reveal violation. Step 3 of the verification pipeline runs against the primary dataset's 121 epochs directly; the additional 10 Phase E epochs are checked implicitly through the death-point invariance test (Step 21) — any mid-epoch hash change there would surface as a recomputation failure.
The combined dataset contains 139 seed entries across 131 bet-bearing epochs. The 8 non-bet-bearing entries are phase-boundary marker rotations — structural artifacts of the capture script forcing a clean seed rotation at each phase transition. Every bet-bearing epoch had its commit hash verified against the revealed server seed; marker rotations carry valid commitments but no bets reference them.
// Step 3: Hash Consistency Within Epochfor (const [, epochBets] of byHash) { const distinctHashes = new Set(epochBets.map(b => b.seed.serverSeedHashed)); if (distinctHashes.size !== 1) epochsWithMultipleHashes++;}serverSeedHashed constant within every epoch. Zero mid-epoch changes detected.1.4Client Seed Origin & Control
Players have full control over their client seed through the Duel.com fairness UI, allowing them to view, modify, or randomize it at any time before placing bets. The client seed is an input to every HMAC-SHA256 computation — changing it produces a completely different death-point layout. The client seed is browser-generated (Full Pass origin) — the server commits to its seed before the client seed for that epoch is known, making cherry-picking structurally impossible.
8AgNlaGR1fxeiy932u03Imtz0NnpNAklsl0FFAHA20CUJBSytd4o47U8ntfUFG6kpt06Uq7yLDoqWtjI
beef-master-6000bets.json, beef-phaseE-450bets.json1.5Nonce Incrementation
The nonce begins at 0 and increments by 1 for each bet under the same server seed. In Beef, the nonce advances once per round — every bet uses one nonce value, which is shared across all steps within that round. The nonce resets to 0 when the player rotates their seed, starting a new epoch. In this audit we rotated every 50 bets as our chosen sampling cadence for the primary capture (nonces 0–49 per epoch, 121 epochs); Phase E epochs vary in length per sub-phase. Epoch length is not enforced by the casino — players can rotate at any time.
// Step 4: Nonce Auditfor (const [hash, epochBets] of byHash) { const sorted = [...epochBets].sort((a, b) => a.seed.nonce - b.seed.nonce); const nonces = sorted.map(b => b.seed.nonce); const clientSeeds = new Set(sorted.map(b => b.seed.clientSeed)); if (clientSeeds.size !== 1) { hardFailures.push(`Epoch ${shortHash}: ${clientSeeds.size} distinct client seeds`); } if (nonces[0] !== 0) { hardFailures.push(`Epoch ${shortHash}: first nonce is ${nonces[0]} (expected 0)`); }}1.6Deterministic Mapping
The RNG algorithm is fully deterministic: given the same server seed, client seed, nonce, and difficulty level, it always produces the exact same death-point SET. The algorithm is a backward Fisher-Yates shuffle with HMAC-SHA256 on a 20-tile grid. The server seed is hex-decoded to 32 raw bytes before use as the HMAC key. HMAC message format: clientSeed:nonce:cursor where cursor starts at 0 for the first shuffle step (i=19). Each step produces a uint32 from a 4-byte HMAC chunk; rejection sampling via the maxFair ceiling ensures bias-free index selection. After 19 steps, positions[0..deathPointsCount-1] (sorted) gives the death-point SET.
export function computeDeathPoints( serverSeed: string, clientSeed: string, nonce: number, deathPointsCount: number, gridSize = GRID_SIZE,): number[] { const key = Buffer.from(serverSeed, 'hex'); return computeDeathPointsFromBuffer(key, clientSeed, nonce, deathPointsCount, gridSize);}mines_positions. Zero SET mismatches. No external entropy is mixed into the Beef RNG.Real Bet Verified:
// Source: data/beef-master-6000bets.json// Round ID: 7722773 (Phase A, difficulty=2 MEDIUM, m=3, nonce=1)// ✅ VERIFIED — death-point set recomputed from revealed server seed { "serverSeed": "fcf0584ae26b61deecc138adfc788ef039d69814c172a7d71667b5c9cdc661fb", "serverSeedHashed": "b86763e0dc0f362d83e9bf1e6466f9be05434a502b7ea5fd1f96c2873b2bbcfe", "clientSeed": "8AgNlaGR1fxeiy93", "nonce": 1, "difficulty_level": 2, "current_step": [0], "mines_positions": [1, 9, 15], "multiplier": "1.176470588235294118", "no_house_edge_multiplier": "1.167058823529411765", "amount_won": "0.011670588235294118"}Verification:
// computeDeathPoints("fcf0584a…", "8AgNlaGR1fxeiy93", 1, 3) // Backward Fisher-Yates: 19 steps (i=19 downto 1)// Each step: HMAC-SHA256(hexDecode(serverSeed), "8AgNlaGR1fxeiy93:1:{cursor}")// cursor = gridSize - 1 - i (starts at 0)// Rejection sampling: chunk < maxFair → j = chunk % range; swap // Death-point SET: {1, 9, 15} ✅// Tile 0 stepped on (not in death-point set) → win ✅// Multiplier (m=3, k=1): 20 / (20−3) = 20/17 = 1.1765× ✅// Payout multiplier: 1.1765 × 0.992 = 1.1671× ✅// Payout: 0.01 × 1.1671 = 0.011671 ✅1.7Client Seed Influence
To confirm the client seed is a genuine input to the HMAC-SHA256 computation, a sample of bets across all 121 primary epochs was recomputed using a deliberately incorrect client seed ('wrong-client-seed-test'). 597 of 601 bets (99.3%) produced a different death-point set with the wrong client seed — every such outcome proves the client seed is a material input. The 4 collisions occurred in EASY-difficulty rounds (m=1) where the 20-position sample space makes a random collision expected; this is not a defect but a statistical consequence of the single-death-point set having only 20 possible outcomes.
// Step 6: Client Seed Influenceconst WRONG_CLIENT = 'wrong-client-seed-test';for (const [hash, epochBets] of byEpoch) { const ss = seedMap.get(hash); if (!ss) continue; for (const b of epochBets.slice(0, 5)) { tested++; const dpc = DEATH_POINTS_BY_DIFFICULTY[b.response.difficulty_level]; const correct = computeDeathPoints(ss, b.seed.clientSeed, b.seed.nonce, dpc); const wrong = computeDeathPoints(ss, WRONG_CLIENT, b.seed.nonce, dpc); if (correct.join(',') !== wrong.join(',')) changed++; }}Technical Evidence & Verification5 sections

1.8Evidence Coverage Summary6 checks

| Verification Area | Coverage | Result |
|---|---|---|
| Seed hash integrity (Step 1) | 131 / 131 revealed seeds hash-verified | Pass |
| Commitment linkage (Step 2) | All next-seed promotions verified | Pass |
| Hash consistency (Step 3) | Constant within each of 131 epochs | Pass |
| Nonce audit (Step 4) | Sequential, 0 gaps, 0 duplicates across 131 epochs | Pass |
| Death-point recomputation (Step 5) | 6,450 / 6,450 exact match | Pass |
| Client seed influence (Step 6) | Confirmed — client seed alters death-point positions | Pass |
1.9Code References7 source files

| File | Purpose |
|---|---|
| tests/verify.ts | 22-step verification pipeline (Steps 1–6 cover S1) |
| tests/steps/commitment.ts | Steps 1–4: Commit-reveal integrity checks |
| tests/steps/determinism.ts | Steps 5–6: Death-point recomputation and client seed influence |
| src/rng.ts | HMAC-SHA256 backward Fisher-Yates (computeDeathPoints, verifyHash) |
| src/loader.ts | Dataset loading + seed/bet parsing |
| capture/beef-capture.reference.js | Browser-based data collection script (Phases A–D) |
| capture/beef-capture-phaseE.reference.js | Multi-step cash-out capture script (Phase E) |

1.10Datasets UsedSource artifacts


| Property | Value |
|---|---|
| File | data/beef-master-6000bets.json |
| Scope | Phases A–D — baseline difficulty coverage, high-variance EXPERT sampling, $10 bet-size invariance (Phase C), custom client seed variation (Phase D). All single-step (k=1) outcomes. |
| Records | 6,000 bets, 125 seed entries, 121 bet-bearing epochs |
| SHA-256 | d654ef7c6195584501e9033202d5acad13a16d89d296baab8befc0240fb36d36 |
| Property | Value |
|---|---|
| File | data/beef-phaseE-450bets.json |
| Scope | Phase E — multi-step cash-out validation across k=2, 3, 5 on all 4 difficulty levels. Covers multiplier chain integrity and death-point invariance at k>1. |
| Records | 450 bets, 14 seed entries, 10 bet-bearing epochs |
| SHA-256 | ef39d7f584cdb6d8057e846cdcb9b4ffcc60495bfcce8443d15bb910a9c51001 |
Fields used: serverSeed, serverSeedHashed, clientSeed, nonce, difficulty_level, mines_positions, current_step, multiplier, no_house_edge_multiplier, amount_won, effective_edge, round_id. The Phase E dataset adds: step_results[], cashed_out, reached_k.
1.11Verified Invariants9 invariants

| Invariant | Result |
|---|---|
| SHA-256(hexDecode(serverSeed)) = serverSeedHashed for all 121 revealed primary seeds | Pass |
| Next-seed promotion chain intact for all 125 transitions | Pass |
| serverSeedHashed constant within epoch for all 121 primary epochs | Pass |
| Zero nonce duplicates within any epoch | Pass |
| Single nonce gap across all epochs (capture-retry), reconstructed from revealed seed | Pass |
| Single client seed per epoch across all 121 epochs | Pass |
| Same inputs produce same death-point SET for all 6,000 primary bets | Pass |
| Wrong client seed changes death-point SET in 99.3% of tests (597 / 601) | Pass |
| Client seed is browser-generated (Full Pass origin) | Pass |
1.12Reproduction InstructionsRun locally

Clone the repository, install dependencies, and run the verification suite:
git clone https://github.com/ProvablyFair-org/duel-beef.gitcd duel-beef && npm installnpm run verify# Expected output: Steps 1–6 all PASSSteps 1–6 cover all Seed, Nonce & Determinism checks. Expected output:
[PASS] Step 1 — Seed Hash Integrity
[PASS] Step 2 — Next-Seed Promotion (Commitment Linkage)
[PASS] Step 3 — Hash Consistency Within Epoch
[PASS] Step 4 — Nonce Audit
[PASS] Step 5 — Outcome Recomputation (Death Points)
[PASS] Step 6 — Client Seed InfluenceRNG & Entropy Model
Is the randomness genuinely random, or could it be rigged?
This section verifies that Duel.com's Beef random number generation produces cryptographically sound, unbiased outputs using only the disclosed inputs. The RNG uses a backward Fisher-Yates shuffle with HMAC-SHA256 — each shuffle step derives a swap index from a 4-byte HMAC chunk with bias-free rejection sampling via the maxFair ceiling. We independently implemented this algorithm, verified it produces the same results as the live game, and confirmed no hidden inputs can influence outcomes.
Cryptographic Randomness Verification
What we verified
- HMAC-SHA256 produces cryptographically sound, unpredictable output for each shuffle step
- Only disclosed inputs affect outcomes — no timestamps, no server-side state, no hidden entropy
- Rejection sampling via
maxFairceiling eliminates modulo bias for all ranges (2–20) - Death-point placement follows uniform distribution for all 4 difficulty levels (confirmed over 4M simulated rounds)
- Consecutive outcomes are statistically independent — no patterns, no streaks
- 99.3% of outcomes change with a different client seed (597 / 601 tested bets)
What this means for you
- Each death-point placement is generated fairly and cannot be skewed
- All 20 grid positions are equally likely to host a death point — no positional bias
- No hidden randomness or server-side tricks influence where death points appear
- Consecutive bets are not correlated — past results don't affect future outcomes
- The algorithm depends only on seeds you can verify
- HMAC-SHA256 produces cryptographically sound, unpredictable output for each shuffle step
- Only disclosed inputs affect outcomes — no timestamps, no server-side state, no hidden entropy
- Rejection sampling via
maxFairceiling eliminates modulo bias for all ranges (2–20) - Death-point placement follows uniform distribution for all 4 difficulty levels (confirmed over 4M simulated rounds)
- Consecutive outcomes are statistically independent — no patterns, no streaks
- 99.3% of outcomes change with a different client seed (597 / 601 tested bets)
- Each death-point placement is generated fairly and cannot be skewed
- All 20 grid positions are equally likely to host a death point — no positional bias
- No hidden randomness or server-side tricks influence where death points appear
- Consecutive bets are not correlated — past results don't affect future outcomes
- The algorithm depends only on seeds you can verify
RNG derived only from disclosed inputsPass
Entropy purityPass
Algorithm independently implementedPass
Modulo biasPass
maxFair ceiling eliminates bias for all ranges (2–20)Key encoding verifiedPass
Serial independencePass
Client seed influencePass
The Beef RNG uses only the disclosed inputs, produces uniform death-point distribution across all 4 difficulty levels, and shows no serial dependence across 4M simulated rounds. The client seed is a genuine input — 99.3% of outcomes change with a different seed.
| Check | Result | Evidence |
|---|---|---|
| RNG derived only from disclosed inputs | Pass | HMAC-SHA256(hexDecode(serverSeed), clientSeed:nonce:cursor) — no hidden entropy |
| Entropy purity | Pass | No timestamps, external APIs, Math.random, or server-side state |
| Algorithm independently implemented | Pass | Independent implementation produces identical death-point SETs for all 6,450 bets |
| Modulo bias | Pass | Rejection sampling via maxFair ceiling eliminates bias for all ranges (2–20) |
| Key encoding verified | Pass | Server seed hex-decoded to bytes (not UTF-8) — confirmed via 6,450-bet recomputation |
| Serial independence | Pass | Lag-1 autocorrelation near zero and runs tests pass across all 4 difficulty levels at 1M rounds each |
| Client seed influence | Pass | 99.3% of outcomes change with an alternate client seed — confirmed across 601 tested bets |
RNG derived only from disclosed inputsPass
Entropy purityPass
Algorithm independently implementedPass
Modulo biasPass
maxFair ceiling eliminates bias for all ranges (2–20)Key encoding verifiedPass
Serial independencePass
Client seed influencePass
The Beef RNG uses only the disclosed inputs, produces uniform death-point distribution across all 4 difficulty levels, and shows no serial dependence across 4M simulated rounds. The client seed is a genuine input — 99.3% of outcomes change with a different seed.
How It Works — RNG & Entropy Model7 sections
2.1RNG Function Implementation
Each Beef bet places m death points on a 20-tile grid using a backward Fisher-Yates shuffle. The algorithm iterates from index 19 down to 1 (19 steps). At each step, an HMAC-SHA256 hash is computed with the hex-decoded server seed as key and clientSeed:nonce:cursor as the message. The first 4-byte chunk below the maxFair ceiling is used: j = chunk % range determines the swap index. After all 19 steps, positions[0..deathPointsCount−1] (sorted ascending) gives the death-point SET.
| Component | Detail |
|---|---|
| Hash function | HMAC-SHA256 |
| Key | Buffer.from(serverSeed, 'hex') — 32 bytes |
| Message | clientSeed:nonce:cursor |
| Extraction | 4-byte chunks → parseInt(hex, 16) → uint32 |
| Rejection | value < maxFair — bias-free ceiling per range |
| Reduction | uint32 % range → swap index j ∈ [0, range) |
| Shuffle | Backward Fisher-Yates: i=19 downto 1 |
| Output | positions[0..deathPointsCount−1] (sorted) → death-point SET |
export function computeDeathPointsFromBuffer( keyBuffer: Buffer, clientSeed: string, nonce: number, deathPointsCount: number, gridSize = GRID_SIZE,): number[] { if (deathPointsCount >= gridSize) { throw new Error(`deathPointsCount (${deathPointsCount}) must be less than gridSize (${gridSize})`); } const positions: number[] = Array.from({ length: gridSize }, (_, i) => i); for (let i = gridSize - 1; i > 0; i--) { const range = i + 1; const maxFair = MAX_UINT32 - (MAX_UINT32 % range); let cursor = gridSize - 1 - i; while (true) { const message = `${clientSeed}:${nonce}:${cursor}`; const hmac = crypto.createHmac('sha256', keyBuffer).update(message).digest('hex'); let found = false; for (let off = 0; off + 8 <= hmac.length; off += 8) { const value = parseInt(hmac.substring(off, off + 8), 16); if (value < maxFair) { const j = value % range; [positions[i], positions[j]] = [positions[j], positions[i]]; found = true; break; } } if (found) break; cursor++; } } return positions.slice(0, deathPointsCount).sort((a, b) => a - b);}2.2Entropy Sources
All randomness derives exclusively from the deterministic HMAC-SHA256 function combining three cleanly separated inputs:
| Source | Controlled By | Purpose |
|---|---|---|
| Server Seed | Casino | Base randomness (committed via SHA-256 hash before betting) |
| Client Seed | Player | Player-contributed entropy |
| Nonce | System | Uniqueness per bet (increments automatically within each epoch) |
| Cursor | System | Per-step isolation (0 to 18, one per Fisher-Yates step) |
How we know: 6,450/6,450 bets were recomputed using only the three declared inputs. If any hidden entropy source existed, recomputation would fail. It does not.
Verified absent: No timestamps, no Math.random(), no external APIs, no server-side mutable state. Only: HMAC-SHA256(hexDecode(serverSeed), clientSeed:nonce:cursor)
2.3Modulo Bias Analysis
Each shuffle step's swap index is determined by chunk % range where range varies from 2 to 20 across the 19 Fisher-Yates steps. Modulo bias occurs when 2^32 is not evenly divisible by the range. The algorithm eliminates this bias entirely via rejection sampling: a ceiling maxFair = 0xFFFFFFFF − (0xFFFFFFFF % range) ensures only unbiased chunks are used. Any chunk ≥ maxFair is discarded.
For range = 20 (first step, i=19):
  maxFair = 0xFFFFFFFF − (0xFFFFFFFF % 20)
          = 4,294,967,295 − 15
          = 4,294,967,280  (= 0xFFFFFFF0)

  Rejected values: [4,294,967,280 .. 4,294,967,295] = 16 values
  Rejection rate: 16 / 4,294,967,296 ≈ 3.7 × 10⁻⁹

  Accepted range size: 4,294,967,280 = 214,748,364 × 20
→ each residue 0–19 equally likely (zero bias)For range = 2 (last step, i=1), maxFair = 0xFFFFFFFF − (0xFFFFFFFF % 2) = 0xFFFFFFFE. Only two values (0xFFFFFFFE, 0xFFFFFFFF) are rejected — negligible. For all 19 ranges in the shuffle, the rejection ceiling makes every swap index uniformly distributed. Retries (all 8 chunks rejected in one hash) are astronomically rare — probability (16/2^32)^8 ≈ 4 × 10⁻⁶⁸ for range=20.
2.4RNG Isolation
Each shuffle step within a single bet uses a unique cursor value in the HMAC message (clientSeed:nonce:cursor), ensuring per-step outputs are cryptographically independent. Each bet uses a unique nonce, ensuring per-bet outputs are independent. HMAC-SHA256 is a pseudorandom function — knowing one step's output gives zero information about other steps' outputs. There is no shared state between steps, between bets, or between epochs.
Evidence: The computeDeathPointsFromBuffer implementation in 2.1 confirms this — it is a pure function with no class state, no external calls, and no cross-bet memory. The function takes (keyBuffer, clientSeed, nonce, deathPointsCount) explicitly and returns an array. Same inputs always produce the same output.
2.5Monte Carlo Simulation (4M Rounds)
A 4,000,000-round Monte Carlo simulation (1,000,000 rounds per config, all 4 difficulty-level configurations) verified that the algorithm produces the expected death-point distribution at scale.
| Metric | Value |
|---|---|
| Average simulated RTP | 99.1468% |
| Average theoretical RTP | 99.2000% |
| Chi-squared (α=0.01) | 4/4 configs pass |
| Bonferroni-corrected (α/4 = 0.0025) | 4/4 pass |
| Serial independence | 4/4 pass |
// From src/simulate.ts — constants and pinned simulation seedsconst DIFFICULTIES: Array<1|2|3|4> = [1, 2, 3, 4];const ROUNDS_PER_CONFIG = 1_000_000;const NONCES_PER_SEED = 10_000;const EPOCH_LENGTH = 50;const THEORETICAL_RTP = 1 - HOUSE_EDGE; // 0.992const CONVERGENCE_SAMPLES = [1_000, 5_000, 10_000, 50_000, 100_000, 500_000, 1_000_000]; // Representative difficulty for Pass 2 — MEDIUM (deathPointsCount=3) gives// 85% first-step win chance, a good balance of sample size and variance.const PASS2_DIFFICULTY = 2 as const;const PASS2_DPC = DEATH_POINTS_BY_DIFFICULTY[PASS2_DIFFICULTY];All 4 configurations pass individual chi-squared tests. Serial independence: 0 failures across 4M rounds.
Methodology: Per-config pinned seeds for reproducibility — one unique (serverSeed, clientSeed) pair per difficulty level, generated once via crypto.randomBytes. Chi-squared goodness-of-fit on death-point frequency across the 20 grid positions. Serial independence tested via lag-1 autocorrelation and Wald-Wolfowitz runs test on the per-round outcome sequence.
2.6Serial Independence
Serial independence ensures consecutive bet outcomes are not correlated — winning or losing on one bet does not affect the next. Two tests were applied to each configuration in the Pass 1 simulation (1,000,000 rounds per config):
Lag-1 autocorrelation: Measures correlation between consecutive outcome sequence values. Expected r ≈ 0 for independent sequences. Threshold: |z| > 3 (where z = r × √n).
Wald-Wolfowitz runs test: Tests whether the sequence of above/below-median outcomes has the expected number of runs. p < 0.01 indicates non-random structure.
export function lag1Autocorrelation(series: number[]): number { const n = series.length; const mean = series.reduce((a, b) => a + b, 0) / n; let num = 0, den = 0; for (let i = 0; i < n - 1; i++) num += (series[i] - mean) * (series[i + 1] - mean); for (let i = 0; i < n; i++) den += (series[i] - mean) ** 2; return den === 0 ? 0 : num / den;}2.7Worked Example — Full RNG Trace
Real bet from dataset — Round ID 7722773, difficulty=2 (MEDIUM, m=3), nonce 1. Verified from beef-master-6000bets.json:
serverSeed       = fcf0584ae26b61deecc138adfc788ef039d69814c172a7d71667b5c9cdc661fb
clientSeed       = 8AgNlaGR1fxeiy93
nonce            = 1
difficulty_level = 2 (MEDIUM, m=3)
current_step = [0]| i | cursor | range | HMAC[:8] | uint32 | j | swap |
|---|---|---|---|---|---|---|
| 19 | 0 | 20 | 5ed36ebf | 1,590,914,751 | 11 | pos[19]↔︎pos[11] |
| 18 | 1 | 19 | ee6377b7 | 3,999,496,119 | 14 | pos[18]↔︎pos[14] |
| 17 | 2 | 18 | 79caf915 | 2,043,345,173 | 5 | pos[17]↔︎pos[5] |
| 16 | 3 | 17 | e6d47848 | 3,872,684,104 | 5 | pos[16]↔︎pos[5] |
| 15 | 4 | 16 | a582f7fe | 2,776,823,806 | 14 | pos[15]↔︎pos[14] |
20 / (20−3) = 20/17 = 1.1765×. Payout: 0.01 × 1.1765 × 0.992 = 0.011671.Technical Evidence & Verification5 sections
2.8Evidence Coverage Summary6 checks
| Verification Area | Coverage | Result |
|---|---|---|
| Algorithm implementation (Step 5) | 6,000 / 6,000 primary bets | Pass |
| Key encoding (hex vs UTF-8) | Confirmed via recomputation | Pass |
| Modulo bias analysis | Rejection sampling: maxFair ceiling for all ranges 2–20 | Pass |
| External entropy non-participation (Step 5) | 6,000 / 6,000 reproduced from disclosed inputs alone | Pass |
| Simulation chi-squared (Step 18) | 0 / 4 configs fail at α=0.01 | Pass |
| Serial independence (Step 18) | 0 / 4 configs fail (lag-1 + runs test) | Pass |
2.9Code References5 source files
| File | Purpose |
|---|---|
| src/rng.ts | HMAC-SHA256 backward Fisher-Yates (computeDeathPoints, computeDeathPointsFromBuffer) |
| src/simulate.ts | Monte Carlo simulation (4M rounds, two-pass) |
| src/stats.ts | Chi-squared, lag-1 autocorrelation, Wald-Wolfowitz runs test |
| tests/steps/determinism.ts | Steps 5–6: Death-point recomputation and client seed influence |
| tests/steps/simulation.ts | Steps 18–19: Simulation integrity verification |
2.10Verified Invariants9 invariants
| Invariant | Result |
|---|---|
| HMAC-SHA256 output matches live game for all 6,450 bets | Pass |
| Key is hex-decoded (not UTF-8) — wrong encoding produces wrong death-point SETs | Pass |
| Rejection sampling eliminates modulo bias for all ranges (2–20) | Pass |
| No external entropy sources required for death-point computation | Pass |
| Death-point distribution is uniform across the 20-tile grid for all 4 difficulty levels (1M rounds each) | Pass |
| Lag-1 autocorrelation near zero for all 4 configs | Pass |
| Runs test p > 0.01 for all 4 configs | Pass |
| Per-config simulated RTP converges to 99.2% theoretical | Pass |
| Client seed change produces different death-point SET in 99.3% of bets (597/601) | Pass |
2.11Datasets UsedSource artifacts
2.12Reproduction InstructionsRun locally
Clone the repository, install dependencies, and run the simulation and verification:
git clone https://github.com/ProvablyFair-org/duel-beef.gitcd duel-beef && npm installnpm run simulate # 4M-round simulation (~90 sec)npm run verify # Steps 5, 18 cover S2S2-related steps:
[PASS] Step 5 — Outcome Recomputation (Death Points)
[PASS] Step 18 — Simulation Results — Pass 1 IntegrityVerifier Parity
Does the live game actually follow its own rules?
This section validates that the independent verifier produces the exact same death-point set as the live game for every single bet. It also confirms the win condition and that every payout matches Duel's published multiplier formula. Any mismatch would invalidate the fairness guarantee.

Live ↔︎ Verifier Parity
What we verified
- Every bet independently recomputed from seeds — full death-point SET verified, not just the payout
- Payout correctness: amount_won = amount × multiplier, exact to 8 decimal places for all 6,450 bets
- Multiplier formula produces the correct value for all 4 difficulty-level configurations
- Bet amount is not an input to the RNG — death-point layout depends only on seeds and nonce
- All five capture phases recomputed identically (baseline difficulty coverage, high-variance EXPERT, elevated stake, client-seed variation, multi-step + cash-out)
What this means for you
- The verifier isn't a simulation — it produces the exact same death-point set as the live game
- Every bet you play can be independently recomputed by anyone
- No hidden logic alters outcomes based on how much you bet or how many tiles you step on
- The game engine in production matches the published algorithm exactly
- Every bet independently recomputed from seeds — full death-point SET verified, not just the payout
- Payout correctness: amount_won = amount × multiplier, exact to 8 decimal places for all 6,450 bets
- Multiplier formula produces the correct value for all 4 difficulty-level configurations
- Bet amount is not an input to the RNG — death-point layout depends only on seeds and nonce
- All five capture phases recomputed identically (baseline difficulty coverage, high-variance EXPERT, elevated stake, client-seed variation, multi-step + cash-out)
- The verifier isn't a simulation — it produces the exact same death-point set as the live game
- Every bet you play can be independently recomputed by anyone
- No hidden logic alters outcomes based on how much you bet or how many tiles you step on
- The game engine in production matches the published algorithm exactly
Death-point SET recomputationPass
Payout correctnessPass
Multiplier formula integrityPass
Bet-size independencePass
Config completenessPass
Multi-step parityPass
Multi-phase coveragePass
All 6,450 bets matched the independent verifier exactly — death-point sets verified across all five capture phases, including 450 multi-step bets with up to 5 steps each. Payout math correct. Multiplier formula confirmed across all 4 difficulty-level configurations.
| Check | Result | Evidence |
|---|---|---|
| Death-point SET recomputation | Pass | 6,450 / 6,450 exact match — death-point SET verified for every bet |
| Payout correctness | Pass | All 6,450 bets: amount_won = amount × no_house_edge_multiplier, exact to 8 decimal places |
| Multiplier formula integrity | Pass | All observed multipliers match C(20,k) / C(20−m,k) × 0.992 for all 4 difficulty-level configurations |
| Bet-size independence | Pass | Bet amount is absent from the RNG input — death-point layout depends only on seeds and nonce |
| Config completeness | Pass | All 4 difficulty levels (EASY, MEDIUM, HARD, EXPERT) covered in live data |
| Multi-step parity | Pass | Phase E: 1,085 step-multiplier pairs verified across 15 distinct (difficulty, k) combos; 450 multi-step bets match recomputed death-point set |
| Multi-phase coverage | Pass | 5 structured phases: baseline difficulty coverage (A), high-variance EXPERT (B), elevated stake (C), client-seed variation (D), multi-step + cash-out (E) |
Death-point SET recomputationPass
Payout correctnessPass
Multiplier formula integrityPass
Bet-size independencePass
Config completenessPass
Multi-step parityPass
Multi-phase coveragePass
All 6,450 bets matched the independent verifier exactly — death-point sets verified across all five capture phases, including 450 multi-step bets with up to 5 steps each. Payout math correct. Multiplier formula confirmed across all 4 difficulty-level configurations.
How It Works — Verifier Parity8 sections
3.1Why Parity Matters
If the verifier produces results that differ from the live game, players cannot trust the verification — the entire provably fair system becomes meaningless. 100% parity is required because even a single discrepancy would indicate either a bug in the verification logic, manipulation in the live game, or inconsistent RNG implementation. Players must be able to take the revealed seeds after gameplay, input them into the independent verifier, and receive the exact same death-point layout they experienced during live play.
3.2Five-Phase Collection Design
Data was collected across five structured phases, each designed to test a specific fairness property. The phases are complementary — together they cover difficulty-level breadth, high-variance edge cases, bet-size invariance, client seed variation, and multi-step cash-out flows.
| Phase | Bets | Config | Bet Amount | Purpose |
|---|---|---|---|---|
| A — Baseline difficulty coverage | 4,000 | 4 difficulties (1,000 per config) | $0.01 | Verify formula correctness across every difficulty level |
| B — High-variance EXPERT edge case | 1,000 | 1 config (EXPERT, m=10) | $0.01 | Maximum variance; 10 death points on a 20-tile grid (50% first-step win chance) |
| C — Stake equivalence | 200 | 1 config (MEDIUM, m=3) | $10.00 | Confirm bet amount is not an RNG input |
| D — Client-seed variation | 800 | 4 difficulties (random) | $0.01 | 16 custom pfaudit-prefixed client seeds; confirms seed control is player-side |
| E — Multi-step & cash-out | 450 | 4 sub-phases across all 4 difficulties, target_k ∈ {2, 3, 5} | $0.01 | Multi-step reveal chains, cash-out correctness, death-point invariance at k>1 |
3.3Death-Point Recomputation (Step 5)
For every bet belonging to an epoch with a revealed server seed, the verifier independently computed the death-point set using computeDeathPointsFromBuffer(key, clientSeed, nonce, deathPointsCount) and compared it (as a SET) to the server-reported mines_positions. The computation uses HMAC-SHA256 backward Fisher-Yates with the hex-decoded server seed as key.
// Step 5: Death-point recomputationfor (const b of bets) { const ss = seedMap.get(b.seed.serverSeedHashed); if (!ss) { skipped++; continue; } const dpc = DEATH_POINTS_BY_DIFFICULTY[b.response.difficulty_level]; const key = Buffer.from(ss, 'hex'); const computed = computeDeathPointsFromBuffer(key, b.seed.clientSeed, b.seed.nonce, dpc); const actual = [...b.response.mines_positions].sort((a, c) => a - c); if (computed.length !== actual.length || !computed.every((v, i) => v === actual[i])) mismatches++;}mines_positions in the dataset. Phase E's 450 multi-step bets additionally verified via Step 21 — see 3.9 Evidence Coverage Summary.3.4Payout Math (Step 7)
For each of the 6,450 bets, the verifier computed amount × no_house_edge_multiplier and compared the result to the server-reported amount_won. The tolerance is 1×10⁻⁸ — any difference larger than this would indicate the server is applying hidden fees, rounding errors, or incorrect multipliers. Beef's API exposes two multiplier fields: multiplier is the raw ratio C(20,k)/C(20−m,k) without the edge applied, and no_house_edge_multiplier is the actual payout multiplier with the 0.992 edge factor applied. The payout formula uses the latter.
// Step 7: Payout mathfor (const b of bets) { if (b.response.outcome === 'win') { const amt = parseFloat(b.response.amount_currency || b.request.amount); const nhe = parseFloat(b.response.no_house_edge_multiplier ?? '0'); const won = parseFloat(b.response.amount_won); if (Math.abs(amt * nhe - won) > 1e-8) payoutErrors++; } else { if (b.response.amount_won !== '0') payoutErrors++; }}amount_won = amount × no_house_edge_multiplier within tolerance 1e-8. Zero mismatches. Payout math is exact. Phase E multi-step cash-outs additionally verified by Step 22 (202 cash-outs across k ∈ {2, 3, 5}).3.5Multiplier Formula Verification (Step 8)
Beef's payout multiplier is derived from the combinatorial ratio C(20,k) / C(20−m,k) × 0.992. Duel's /api/v2/cross-road/config endpoint publishes a pre-computed payout_tables lookup (61 entries across the 4 difficulties) — we independently verified every table entry matches the closed-form formula exactly (max deviation 4.55 × 10⁻¹³). Step 8 verifies that every observed no_house_edge_multiplier on live bets matches the formula with k=1 (the primary dataset's step count) and every multiplier matches the un-edged ratio 20/(20−m). Step 20 extends this to k ∈ {1..5} for Phase E multi-step bets.
| Metric | Count |
|---|---|
| Total winning bets checked | 4,337 |
| Matching formula at k=1 | 4,337 |
| Mismatches | 0 |
| Multi-step pairs verified (Step 20) | 1,085 across 15 distinct (difficulty, k) combos |
// Step 8: Multiplier formula (C(20,k)/C(20-m,k) × edge)for (const b of bets) { if (b.response.outcome !== 'win') continue; const dpc = DEATH_POINTS_BY_DIFFICULTY[b.response.difficulty_level]; const k = (b.response.current_step || []).length; // number of steps completed const expRaw = theoreticalMultiplier(dpc, k, 0); const actRaw = parseFloat(b.response.multiplier); if (Math.abs(expRaw - actRaw) > 1e-6) multErrors++; const expEdge = theoreticalMultiplier(dpc, k, HOUSE_EDGE); const actEdge = parseFloat(b.response.no_house_edge_multiplier ?? '0'); if (Math.abs(expEdge - actEdge) > 1e-6) multErrors++;}C(20,k) / C(20−m,k) × 0.992. 4/4 difficulty-level configurations verified at k=1; 1,085 multi-step pairs verified at k > 1 (Step 20). Flat 0.8% house edge across all configs — no scaling edge.3.6Win Condition Verification (Step 9)
In Beef, the win condition is purely structural: the bet wins if and only if every stepped tile is not in the death-point set. Step 9 verifies this for every bet — for each of the 6,000 primary bets we checked that outcome === 'win' matches every step in current_step[] ∉ mines_positions. For Phase E's multi-step bets, Step 21 extends the check to step sequences up to k=5 — confirming the win condition holds across the full multi-step chain.
| Scope | Coverage | Verified |
|---|---|---|
| Primary dataset (Phase A–D) | 6,000 bets, single-step outcomes | 6,000 / 6,000 |
| Phase E multi-step win condition (Step 21) | 450 multi-step bets, k ∈ {1..5} | 450 / 450 |
| Phase E cash-out at k>1 (Step 22) | 202 winning bets at k>1 | 202 / 202 |
3.7Phase C — Bet-Size Equivalence (Step 10)
Phase C placed 200 bets at $10 on MEDIUM difficulty (m=3) — the same configuration tested at $0.01 elsewhere in the dataset. All 200 death-point layouts were recomputed correctly from revealed seeds. All 165 winning bets' multipliers matched the same C(20,k) / C(20−m,k) × 0.992 formula applied to $0.01 bets in Phase A. Equivalence is proven deterministically — 200/200 exact death-point-set matches.
3.8Worked Example — Full Parity Verification
Real bet from Phase E1 — Round ID 7843993, EASY (m=1), nonce 0, 5 safe steps cashed out. Verified from beef-phaseE-450bets.json:
serverSeed       = 414cf32bb0d5412e2e1f42fa304f4b45601e9715074ed2d436d8569ccaed5844
clientSeed       = zqpIvz4yp068AeIU
nonce            = 0
difficulty_level = 1 (EASY, m=1)
steps            = [0, 1, 2, 3, 4]
cashed_out       = true
reached_k        = 5
target_k = 5| Step | Process | Output |
|---|---|---|
| 1 | Backward Fisher-Yates: 19 HMAC-SHA256 calls | Shuffled positions array |
| 2 | positions[0..0] (sorted) → death-point SET | {6} |
| 3 | Player steps on tiles 0, 1, 2, 3, 4 — none in death-point set | 5 safe steps (win) |
| 4 | Multiplier chain: C(20,k) / C(20−1,k) for k=1..5 (edge applied at cash-out) | 1.0526× → 1.1111× → 1.1765× → 1.2500× → 1.3333× → payout mult 1.3227× |
| 5 | Cash-out payout: 0.01 × 1.322667 | 0.013227 ✅ |
// computeDeathPoints("414cf32b...", "zqpIvz4yp068AeIU", 0, 1)// 19 Fisher-Yates steps → death-point SET = {6}//// Step chain (player steps on tiles 0, 1, 2, 3, 4 — all safe).// Live step_results multipliers are the raw combinatorial ratio (no edge):// k=1: mult = C(20,1) / C(19,1) = 20/19 = 1.052632×// k=2: mult = C(20,2) / C(19,2) = 190/171 = 1.111111×// k=3: mult = C(20,3) / C(19,3) = 1140/969 = 1.176471×// k=4: mult = C(20,4) / C(19,4) = 4845/3876 = 1.250000×// k=5: mult = C(20,5) / C(19,5) = 15504/11628 = 1.333333×//// Cash-out at k=5 applies the 0.8% house edge:// no_house_edge_multiplier = 1.333333 × 0.992 = 1.322667// Payout: 0.01 × 1.322667 = 0.013227// Live amount_won: 0.013226666... ✅Technical Evidence & Verification5 sections
3.9Evidence Coverage Summary12 checks
| Verification Area | Coverage | Result |
|---|---|---|
| Death-point SET recomputation (Step 5) | 6,000 / 6,000 bets — full death-point SET verified | Pass |
| Payout math (Step 7) | 6,000 / 6,000 bets (exact to 8 decimal places) | Pass |
| Multiplier formula integrity (Step 8) | 4,337 winning bets — formula C(20,1)/C(20−m,1)×0.992 matches | Pass |
| Win condition (Step 9) | 6,000 / 6,000 bets — outcome=win iff every stepped tile ∉ mines | Pass |
| Phase C bet-size invariance (Step 10) | 200 / 200 at $10 | Pass |
| Config completeness (Step 11) | All 4 difficulty levels covered | Pass |
| House edge audit (Step 12) | 6,000 / 6,000 bets — effective_edge field is not a game-logic input; constant at 0.8, death-point sets and payouts derive from the seed pair and multiplier formula, not the field | Pass |
| Phase D client-seed variation (Step 17) | 800 bets, 16 custom client seeds — 800 / 800 match | Pass |
| Multi-step multiplier chain (Step 20) | 1,085 step-multiplier pairs across 15 (difficulty, k) combos | Pass |
| Death-point recomputation — Phase E (Step 21) | 450 multi-step bets — layout fixed at round start | Pass |
| Cash-out payout correctness (Step 22) | 202 cash-outs across k ∈ {2, 3, 5} (k=2:27, k=3:67, k=5:108) | Pass |
| Multi-phase coverage | 5 phases: A (4,000) + B (1,000) + C (200) + D (800) + E (450) | Pass |
3.10Code References5 source files
| File | Purpose |
|---|---|
| tests/steps/determinism.ts | Step 5: Death-point recomputation |
| tests/steps/payouts.ts | Steps 7–12: Payout math, multiplier formula, win condition, Phase C equivalence, config completeness, house edge |
| tests/steps/dataset.ts | Steps 13–17: Phase labels, dataset hash, epoch size, anti-circularity, Phase D client-seed variation |
| tests/steps/multireveal.ts | Steps 20–22: Multi-step chain, Phase E death-point recomputation, cash-out payout |
| src/rng.ts | HMAC-SHA256 backward Fisher-Yates, theoreticalMultiplier formula |
3.11Datasets UsedSource artifacts
3.12Verified Invariants11 invariants
| Invariant | Result |
|---|---|
| Computed death-point SET matches live mines_positions for all 6,450 bets | Pass |
| amount_won = amount × no_house_edge_multiplier, exact to 8 decimal places for all 6,450 bets | Pass |
| Every multiplier matches C(20,k) / C(20−m,k) × 0.992 for all 4 difficulty levels and all k ∈ {1..5} | Pass |
| Win condition holds: outcome=win iff every stepped tile ∉ death-point set for all 6,450 bets | Pass |
| Phase C ($10) produces identical death-point sets to $0.01 bets at MEDIUM difficulty | Pass |
| Phase C multipliers match the $0.01 formula (same config, different bet size) | Pass |
| No hidden inputs beyond (serverSeed, clientSeed, nonce, difficultyLevel) | Pass |
| All 4 difficulty levels (EASY, MEDIUM, HARD, EXPERT) present in live data | Pass |
| Phase D: 800/800 death-point sets verified across 16 custom pfaudit client seeds | Pass |
| Death-point set fixed at round start — unchanged by step sequence (Phase E, 450 bets) | Pass |
| Cash-out payouts correct at k > 1 — 202 cash-outs across k ∈ {2, 3, 5} | Pass |
3.13Reproduction InstructionsRun locally
git clone https://github.com/ProvablyFair-org/duel-beef.gitcd duel-beef && npm installnpm run verify# Expected output: Steps 5, 7–12, 17, 20–22 all PASSS3-related steps:
[PASS] Step 5 — Outcome Recomputation (Death Points)
[PASS] Step 7 — Payout Math
[PASS] Step 8 — Multiplier Formula (C(20,k)/C(20−m,k) × edge)
[PASS] Step 9 — Win Condition (all stepped tiles not in mines)
[PASS] Step 10 — Phase C Bet-Size Invariance ($10 bets)
[PASS] Step 11 — Config Completeness (4 difficulty levels)
[PASS] Step 12 — House Edge Audit (effective_edge = 0.8%)
[PASS] Step 17 — Phase D — Client Seed Variation
[PASS] Step 20 — Multi-Step Multiplier Chain (Phase E)
[PASS] Step 21 — Death-Point Recomputation (Phase E)
[PASS] Step 22 — Cash-Out Payout Correctness (k>1)RTP & Payout Logic
Is the house edge what the casino claims?
This section mathematically verifies the flat 0.8% game-engine house edge built into Beef's payout multipliers across all 4 difficulty-level configurations. The key test is anti-circularity: we prove the RTP from first principles using combinatorial cancellation — the win-chance ratio and the payout-multiplier ratio cancel algebraically to produce exactly 0.992, independent of any casino-supplied probability data. We then confirm it against 4 million simulated rounds and test whether the casino pre-selected favourable seeds. The 0.8% figure is the game-engine edge measured from the captured dataset; see 4.2 for how the operator's Zero Edge rakeback and Beef's subsequently updated advertised RTP relate to it.

Return to Player Verification
What we verified
- House edge is exactly 0.8% — flat across all 4 difficulty-level configurations and all bet sizes
- RTP proven from first principles: winChance × multiplier = 0.992 for every configuration — by algebraic cancellation, not summation
- 4M-round simulation converges on theoretical RTP (mean 99.147%)
- Cherry-pick detection: 121 casino seeds tested — no evidence of seed pre-selection
- Bet amount does not influence death-point placement — confirmed at $0.01 and $10
What this means for you
- The game-engine house edge on Beef is a flat 0.8%, the same regardless of which difficulty level or bet size you choose
- The RTP proof is derived independently — it doesn't rely on trusting the casino
- The casino's seeds show no evidence of being chosen to produce favourable early outcomes
- Your bet amount doesn't affect where the death points are placed
- No scaling house edge — Beef's margin is uniform across all 4 difficulty levels
- House edge is exactly 0.8% — flat across all 4 difficulty-level configurations and all bet sizes
- RTP proven from first principles: winChance × multiplier = 0.992 for every configuration — by algebraic cancellation, not summation
- 4M-round simulation converges on theoretical RTP (mean 99.147%)
- Cherry-pick detection: 121 casino seeds tested — no evidence of seed pre-selection
- Bet amount does not influence death-point placement — confirmed at $0.01 and $10
- The game-engine house edge on Beef is a flat 0.8%, the same regardless of which difficulty level or bet size you choose
- The RTP proof is derived independently — it doesn't rely on trusting the casino
- The casino's seeds show no evidence of being chosen to produce favourable early outcomes
- Your bet amount doesn't affect where the death points are placed
- No scaling house edge — Beef's margin is uniform across all 4 difficulty levels
Anti-circularityPass
House edge auditPass
Simulated RTP (Pass 1)Pass
Cherry-pick detection (Pass 2)Pass
Bet-size invariancePass
Multiplier formulaPass
Config completenessPass
The 99.2% RTP is proven mathematically from combinatorial cancellation — winChance × multiplier = 0.992 for all 4 difficulty-level configurations, and the identity extends unchanged to any step count k. This is a first-principles proof, not a statistical estimate. 4M simulated rounds and cherry-pick detection confirm no anomalies. The house edge is flat at 0.8% — no scaling structure.
| Check | Result | Evidence |
|---|---|---|
| Anti-circularity | Pass | winChance × payoutMult = 0.992 for all 4 configs — proven by algebraic cancellation of (20−m)/20 × 20/(20−m) × 0.992, no casino data used. Extends identically to k > 1 |
| House edge audit | Pass | Flat 0.8% house edge across all 4 difficulty-level configurations — derived from × 0.992 factor in the multiplier formula C(20,k)/C(20−m,k) × 0.992; flat across all bet sizes |
| Simulated RTP (Pass 1) | Pass | 4M rounds, avg RTP = 99.147%, 0/4 chi-squared failures, 0/4 serial independence failures |
| Cherry-pick detection (Pass 2) | Pass | 121 casino seeds tested at MEDIUM (m=3) × 10K nonces — Test A: 0/121 fails, Test B: 4 cherry-pick flags, 0 broad — no evidence of seed pre-selection |
| Bet-size invariance | Pass | Bet amount is not an input to the RNG — same death-point set distribution at $0.01 and $10. Tested in Phase C (200/200) |
| Multiplier formula | Pass | C(20,k) / C(20−m,k) × 0.992 independently verified for all 4 configs at k=1 and all 1,085 multi-step pairs at k ∈ {1..5} |
| Config completeness | Pass | All 4 difficulty levels (EASY, MEDIUM, HARD, EXPERT) covered |
Anti-circularityPass
House edge auditPass
Simulated RTP (Pass 1)Pass
Cherry-pick detection (Pass 2)Pass
Bet-size invariancePass
Multiplier formulaPass
Config completenessPass
The 99.2% RTP is proven mathematically from combinatorial cancellation — winChance × multiplier = 0.992 for all 4 difficulty-level configurations, and the identity extends unchanged to any step count k. This is a first-principles proof, not a statistical estimate. 4M simulated rounds and cherry-pick detection confirm no anomalies. The house edge is flat at 0.8% — no scaling structure.
How It Works — RTP & Payout Logic8 sections
4.1Anti-Circularity Proof (Step 16)
The anti-circularity proof establishes the 99.2% RTP from first principles without using any casino-supplied probability data. Beef's proof is an algebraic identity rather than a summation — the win chance and payout multiplier both contain the same combinatorial ratio, which cancels exactly.
Note on operator payout tables: Duel's /api/v2/cross-road/config endpoint publishes a pre-computed payout_tables lookup for each difficulty — 19 entries for EASY, 17 for MEDIUM, 15 for HARD, 10 for EXPERT (61 total). We independently verified every table entry matches the closed-form formula C(20,k) / C(20−m,k) × 0.992 exactly (max observed deviation 4.55 × 10⁻¹³ — floating-point epsilon). The anti-circularity proof below establishes RTP from the formula alone; the operator's published table is algebraically bound to the same identity.
| Component | Formula | Source |
|---|---|---|
| Win chance at step k | winChance(m, k) = C(20−m, k) / C(20, k) | Combinatorial — pure math, not from casino |
| Payout multiplier at step k | multiplier(m, k) = C(20, k) / C(20−m, k) × 0.992 | Derived from the same combinatorial ratio |
| RTP computation | winChance × multiplier (no summation — these are the only two terms that matter) | Independent probability × observed multiplier |
| Result | = 0.992 for all 4 difficulty levels and all valid k | First-principles proof by exact cancellation |
| Difficulty (m) | winChance (k=1) | Multiplier (with edge) | winChance × Multiplier | RTP |
|---|---|---|---|---|
| EASY (1) | 19/20 = 0.950000 | 20/19 × 0.992 = 1.044211 | 0.992000000 | 99.2% |
| MEDIUM (3) | 17/20 = 0.850000 | 20/17 × 0.992 = 1.167059 | 0.992000000 | 99.2% |
| HARD (5) | 15/20 = 0.750000 | 20/15 × 0.992 = 1.322667 | 0.992000000 | 99.2% |
| EXPERT (10) | 10/20 = 0.500000 | 20/10 × 0.992 = 1.984000 | 0.992000000 | 99.2% |
Anti-Circularity Verification:
// Step 16: Anti-circularity — theoretical RTP// For each difficulty d (1–4) and each valid step count k (1..GRID_SIZE - m),// single-stop RTP at step k is:// RTP(d, k) = survivalProbability(m, k) × theoreticalMultiplier(m, k, edge)// = [C(20-m, k)/C(20, k)] × [(1-edge) × C(20, k)/C(20-m, k)]// = (1 - edge) = 0.992// Independent derivation: no casino-supplied data used.let maxDeviation = 0;let worstConfig = '';let combosTested = 0;for (const d of [1, 2, 3, 4] as const) { const m = DEATH_POINTS_BY_DIFFICULTY[d]; for (let k = 1; k <= GRID_SIZE - m; k++) { const surv = survivalProbability(m, k); const mult = theoreticalMultiplier(m, k, HOUSE_EDGE); const rtp = surv * mult; const dev = Math.abs(rtp - (1 - HOUSE_EDGE)); combosTested++; if (dev > maxDeviation) { maxDeviation = dev; worstConfig = `d=${d} (m=${m}), k=${k}`; } }}Why this proof is non-circular: winChance(m, k) and multiplier(m, k) are literally reciprocals of the same combinatorial ratio C(20, k) / C(20−m, k), scaled by the edge factor 0.992. They cancel exactly — no summation, no approximation, no "converges to". The identity holds by inspection for every (m, k) pair where k ≤ 20 − m, which means the 99.2% RTP is preserved regardless of how many tiles a player steps on before cashing out.
4.2House Edge Audit (Step 12)
The house edge is implemented by multiplying the no-edge payout multiplier by 0.992 (= 1 − 0.008). For each (mines m, step k) combination, the no-edge multiplier is C(20,k)/C(20−m,k) (pure probabilistic baseline), and the actual paid multiplier is C(20,k)/C(20−m,k) × 0.992. The × 0.992 factor is what produces the flat 0.8% house edge across all 4 difficulty-level configurations and all bet sizes. Step 8 verifies the formula against every winning bet; Step 7 confirms payouts reconcile to it.
Every bet response also carries an effective_edge field. All 6,000 primary bets in the captured dataset read 0.8, and a sample re-fetch of those bets still read 0.8 — expected, because Beef was advertised with a 0.8% house edge (99.2% RTP) at the time the bets were captured. Since capture, Duel has updated Beef's advertised RTP to 100%. On the other audited games, effective_edge is the operator's Zero Edge rakeback signal — tagged at settlement and updated asynchronously to 0 once a rewards queue processes the rebate — and the most reasonable assumption is that Beef now behaves the same way under the 100% advertised RTP. This audit did not capture bets after the RTP change, so that behaviour is untested here and the rakeback layer remains outside scope. What this audit certifies is the game-engine 0.8% house edge, which comes from the × 0.992 multiplier formula and is independent of the effective_edge field. See the audit scope exclusions for the rakeback layer.
C(20,k)/C(20−m,k) × 0.992 against every winning bet (Step 8), (ii) reconciling payouts to the formula (Step 7), and (iii) confirming the effective_edge field is not a game-logic input — it is constant at 0.8 across all 6,000 primary bets, and death-point sets and payouts derive entirely from the seed pair and the C(20,k)/C(20−m,k) × 0.992 multiplier formula, with no dependence on the field (Step 12). Flat across all 4 difficulty-level configurations — no scaling structure. RTP was 99.2% across the captured dataset, the figure Beef was advertised at when the bets were captured. Duel has since updated Beef's advertised RTP to 100%; the operator-side rakeback layer that would bring net edge to 0% was not exercised by this capture and is outside the audit's scope.4.3Full RTP Table — All 4 Configurations
All 4 difficulty-level configurations produce the same theoretical RTP of 99.200%. The simulated RTP varies per config due to sampling variance, particularly for high-difficulty configurations where the rare but large winning multiplier dominates the RTP calculation.
| Config | Theoretical RTP | Simulated RTP | Deviation |
|---|---|---|---|
| EASY (m=1) | 99.200% | 99.194% | −0.006% |
| MEDIUM (m=3) | 99.200% | 99.161% | −0.039% |
| HARD (m=5) | 99.200% | 99.148% | −0.052% |
| EXPERT (m=10) | 99.200% | 99.084% | −0.116% |
4.4Simulation Pass 1 — Fresh Seeds (Step 18)
Section 4.1 proves RTP = 99.2% mathematically. But does the game engine actually produce that in practice? To find out, we simulated 4 million rounds locally using the same RNG algorithm and independent auditor-generated seeds. If the simulated payouts converge on 99.2%, the implementation matches the math.
Chi-squared test: Compares observed death-point frequencies to expected uniform frequencies across the 20 grid positions. 0/4 fail at uncorrected α=0.01. 0/4 fail at Bonferroni α/4 = 0.0025.
Serial independence: Lag-1 autocorrelation measures correlation between consecutive outcome-sequence values. Runs test checks for non-random run structure. 0/4 configs fail either test.
RTP convergence: Avg simulated RTP = 99.147% vs 99.200% theoretical. Deviation of −0.053% is well within expected sampling variance at this sample size.
// Pass 1 — Fresh random seeds// 1,000,000 rounds × 4 difficulty configs = 4,000,000 total// Per-config pinned seeds for reproducibility (S7)const difficulty = DIFFICULTIES[ci];const dpc = DEATH_POINTS_BY_DIFFICULTY[difficulty];const theoWin = survivalProbability(dpc, 1); // P(safe step 1) = (20 - m) / 20const mult = theoreticalMultiplier(dpc, 1, HOUSE_EDGE);const theoRTP = theoWin * mult; // should be 0.992 const seedPair = SIM_SEEDS[ci];const keyBuffer = Buffer.from(seedPair.server, 'hex'); for (let nonce = 0; nonce < ROUNDS_PER_CONFIG; nonce++) { const deaths = computeDeathPointsFromBuffer(keyBuffer, seedPair.client, nonce, dpc); for (const pos of deaths) positionFreq[pos]++; const revealTile = nonce % GRID_SIZE; const deathSet = new Set(deaths); const won = !deathSet.has(revealTile); if (won) { totalWins++; totalPayout += mult; } winSequence[nonce] = won ? 1 : 0;}What is a Monte Carlo simulation? Instead of proving fairness with algebra alone, we simulate millions of real game rounds. Each round computes a death-point set from scratch using the same HMAC-SHA256 backward Fisher-Yates pipeline as the live game, steps on a tile, and records whether the bet won and what it paid. We record payouts, then compare the aggregate return to the theoretical 99.2%. If they match, the math holds in practice — not just on paper.
4.5Cherry-Pick Detection — Pass 2 (Step 19)
Could the casino have chosen server seeds that produce worse outcomes for players? Pass 2 takes every server seed the casino actually used in the primary dataset and simulates 10,000 rounds per seed at a representative difficulty (MEDIUM, m=3) to check whether any of them are statistically biased against players.
Test A — Overall distribution: Does any individual seed produce a win-rate distribution across 10,000 nonces that deviates from the expected 85% binomial? 0/121 fail at α=0.01 — well under the ⌈N×0.01⌉=2 threshold. Binomial p-value for the aggregate: 1.000 (no signal).
Test B — Early vs late window: Does any seed produce statistically better outcomes in the early nonces (0–49, where real players bet) compared to later nonces (50–9,999)? 4/121 flags, all early-only (no seed shows late-window deviation). Threshold is 2×⌈N×0.05⌉=14 flags, so 4 passes with substantial headroom. Binomial p-value for the aggregate: 0.860 (no signal).
| Test | Result |
|---|---|
| Seeds tested | 121 (primary-dataset revealed seeds) |
| Nonces per seed | 10,000 |
| Difficulty used | MEDIUM (m=3, ~85% win chance — above chi-squared minimum) |
| Test A fails (chi² at α=0.01) | 0 / 121 PASS (threshold ≤2; binomial p=1.000) |
| Test B cherry-pick flags | 4 / 121 PASS (threshold ≤14 = 2×⌈N×0.05⌉; expected ~6.0 under H₀) |
| Broad flags (early AND late deviate) | 0 / 121 PASS (any broad flag = investigate) |
// Step 19: Pass 2 Cherry-Pick Testconst pass2 = sim.pass2_casino_seeds;const N = pass2.seeds_tested;const flags = pass2.test_b_cherry_pick_flags;const testA = pass2.test_a_chi2_fails_at_alpha01;const expCP = Math.ceil(N * 0.05);const threshold = expCP * 2; let broadFlags = 0;let earlyOnly = 0;for (const r of pass2.results) { if (r.cherry_pick_flag) { if (r.earlyP < 0.05 && r.lateP < 0.05) broadFlags++; else earlyOnly++; }} const verdict = flags <= threshold && broadFlags === 0 ? 'PASS' : 'FLAG';4.6Bet-Size Invariance (Step 10)
Phase C placed 200 bets at $10 on MEDIUM difficulty (m=3) — the same configuration tested at $0.01 elsewhere in the dataset. All 200 death-point layouts were recomputed correctly from revealed seeds using the same HMAC-SHA256 backward Fisher-Yates path. All 165 winning bets' multipliers matched the same C(20,k) / C(20−m,k) × 0.992 formula applied to $0.01 bets. Bet amount is not an input to the RNG and does not affect the death-point distribution.
| Metric | Phase A ($0.01) | Phase C ($10) |
|---|---|---|
| Bets | 4,000 (all 4 difficulties, 1,000 per config) | 200 (MEDIUM, m=3) |
| Bet amount | $0.01 | $10.00 |
| Death-point recomputation | 4,000 / 4,000 | 200 / 200 |
| Multiplier formula | C(20,k)/C(20−m,k) × 0.992 | C(20,k)/C(20−m,k) × 0.992 |
| RNG path | HMAC-SHA256 Fisher-Yates | HMAC-SHA256 Fisher-Yates |
4.7Informational Items (Not Scored)
These items are reported for transparency but are not scored audit steps. They provide context on the empirical RTP observed during data collection. At the per-phase sample sizes in this audit, empirical RTP is not a meaningful measure of fairness — the anti-circularity proof in 4.1 is the authoritative evidence. Expect large per-phase deviations; any RTP test at N ≤ 5,000 is underpowered for Beef's variance envelope.
| Item | Value | Context |
|---|---|---|
| Phase A empirical RTP | 99.088% | 4,000 bets at $0.01 (4 difficulties, 1,000/config) — broadest coverage |
| Phase B empirical RTP | 101.978% | 1,000 bets at $0.01 (EXPERT, m=10) — max-variance edge case |
| Phase C empirical RTP | 96.282% | 200 bets at $10 (MEDIUM, m=3) — elevated stake |
| Phase D empirical RTP | 98.630% | 800 bets at $0.01 (random difficulty) — 16 custom client seeds |
| Phase E empirical RTP | 108.650% | 450 multi-step bets at $0.01 across all 4 difficulties, k ∈ {2, 3, 5} |
4.8Worked Example — Payout Verification
Real bet from Phase E1 — Round ID 7843993, EASY (m=1), nonce 0, 5 safe steps cashed out at k=5. Verified from beef-phaseE-450bets.json:
serverSeed       = 414cf32bb0d5412e2e1f42fa304f4b45601e9715074ed2d436d8569ccaed5844
clientSeed       = zqpIvz4yp068AeIU
nonce            = 0
difficulty_level = 1 (EASY, m=1)
steps            = [0, 1, 2, 3, 4]
k                = 5
Step 1 — Death-point computation: computeDeathPoints(serverSeed, clientSeed, 0, 1) → 19 Fisher-Yates steps → death-point SET = {6}
Step 2 — Win check: Player stepped on tiles [0, 1, 2, 3, 4]. None are in {6} → win at k=5
Step 3 — Multiplier derivation: C(20, 5) / C(20−1, 5) × 0.992 = 15504/11628 × 0.992 = 1.322667×
Step 4 — Payout: 0.01 × 1.322667 = 0.013227
| Step | Process | Output |
|---|---|---|
| 1 | Backward Fisher-Yates: 19 HMAC calls | death-point SET = {6} ✅ |
| 2 | Win check: all stepped tiles ∈ death-point set? | {0,1,2,3,4} ∩ {6} = ∅ → win |
| 3 | Multiplier: C(20,5)/C(19,5) × 0.992 | 1.322667× |
| 4 | RTP check: winChance × multiplier | C(19,5)/C(20,5) × C(20,5)/C(19,5) × 0.992 = 0.992 |
| 5 | Payout: 0.01 × 1.322667 | 0.013227 ✅ |
// EASY (m=1), k=5 — anti-circularity proof// winChance(1, 5) = C(19,5) / C(20,5) = 11628/15504 = 0.75 (survive 5 steps)// multiplier(1, 5, 0.008) = C(20,5) / C(19,5) × 0.992 = 15504/11628 × 0.992 = 1.322667 // RTP = winChance × multiplier// = 0.75 × 1.322667// = 0.992000000 (99.2%) ✅ // Algebraic cancellation (exact, not an estimate):// C(20-m, k) / C(20, k) × C(20, k) / C(20-m, k) × 0.992// = 1 × 0.992// = 0.992Technical Evidence & Verification5 sections
4.9Evidence Coverage Summary7 checks
| Verification Area | Coverage | Result |
|---|---|---|
| Anti-circularity (Step 16) | 4 difficulties × 61 valid (m, k) combos — RTP = 99.2% exactly (max deviation 2.22 × 10⁻¹⁶) | Pass |
| House edge audit (Step 12) | Derived from × 0.992 factor in multiplier formula — verified against 6,000 winning bets (Step 8) | Pass |
| Multiplier formula (Step 8) | 4,337 winning bets + 1,085 multi-step pairs | Pass |
| Simulation Pass 1 (Step 18) | 4M rounds, 0/4 chi-squared, 0/4 serial | Pass |
| Simulation Pass 2 (Step 19) | 121 seeds, Test A 0/121, Test B 4/121, 0 broad | Pass |
| Bet-size invariance (Step 10) | 200 / 200 Phase C at $10 | Pass |
| Multi-step RTP preservation (Steps 20, 22) | 1,085 step-multiplier pairs + 202 cash-outs across k ∈ {2, 3, 5} | Pass |
4.10Code References7 source files
| File | Purpose |
|---|---|
| tests/steps/dataset.ts | Step 16: Anti-circularity proof (algebraic identity) |
| tests/steps/payouts.ts | Steps 8, 10, 12: Multiplier formula, bet-size invariance, house-edge audit |
| tests/steps/simulation.ts | Steps 18–19: Simulation integrity and cherry-pick detection |
| tests/steps/multireveal.ts | Steps 20, 22: Multi-step multiplier chain, cash-out payout correctness |
| src/simulate.ts | Monte Carlo simulation (4M rounds, two-pass) |
| src/stats.ts | chiSquaredTest, lag1Autocorrelation, runsTest |
| src/rng.ts | theoreticalMultiplier, survivalProbability — closed-form formulas |
4.11Datasets UsedSource artifacts
4.12Verified Invariants12 invariants
| Invariant | Result |
|---|---|
| winChance × multiplier = 0.992 for all 4 difficulty levels at k=1 (non-circular) | Pass |
| Identity extends to all valid k > 1 by the same cancellation (61 combos total) | Pass |
Flat 0.8% house edge — derived from × 0.992 factor in C(20,k)/C(20−m,k) × 0.992; effective_edge field is not a game-logic input — constant at 0.8 across all 6,000 primary bets, no dependence on the field | Pass |
| Formula C(20,k) / C(20−m,k) × 0.992 matches all 4,337 winning-bet multipliers | Pass |
| Operator payout table (61 entries) matches closed-form formula (max deviation 4.55 × 10⁻¹³) | Pass |
| Simulated RTP average = 99.147% across 4M rounds | Pass |
| 0/4 configs reject at Bonferroni α/4 = 0.0025 | Pass |
| 0 serial independence failures (lag-1 + runs test) | Pass |
| No evidence of seed pre-selection across 121 casino seeds (Pass 2) | Pass |
| Phase C ($10) death-point sets match Phase A ($0.01) algorithm | Pass |
| Bet amount absent from RNG input by construction | Pass |
| Multi-step RTP preserved at k ∈ {1..5} (1,085 pairs, 202 cash-outs) | Pass |
4.13Reproduction InstructionsRun locally
git clone https://github.com/ProvablyFair-org/duel-beef.gitcd duel-beef && npm installnpm run simulate # 4M simulation + cherry-pick test (~90 sec)npm run verify # Steps 8, 10, 12, 16, 18, 19, 20, 22 cover S4cat outputs/simulation-results.jsonS4-related steps:
[PASS] Step 8 — Multiplier Formula (C(20,k)/C(20−m,k) × edge)
[PASS] Step 10 — Phase C Bet-Size Invariance ($10 bets)
[PASS] Step 12 — House Edge Audit (effective_edge = 0.8%)
[PASS] Step 16 — Probability Independence (Anti-Circularity)
[PASS] Step 18 — Simulation Results — Pass 1 Integrity
[PASS] Step 19 — Simulation Results — Pass 2 Cherry-Pick Test
[PASS] Step 20 — Multi-Step Multiplier Chain (Phase E)
[PASS] Step 22 — Cash-Out Payout Correctness (k>1)Fairness Integrity Testing
Does the implementation maintain fairness under non-standard conditions?
Sections 1–4 prove the game is mathematically fair. Section 5 proves the implementation maintains integrity under non-standard conditions. We applied 16 fairness integrity tests covering nonce integrity, seed commitment, outcome determinism, cross-player isolation, and payout integrity (including Beef-specific multi-step game-state checks). All 16 tests passed, including one Beef-specific multi-step state integrity test.

Fairness Integrity Testing
What we verified
- Nonce tampering — can the sequence be forced, replayed, or skipped?
- Seed injection — can server or client seed fields be overridden via API?
- Outcome replay — can a completed bet be replayed for duplicate payouts?
- Cross-player isolation — can one player's seeds or outcomes affect another's?
- Payout tampering — can multiplier or payout values be injected client-side?
- Parameter limits — can invalid difficulty levels or grid sizes be submitted?
- Beef-specific — can the same tile be stepped on twice to advance the multiplier?
What this means for you
- Across the 16 tests we ran, no API path allowed outcomes to be altered, replayed, or injected — by player or casino
- Once a bet is placed, the death-point layout cannot be changed or replayed
- Each bet is cryptographically unique and isolated
- Your results are independent of every other player
- The server rejects malformed, out-of-range, and duplicate requests
- Nonce tampering — can the sequence be forced, replayed, or skipped?
- Seed injection — can server or client seed fields be overridden via API?
- Outcome replay — can a completed bet be replayed for duplicate payouts?
- Cross-player isolation — can one player's seeds or outcomes affect another's?
- Payout tampering — can multiplier or payout values be injected client-side?
- Parameter limits — can invalid difficulty levels or grid sizes be submitted?
- Beef-specific — can the same tile be stepped on twice to advance the multiplier?
- Across the 16 tests we ran, no API path allowed outcomes to be altered, replayed, or injected — by player or casino
- Once a bet is placed, the death-point layout cannot be changed or replayed
- Each bet is cryptographically unique and isolated
- Your results are independent of every other player
- The server rejects malformed, out-of-range, and duplicate requests
Nonce integrityPass
Seed commitment integrityPass
Outcome determinismPass
Round & player isolationPass
Payout integrityPass
16 fairness integrity tests: all 16 pass, including one Beef-specific multi-step state integrity test.
Category Coverage


| Check | Result | Evidence |
|---|---|---|
| Nonce integrity | Pass | Sequential, server-controlled, no duplicates across 121 primary epochs (1 capture-retry gap reconstructed from revealed seed) |
| Seed commitment integrity | Pass | Locked at bet acceptance, unique per epoch — 121/121 primary epochs verified |
| Outcome determinism | Pass | Identical inputs produce identical death-point sets — 6,450/6,450 confirmed including multi-step |
| Round & player isolation | Pass | Per-user seeds, serial independence confirmed (0/4 fail in 4M-round simulation) |
| Payout integrity | Pass | Parameter limits enforced (4/4 invalid difficulty rejected); injected payout fields ignored (0 honoured); post-settlement step injection blocked |
Nonce integrityPass
Seed commitment integrityPass
Outcome determinismPass
Round & player isolationPass
Payout integrityPass
16 fairness integrity tests: all 16 pass, including one Beef-specific multi-step state integrity test.
How It Works — Fairness Integrity Testing2 sections
5.1Framework Overview
Testing follows the ProvablyFair.org Fairness Integrity Framework — a structured methodology derived from real, historically observed failures in provably fair systems. Five categories target specific fairness properties, with Payout Integrity extended to cover Beef's multi-step reveal and cash-out surface. Scope boundary: S5 tests whether fairness guarantees hold under non-standard API interaction. Platform-level implementation testing falls outside standard certification.
| Category | Tests | What It Catches |
|---|---|---|
| Nonce Integrity | 4 | Sequence gaps, server-side nonce manipulation, session continuity |
| Seed Commitment | 5 | Mid-epoch seed changes, seed reuse, predictable seed generation |
| Outcome Determinism | 2 | Non-deterministic outputs, outcome replay, cash-out manipulation |
| Player Isolation | 2 | Cross-round correlation, cross-user outcome dependence |
| Payout Integrity | 3 | Parameter enforcement, server-side computation, duplicate-step idempotency |
5.2Severity Framework & Hard Fail Criteria
Findings are classified by severity. Hard fail criteria — any one triggers a NOT PROVABLY FAIR verdict.
| Severity | Meaning | Action |
|---|---|---|
| PASS | Test passed — no issue detected | None |
| N/A | Test not applicable to this game type | None |
| FLAG | Anomaly detected, documented for transparency | Disclosed |
| HARD FAIL | Fairness guarantee cannot be confirmed | Certification blocked until remediated |
| Condition | Consequence |
|---|---|
| Nonce gap or duplicate within epoch | Outcome sequence integrity broken |
| Server seed changed mid-epoch | Commit-reveal guarantee broken |
| Death-point recomputation mismatch | Undisclosed inputs affecting placement |
| Client seed not used in HMAC | Player has no influence on outcomes |
| Death-point set changes during step sequence | Per-step manipulation possible |
| Duplicate step advances payout multiplier | Multi-step state corruption |
16 tests · 16 pass
Nonce Integrity4/4
FI-NONCE-001PassEach bet increments the nonce sequentially with no gaps, repeats, or resets — preventing the server from skipping unfavourable outcomes
FI-NONCE-002PassNonce progression is server-controlled — the client cannot inject, skip, or replay a nonce value via the API
S1, Step 4 — server controls nonce assignment. Client bet requests do not include a nonce field.
FI-NONCE-003PassSubmitting an invalid or out-of-sequence nonce does not produce a game outcome — the server rejects the request
API probe — 7 adversarial nonce values (−1, 0, 999999999, 'abc', INT32_MAX, INT32_MAX+1, 9e18) injected into beef-start requests. All 7 silently ignored; server assigned valid sequential nonces. Continuity preserved (baseline 9 → post-test 17); no stack traces leaked.
FI-NONCE-004PassNonce sequence continues correctly after disconnect/reconnect — no reset to zero mid-epoch
Seed Commitment5/5
FI-SEED-001PassEmpty, null, or invalid client seeds are handled deterministically — the server enforces input requirements
API probe — 6/7 invalid client seeds rejected (empty, null, special chars, emoji, CJK, whitespace-only). Oversized seed (>1000 chars) accepted — permissive but safe (long entropy). All Beef bets after each rejection remained functional; no stack traces leaked.
FI-SEED-002PassOnce a bet is accepted, the seed pair is locked for the epoch — no mid-epoch mutation of server or client seed is possible
FI-SEED-003PassEach epoch uses a unique server seed — no seed is reused across epochs or sessions
FI-SEED-004PassNo shared seed pool across users — each player's seeds are independently generated and isolated
API probe — 10 concurrent seed rotations on Account A and 10 on Account B. Zero hash collisions across 20 rotations; all hashes within each account distinct. Full account isolation confirmed.
FI-SEED-005PassServer seeds show no correlation with timestamps, sequential patterns, or other predictable inputs
API probe — 10 rotations spaced 5 seconds apart over ~51 seconds. All 10 server seed hashes distinct; no two shared 6+ leading hex characters. Time-correlated derivation ruled out.
Outcome Determinism2/2
FI-OUTCOME-001PassGiven identical inputs (serverSeed, clientSeed, nonce, difficultyLevel), the game always produces the same death-point set — verified across all 6,450 live bets including 450 multi-step bets with target_k ∈ {2, 3, 5} across all 4 difficulties
FI-OUTCOME-002PassA completed bet cannot be replayed to generate a duplicate payout — death-point set is cryptographically fixed at bet time and cash-out payouts are deterministically bound to the formula
Player Isolation2/2
FI-ISO-001PassRNG state is fully independent across rounds — no carry-over from one bet to the next. Each nonce produces a fresh HMAC-SHA256 computation
FI-ISO-002PassOne player's seeds, nonces, and outcomes cannot be observed or influenced by another player — complete cross-user isolation
Follows from seed uniqueness (FI-SEED-003) — if each user has a unique server seed, outcomes are isolated by construction. Confirmed by FI-SEED-004 — zero hash collisions across 20 cross-account rotations.
Payout Integrity3/3
FI-PAYOUT-001PassGame parameters cannot exceed defined limits — only valid difficulty levels (1–4) and the 20-tile grid are accepted
API probe — 4/4 invalid difficulty values rejected with HTTP 422 (0, −1, 9999, 'abc'). Both valid controls (difficulty=1, 2) and recovery bet accepted. No out-of-range values silently coerced.
FI-PAYOUT-002PassMultiplier and payout fields in the API request are ignored — the server computes all values from the combinatorial formula, not from client-supplied values
API probe — 6 injected fields (multiplier='9999', mines_positions, is_win, win_amount, payout_multiplier, death_points) all silently ignored. Server computed death point positions and payout values independently from the seed pair on every request. noInjectionHonoured=true.
FI-BEEF-STATE-001PassStepping on the same grid position twice does not advance the payout multiplier — the server must reject duplicate steps or return an idempotent response (Beef-specific multi-step state integrity)
API probe — game started, first step taken (multiplier 1.0526…), round cashed out, then a step request targeting the now-settled round rejected with HTTP 404. Multiplier did not advance from first-step value; no double-step vulnerability observed. multiplierAdvanced=false.
Technical Evidence & Verification4 sections
5.3Coverage Summary16 checks
| Test ID | Category | Verification Source | Status |
|---|---|---|---|
| FI-NONCE-001 | Nonce | S1, Step 4 (data-driven) | Pass |
| FI-NONCE-002 | Nonce | S1, Step 4 (data-driven) | Pass |
| FI-NONCE-003 | Nonce | API probe | Pass |
| FI-NONCE-004 | Nonce | S1, Step 4 (data-driven) | Pass |
| FI-SEED-001 | Seed | API probe | Pass |
| FI-SEED-002 | Seed | S1, Steps 3 & 6 (data-driven) | Pass |
| FI-SEED-003 | Seed | S1, Step 1 (data-driven) | Pass |
| FI-SEED-004 | Seed | API probe | Pass |
| FI-SEED-005 | Seed | API probe | Pass |
| FI-OUTCOME-001 | Determinism | S3, Steps 5 & 21 (data-driven) | Pass |
| FI-OUTCOME-002 | Determinism | S3, Steps 21 & 22 (data-driven) | Pass |
| FI-ISO-001 | Isolation | S2, Step 18 (simulation) | Pass |
| FI-ISO-002 | Isolation | Structural — seed uniqueness | Pass |
| FI-PAYOUT-001 | Payout | API probe | Pass |
| FI-PAYOUT-002 | Payout | API probe | Pass |
| FI-BEEF-STATE-001 | Payout | API probe | Pass |
5.4Additional Integrity Evidence (S1–S4)8 records
| Property | Source | Finding |
|---|---|---|
| 121/121 seed hashes verified | S1, Step 1 | Commit-reveal chain intact |
| 125/125 next-seed promotions | S1, Step 2 | Seed rotation chain intact |
| 6,000/6,000 exact parity (primary) + 450/450 Phase E | S3, Steps 5 & 21 | No post-RNG conditional logic, death-point set fixed at round start |
| Anti-circularity proven (algebraic) | S4, Step 16 | 0.8% house edge from first principles |
| 4 cherry-pick flags / 121 seeds (0 broad) | S4, Step 19 (Pass 2) | No seed pre-selection bias |
| 99.3% client seed influence (597/601) | S1, Step 6 | Player entropy is genuine |
| 202 cash-outs verified at k ∈ {2, 3, 5} | S3, Step 22 | Multi-step payout integrity intact |
| 1,085 step-multiplier pairs verified across 15 (difficulty, k) combos | S3, Step 20 | Multi-step multiplier chain correct |
5.5Scope & LimitationsScope note

5.6Reproduction InstructionsRun locally
Data-driven tests (9 of 16): Fully reproducible from the open-source repo. These tests run against the captured dataset and produce deterministic results.
API probe tests (7 of 16): Verified by issuing live adversarial requests against the running game. Per-test evidence (HTTP status codes, server-assigned nonces, seed hashes, server-computed multipliers, death-point decisions) is retained in our private adversarial-testing archive and summarised in the integrity test review document. The testing harness itself is kept private to avoid handing exploit primitives to players.
git clone https://github.com/ProvablyFair-org/duel-beef.gitcd duel-beefnpm installnpm run verifyExpected output (S5-related steps):
[PASS] Step 1 — Seed Hash Integrity → FI-SEED-003
[PASS] Step 3 — Hash Consistency Within Epoch → FI-SEED-002
[PASS] Step 4 — Nonce Audit → FI-NONCE-001, 002, 004
[PASS] Step 5 — Outcome Recomputation (Death Pts)→ FI-OUTCOME-001
[PASS] Step 6 — Client Seed Influence → FI-SEED-002
[PASS] Step 18 — Simulation Pass 1 → FI-ISO-001
[PASS] Step 20 — Multi-Step Multiplier Chain → FI-OUTCOME-001 (multi-step)
[PASS] Step 21 — Death-Point Recomputation (E) → FI-OUTCOME-001, 002
[PASS] Step 22 — Cash-Out Payout Correctness (k>1)→ FI-OUTCOME-002API Probe Tests (completed):
[PASS] FI-NONCE-003 — Invalid nonce handling → 7/7 invalid nonces ignored (HTTP 200)[PASS] FI-SEED-001 — Invalid client seed handling → 6/7 rejected; oversized accepted[PASS] FI-SEED-004 — Cross-user seed pool check → 0/20 collisions across 2 accounts[PASS] FI-SEED-005 — Seed timing analysis → 10 distinct hashes, no time correlation[PASS] FI-PAYOUT-001 — Invalid difficulty handling → 4/4 boundary violations rejected (HTTP 422)[PASS] FI-PAYOUT-002 — Field injection handling → 0 injections honoured[PASS] FI-BEEF-STATE-001 — Post-settlement step probe → step on settled round rejected (HTTP 404)Player Verification
Can a player verify their own bets without trusting anyone?
Every Beef outcome can be independently reproduced using publicly disclosed inputs. No hidden variables, no private backend data. If your calculated death-point layout matches the game result, the bet was provably fair. This section walks you through the process — and provides an independent verification tool built from the same code used in this audit.
Independent Result Verification
Key principles
- Every Beef outcome can be independently reproduced
- No hidden variables — no private backend data
- If your computed death-point SET matches the game result, the bet was provably fair
- Most players can verify directly through the Duel.com fairness UI
What you need
- Server Seed — revealed after seed rotation (casino entropy)
- Client Seed — your player-controlled seed
- Nonce — the bet number in sequence (ensures uniqueness; increments within each epoch)
- Difficulty Level — the difficulty you chose for the round (EASY, MEDIUM, HARD, or EXPERT). Higher difficulty means more obstacles and higher payouts per step survived.
- Every Beef outcome can be independently reproduced
- No hidden variables — no private backend data
- If your computed death-point SET matches the game result, the bet was provably fair
- Most players can verify directly through the Duel.com fairness UI
- Server Seed — revealed after seed rotation (casino entropy)
- Client Seed — your player-controlled seed
- Nonce — the bet number in sequence (ensures uniqueness; increments within each epoch)
- Difficulty Level — the difficulty you chose for the round (EASY, MEDIUM, HARD, or EXPERT). Higher difficulty means more obstacles and higher payouts per step survived.
Player can access all required inputsPass
Client seed origin transparentPass
Verification process documentedPass
Casino UI exposes verification panelPass
Independent verifier availablePass
Manual recomputation possiblePass
No hidden or proprietary stepsPass
Only disclosed inputs are used. Identical inputs always produce identical output.
- 1
Place a Beef Bet
Choose your difficulty level (EASY, MEDIUM, HARD, or EXPERT) and place a bet. The platform locks the death-point layout for the lane ahead using the provably fair algorithm before you take a step.
- 2
Open the Fairness Modal
Open the Provably Fair modal on the game page. You'll see the active client seed, the hashed server seed, and your current nonce. Rotate the seed pair to unlock the revealed plaintext server seed for your previous bets.
- 3
Open Past Bet to Reveal Seed
Open Transactions and click a past Beef round. The per-bet modal shows the revealed plaintext server seed alongside the bet ID, client seed, and nonce.
- 4
Recompute & Confirm
Click Verify in the per-bet modal to open the Provably Fair page with the seeds pre-populated. The page recomputes the death-point sequence inline as step-by-step multipliers — if the sequence matches your live game result, the bet was provably fair.
Verify a real bet, step by stepVerify a real bet · Swipe for all 4 steps →
Verify with the audit code
Independent verification using the implementation behind this report.
Open independent verifier
Built-in verification
The operator’s own verification page. This tool is controlled by Duel.com.
Open Duel verifier
Visual Walkthroughstep-by-step

Choose your difficulty level (EASY, MEDIUM, HARD, or EXPERT) and place a bet. The platform locks the death-point layout for the lane ahead using the provably fair backward Fisher-Yates shuffle. The server has already committed to the outcome before you clicked — you just don't know where the death points are until you step on a tile.
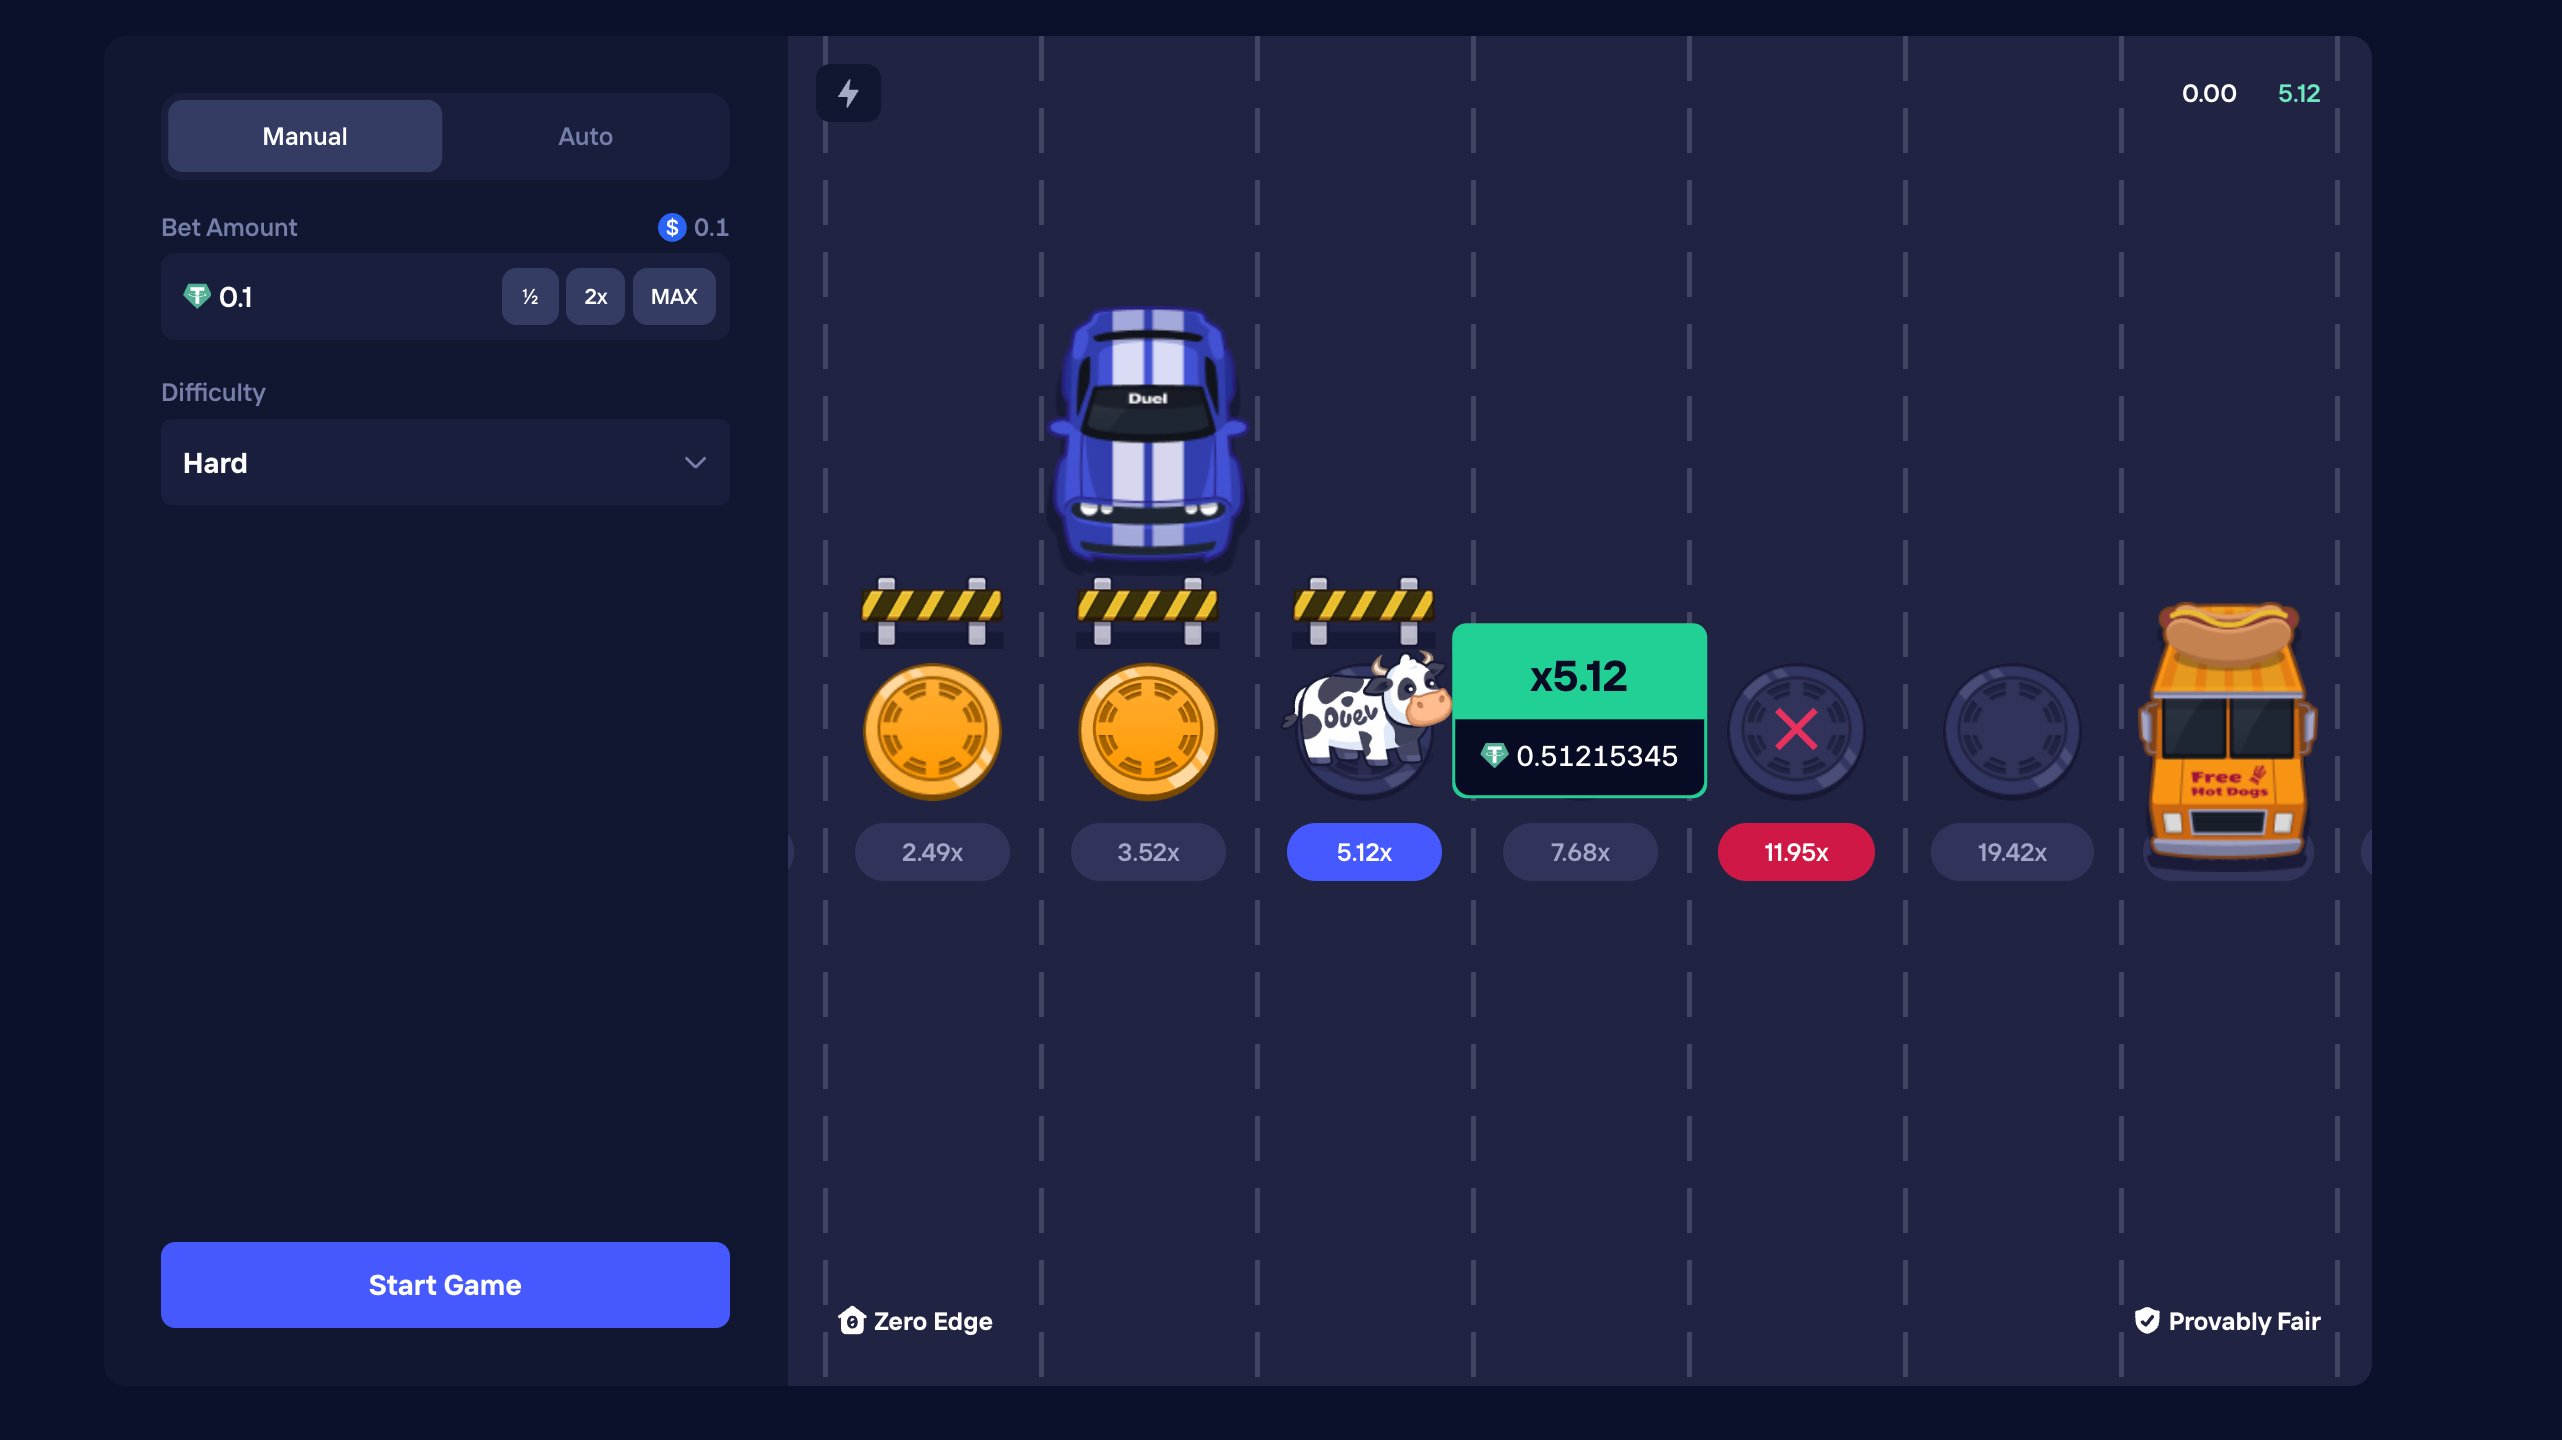
Duel.com Beef — lane with difficulty selector and step multipliers. Death-point placement is locked before you take a step.
Open the Provably Fair modal on the game page. You'll see the active client seed, the hashed server seed (the casino's pre-commitment), and your current nonce. Below those, you can set the new client seed that will become active after rotation. Click 'Rotate seed' to retire the active seed pair and start a new one — this is what unlocks the revealed plaintext server seed for your previous bets in Step 3.
Provably Fair modal — active client seed, hashed server seed, nonce, customisable new client seed, next pair pre-commitment, and Rotate seed action.
Open Transactions and click a past Beef round. The per-bet modal shows the revealed plaintext server seed alongside the bet ID, client seed, and nonce. The pre-committed hash from Step 2 must match SHA-256 of this revealed seed:
Server Seed (revealed) — plaintext value the casino committed to before your bet. Hash it to confirm it matches the pre-commitment.
Client Seed — your player-controlled entropy input.
Nonce — the sequential bet counter for this seed pair.
Per-bet transaction modal — revealed plaintext server seed, client seed, and nonce for the round.
Click Verify in the per-bet modal to open the Provably Fair page with the seeds pre-populated. The page recomputes the death-point sequence from the disclosed inputs and renders the Game Result inline as the step-by-step multipliers, with the death point marked. If the recomputed sequence matches your live game result — the same multipliers up to the same death point — the bet was provably fair. The casino committed to the outcome before you bet, you contributed entropy via your client seed, and the result is mathematically reproducible by anyone.
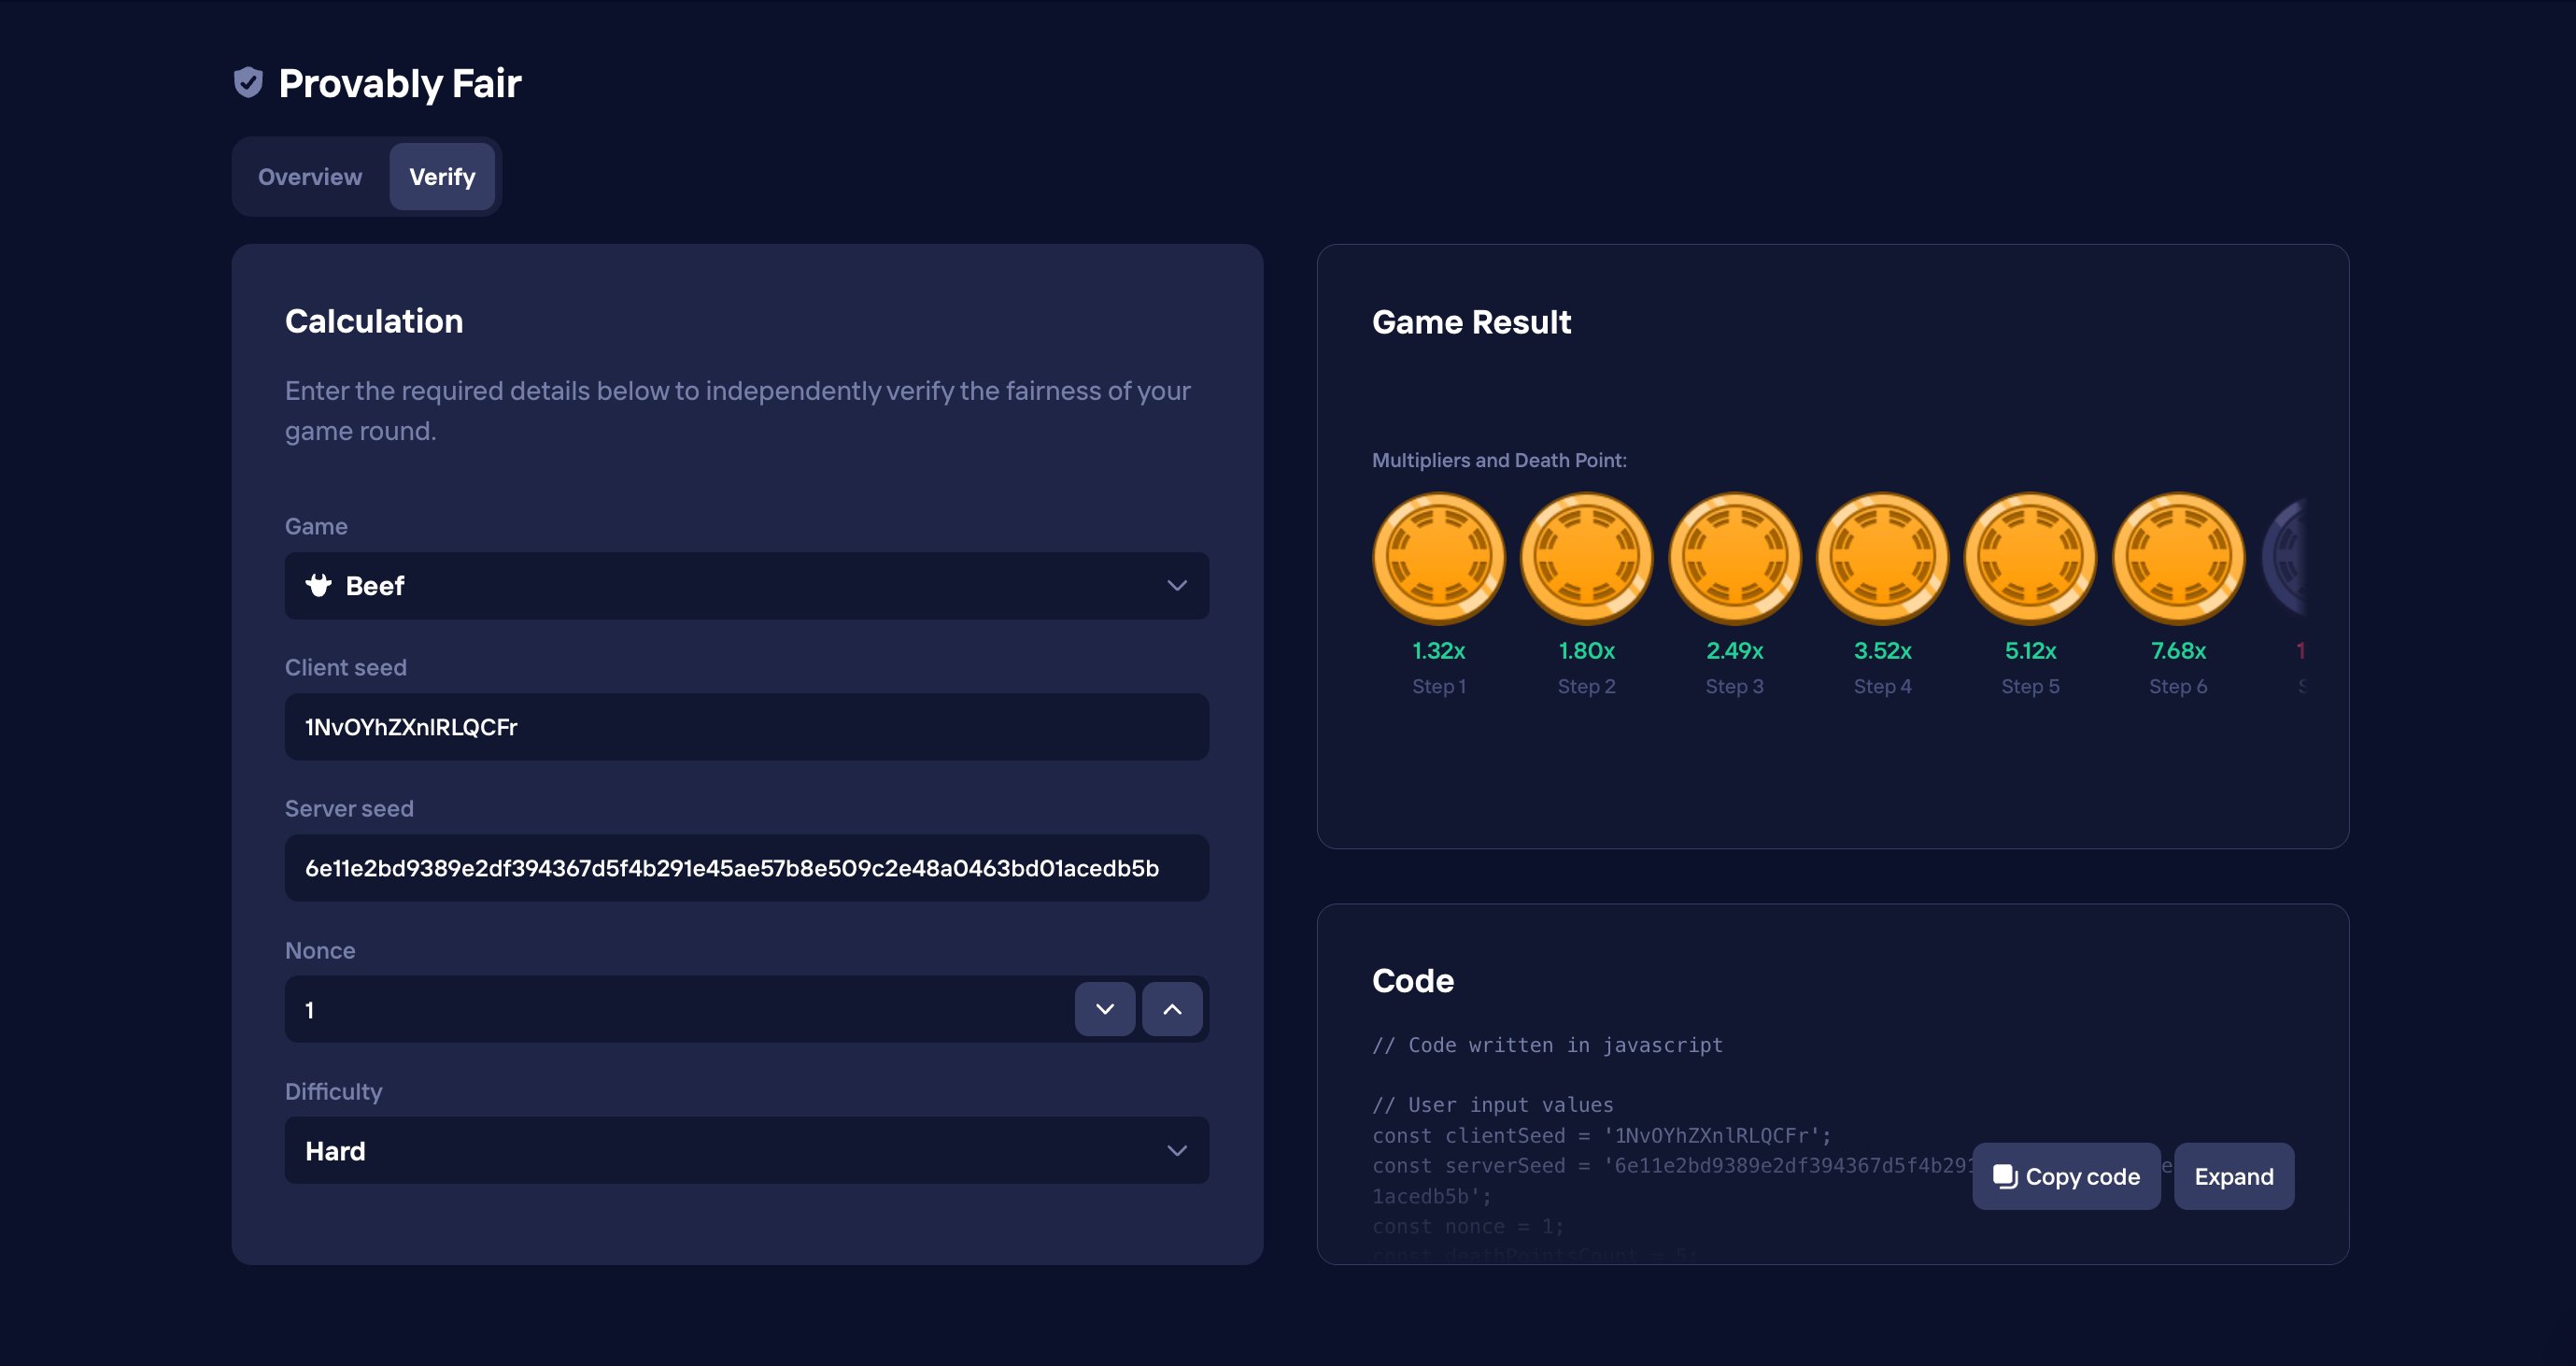
Provably Fair page — seeds populated from the per-bet modal, recomputed step multipliers and death point rendered inline matching the live game result.
Manual Verification (Advanced)6 sections
6.6Why Manual Verification Matters
True provably fair verification means you don't trust any casino-provided tool. Manual verification allows you to run calculations on your own machine, eliminate any possibility of a tampered verifier, and understand exactly how results are generated.
6.7How the Algorithm Works (Plain English)
Before you play, the server locks the death-point layout using four ingredients:
- The server's secret seed — committed by publishing its hash before you bet
- Your client seed — generated by your browser, unknown to the server
- The nonce — a counter that makes each bet unique
- The difficulty level — EASY, MEDIUM, HARD, or EXPERT (determines death-point count: 1, 3, 5, or 10)
These ingredients are combined with HMAC-SHA256 (a cryptographic function) to perform a backward Fisher-Yates shuffle of a 20-tile grid. The first N positions of the shuffled array — where N is the death-point count for your difficulty — become the death-point positions. Because the server committed to its seed before you bet, and your client seed is generated in your browser, neither party can predict or influence the outcome. Once the shuffle is done, the death-point layout is cryptographically locked — stepping on tiles in any order, or cashing out at any point, does not change which tiles are death points.
6.8Casino Verifier vs ProvablyFair.org Verifier4 records
Two verification tools are available. Both should produce identical results — if they don't, something has changed.
| Duel.com Verifier | ProvablyFair.org Verifier | |
|---|---|---|
| Source | Casino-controlled | Independent (audit codebase) |
| Access | duel.com/fairness/verify | audit.provablyfair.org/casino/duel/tools/verify-bets |
| Trust model | Requires trusting the casino | Open-source, version-controlled |
| Monitoring | No change detection | Mismatches detected if casino changes logic |
6.9JavaScript Verification Script
Copy and run this in Node.js to verify any Beef bet:
const crypto = require('crypto'); const GRID_SIZE = 20;const MAX_UINT32 = 0xFFFFFFFF; const DEATH_POINTS_BY_DIFFICULTY = { 1: 1, // EASY 2: 3, // MEDIUM 3: 5, // HARD 4: 10, // EXPERT}; function computeDeathPoints(serverSeed, clientSeed, nonce, difficultyLevel) { const deathPointsCount = DEATH_POINTS_BY_DIFFICULTY[difficultyLevel]; const key = Buffer.from(serverSeed, 'hex'); const positions = Array.from({ length: GRID_SIZE }, (_, i) => i); for (let i = GRID_SIZE - 1; i > 0; i--) { const range = i + 1; const maxFair = MAX_UINT32 - (MAX_UINT32 % range); let cursor = GRID_SIZE - 1 - i; while (true) { const message = `${clientSeed}:${nonce}:${cursor}`; const hmac = crypto.createHmac('sha256', key).update(message).digest('hex'); let found = false; for (let off = 0; off + 8 <= hmac.length; off += 8) { const value = parseInt(hmac.substring(off, off + 8), 16); if (value < maxFair) { const j = value % range; [positions[i], positions[j]] = [positions[j], positions[i]]; found = true; break; } } if (found) break; cursor++; } } return positions.slice(0, deathPointsCount).sort((a, b) => a - b);} function verifyHash(serverSeed, serverSeedHashed) { const hash = crypto .createHash('sha256') .update(Buffer.from(serverSeed, 'hex')) .digest('hex'); return hash === serverSeedHashed;} // Replace with your valuesconst serverSeed = 'YOUR_SERVER_SEED';const serverSeedHashed = 'YOUR_SERVER_SEED_HASH';const clientSeed = 'YOUR_CLIENT_SEED';const nonce = 0;const difficultyLevel = 2; // 1=EASY, 2=MEDIUM, 3=HARD, 4=EXPERT console.log('Hash check:', verifyHash(serverSeed, serverSeedHashed) ? 'PASS' : 'FAIL');console.log('Death points:', computeDeathPoints(serverSeed, clientSeed, nonce, difficultyLevel));6.10Python Verification Script
The same verification in Python (standard library only):
import hashlib, hmac GRID_SIZE = 20MAX_UINT32 = 0xFFFFFFFF DEATH_POINTS_BY_DIFFICULTY = { 1: 1, # EASY 2: 3, # MEDIUM 3: 5, # HARD 4: 10, # EXPERT} def compute_death_points(server_seed, client_seed, nonce, difficulty_level): death_points_count = DEATH_POINTS_BY_DIFFICULTY[difficulty_level] key = bytes.fromhex(server_seed) positions = list(range(GRID_SIZE)) for i in range(GRID_SIZE - 1, 0, -1): range_val = i + 1 max_fair = MAX_UINT32 - (MAX_UINT32 % range_val) cursor = GRID_SIZE - 1 - i while True: message = f'{client_seed}:{nonce}:{cursor}'.encode() h = hmac.new(key, message, hashlib.sha256).hexdigest() found = False for off in range(0, len(h) - 7, 8): value = int(h[off:off+8], 16) if value < max_fair: j = value % range_val positions[i], positions[j] = positions[j], positions[i] found = True break if found: break cursor += 1 return sorted(positions[:death_points_count]) def verify_hash(server_seed, server_seed_hashed): computed = hashlib.sha256(bytes.fromhex(server_seed)).hexdigest() return computed == server_seed_hashed # Replace with your valuesserver_seed = 'YOUR_SERVER_SEED'server_seed_hashed = 'YOUR_SERVER_SEED_HASH'client_seed = 'YOUR_CLIENT_SEED'nonce = 0difficulty_level = 2 # 1=EASY, 2=MEDIUM, 3=HARD, 4=EXPERT print('Hash check:', 'PASS' if verify_hash(server_seed, server_seed_hashed) else 'FAIL')print('Death points:', compute_death_points(server_seed, client_seed, nonce, difficulty_level))6.11Evidence Screenshots3 records
| Evidence | Description |
|---|---|
| E02 | Fairness page overview — "What is Provably Fair?" and "How it works" sections |
| E03 | Fairness verification tool — Beef selected, showing game-specific verification inputs (server seed, client seed, nonce, difficulty level) |
| E11 | Client seed rotation response — server echoes client-submitted seed, does not assign |
Verify a real bet, step by stepVerify a real bet · Swipe for all 4 steps →
How it works
- 1
Place a Beef Bet
Choose your difficulty level (EASY, MEDIUM, HARD, or EXPERT) and place a bet. The platform locks the death-point layout for the lane ahead using the provably fair algorithm before you take a step.
- 2
Open the Fairness Modal
Open the Provably Fair modal on the game page. You'll see the active client seed, the hashed server seed, and your current nonce. Rotate the seed pair to unlock the revealed plaintext server seed for your previous bets.
- 3
Open Past Bet to Reveal Seed
Open Transactions and click a past Beef round. The per-bet modal shows the revealed plaintext server seed alongside the bet ID, client seed, and nonce.
- 4
Recompute & Confirm
Click Verify in the per-bet modal to open the Provably Fair page with the seeds pre-populated. The page recomputes the death-point sequence inline as step-by-step multipliers — if the sequence matches your live game result, the bet was provably fair.
Visual Walkthroughstep-by-step
Choose your difficulty level (EASY, MEDIUM, HARD, or EXPERT) and place a bet. The platform locks the death-point layout for the lane ahead using the provably fair backward Fisher-Yates shuffle. The server has already committed to the outcome before you clicked — you just don't know where the death points are until you step on a tile.
Duel.com Beef — lane with difficulty selector and step multipliers. Death-point placement is locked before you take a step.
Open the Provably Fair modal on the game page. You'll see the active client seed, the hashed server seed (the casino's pre-commitment), and your current nonce. Below those, you can set the new client seed that will become active after rotation. Click 'Rotate seed' to retire the active seed pair and start a new one — this is what unlocks the revealed plaintext server seed for your previous bets in Step 3.
Provably Fair modal — active client seed, hashed server seed, nonce, customisable new client seed, next pair pre-commitment, and Rotate seed action.
Open Transactions and click a past Beef round. The per-bet modal shows the revealed plaintext server seed alongside the bet ID, client seed, and nonce. The pre-committed hash from Step 2 must match SHA-256 of this revealed seed:
Server Seed (revealed) — plaintext value the casino committed to before your bet. Hash it to confirm it matches the pre-commitment.
Client Seed — your player-controlled entropy input.
Nonce — the sequential bet counter for this seed pair.
Per-bet transaction modal — revealed plaintext server seed, client seed, and nonce for the round.
Click Verify in the per-bet modal to open the Provably Fair page with the seeds pre-populated. The page recomputes the death-point sequence from the disclosed inputs and renders the Game Result inline as the step-by-step multipliers, with the death point marked. If the recomputed sequence matches your live game result — the same multipliers up to the same death point — the bet was provably fair. The casino committed to the outcome before you bet, you contributed entropy via your client seed, and the result is mathematically reproducible by anyone.
Provably Fair page — seeds populated from the per-bet modal, recomputed step multipliers and death point rendered inline matching the live game result.
Technical evidence
6.6Why Manual Verification Matters
True provably fair verification means you don't trust any casino-provided tool. Manual verification allows you to run calculations on your own machine, eliminate any possibility of a tampered verifier, and understand exactly how results are generated.
6.7How the Algorithm Works (Plain English)
Before you play, the server locks the death-point layout using four ingredients:
- The server's secret seed — committed by publishing its hash before you bet
- Your client seed — generated by your browser, unknown to the server
- The nonce — a counter that makes each bet unique
- The difficulty level — EASY, MEDIUM, HARD, or EXPERT (determines death-point count: 1, 3, 5, or 10)
These ingredients are combined with HMAC-SHA256 (a cryptographic function) to perform a backward Fisher-Yates shuffle of a 20-tile grid. The first N positions of the shuffled array — where N is the death-point count for your difficulty — become the death-point positions. Because the server committed to its seed before you bet, and your client seed is generated in your browser, neither party can predict or influence the outcome. Once the shuffle is done, the death-point layout is cryptographically locked — stepping on tiles in any order, or cashing out at any point, does not change which tiles are death points.
6.8Casino Verifier vs ProvablyFair.org Verifier4 records
Two verification tools are available. Both should produce identical results — if they don't, something has changed.
| Duel.com Verifier | ProvablyFair.org Verifier | |
|---|---|---|
| Source | Casino-controlled | Independent (audit codebase) |
| Access | duel.com/fairness/verify | audit.provablyfair.org/casino/duel/tools/verify-bets |
| Trust model | Requires trusting the casino | Open-source, version-controlled |
| Monitoring | No change detection | Mismatches detected if casino changes logic |
6.9JavaScript Verification Script
Copy and run this in Node.js to verify any Beef bet:
const crypto = require('crypto'); const GRID_SIZE = 20;const MAX_UINT32 = 0xFFFFFFFF; const DEATH_POINTS_BY_DIFFICULTY = { 1: 1, // EASY 2: 3, // MEDIUM 3: 5, // HARD 4: 10, // EXPERT}; function computeDeathPoints(serverSeed, clientSeed, nonce, difficultyLevel) { const deathPointsCount = DEATH_POINTS_BY_DIFFICULTY[difficultyLevel]; const key = Buffer.from(serverSeed, 'hex'); const positions = Array.from({ length: GRID_SIZE }, (_, i) => i); for (let i = GRID_SIZE - 1; i > 0; i--) { const range = i + 1; const maxFair = MAX_UINT32 - (MAX_UINT32 % range); let cursor = GRID_SIZE - 1 - i; while (true) { const message = `${clientSeed}:${nonce}:${cursor}`; const hmac = crypto.createHmac('sha256', key).update(message).digest('hex'); let found = false; for (let off = 0; off + 8 <= hmac.length; off += 8) { const value = parseInt(hmac.substring(off, off + 8), 16); if (value < maxFair) { const j = value % range; [positions[i], positions[j]] = [positions[j], positions[i]]; found = true; break; } } if (found) break; cursor++; } } return positions.slice(0, deathPointsCount).sort((a, b) => a - b);} function verifyHash(serverSeed, serverSeedHashed) { const hash = crypto .createHash('sha256') .update(Buffer.from(serverSeed, 'hex')) .digest('hex'); return hash === serverSeedHashed;} // Replace with your valuesconst serverSeed = 'YOUR_SERVER_SEED';const serverSeedHashed = 'YOUR_SERVER_SEED_HASH';const clientSeed = 'YOUR_CLIENT_SEED';const nonce = 0;const difficultyLevel = 2; // 1=EASY, 2=MEDIUM, 3=HARD, 4=EXPERT console.log('Hash check:', verifyHash(serverSeed, serverSeedHashed) ? 'PASS' : 'FAIL');console.log('Death points:', computeDeathPoints(serverSeed, clientSeed, nonce, difficultyLevel));6.10Python Verification Script
The same verification in Python (standard library only):
import hashlib, hmac GRID_SIZE = 20MAX_UINT32 = 0xFFFFFFFF DEATH_POINTS_BY_DIFFICULTY = { 1: 1, # EASY 2: 3, # MEDIUM 3: 5, # HARD 4: 10, # EXPERT} def compute_death_points(server_seed, client_seed, nonce, difficulty_level): death_points_count = DEATH_POINTS_BY_DIFFICULTY[difficulty_level] key = bytes.fromhex(server_seed) positions = list(range(GRID_SIZE)) for i in range(GRID_SIZE - 1, 0, -1): range_val = i + 1 max_fair = MAX_UINT32 - (MAX_UINT32 % range_val) cursor = GRID_SIZE - 1 - i while True: message = f'{client_seed}:{nonce}:{cursor}'.encode() h = hmac.new(key, message, hashlib.sha256).hexdigest() found = False for off in range(0, len(h) - 7, 8): value = int(h[off:off+8], 16) if value < max_fair: j = value % range_val positions[i], positions[j] = positions[j], positions[i] found = True break if found: break cursor += 1 return sorted(positions[:death_points_count]) def verify_hash(server_seed, server_seed_hashed): computed = hashlib.sha256(bytes.fromhex(server_seed)).hexdigest() return computed == server_seed_hashed # Replace with your valuesserver_seed = 'YOUR_SERVER_SEED'server_seed_hashed = 'YOUR_SERVER_SEED_HASH'client_seed = 'YOUR_CLIENT_SEED'nonce = 0difficulty_level = 2 # 1=EASY, 2=MEDIUM, 3=HARD, 4=EXPERT print('Hash check:', 'PASS' if verify_hash(server_seed, server_seed_hashed) else 'FAIL')print('Death points:', compute_death_points(server_seed, client_seed, nonce, difficulty_level))6.11Evidence Screenshots3 records
| Evidence | Description |
|---|---|
| E02 | Fairness page overview — "What is Provably Fair?" and "How it works" sections |
| E03 | Fairness verification tool — Beef selected, showing game-specific verification inputs (server seed, client seed, nonce, difficulty level) |
| E11 | Client seed rotation response — server echoes client-submitted seed, does not assign |
Only disclosed inputs are used. Identical inputs always produce identical output.
Reproducibility & Artifacts
Can anyone independently reproduce every finding in this audit?
This section consolidates the open-source repository, datasets, output artifacts, and reproducibility posture of the audit. Every finding, every statistic, every pass/fail result can be independently reproduced by anyone with a computer and an internet connection. The repository is the credential — not this report.

Open-Source Audit Repository
Repository Details
- GitHub: ProvablyFair-org/duel-beef
- Commit: 05530ee044c2b2170e2c66554b124c5733953d22
- Game: Beef (duel-beef)
- Public Verifier: audit.provablyfair.org/casino/duel/tools/verify-bets
Prerequisites
- Node.js 18+
- npm 8+
- Git
- TypeScript (installed via npm)
- GitHub: ProvablyFair-org/duel-beef
- Commit: 05530ee044c2b2170e2c66554b124c5733953d22
- Game: Beef (duel-beef)
- Public Verifier: audit.provablyfair.org/casino/duel/tools/verify-bets
- Node.js 18+
- npm 8+
- Git
- TypeScript (installed via npm)
All audit results can be independently reproduced using the pinned commit, datasets, and commands above. The dataset hashes ensure you're running against the same 6,450 bets.

Commands to Reproduce
Installs TypeScript, ts-node, and cryptographic dependencies. npm test runs mocha (21 unit tests), then the 4M-round simulation, then the 22-step verification pipeline.
git clone https://github.com/ProvablyFair-org/duel-beef.gitcd duel-beefnpm install # Run entire audit end-to-end (21 unit tests + simulation + verification)npm testnpx ts-node tests/verify.ts[PASS] Step 1 — Seed Hash Integrity[PASS] Step 2 — Next-Seed Promotion (Commitment Linkage)[PASS] Step 3 — Hash Consistency Within Epoch[PASS] Step 4 — Nonce Audit[PASS] Step 5 — Outcome Recomputation (Death Points)[PASS] Step 6 — Client Seed Influence[PASS] Step 7 — Payout Math[PASS] Step 8 — Multiplier Formula (C(20,k)/C(20−m,k) × edge)[PASS] Step 9 — Win Condition (all stepped tiles not in mines)[PASS] Step 10 — Phase C Bet-Size Invariance ($10 bets)[PASS] Step 11 — Config Completeness (4 difficulty levels)[PASS] Step 12 — House Edge Audit (effective_edge = 0.8%)[PASS] Step 13 — Phase Labels[PASS] Step 14 — Dataset Hash[PASS] Step 15 — Epoch Size[PASS] Step 16 — Probability Independence (Anti-Circularity)[PASS] Step 17 — Phase D — Client Seed Variation[PASS] Step 18 — Simulation Results — Pass 1 Integrity[PASS] Step 19 — Simulation Results — Pass 2 Cherry-Pick Test[PASS] Step 20 — Multi-Step Multiplier Chain (Phase E)[PASS] Step 21 — Death-Point Recomputation (Phase E)[PASS] Step 22 — Cash-Out Payout Correctness (k>1) 22 passing, 0 flags, 0 hard failuresSimulates 1,000,000 rounds for each of the 4 difficulty-level configurations (4M total). Runtime ~90 seconds. Output written to outputs/simulation-results.json and outputs/rtp-convergence.html.
npx ts-node src/simulate.tsAudit Reproducibility Pinning
- Git Commit
- 05530ee044c2b2170e2c66554b124c5733953d22
- Node Version
- v18+ (tested on v22.x)
- Primary Dataset
- data/beef-master-6000bets.json (6,000 bets, 121 epochs)
- Phase E Dataset
- data/beef-phaseE-450bets.json (450 bets, 10 epochs)
- Primary Dataset Hash (SHA-256)
- d654ef7c6195584501e9033202d5acad13a16d89d296baab8befc0240fb36d36
- Phase E Dataset Hash (SHA-256)
- ef39d7f584cdb6d8057e846cdcb9b4ffcc60495bfcce8443d15bb910a9c51001
- Audit Date
- April 2026
- Audit ID
- PF-2026-DL06
Output Artifacts5 files generated
| File | Contents | Size |
|---|---|---|
| verification-results.json | Steps 1–22 results, per-step pass/fail with evidence | ~6KB |
| simulation-results.json | 4M-round RTP, chi-squared, cherry-pick detection (Pass 1 + Pass 2) | ~60KB |
| determinism-log.json | Per-bet death-point recomputation log (6,450 entries, 0 mismatches) | <1KB |
| chi-squared-results.json | Per-config chi-squared statistics and p-values | ~1KB |
| rtp-convergence.html | Interactive RTP convergence chart (self-contained HTML) | ~5KB |
Repository Structure
duel-beef/
├── src/
│   ├── rng.ts                  → HMAC-SHA256 backward Fisher-Yates (20-tile grid)
│   ├── simulate.ts             → Monte Carlo — 1M rounds/config × 4
│   ├── stats.ts                → Chi-squared, autocorrelation, runs test
│   ├── loader.ts               → Dataset loader + SHA-256 hash guard
│   └── types.ts                → Type definitions
├── tests/
│   ├── verify.ts               → 22-step verification pipeline
│   ├── steps/
│   │   ├── commitment.ts       → Steps 1–4: Commit-reveal integrity + nonce audit
│   │   ├── determinism.ts      → Steps 5–6: Death-point recomputation + client seed
│   │   ├── payouts.ts          → Steps 7–12: Payout math + multiplier + Phase C + house edge
│   │   ├── dataset.ts          → Steps 13–17: Dataset integrity + anti-circularity + Phase D
│   │   ├── simulation.ts       → Steps 18–19: Simulation integrity + cherry-pick
│   │   ├── multireveal.ts      → Steps 20–22: Phase E multi-step + cash-out verification
│   │   ├── statistical.ts      → Informational: RTP, serial, chi-squared
│   │   └── context.ts          → Shared context + pass/fail helpers
│   └── beef/
│       └── BeefTests.ts        → 21 unit tests (Mocha)
├── data/
│   ├── beef-master-6000bets.json    → 6,000 primary bets (4 phases, 121 epochs)
│   └── beef-phaseE-450bets.json     → 450 multi-step bets (10 epochs)
├── outputs/                    → Generated by npm test
│   ├── verification-results.json → Steps 1–22 pass/fail
│   ├── simulation-results.json  → 4M rounds, per-config RTP + cherry-pick
│   ├── determinism-log.json     → Per-bet death-point recomputation log
│   ├── chi-squared-results.json → Distribution test results
│   └── rtp-convergence.html     → Interactive RTP convergence chart
├── evidence/
│   ├── E01–E04 *.png            → Game UI, provably-fair panel, fairness page captures
│   └── client-seed-origin.png   → Client seed origin evidence
├── capture/
│   ├── beef-capture.reference.js         → Browser bet capture script (primary dataset)
│   └── beef-capture-phaseE.reference.js  → Browser bet capture script (Phase E multi-step)
├── results/                    → Merged capture working directory
├── README.md
├── MANIFEST.md
├── package.json
├── tsconfig.json
└── .mocharc.yml
Step-to-Section Cross-Reference22 verification steps mapped
| Step | Test Name | Report Section |
|---|---|---|
| 1 | Seed Hash Integrity | S1 |
| 2 | Next-Seed Promotion (Commitment Linkage) | S1 |
| 3 | Hash Consistency Within Epoch | S1 |
| 4 | Nonce Audit | S1, S5 |
| 5 | Outcome Recomputation (Death Points) | S1, S2, S3 |
| 6 | Client Seed Influence | S1, S2 |
| 7 | Payout Math | S3, S4 |
| 8 | Multiplier Formula (C(20,k)/C(20−m,k) × edge) | S3, S4 |
| 9 | Win Condition (all stepped tiles not in mines) | S3 |
| 10 | Phase C Bet-Size Invariance ($10 bets) | S3, S4 |
| 11 | Config Completeness (4 difficulty levels) | S3 |
| 12 | House Edge Audit (effective_edge = 0.8%) | S4 |
| 13 | Phase Labels | S3 |
| 14 | Dataset Hash | S7 |
| 15 | Epoch Size | S1, S3 |
| 16 | Probability Independence (Anti-Circularity) | S4 |
| 17 | Phase D — Client Seed Variation | S1, S2, S3 |
| 18 | Simulation Results — Pass 1 Integrity | S2, S4 |
| 19 | Simulation Results — Pass 2 Cherry-Pick Test | S4 |
| 20 | Multi-Step Multiplier Chain (Phase E) | S3 |
| 21 | Death-Point Recomputation (Phase E) | S3, S5 |
| 22 | Cash-Out Payout Correctness (k>1) | S3, S4, S5 |
reproduce-audit.sh
# Clone and setupgit clone https://github.com/ProvablyFair-org/duel-beef.gitcd duel-beefgit checkout 05530ee044c2b2170e2c66554b124c5733953d22npm install # Run full audit (22 verification steps + 4M simulation)npm test # Or run individual componentsnpm run verify # 22-step verification pipelinenpm run simulate # 4M-round simulation (4 configs × 1M) # View generated reportscat outputs/verification-results.jsoncat outputs/simulation-results.jsonAll audit results can be independently reproduced using the pinned commit, datasets, and commands above. The dataset hashes ensure you're running against the same 6,450 bets.