Plinko
Independent verification, backed by open-source code.


 Passed
- Live bets verified
- 8,100
- 162 active seed pairs
- Verifier parity
- 100%
- 0 mismatched outcomes
- Simulation roundsSimulated RTP 99.917%
- 27M
- Simulated RTP 99.917% · 27 configurations
- Proven RTP · base tier
- 99.9%
- Base stake tier · 0.1% house edge
Verification pipeline
Real bets. Independently reproduced.
Placed at Duel.com on 10 April 2026. Our own RNG code, written from the spec, reproduces all 8,100 recorded outcomes.
The casino result, reproduced.
- Casino outcome
- Slot 6 / 9
- Our reproduction
- Slot 6 / 9
- Recorded payout
- $0.0101


- Seed Hash IntegrityPass
- Next-Seed PromotionPass
- Hash Consistency Within EpochPass
- Slot Recomputation & Bit-Extraction BoundPass
- Client Seed InfluencePass
- Payout MathPass
- Multiplier Table ProvenancePass
- Phase C Code-Path EquivalencePass
- Zero Edge AuditPass
- Config Completeness & Cell CoveragePass
- Epoch Size & CountPass
- Multiplier Table + SymmetryPass
- Population & Phase LabelsPass
- Dataset HashPass
- Scaling Edge AnalysisPass
- Probability IndependencePass
- Phase D — Client Seed VariationPass
- Simulation Pass 1Pass
- Simulation Pass 2 — Cherry-Pick TestPass
- Artifact IntegrityPass
- Published-Pin Drift ScanPass
- Epoch-Window Slot FitPass

The repo is the credential. You don’t have to trust us: the audit ships as code. Check out release v1.4.2 and run npm test to re-run it: 23 scored steps, 27M simulated rounds replayed, 8,100 live bets re-verified, and the results compared with the committed ones.

This audit independently validates the Plinko game operated by Duel.com under ProvablyFair.org Framework 1.1. We placed 8,100 real bets across 162 seed pairs on 10 April 2026 and recomputed every outcome with our own code, written from the spec. Release v1.4.2 re-runs that evidence: 22 of 23 scored steps pass, and one carries a capture flag that is limited by our capture script, not a Duel issue.

Audit Verdict
Tap a result to inspect the evidence.
| Check | Result | Reference |
|---|---|---|
| Proven RTP | Pass | 99.9% on all 27 settings at the base stake tier · RTP claim rule: 0 of 27 outside ±0.1 pp of the published 99.9% · 99.917% simulated (27M rounds) |
| Live ↔︎ Verifier Parity | Pass | 8,100 / 8,100 slots recomputed, 0 mismatches · both ProvablyFair.org player verifiers agree on slot and path |
| Commit-Reveal System | Pass | 162 / 162 revealed seeds match their commitments and 166 / 166 next-seed promotions link up (consistency checks) · the capture recorded each commitment before its epoch’s first bet |
| Nonce Audit | Capture flag | Nonces sequential under every commitment. Two bets our capture missed were reconstructed from the revealed seeds: limited by our capture script, not a Duel issue (Step 4) |
| Client Seed | Pass | Set in the browser and submitted at rotation · a wrong client seed changes the path and slot as often as chance predicts |
| RNG Analysis | Pass | HMAC-SHA256 per row, rebuilt from the written spec · exact 50/50 per bounce · no hidden inputs |
| Payout Logic | Pass | All 8,100 multipliers on the 8-decimal grid · win_amount = stake × multiplier to relative 1e-12 |
| Scaling House Edge | Info | 0.1% at the base stake tier, rising to 2.0% at larger stakes in the config · explained from the config, not certified · see S4.7 |
| Anti-Circularity | Pass | Theoretical RTP from first principles: binomial P(slot) × the paid multiplier table, no operator probability or RTP figure used |
| Integrity Checks | Pass | 15 standard fairness integrity tests — 14 pass, 1 N/A |
| Determinism | Pass | Same inputs, same slot on 8,100 / 8,100 bets · npm test reproduces the committed results (exit 0) |

Overall StatusPass
Proven RTPPass
Live ↔︎ Verifier ParityPass
Commit-Reveal SystemPass
Nonce AuditCapture flag
Client SeedPass
RNG AnalysisPass
Payout LogicPass
Scaling House EdgeInfo
Anti-CircularityPass
Integrity ChecksPass
DeterminismPass

What Was Audited
✓ Audited
- The RNG algorithm is deterministic and verifiable
- Revealed server seeds match the SHA-256 commitments their bets carried
- Client seed is set in the browser and players can change it at any time
- Nonces count up from 0 under each commitment with no repeat
- Slot outcomes are computed via HMAC-SHA256 with one call per row
- Slot positions are reproducible from server seed, client seed, nonce and row count
- Payouts match the multiplier table for all 27 configurations at the base stake tier
- Theoretical RTP is 99.9% on all 27 configurations at the base stake tier, and the published 99.9% holds on every one
- Bet amount does not influence the RNG or slot outcome
- Players can independently verify every bet

— What Audit Excludes
- Scaling house edge above the base stake tier — explained from the config in S4.7
- Max win
- Rakeback, Zero Edge and promotions — 99.9% is the proven RTP; these are operator-side
- Cross-account sampling
- Duel’s server code and seed generation — outcomes are verified from the captured rounds and their commitments
- Infrastructure or server security
- Wallet, payments, or operational systems outside game logic
- The RNG algorithm is deterministic and verifiable
- Revealed server seeds match the SHA-256 commitments their bets carried
- Client seed is set in the browser and players can change it at any time
- Nonces count up from 0 under each commitment with no repeat
- Slot outcomes are computed via HMAC-SHA256 with one call per row
- Slot positions are reproducible from server seed, client seed, nonce and row count
- Payouts match the multiplier table for all 27 configurations at the base stake tier
- Theoretical RTP is 99.9% on all 27 configurations at the base stake tier, and the published 99.9% holds on every one
- Bet amount does not influence the RNG or slot outcome
- Players can independently verify every bet
- Scaling house edge above the base stake tier — explained from the config in S4.7
- Max win
- Rakeback, Zero Edge and promotions — 99.9% is the proven RTP; these are operator-side
- Cross-account sampling
- Duel’s server code and seed generation — outcomes are verified from the captured rounds and their commitments
- Infrastructure or server security
- Wallet, payments, or operational systems outside game logic
- Every guarantee below applies to the base stake tier (bracket 0), where every captured bet was placed
- Outcomes are deterministic and reproducible from the recorded inputs
- Live game results match independent recomputation for every captured bet (8,100 / 8,100)
- The slot distribution of 27M simulated rounds is consistent with binomial B(rows, 0.5) on all 27 configurations
- Theoretical RTP is 99.9% on all 27 configurations at the base stake tier, derived from first principles
- The published 99.9% RTP holds on all 27 configurations within the ±0.1 pp band of the RTP claim rule
- The client seed is a genuine input: a wrong client seed changes outcomes as often as chance predicts
- All scored steps pass apart from one capture flag, which is limited by our capture script, not a Duel issue
What Audit Covers

| Area | Description |
|---|---|
| Commit-Reveal System | SHA-256 commitments, next-seed promotion, reveal on rotation; commitment timing from the capture records |
| Client Seed Origin | Browser-generated, player-controlled, submitted at rotation and echoed by the server |
| Seed Handling | Client seed control, nonce lifecycle, seed pair rotation |
| RNG Analysis | HMAC-SHA256 per-row algorithm, rebuilt from the written spec; bias bound; Duel’s Verify-tab code run as a second check |
| Payout Logic | Multiplier table provenance, payout math, bet-size invariance at $0.01 and $10 |
| Live Parity | Independent slot recomputation of all 8,100 live bets; both ProvablyFair.org player verifiers executed on every bet |
| RTP Validation | Theoretical RTP from first principles, the RTP claim rule, 27M simulated rounds, cherry-pick screening (Pass 2) |
| Fairness Integrity | Standard integrity matrix — 15 tests across commit-reveal, determinism, payout, isolation, and parameter enforcement |
What Audit Guarantees

- Every guarantee below applies to the base stake tier (bracket 0), where every captured bet was placed
- Outcomes are deterministic and reproducible from the recorded inputs
- Live game results match independent recomputation for every captured bet (8,100 / 8,100)
- The slot distribution of 27M simulated rounds is consistent with binomial B(rows, 0.5) on all 27 configurations
- Theoretical RTP is 99.9% on all 27 configurations at the base stake tier, derived from first principles
- The published 99.9% RTP holds on all 27 configurations within the ±0.1 pp band of the RTP claim rule
- The client seed is a genuine input: a wrong client seed changes outcomes as often as chance predicts
- All scored steps pass apart from one capture flag, which is limited by our capture script, not a Duel issue
References
Plinko — Game Rules6 sections▶

Plinko is a ball-drop game on a triangular peg board. You pick the number of rows (8–16) and a risk level (low, medium, or high). The ball bounces left or right at each row — a fair 50/50 each time — and lands in one of the slots at the bottom. The slot it lands in decides your payout multiplier.
How to Play
1. Choose row count — Select between 8 and 16 rows. More rows means more bounces and more possible slot positions.
2. Choose risk level — Select low, medium, or high. Higher risk shifts payout weight toward edge slots.
3. Enter bet amount — Choose how much to wager.
4. Drop the ball — The ball bounces through the peg board and lands in a slot.
5. Outcome — Payout = bet amount × multiplier for the landing slot.
Win Conditions
The win condition in Plinko depends on which slot the ball lands in.
| Outcome | Condition | Example (16r/high) |
|---|---|---|
| Jackpot (edge slot) | Ball lands in slot 0 or 16 | 1009.33× — 1 in 32,768 chance (either edge) |
| Win (outer slots) | Ball lands near edges | Slot 4 → 4.04× |
| Partial return | Ball lands near center | Slot 8 → 0.20× |
Risk vs Reward
The core mechanic of Plinko is the tradeoff between row count, risk level, and payout shape.
- Row count controls granularity — more rows means more possible slots; on medium and high risk, more rows also raise the edge multipliers
- Risk level controls payout shape — low risk has flatter payouts; high risk concentrates value at edge slots with a 0.2× center floor
- RTP is constant — all 27 configurations have the same theoretical RTP (99.9% at the base stake tier) regardless of rows or risk
Parameters
| Parameter | Value | Notes |
|---|---|---|
| Row Count | 8–16 | Player selects; determines slot count |
| Risk Levels | Low, Medium, High | Affects multiplier table, not slot probabilities |
| House Edge | 0.1% (base stake tier) | Progressive: rises at larger stakes, set in the config |
| Theoretical RTP | 99.9% | Derived on all 27 configurations at the base stake tier |
| Configurations | 27 | 9 row counts × 3 risk levels |
| RNG Algorithm | HMAC-SHA256 | One HMAC call per row; key = hex-decoded server seed |
Seed Formats
Every Plinko bet uses three cryptographic inputs to generate the result.
| Seed Type | Format | Example | Purpose |
|---|---|---|---|
| Server Seed | 64-char hex (32 bytes) | 5de225f630d2de83… | Casino-provided randomness |
| Client Seed | Alphanumeric string | MAAxNnpj1uB4AobA | Player-contributed entropy |
| Nonce | Integer (0, 1, 2…) | 23 | Ensures uniqueness per bet within epoch |
Multiplier Tables & Payout
Payouts in Plinko are set by the landing slot, row count and risk level. The multipliers are calibrated so the theoretical RTP is 99.9% on all 27 configurations at the base stake tier.
win_amount = bet_amount × multiplier_table[rows][risk][slot]| Rows | Risk | Edge Multiplier (slot 0/N) | Center Multiplier | RTP |
|---|---|---|---|---|
| 8 | Low | 5.65× | 0.50× | 99.9% |
| 8 | High | 29.25× | 0.20× | 99.9% |
| 16 | Low | 16.15× | 0.50× | 99.9% |
| 16 | High | 1009.33× | 0.20× | 99.9% |
Why Provably Fair Matters▶

Traditional online casinos require players to trust that games are fair. Provably fair systems replace much of that trust with checks players can run themselves: each outcome can be recomputed and checked against a commitment made before the bet. In a Provably Fair system:
- The casino commits to its server seed before the player bets
- The player contributes randomness that the casino cannot predict
- Anyone can verify the outcome after the fact
High-Level Overview7 sections▶

Checklist Reference
Based on the ProvablyFair.org Audit Execution Checklist, here are the tests covered under this audit document.
1. Commit-Reveal System & Seed Handling
| Test | Description |
|---|---|
| Server seed commit exists before play | SHA-256 hash shown before betting; recorded before each epoch’s first bet in the capture |
| Server seed reveal matches commit | SHA-256(hexDecode(revealed)) = committed hash, a consistency check |
| Client seed control | Player can set/change client seed via rotation UI |
| Nonce increments correctly | Starts at 0, +1 per bet, resets at epoch boundary |
| Full determinism | Same inputs → same result |
2. Randomness & Entropy Model
| Test | Description |
|---|---|
| RNG depends only on seeds + nonce | No external inputs — slot is a pure function of (server seed, client seed, nonce) |
| No mixed entropy sources | No timestamps, Math.random, etc. |
| Unbiased mapping | int % 2 on uint32 has zero modulo bias |
| No state leakage | RNG isolated per round — each row uses unique cursor |
3. Verifier ↔︎ Live Parity
| Test | Description |
|---|---|
| Live outcomes match verifier | 8,100 / 8,100 slots recomputed with 0 mismatches |
| Multi-phase verification | Phases A (all configs), B (deep sample), C (bet-size check), D (client seed) |
| Bet-size invariance | $10 bets use the same RNG and multiplier table as $0.01 bets |
4. Game Logic & RTP Validation
| Test | Description |
|---|---|
| Anti-circularity proof | Binomial P(slot) × the paid multipliers = 99.9%, from first principles |
| House edge audit | 0.1% on all 27 configurations at the base stake tier |
| Payout rules correctness | Multipliers on the 8-decimal grid; win amount = stake × multiplier at relative 1e-12 |
| Simulated RTP | 27M rounds consistent with the theoretical 99.9% |
| Cherry-pick detection | Tests A, B and C on 162 revealed seeds find no sign of seed selection |
| RTP claim rule | The published 99.9% holds on all 27 settings within ±0.1 pp |
5. Fairness Integrity & Player Verification
| Test | Description |
|---|---|
| Player can reproduce results offline | Using seeds + nonce + row count |
| Verifier logic matches live logic | Same HMAC-SHA256 per-row algorithm; both player verifiers run on all 8,100 bets |
| Verifier publicly accessible | ProvablyFair.org verifier — no login required |
| No reliance on private APIs | Fully client-side verification |
| 23 scored verification steps | Commit-reveal, determinism, payout, RTP, simulation and package integrity |
High-Level Flow
To get an overview of how the process works, here is a high-level breakdown:
1. Player Bets — Selects row count (8–16), risk level, and bet amount
2. Seeds Combined — HMAC-SHA256(hexDecode(serverSeed), clientSeed:nonce:cursor) for each row
3. RNG Output — Each row produces a uint32; int % 2 determines left (0) or right (+1)
4. Slot Accumulation — Sum of right-bounces across all rows = final slot (0 to rows)
5. Multiplier Lookup — final_slot maps to multiplier via scaling_edge[rows][risk][0].multipliers[final_slot]
6. Payout Result — win_amount = bet_amount × payout_multiplier
Provably Fair Model
Provably fair gambling systems use cryptographic primitives to make outcomes checkable. The model relies on three components: a server seed committed via hash before play, a player-controlled client seed, and an incrementing nonce. These inputs are combined using HMAC-SHA256 to produce deterministic, verifiable results. This section describes the common provably fair architecture as Duel Plinko implements it.
Commit-Reveal Model
The Commit-Reveal model is integral to ensuring fairness and transparency in online gambling. This model involves several key phases:
Commit Phase:
Before any bets are placed, the casino generates a secret server seed and shows the player only the SHA-256 hash of the hex-decoded seed. The hash fixes the seed without revealing it: the player cannot know the seed in advance but can check it against the hash later.
Bet Phase:
The player places their bet. The server combines the server seed with the player’s client seed and the nonce via HMAC-SHA256 to compute each row’s outcome. Every bet in an epoch uses the same server seed and client seed pair.
Reveal Phase:
When the player rotates the seed pair, the server reveals the plaintext server seed. The player can then verify SHA-256(hexDecode(serverSeed)) against the commitment they saved before betting.
Verify Phase:
Anyone can recompute every bet’s slot from the revealed server seed, client seed, and nonce using the published HMAC-SHA256 algorithm.
Player-Controlled Client Seed
The player’s client seed is generated by the browser and submitted to the server via the seed rotation UI. Players can set their own client seed at any time. This means:
- The casino cannot predict the full RNG input
- Players contribute entropy that they control
- Results depend on both parties’ inputs
Nonce Lifecycle
The nonce is a counter that increments with each bet within an epoch:
- Starts at 0 for each new server seed
- Increments by exactly 1 per bet
- Never reused within the same seed epoch
- Resets to 0 when the server rotates to a new server seed
Seed Epoch: (serverSeed, clientSeed) Bet 1: nonce = 0 → Slot ABet 2: nonce = 1 → Slot BBet 3: nonce = 2 → Slot C ...[Player rotates seed — epoch complete]Next bet: nonce = 0 → Slot X (new seed pair)Determinism Guarantee
Given identical inputs, the output is always identical:
HMAC-SHA256(hexDecode(serverSeed), clientSeed:nonce:cursor) → Always same hashSame hash per row → Always same left/right bounceSame bounces across all rows → Always same final slotSame slot + same config → Always same payoutTechnical Glossary7 categories▶

Core Concepts
| Term | Definition |
|---|---|
| Provably Fair | A cryptographic system that lets players check each game outcome against a commitment the casino made before the bet. Relies on commit-reveal schemes and deterministic algorithms. |
| Commit-Reveal Protocol | A two-phase process in which the casino commits to a secret server seed (by showing its hash) before the player bets, then reveals the seed after the bet. |
| Determinism | The property that identical inputs always produce identical outputs. Same server seed, client seed, nonce, and row count must always generate the same slot position. |
| Client Seed Origin | How the client seed is generated. Full Pass: browser-generated default + player-customizable seed. Conditional Pass: server-assigned default + player-customizable seed. Hard Fail: player cannot set their own seed. Duel: Full Pass. |
Seed System
| Term | Definition |
|---|---|
| Server Seed | A secret 32-byte value generated by Duel.com, transmitted as a 64-character hex string. Its hash is shown to players before betting; the seed itself is revealed after rotation. |
| Client Seed | A random value controlled by the player, generated by the browser. Players can change it at any time via the seed rotation UI. |
| Nonce | A sequential counter that increments per bet within an epoch. Resets to 0 when the server rotates to a new server seed. |
| Hashed Server Seed | SHA-256(hexDecode(serverSeed)) — the commitment hash shown before betting. After rotation, players verify the revealed seed produces this hash. |
| Cursor | Zero-based row index (0 to rows−1) used in the HMAC message. Each cursor value produces one row’s left/right bounce. |
Cryptographic Functions
| Term | Definition |
|---|---|
| HMAC-SHA256 | Hash-based Message Authentication Code using SHA-256. Duel Plinko uses HMAC-SHA256 with the hex-decoded server seed as key and clientSeed:nonce:cursor as message. One call per row. |
| SHA-256 | Secure Hash Algorithm 256-bit. Used for server seed commitment: SHA-256(hexDecode(serverSeed)) = serverSeedHashed. |
| Hex Decoding | Converting a 64-character hex string to 32 raw bytes. Critical for the HMAC key — using the hex string as UTF-8 produces wrong outputs. |
Verification Terms
| Term | Definition |
|---|---|
| Verifier | A tool that independently calculates slot outcomes from the seeds, nonce and row count. Both ProvablyFair.org verifiers are pinned and run on all 8,100 captured bets in this audit. |
| Parity | Degree of matching between verifier and live game results. 100% parity = every slot matches. This audit: 8,100/8,100 exact match. |
| Anti-Circularity | Theoretical RTP derived from first principles: independently computed binomial B(rows, 0.5) probabilities × the paid multiplier table = 99.9%, with no operator-supplied probability or RTP figure. |
Game Mechanics
| Term | Definition |
|---|---|
| Slot | The ball’s final landing position (0 to rows). Slot = count of right-bounces across all rows. Each slot has a corresponding payout multiplier. |
| Row Count | Player-selected parameter (8–16) determining the number of peg rows and HMAC calls per bet. More rows = more possible slots. |
| Risk Level | Player-selected parameter (low, medium, high) that determines the multiplier table. Higher risk = more value at edge slots, less at center. |
| Binomial Distribution | B(rows, 0.5) — the probability distribution for slot outcomes. P(slot = k) = C(rows, k) × 0.5^rows. Each row is an independent 50/50 event. |
| Progressive House Edge | The config’s 191 bet-size brackets per configuration, with the edge rising from 0.1% to 2.0%. The base stake tier (0.1% edge) covers bets up to about $336 on the most restrictive configuration. |
Audit Terms
| Term | Definition |
|---|---|
| Epoch | A sequence of bets using the same server seed and client seed pair. Ends when the player rotates seeds. |
| Phase | A structured data collection segment. Phase A: all 27 configs. Phase B: deep 16r/high sample. Phase C: $10 bet-size check. Phase D: client seed verification. |
| Cherry-Pick Detection | Screening for selective seed deployment. Pass 2 replays all 162 revealed seeds over 10,000 nonces (Tests A and B) and scores the payouts each epoch actually served against a calibrated null (Test C). |
| Master Dataset | data/plinko-master-8100bets.json — the primary dataset containing all 8,100 bets and 166 seed entries across four phases. |
| Framework 1.1 | The ProvablyFair.org audit framework this release is certified under. Releases under it carry the RTP claim rule, game profile coverage, capture flags and the reproduction gate. |
| Base Stake Tier | Bracket 0 of the config’s stake ladder, where the house edge is 0.1%. Every captured bet was placed in it, and the RTP guarantees in this report apply to it only. |
| RTP Claim Rule | RTP-CLAIM 1.2.0: the RTP figure a casino publishes is held against the true RTP of every setting it covers, within ±0.1 pp. A house-side miss makes the verdict RTP FIGURE OVERSTATED (exit 5). |
| Capture Flag | A flag raised by a limitation of our own capture, not the operator. It is disclosed and verdict-neutral: here, two bets our capture missed, reconstructed from the revealed seeds (Step 4). |
| Game Profile | The framework’s list of checks for a game type: PLINKO-01 to PLINKO-39 in the Plinko profile 1.0.2. Each is covered by a scored step, a package check, or marked n/a with a reason. |
| Reproduction Gate | Every run writes to outputs/run/ and is compared with the committed results: integers and strings exactly, other values within 1e-14 absolute + 1e-12 relative. A difference beyond that exits 1. |
Data Formats
| Term | Definition |
|---|---|
| plinko-master-8100bets.json | The 8,100-bet dataset used throughout this audit. SHA-256: 3cf9359d88220bc800bb32edfe04399f55b909302262928ee3a0582715635267. |
| plinkoConfig.json | Duel.com’s game configuration: all 27 multiplier tables, 191 bet-size brackets per configuration and probability arrays, as served at GET /api/v2/games/plinko/config. A re-fetch on 5 October 2026 returned identical bytes. SHA-256: 78f0a39201a8c24fd1577143732e004f77e27d4d36efeedc6b3f7b93b2078fed. |
| verification-results.json | Output of the 23-step verification suite: every step result with its details, the game profile mapping and the verdict. |
| simulation-results.json | Two-pass simulation output: Pass 1 (27M rounds, pinned seeds) and Pass 2 (162 casino seeds × 10,000 nonces, cherry-pick detection). |
| rtp-claim-table.json | The RTP claim rule’s table: the exact RTP of all 27 settings against the published 99.9%. |
Seed, Nonce & Determinism
Can the casino change your outcome after you bet?
Every Plinko drop on Duel.com is fixed by four inputs: server seed, client seed, nonce and row count. Duel publishes the SHA-256 hash of the server seed (the commitment) and reveals the seed itself when you rotate. All 162 revealed seeds hash to the commitments their bets carried, and every rotation links to the hash Duel had pre-committed as next. These are consistency checks. That each commitment was shown before its bets rests on the capture’s own records, which stored every epoch’s commitment from the rotation response before its first bet.
Revealed seeds match their commitments. The capture recorded each commitment before its first bet.

Commit-Reveal Consistency
What we verified
- All 162 revealed server seeds hash to the commitment their epoch’s bets carried
- All 166 rotations link to the hash Duel pre-committed as next, anchored by a reading taken before the capture began
- The capture recorded each epoch’s commitment from the rotation response before the epoch’s first bet
- Nonces count up from 0 under each commitment with no repeat; two bets our capture missed carry a capture flag
- The client seed is set in the browser; a wrong client seed changes the path and slot as often as chance predicts
- Identical inputs always produce the same slot: 8,100 / 8,100 recomputed
What this means for you
- A seed swapped after your bet would not match the commitment you saved
- Save the commitment before you bet: your copy is what shows the seed was fixed in time
- Your client seed is a real input to every row of every drop
- Every bet can be rechecked from its seeds, today or months later
- Seed selection is screened statistically in S4.5, which finds no sign of cherry-picking


- All 162 revealed server seeds hash to the commitment their epoch’s bets carried
- All 166 rotations link to the hash Duel pre-committed as next, anchored by a reading taken before the capture began
- The capture recorded each epoch’s commitment from the rotation response before the epoch’s first bet
- Nonces count up from 0 under each commitment with no repeat; two bets our capture missed carry a capture flag
- The client seed is set in the browser; a wrong client seed changes the path and slot as often as chance predicts
- Identical inputs always produce the same slot: 8,100 / 8,100 recomputed
- A seed swapped after your bet would not match the commitment you saved
- Save the commitment before you bet: your copy is what shows the seed was fixed in time
- Your client seed is a real input to every row of every drop
- Every bet can be rechecked from its seeds, today or months later
- Seed selection is screened statistically in S4.5, which finds no sign of cherry-picking
Commitment matches revealed seedPass
Commitment shown before betsInfo
Next-seed promotionPass
Hash consistency within epochPass
Nonce sequencingCapture flag
Client seed originPass
Client seed influencePass
Deterministic outputPass
All 162 revealed seeds match their commitments and all 166 next-seed promotions link up. Each commitment was recorded before its epoch’s first bet; that timing rests on the capture’s records. Nonces run in order; two bets our capture missed are reconstructed from the revealed seeds and carry a capture flag, limited by our capture script, not a Duel issue. The same inputs always produce the same slot.
| Check | Result | Evidence |
|---|---|---|
| Commitment matches revealed seed | Pass | 162 / 162 revealed seeds hash to the commitment their bets carried (Step 1). A consistency check, not a timestamp |
| Commitment shown before bets | Info | Recorded before the first bet in 162 / 162 epochs, 1.1 to 11.3 s ahead (capture timestamps, not scored) |
| Next-seed promotion | Pass | 166 / 166 rotations link to the pre-committed next hash, anchored before epoch 0 (Step 2) |
| Hash consistency within epoch | Pass | 162 epochs, one commitment each, 162 distinct commitments (Step 3) |
| Nonce sequencing | Capture flag | Sequential from 0 with no repeat in all 162 epochs. Two bets our capture missed were reconstructed from the revealed seeds: limited by our capture script, not a Duel issue (Step 4) |
| Client seed origin | Pass | Set in the browser and submitted at rotation; the server echoes it and does not assign it. In this capture our script generated the seeds |
| Client seed influence | Pass | Wrong client seed: path coincided 10 times (5.16 expected), slot 1,281 times (1,275.86 expected); 6,819 / 8,100 slots changed (Step 6) |
| Deterministic output | Pass | Same (serverSeed, clientSeed, nonce, rows) always gives the same slot: 8,100 / 8,100 (Step 5) |
Commitment matches revealed seedPass
Commitment shown before betsInfo
Next-seed promotionPass
Hash consistency within epochPass
Nonce sequencingCapture flag
Client seed originPass
Client seed influencePass
Deterministic outputPass
All 162 revealed seeds match their commitments and all 166 next-seed promotions link up. Each commitment was recorded before its epoch’s first bet; that timing rests on the capture’s records. Nonces run in order; two bets our capture missed are reconstructed from the revealed seeds and carry a capture flag, limited by our capture script, not a Duel issue. The same inputs always produce the same slot.
How It Works — Seed, Nonce & Determinism8 sections
1.1Server Seed Commitment
Before an epoch’s bets, Duel publishes a commitment: serverSeedHashed = SHA-256(hexDecode(serverSeed)), where the server seed is a 64-character hex string (32 bytes). Every bet response in the epoch carries it. When you rotate, Duel reveals the seed, and anyone can recompute the hash. Step 1 does this for every revealed seed: a match shows the revealed seed is the one the bets were committed to. It is a consistency check; when the commitment was shown is covered in 1.4.
// §1.2: commitment = lowercase hex of SHA-256 over the hex-decoded seed bytes.// A seed that is not 64 hex characters cannot match, so it returns false.export function verifyHash(serverSeed: string, serverSeedHashed: string): boolean { let key: Buffer; try { key = decodeServerSeed(serverSeed); } catch { return false; } if (typeof serverSeedHashed !== "string") return false; return sha256Buffer(key) === serverSeedHashed.toLowerCase();}Real Example from Live Data:
// bets[0].response — bet 71591629, Phase A, the epoch's first bet{ "server_seed_hashed": "9fae5bb7897874cb71d7bd1be6dca522ddcd8f0c8f18ecaab9c5474d63b9be5a", "client_seed": "MAAxNnpj1uB4AobA", "nonce": 0}// seeds[1] — the next rotation reveals the epoch's server seed{ "serverSeed": "5de225f630d2de838265252752ab4ba050a3f20a53711e23a0a43979abf755bd", "revealedFrom": { "transactionId": 517122072 }}Verification:
const crypto = require('crypto'); const serverSeed = "5de225f630d2de838265252752ab4ba050a3f20a53711e23a0a43979abf755bd"; const hashedServerSeed = crypto .createHash("sha256") .update(Buffer.from(serverSeed, 'hex')) .digest("hex"); console.log(hashedServerSeed);// Output: 9fae5bb7897874cb71d7bd1be6dca522ddcd8f0c8f18ecaab9c5474d63b9be5a ✅1.2Commitment Linkage (Next-Seed Promotion)
Duel also publishes the hash of the next server seed. At every rotation, the hash pre-committed as next (previousNextHash) must equal the hash that becomes active (newActiveHash), and the previous seed entry’s nextServerSeedHash must agree. The chain is anchored before epoch 0 by a reading taken before the capture’s first rotation (GET /api/v2/client-seed); the seed behind that hash is revealed with epoch 0. Evidence begins at that reading. Like the hash match, these equalities show the seed records fit together, not when a hash was shown.
for (let i = 0; i < seeds.length; i++) { const s = seeds[i]; if (!s.nextSeedPromotion) { failures.push(`seed[${i}] (${s.context}): no nextSeedPromotion record — this rotation is unverified, not exempt`); continue; } checked++; const { previousNextHash, newActiveHash } = s.nextSeedPromotion; const linkageOk = previousNextHash === newActiveHash; // Cross-check against the seed-level fields where available: the // previous entry's nextServerSeedHash should equal this entry's // serverSeedHashed (same property, captured independently from the API). let seedFieldOk = true; if (i > 0) { const prevNextHash = seeds[i - 1].seed.nextServerSeedHash; const thisActive = s.seed.serverSeedHashed; if (prevNextHash && thisActive && prevNextHash !== thisActive) { seedFieldOk = false; } }Anchoring the chain before epoch 0:
const preCaptureNextHash = anchor.nextSeedPromotion.previousNextHash; const epoch0Hash = anchor.seed.serverSeedHashed; if (preCaptureNextHash !== epoch0Hash) { anchorIssues.push( `pre-capture next-hash ${preCaptureNextHash.substring(0, 16)}... ≠ epoch 0's active hash ` + `${epoch0Hash.substring(0, 16)}... — epoch 0 was not the commitment the account already held` ); } if (!anchor.seed.serverSeed) { anchorIssues.push("epoch 0's server seed is never revealed, so the anchor commitment has no plaintext behind it"); } else if (!verifyHash(anchor.seed.serverSeed, epoch0Hash)) { anchorIssues.push(`SHA-256(epoch 0 revealed seed) ≠ ${epoch0Hash.substring(0, 16)}...`); }}1.3Hash Consistency Within Epoch
An epoch is the run of bets under one server seed. Step 3 delimits each epoch by the nonce returning to 0 in capture order, not by the hash being tested, then requires one server_seed_hashed across every bet of the epoch. A seed swapped mid-epoch would put two hashes inside one run and fail. The number of runs must also equal the number of distinct commitments.
const failures: string[] = [];const runs: Bet[][] = [];let current: Bet[] = [];for (const bet of bets) { if (bet.response.nonce === 0 && current.length) { runs.push(current); current = []; } current.push(bet);}if (current.length) runs.push(current); runs.forEach((runBets, i) => { const hashes = new Set(runBets.map(b => b.response.server_seed_hashed)); if (hashes.size !== 1) { failures.push( `Epoch ${i} (nonces ${runBets[0].response.nonce}–${runBets[runBets.length - 1].response.nonce}): ` + `${hashes.size} distinct server_seed_hashed among ${runBets.length} bets` ); }});if (runs.length !== byHash.size) { failures.push( `${runs.length} epochs in capture order but ${byHash.size} distinct server_seed_hashed values — ` + `an epoch was split across commitments or two epochs share one` );}server_seed_hashed, and 162 distinct commitments. 0 mid-epoch changes.1.4Commitment Timing (Capture Records)
Steps 1–3 are consistency checks: a seed and hash pair made after settlement would pass them too. Timing comes from the capture. Every rotation response (POST /api/v2/client-seed/rotate) returns the new server_seed_hashed and next_server_seed_hash, and the capture stored them as the epoch’s seed entry before it placed the epoch’s first bet. The first epoch’s hash was already outstanding as “next” at the pre-capture reading.
| Property | Value |
|---|---|
| Epochs with bets | 162 |
| Seed entry recorded before the first bet | 162 / 162 |
| Lead time before the first bet | 1.1 to 11.3 seconds (capture timestamps; measured, not scored) |
| Pre-capture reading | The next-seed hash read before the first rotation equals epoch 0’s commitment (Step 2) |
1.5Client Seed Origin & Control
On Duel the browser generates the client seed and submits it with POST /api/v2/client-seed/rotate. The response carries only the new server_seed_hashed, the next_server_seed_hash, the echoed client_seed and the reset nonce: the server does not generate or assign the client seed. Players can set their own client seed at any time through the fairness modal, and it is an input to every HMAC-SHA256 computation.
Where this capture’s client seeds came from: for Phases A–C our capture script generated each epoch’s seed at capture time with Math.random, and they are recorded with every bet. Phase D used ten seeds built as 'pfaudit' + Date.now() in base 36, which are clock-derived and therefore guessable. Every bet still recomputes from its recorded seed, and Pass 2 (S4.5) tests the server seeds they were paired with.
0fFB4mFVNIQOSDzR3FfHxJWEayg31gaNKWooaSzlek9LYZzcLPzKd5K1ULzrG2XcMAAxNnpj1uB4AobA
pfaudit seeds in Phase D. Evidence: data/plinko-master-8100bets.json and the rotation-response screenshot.1.6Nonce Incrementation
The nonce starts at 0 and counts up by one per bet under the active server seed; it resets when the seed pair is rotated. The 50-bet epochs are the capture’s own rotation interval, not a Duel rule.
In two epochs our capture lost one bet response (nonce 20 and nonce 32). Duel had processed those bets, so the next bet received the next nonce (21 and 33) and the epoch ran to nonce 50. We reconstructed both missed outcomes from the revealed server seeds, which hash to the pre-bet commitments: slot 8 in both, on 16 rows. The capture did not witness them, so Step 4 raises a capture flag. It is limited by our capture script, not a Duel issue, and it does not count against the verdict.
for (const [hash, epochBets] of byHash) { const sorted = [...epochBets].sort((a, b) => a.response.nonce - b.response.nonce); const shortHash = hash.substring(0, 16); const nonces = sorted.map(b => b.response.nonce); const clientSeeds = new Set(sorted.map(b => b.response.client_seed)); if (clientSeeds.size !== 1) { hardFailures.push(`Epoch ${shortHash}: ${clientSeeds.size} distinct client seeds`); } if (nonces[0] !== 0) { hardFailures.push(`Epoch ${shortHash}: first nonce is ${nonces[0]} (expected 0)`); } const hasNonce50 = nonces.includes(50); const missingNonces = Array.from({ length: 51 }, (_, i) => i).filter(i => !nonces.includes(i)); const isRetryPattern = hasNonce50 && missingNonces.length === 1 && nonces.length === 50;Reconstructing a missed nonce:
if (isRetryPattern) { const missedNonce = missingNonces[0]; const seedEntry = revealedMap.get(hash); const clientSeedVal = sorted[0].response.client_seed; const rowsSet = new Set(sorted.map(b => b.request.rows)); // A missed nonce is RECONSTRUCTED, not verified: when the revealed server seed hashes to // the commitment the epoch's bets carried, the outcome computed from it is the one that // seed fixes, but the capture never saw the server's response for it. The hash match is a // consistency check (P1), not a witness, so these are a capture-origin FLAG (L2), never a // PASS. Reconstruction is gated on that hash match; without it the nonce is unverifiable. const commitmentVerified = seedEntry ? verifyHash(seedEntry.seed.serverSeed!, hash) : false; if (seedEntry && rowsSet.size === 1 && commitmentVerified) { const rows = sorted[0].request.rows; const computedSlot = computeSlot(seedEntry.seed.serverSeed!, clientSeedVal, missedNonce, rows); reconstructedDetails.push({ epoch: shortHash, missedNonce, rows, computedSlot }); captureArtifacts.push( `Epoch ${shortHash}: capture-retry — nonce ${missedNonce} missed live; reconstructed from the revealed server seed, which hashes to the pre-bet commitment (computed slot=${computedSlot}); the capture did not witness this outcome` );1.7Deterministic Mapping
The RNG is fully deterministic: the same server seed, client seed, nonce and row count always produce the same slot. The server seed is hex-decoded to 32 raw bytes and used as the HMAC-SHA256 key. The message for each row is clientSeed:nonce:cursor, where cursor is the zero-based row index. The first 4 bytes of each digest are read as a big-endian uint32, and u mod 2 decides the bounce: 1 moves right, 0 moves left. The slot is the number of right-bounces.
// §2 Steps 1–3: slot in 0 … rows.export function computeSlotFromBuffer(key: Buffer, clientSeed: string, nonce: number, rows: number): number { return computePathFromBuffer(key, clientSeed, nonce, rows).slot;} // §1.1 / §2 Step 1: the server seed is 64 hex characters, and the HMAC key is// the 32 bytes they encode (not the ASCII text).function decodeServerSeed(serverSeed: string): Buffer { if (typeof serverSeed !== "string" || serverSeed.length !== 64 || !HEX_RE.test(serverSeed)) { throw new TypeError("serverSeed must be 64 hex characters"); } return Buffer.from(serverSeed, "hex");} export function computeSlot(serverSeed: string, clientSeed: string, nonce: number, rows: number): number { return computeSlotFromBuffer(decodeServerSeed(serverSeed), clientSeed, nonce, rows);}final_slot, 0 mismatches, 0 skipped.Real Bet Verified:
// Source: data/plinko-master-8100bets.json// Bet ID: 71591629 (Phase A, 8 rows, high risk, nonce 0)// ✅ VERIFIED — slot recomputed from revealed server seed { "serverSeed": "5de225f630d2de838265252752ab4ba050a3f20a53711e23a0a43979abf755bd", "serverSeedHashed": "9fae5bb7897874cb71d7bd1be6dca522ddcd8f0c8f18ecaab9c5474d63b9be5a", "clientSeed": "MAAxNnpj1uB4AobA", "nonce": 0, "rows": 8, "risk_level": "high", "final_slot": 3, "payout_multiplier": "0.30253628", "win_amount": "0.0030253628"}Verification:
// computeSlot("5de225f6...", "MAAxNnpj1uB4AobA", 0, 8) // For each cursor 0..7:// message = "MAAxNnpj1uB4AobA:0:{cursor}"// hmac = HMAC-SHA256(hexDecode("5de225f6..."), message)// slot += parseInt(hmac[0..7], 16) % 2 // Final slot: 3 ✅// Multiplier (high/8, slot 3): 0.30253628× ✅// Payout: 0.01 × 0.30253628 = 0.0030253628 ✅1.8Client Seed Influence
All 8,100 bets were dropped again with a wrong client seed (WRONG_CLIENT_SEED_FOR_AUDIT_TEST) on the same server seed and nonce. Some coincidence is expected by chance, so Step 6 scores two statistics against the exact Poisson-binomial null of each bet’s own board rather than a round-number rate. The ordered path coincides with probability 2^-rows. The slot coincides far more often: on a 12-row board two independent drops land in the same slot about 16% of the time. An excess of coincidences would mean the client seed is not reaching the HMAC.
| Statistic | Observed | Expected by chance | p (survival) | Threshold |
|---|---|---|---|---|
| Same ordered path | 10 | 5.16 | 0.038 | α = 0.001 |
| Same landing slot | 1,281 | 1,275.86 | 0.442 | α = 0.001 |
for (const [hash, epochBets] of byHash) { const seedEntry = revealedMap.get(hash); if (!seedEntry || epochBets.length !== 50) continue; const serverSeed = seedEntry.seed.serverSeed!; const key = Buffer.from(serverSeed, 'hex'); let changed = 0; for (const bet of epochBets) { const { client_seed, nonce } = bet.response; const { rows } = bet.request; const real = computePathFromBuffer(key, client_seed, nonce, rows); const wrong = computePathFromBuffer(key, wrongClientSeed, nonce, rows); if (wrong.slot !== real.slot) changed++; else sameSlotCount++; if (wrong.path === real.path) samePathCount++; pathNullPs.push(Math.pow(2, -rows)); slotNullPs.push(slotCoincidenceProb(rows)); totalChecked++; } totalChanged += changed; epochResults.push({ hash: hash.substring(0, 20) + '...', changed, total: epochBets.length }); if (changed === 0) { failures.push(`Epoch ${hash.substring(0, 16)}: wrong client seed produced 0 changed slots — client seed may not be in HMAC`); }}Technical Evidence & Verification5 evidence groups

1.9Evidence Coverage Summary7 checks

| Verification Area | Coverage | Result |
|---|---|---|
| Seed hash integrity (Step 1) | 162 / 162 commitments, 3 declared phase-boundary exemptions | Pass |
| Next-seed promotion (Step 2) | 166 / 166 rotations, anchored before epoch 0 | Pass |
| Hash consistency (Step 3) | 162 epochs, 162 distinct commitments | Pass |
| Commitment timing (capture records) | 162 / 162 recorded before the first bet | Info |
| Nonce audit (Step 4) | 162 epochs sequential; 2 capture retries reconstructed | Capture flag |
| Slot recomputation (Step 5) | 8,100 / 8,100 | Pass |
| Client seed influence (Step 6) | Path 10 vs 5.16 expected; slot 1,281 vs 1,275.86 | Pass |
1.10Code References6 source files

| File | Purpose |
|---|---|
| tests/verify.ts | 23-step verification suite (Steps 1–6 cover S1) |
| tests/steps/commitment.ts | Steps 1–4: commitments, next-seed promotion, hash consistency, nonce audit |
| tests/steps/determinism.ts | Steps 5–6: slot recomputation and client seed influence |
| src/rng.ts | HMAC-SHA256 slot computation and verifyHash, rebuilt from docs/ALGORITHM.md |
| src/loader.ts | Dataset loading, pinned population constants and the dataset hash |
| capture/capture-auto.reference.js | Reference record of the capture script that wrote the dataset (not runnable) |

1.11Datasets UsedSource artifacts


| Property | Value |
|---|---|
| Source | Live Plinko bets captured from Duel.com on 10 April 2026 |
| Total Records | 8,100 bets across 162 epochs (166 seed entries) |
| SHA-256 | 3cf9359d88220bc800bb32edfe04399f55b909302262928ee3a0582715635267 |
Fields used: bets — server_seed_hashed, client_seed, nonce, rows, risk_level, final_slot; seed entries — serverSeed, serverSeedHashed, nextServerSeedHash, nextSeedPromotion
1.12Verified Invariants8 invariants

| Invariant | Result |
|---|---|
| SHA-256(hexDecode(serverSeed)) equals the commitment for all 162 revealed seeds | Pass |
| Next-seed promotion links all 166 rotations, anchored before epoch 0 | Pass |
| server_seed_hashed constant within each of 162 epochs | Pass |
| Nonces sequential from 0 with no repeat in every epoch | Pass |
| Two missed nonces reconstructed from commitment-matching revealed seeds | Capture flag |
| Same inputs produce the same slot for all 8,100 bets | Pass |
| Wrong client seed: path and slot coincidences within the exact null (α = 0.001) | Pass |
| Client seed set in the browser and echoed, not assigned, by the server | Pass |
1.13Reproduction InstructionsRun locally

Clone the release, install dependencies and run the suite:
git clone https://github.com/ProvablyFair-org/duel-plinko.gitcd duel-plinkogit checkout v1.4.2npm cinpm test # Steps 1–6 cover S1Steps 1–6 cover Seed, Nonce & Determinism. Expected output:
[PASS] Step 1 — Seed Hash Integrity
[PASS] Step 2 — Next-Seed Promotion (Commitment Linkage)
[PASS] Step 3 — Hash Consistency Within Epoch
[FLAG:capture] Step 4 — Nonce Audit
[PASS] Step 5 — Slot Recomputation & Bit-Extraction Bound
[PASS] Step 6 — Client Seed Influence (exact null)RNG & Entropy Model
Is the randomness genuinely random, or could it be rigged?
This section verifies that Duel.com’s Plinko RNG produces unbiased outputs from the disclosed inputs only. The RNG uses HMAC-SHA256 with one call per row: each row’s bounce comes from the first 4 bytes of the digest, reduced to left or right with u mod 2. The RNG code in the audit is our own implementation, rebuilt from a written specification by an implementer who never opened Duel’s code. Duel’s own published Verify-tab code is run unmodified as a cross-check only.
One HMAC-SHA256 draw per row, an exact 50/50. Our code is written from the spec; Duel’s code is a cross-check.
Cryptographic Randomness Verification
What we verified
- HMAC-SHA256 per row, keyed with the hex-decoded server seed: the algorithm Duel publishes
- Only disclosed inputs affect outcomes: 8,100 / 8,100 slots reproduce from server seed, client seed, nonce and rows
u mod 2on a uint32 has exactly zero modulo bias, computed from the extraction parameters- Our RNG code is rebuilt from a written spec and passes the spec’s own 71 self-test checks
- Duel’s Verify-tab code, run unmodified, agrees with ours on every bet’s slot and path
- 27M simulated rounds are consistent with binomial B(rows, 0.5) and show no serial correlation
What this means for you
- Each row’s bounce is an exact 50/50 and the extraction cannot skew it
- No hidden randomness or server-side state influences the ball’s path
- Consecutive bets showed no correlation across 27M simulated rounds
- The algorithm depends only on seeds you can verify
- The audit does not depend on trusting Duel’s code: the RNG was rebuilt from the spec
- HMAC-SHA256 per row, keyed with the hex-decoded server seed: the algorithm Duel publishes
- Only disclosed inputs affect outcomes: 8,100 / 8,100 slots reproduce from server seed, client seed, nonce and rows
u mod 2on a uint32 has exactly zero modulo bias, computed from the extraction parameters- Our RNG code is rebuilt from a written spec and passes the spec’s own 71 self-test checks
- Duel’s Verify-tab code, run unmodified, agrees with ours on every bet’s slot and path
- 27M simulated rounds are consistent with binomial B(rows, 0.5) and show no serial correlation
- Each row’s bounce is an exact 50/50 and the extraction cannot skew it
- No hidden randomness or server-side state influences the ball’s path
- Consecutive bets showed no correlation across 27M simulated rounds
- The algorithm depends only on seeds you can verify
- The audit does not depend on trusting Duel’s code: the RNG was rebuilt from the spec
RNG derived only from disclosed inputsPass
HMAC-SHA256(hexDecode(serverSeed), clientSeed:nonce:cursor); 8,100 / 8,100 reproduce with no other input (Step 5)Entropy purityPass
Algorithm independently implementedPass
src/rng.ts rebuilt from docs/ALGORITHM.md by an implementer who never opened Duel’s code; 71 spec self-test checks passOperator code cross-checkPass
Modulo biasPass
Key encoding verifiedPass
Serial independencePass
The Plinko RNG uses only the disclosed inputs and has zero modulo bias. Our own implementation, written from the spec, reproduces all 8,100 live bets, and Duel’s own Verify-tab code agrees on every one. 27M simulated rounds are consistent with the binomial model and show no serial dependence.
| Check | Result | Evidence |
|---|---|---|
| RNG derived only from disclosed inputs | Pass | HMAC-SHA256(hexDecode(serverSeed), clientSeed:nonce:cursor); 8,100 / 8,100 reproduce with no other input (Step 5) |
| Entropy purity | Pass | No timestamps, external APIs, Math.random or server-side state; drand is not part of the Plinko RNG |
| Algorithm independently implemented | Pass | src/rng.ts rebuilt from docs/ALGORITHM.md by an implementer who never opened Duel’s code; 71 spec self-test checks pass |
| Operator code cross-check | Pass | Duel’s Verify-tab code, copied 25 Sep 2026 and run unmodified: bucket and L/R path equal ours on 8,100 / 8,100 (Step 5) |
| Modulo bias | Pass | Bias 0, computed from 8 hex characters and modulus 2, against the 2^-32 ceiling (Step 5) |
| Key encoding verified | Pass | Server seed hex-decoded to 32 bytes, not used as UTF-8 text; confirmed by the 8,100-bet recomputation |
| Serial independence | Pass | 0 / 27 configurations fail the lag-1 or runs test at 1M rounds each (Step 19) |
RNG derived only from disclosed inputsPass
HMAC-SHA256(hexDecode(serverSeed), clientSeed:nonce:cursor); 8,100 / 8,100 reproduce with no other input (Step 5)Entropy purityPass
Algorithm independently implementedPass
src/rng.ts rebuilt from docs/ALGORITHM.md by an implementer who never opened Duel’s code; 71 spec self-test checks passOperator code cross-checkPass
Modulo biasPass
Key encoding verifiedPass
Serial independencePass
The Plinko RNG uses only the disclosed inputs and has zero modulo bias. Our own implementation, written from the spec, reproduces all 8,100 live bets, and Duel’s own Verify-tab code agrees on every one. 27M simulated rounds are consistent with the binomial model and show no serial dependence.
How It Works — RNG & Entropy Model8 sections
2.1RNG Function Implementation
Each Plinko bet resolves one row at a time. For a board with rows rows, the algorithm runs rows HMAC-SHA256 computations and adds up the bits. The HMAC key is the server seed hex-decoded to 32 raw bytes. The message for each row is clientSeed:nonce:cursor, where cursor is the zero-based row index and the nonce is printed in plain base 10. The first 8 hex characters (4 bytes) of each digest are read as a big-endian uint32, and u mod 2 gives the bounce: 1 = right (slot increments), 0 = left.
| Component | Detail |
|---|---|
| Hash function | HMAC-SHA256 |
| Key | Buffer.from(serverSeed, 'hex') — 32 bytes |
| Message | clientSeed:nonce:cursor |
| Extraction | First 8 hex chars → parseInt(hex, 16) → uint32 |
| Reduction | uint32 % 2 → 0 (left) or 1 (right) |
| Accumulation | slot += bit for each cursor 0 to rows−1 |
| Output range | 0 to rows (inclusive) |
// §2 Step 1: digest_i = HMAC-SHA256(key, UTF-8(clientSeed + ":" + nonce + ":" + i)).function rowDigestHex(key: Buffer, clientSeed: string, nonce: number, i: number): string { // String(n) of a non-negative safe integer is plain base 10 with no padding, // sign, separators or exponent (§2 Step 1, decimal(x)). const message = `${clientSeed}:${String(nonce)}:${String(i)}`; return createHmac("sha256", key).update(Buffer.from(message, "utf8")).digest("hex");} // §2 Steps 1–3, also returning the per-row bits packed with row 0 as the// highest of `rows` bits (INTERFACE.md convention; §6 O2 leaves on-screen// orientation undetermined, the packing is not a left/right claim).export function computePathFromBuffer( key: Buffer, clientSeed: string, nonce: number, rows: number,): { slot: number; path: number } { checkArgs(clientSeed, nonce, rows); let slot = 0; let path = 0; // §2 Step 1: cursor i runs 0 … rows−1, one HMAC per row. for (let i = 0; i < rows; i++) { const bit = directionBit(rowDigestHex(key, clientSeed, nonce, i)); // §2 Step 3: slot is the count of 1-bits. slot += bit; // Shift left then add: row 0 ends up in the highest of the `rows` bits. // rows ≤ 16, so this never leaves the safe 31-bit range of `<<`. path = (path << 1) | bit; } return { slot, path };}docs/ALGORITHM.md by an implementer who read only that spec and a module-interface file, and tests/plinko/RngSpecTests.ts runs the spec’s own vectors and properties against it (71 checks).The direction bit:
// §2 Step 2: bit = (first 4 digest bytes as big-endian u32) mod 2.export function directionBit(hmacHex: string): number { const { hexChars, modulus } = BIT_EXTRACTION; if (hmacHex.length < hexChars || !HEX_RE.test(hmacHex)) { throw new TypeError(`directionBit: expected a hex digest of at least ${hexChars} hex characters`); } // parseInt on 8 hex chars reads them most-significant first, i.e. big-endian. const u = parseInt(hmacHex.slice(0, hexChars), 16); return u % modulus;}2.2Entropy Sources
All randomness derives exclusively from the deterministic HMAC-SHA256 function combining four cleanly separated inputs:
| Source | Controlled By | Purpose |
|---|---|---|
| Server Seed | Casino | Base randomness (committed via SHA-256 hash before betting) |
| Client Seed | Player | Player-contributed entropy |
| Nonce | System | Uniqueness per bet (increments automatically) |
| Cursor | System | Per-row isolation (0 to rows-1) |
How we know: 8,100 / 8,100 bets were recomputed from the four declared inputs alone. If any hidden entropy source existed, recomputation would fail. It does not.
Verified absent: no timestamps, no Math.random(), no external APIs, no server-side mutable state, and no drand. Only: HMAC-SHA256(hexDecode(serverSeed), clientSeed:nonce:cursor)
2.3Modulo Bias Analysis
Each row’s bounce is parseInt(digest[0..7], 16) % 2, a uint32 modulo 2. Modulo bias occurs when the number of possible values does not divide evenly by the modulus. For modulus 2 there is exactly zero bias: 2^32 = 4,294,967,296 divides evenly by 2, giving exactly 2,147,483,648 values for each direction. Step 5 computes this bound from the parameters the code reads (8 hex characters, modulus 2) rather than asserting it, and compares it with the 2^-32 ceiling. No draw is rejected.
2^32 = 4,294,967,296
4,294,967,296 / 2 = 2,147,483,648  (exact, no remainder)

Even values in [0, 2^32 - 1]: 2,147,483,648  → left  (50.000%)
Odd  values in [0, 2^32 - 1]: 2,147,483,648  → right (50.000%)

Bias: 0.000%const { hexChars, modulus, rejectionSampling } = BIT_EXTRACTION;// Number of distinct values the consumed hex prefix can take.const domainSize = 16 ** hexChars;const remainder = domainSize % modulus;// Each residue gets floor(domain/modulus) values; `remainder` residues get one extra.const minResidueCount = Math.floor(domainSize / modulus);const maxResidueCount = minResidueCount + (remainder === 0 ? 0 : 1);// With rejection sampling, the top `remainder` values would be discarded and// every residue would be exactly uniform. Without it, the worst residue is// off from 1/modulus by (maxCount/domain - 1/modulus).const rejectedDraws = rejectionSampling ? remainder : 0;let bias: number;if (rejectionSampling || remainder === 0) { bias = 0;} else { const hi = Math.abs(maxResidueCount / domainSize - 1 / modulus); const lo = Math.abs(minResidueCount / domainSize - 1 / modulus); bias = Math.max(hi, lo);}A modulus that does not divide 2^32, such as 37, would leave some residues one value richer than others and need rejection sampling. Modulus 2 needs none, so each row is an exact 50/50 decision.
2.4RNG Isolation
Each row within a single bet uses a unique cursor value in the HMAC message (clientSeed:nonce:cursor), ensuring per-row outputs are cryptographically independent. Each bet uses a unique nonce, ensuring per-bet outputs are independent. HMAC-SHA256 is a pseudorandom function — knowing one row’s output gives zero information about other rows’ outputs. There is no shared state between rows, between bets, or between epochs.
Evidence: the functions in 2.1 are pure. They take the key, client seed, nonce and row count explicitly, keep no state between calls and make no external calls. Same inputs always produce the same output.
2.5Operator Code Cross-Check
Duel publishes its Plinko algorithm in the code panel of duel.com → Provably Fair → Verify (Plinko). We copied it verbatim on 25 September 2026 and pinned it by SHA-256 (2,511 bytes). Step 5 runs it unmodified on all 8,100 captured bets as a second check: its validatePlinkoResult bucket must equal the served final_slot and our result, and the L/R path read from its own prefix sums must equal ours. Duel’s code is not the source of ours; its direction rule, position += (value % 2), matches the spec.
| Comparison | Bets | Result |
|---|---|---|
| Duel bucket vs served final_slot | 8,100 / 8,100 | Pass |
| Duel bucket vs our slot | 8,100 / 8,100 | Pass |
| Duel L/R path vs our path | 8,100 / 8,100 | Pass |
for (const { bet, serverSeed } of siteBets) { const o = op.results.get(String(bet.response.id)); const { client_seed, nonce, final_slot } = bet.response; const { rows } = bet.request; const ref = computePathFromBuffer(Buffer.from(serverSeed, 'hex'), client_seed, nonce, rows); if (o) opChecked++; const opPath = pathFromPrefixes(o?.prefixes ?? null); const bad: string[] = []; if (!o || o.slot !== final_slot) { opSlotVsServed++; bad.push(`bucket ${o?.slot} vs served ${final_slot}`); } if (!o || o.slot !== ref.slot) { opSlotVsRng++; bad.push(`bucket ${o?.slot} vs src/rng.ts ${ref.slot}`); } if (opPath === null || opPath !== ref.path || o?.prefixes?.length !== rows) { opPathVsRng++; bad.push(`path ${opPath === null ? 'unreadable' : pathString(opPath, rows)} vs src/rng.ts ${pathString(ref.path, rows)}`); } if (bad.length && opIssues.length < 10) opIssues.push(`operator Verify-tab code, bet ${bet.response.id}: ${bad.join('; ')}`);}Pinned file:
8b3366d1e91edb572cac288e0a853d2b560b2cf5c4468c6848439f957465c9ce2.6Monte Carlo Simulation (27M Rounds)
A 27,000,000-round simulation (1,000,000 rounds per configuration, all 27) checks the slot distribution at scale. Each configuration plays its own seed pair, generated once and pinned in src/sim-seeds.ts, and npm test replays all 27M rounds and requires every slot count to come back exactly.
| Metric | Value |
|---|---|
| Average simulated RTP | 99.917% |
| Average theoretical RTP | 99.900% |
| Chi-squared (α = 0.01) | 0 / 27 configurations fail |
| Bonferroni-corrected (α/27 = 0.00037) | 0 / 27 fail |
| Serial independence | 0 / 27 fail |
for (let nonce = 0; nonce < rounds; nonce++) { const slot = computeSlotFromBuffer(key, client, nonce, rows); slotCounts[slot]++; hitSequence[nonce] = slot; totalPayout += multipliers[slot]; if (nextSampleIdx < samples.length && (nonce + 1) === samples[nextSampleIdx]) { rtpSnapshots.push({ roundCount: nonce + 1, rtp: (totalPayout / (nonce + 1)) * 100 }); nextSampleIdx++; }}const lag1R = lag1Autocorrelation(hitSequence);const median = rows / 2;const runs = runsTest(hitSequence.map((s: number) => s > median));return { slotCounts, totalPayout, rtpSnapshots, lag1R, runsP: runs.pValue };Chi-squared goodness of fit on the slot counts against the independent binomial B(rows, 0.5); serial independence by lag-1 autocorrelation and the Wald-Wolfowitz runs test. Expected counts come from the binomial, not from the config.
2.7Serial Independence
Serial independence means consecutive outcomes are not correlated: one bet’s result tells you nothing about the next. Two tests were applied to each configuration in the Pass 1 simulation (1,000,000 rounds per config):
Lag-1 autocorrelation: Measures correlation between consecutive slot values. Expected r ≈ 0 for independent sequences. Threshold: |z| > 3 (where z = r × √n).
Wald-Wolfowitz runs test: Tests whether the sequence of above/below-median outcomes has the expected number of runs. p < 0.01 indicates non-random structure.
export function lag1Autocorrelation(values: number[]): number { const N = values.length; if (N < 3) return 0; const mu = values.reduce((a, b) => a + b, 0) / N; const variance = values.reduce((acc, x) => acc + Math.pow(x - mu, 2), 0) / N; if (variance === 0) return 0; let cov = 0; for (let i = 0; i < N - 1; i++) { cov += (values[i] - mu) * (values[i + 1] - mu); } return cov / ((N - 1) * variance);}2.8Worked Example — Full RNG Trace
Real bet from dataset — Bet ID 71596330, 16 rows, high risk, nonce 0. Verified from plinko-master-8100bets.json:
serverSeed  = b22261c6dc661d17db31417fb4a2dd1e58eb351ae7d8c77c6f51a2cd81dc84b9
clientSeed  = 9sysyk9uhCw09FzD
nonce       = 0
rows        = 16
risk = high| cursor | HMAC[:8] | uint32 | % 2 | direction | slot |
|---|---|---|---|---|---|
| 0 | a9c2f13f | 2,848,125,247 | 1 | right | 1 |
| 1 | 14895bdb | 344,546,267 | 1 | right | 2 |
| 2 | 4739337b | 1,194,931,067 | 1 | right | 3 |
| 3 | d74021d8 | 3,611,304,408 | 0 | left | 3 |
| 4 | 54078d16 | 1,409,781,014 | 0 | left | 3 |
| 5 | 6074bdba | 1,618,263,482 | 0 | left | 3 |
| 6 | 09ba0b81 | 163,187,585 | 1 | right | 4 |
| 7 | a0b6ea00 | 2,696,342,016 | 0 | left | 4 |
| 8 | ef0695f6 | 4,010,186,230 | 0 | left | 4 |
| 9 | 9a93d48e | 2,593,379,470 | 0 | left | 4 |
| 10 | 3ff81328 | 1,073,222,440 | 0 | left | 4 |
| 11 | 0ea47ffb | 245,661,691 | 1 | right | 5 |
| 12 | 869a92ab | 2,258,277,035 | 1 | right | 6 |
| 13 | 87a5194b | 2,275,744,075 | 1 | right | 7 |
| 14 | fab89728 | 4,206,401,320 | 0 | left | 7 |
| 15 | 32fcaf56 | 855,420,758 | 0 | left | 7 |
final_slot = 7 matches HMAC-SHA256 recomputation exactly. Multiplier (16r/high, slot 7): 0.20186622×. Payout: 0.01 × 0.20186622 = 0.0020186622.Technical Evidence & Verification5 evidence groups
2.9Evidence Coverage Summary8 checks
| Verification Area | Coverage | Result |
|---|---|---|
| Algorithm implementation (Step 5) | 8,100 / 8,100 bets | Pass |
| Spec self-test (unit tests) | 71 checks from the spec’s vectors and properties | Pass |
| Operator code cross-check (Step 5) | 8,100 / 8,100 bucket and L/R path | Pass |
| Key encoding (hex vs UTF-8) | Confirmed by recomputation | Pass |
| Modulo bias (Step 5) | Computed: bias 0 against the 2^-32 ceiling | Pass |
| External entropy non-participation (Step 5) | 8,100 / 8,100 reproduced from disclosed inputs alone | Pass |
| Simulation chi-squared (Step 19) | 0 / 27 configurations fail at α = 0.01 | Pass |
| Serial independence (Step 19) | 0 / 27 configurations fail (lag-1 and runs test) | Pass |
2.10Code References8 source files
| File | Purpose |
|---|---|
| src/rng.ts | HMAC-SHA256 RNG, rebuilt from the written spec (computeSlot, computePathFromBuffer) |
| docs/ALGORITHM.md | The written specification src/rng.ts is rebuilt from |
| tests/plinko/RngSpecTests.ts | The spec’s own vectors and properties, run against src/rng.ts (71 checks) |
| src/operator-verifier.ts | Pins and runs Duel’s Verify-tab code unmodified, as a second check |
| src/pass1.ts | The Pass 1 loop shared by the simulation and its replay |
| src/stats.ts | Chi-squared, lag-1 autocorrelation, Wald-Wolfowitz runs test |
| tests/steps/determinism.ts | Steps 5–6: slot recomputation, bias bound, verifier legs, client seed influence |
| tests/steps/simulation.ts | Steps 19–20: simulation replay and cherry-pick tests |
2.11Verified Invariants8 invariants
| Invariant | Result |
|---|---|
| HMAC-SHA256 output matches the live game for all 8,100 bets | Pass |
| Key is hex-decoded (not UTF-8); the wrong encoding gives different slots | Pass |
| u mod 2 has zero modulo bias (2^32 is exactly divisible by 2) | Pass |
| No external entropy is needed for slot computation | Pass |
| Duel’s Verify-tab code agrees with our implementation on every bet | Pass |
| Slot distribution consistent with binomial B(rows, 0.5) for all 27 configurations (1M rounds each) | Pass |
| Lag-1 |z| ≤ 3 and runs-test p ≥ 0.01 for all 27 configurations | Pass |
| Simulated RTP within 5 standard errors of theoretical on all 27 configurations | Pass |
2.12Datasets UsedSource artifacts
2.13Reproduction InstructionsRun locally
Clone the release, install dependencies and run the suite:
git clone https://github.com/ProvablyFair-org/duel-plinko.gitcd duel-plinkogit checkout v1.4.2npm cinpm test # Steps 5 and 19 cover S2S2-related steps:
[PASS] Step 5 — Slot Recomputation & Bit-Extraction Bound
[PASS] Step 19 — Simulation Results — Pass 1 Integrity (re-derived & replayed)Verifier Parity
Does the live game actually follow its own rules?
This section checks that our independent verifier produces the exact same slot as the live game for every recorded bet, that every payout follows the multiplier table, and that both ProvablyFair.org player verifiers agree with the audit. Any mismatch would invalidate the fairness guarantee.
Every recorded bet recomputed: 8,100 / 8,100 slots and payouts match. Both player verifiers agree.

Live ↔︎ Verifier Parity
What we verified
- Every bet recomputed from its seeds: the full slot position, not just the payout
- Every multiplier is on the 8-decimal grid, and win_amount = stake × multiplier to relative 1e-12
- Every paid multiplier matches the config’s base-tier table for its rows and risk
- Bet amount is not an input to the RNG: $10 bets are computed the same way, and paid from the same table, as $0.01 bets
- This site’s verifier and www.provablyfair.org/verify-bets were run on all 8,100 bets: slot and path match on every one
- All four capture phases recomputed identically
What this means for you
- The verifier isn’t a simulation: it produces the exact same slot as the live game
- Every bet you play can be independently recomputed by anyone
- Your stake changes the payout amount, not where the ball lands
- The live game followed the published algorithm on every captured bet
- Every bet recomputed from its seeds: the full slot position, not just the payout
- Every multiplier is on the 8-decimal grid, and win_amount = stake × multiplier to relative 1e-12
- Every paid multiplier matches the config’s base-tier table for its rows and risk
- Bet amount is not an input to the RNG: $10 bets are computed the same way, and paid from the same table, as $0.01 bets
- This site’s verifier and www.provablyfair.org/verify-bets were run on all 8,100 bets: slot and path match on every one
- All four capture phases recomputed identically
- The verifier isn’t a simulation: it produces the exact same slot as the live game
- Every bet you play can be independently recomputed by anyone
- Your stake changes the payout amount, not where the ball lands
- The live game followed the published algorithm on every captured bet
Slot recomputationPass
Payout correctnessPass
Multiplier table provenancePass
scaling_edge[0].multipliers; 263 of 351 cells paid live (Step 8)Bet-size independencePass
Player-verifier parityPass
Config completenessPass
Multi-phase coveragePass
All 8,100 bets matched the independent verifier exactly across all four capture phases. Payout math is correct and every paid multiplier comes from the base-tier table. Both ProvablyFair.org player verifiers agree on every slot and path.
| Check | Result | Evidence |
|---|---|---|
| Slot recomputation | Pass | 8,100 / 8,100 exact match, slot position verified for every bet (Step 5) |
| Payout correctness | Pass | All 8,100 multipliers on the 8-decimal grid; win_amount = amount × multiplier at relative 1e-12 (Step 7) |
| Multiplier table provenance | Pass | 8,100 / 8,100 match scaling_edge[0].multipliers; 263 of 351 cells paid live (Step 8) |
| Bet-size independence | Pass | 200 / 200 Phase C bets at $10 recompute on the Phase B board and table (Step 9) |
| Player-verifier parity | Pass | Both ProvablyFair.org verifiers run on all 8,100 bets: slot and path match on every bet (Step 5) |
| Config completeness | Pass | All 27 configurations, 200 Phase A bets each (Step 11) |
| Multi-phase coverage | Pass | Phases A (5,400), B (2,000), C (200) and D (500), all recomputed |
Slot recomputationPass
Payout correctnessPass
Multiplier table provenancePass
scaling_edge[0].multipliers; 263 of 351 cells paid live (Step 8)Bet-size independencePass
Player-verifier parityPass
Config completenessPass
Multi-phase coveragePass
All 8,100 bets matched the independent verifier exactly across all four capture phases. Payout math is correct and every paid multiplier comes from the base-tier table. Both ProvablyFair.org player verifiers agree on every slot and path.
How It Works — Verifier Parity9 sections
3.1Why Parity Matters
If the verifier produced results that differ from the live game, players could not rely on verification at all. Parity has to be 100%: a single discrepancy would mean a bug in the verification logic, a change in the live game, or an inconsistent RNG. Players must be able to take the revealed seeds after play, enter them into an independent verifier, and get the exact slot they saw in the game.
3.2Four-Phase Collection Design
Data was collected across four structured phases, each designed to test a specific fairness property. The phases are complementary — together they cover configuration breadth, statistical depth, bet-size invariance, and client seed verification.
| Phase | Bets | Config | Bet Amount | Purpose |
|---|---|---|---|---|
| A — Configuration coverage | 5,400 | All 27 configs, 200 bets each | $0.01 | Verify every config behaves correctly |
| B — High-variance sampling | 2,000 | 16r/high | $0.01 | Deep binomial distribution test on the highest-variance config |
| C — Code-path equivalence | 200 | 16r/high | $10.00 | Confirm bet amount is not in the RNG |
| D — Client seed verification | 500 | All 27 configs, 18–19 bets each over 10 epochs | $0.01 | Confirm the client seed is genuinely used in the HMAC |
3.3Slot Recomputation (Step 5)
For every bet, the verifier computes the slot with computeSlot(serverSeed, clientSeed, nonce, rows) from the epoch’s revealed server seed and compares it with the server-reported final_slot. A bet whose seed was never revealed would count as a failure, not an exclusion, and the number recomputed must equal the 8,100 declared in src/loader.ts.
for (const [hash, epochBets] of byHash) { const seedEntry = revealedMap.get(hash); if (!seedEntry) { skipped += epochBets.length; continue; } const serverSeed = seedEntry.seed.serverSeed!; for (const bet of epochBets) { const { client_seed, nonce, final_slot } = bet.response; const { rows } = bet.request; const computed = computeSlot(serverSeed, client_seed, nonce, rows); determinismLog.push({ id: bet.response.id, phase: bet.phase, rows, risk: bet.request.risk, nonce, computed_slot: computed, actual_slot: final_slot, match: computed === final_slot, }); if (computed !== final_slot) { failures.push(`bet ${bet.response.id}: computed=${computed} actual=${final_slot} (${rows}r/${bet.request.risk} nonce=${nonce})`); } checked++; }}final_slot.3.4Payout Math (Step 7)
Every served payout_multiplier is an exact multiple of 1e-8, so Step 7 checks it on that grid rather than against a tolerance. The win_amount it produces is a full-precision product with no grid, so it is compared with amount_currency × payout_multiplier at a relative tolerance of 1e-12, sized to double arithmetic. A wrong credited amount is a hard fail, not a flag.
const MULT_DP = 8;const offGrid = (x: number): number => Math.abs(x * 10 ** MULT_DP - Math.round(x * 10 ** MULT_DP));// Slack is IEEE-754 representation error in the scaling and nothing else, sized from the// magnitude of the scaled value rather than picked as a round number.const onGrid = (x: number): boolean => Number.isFinite(x) && offGrid(x) < Math.max(1e-9, Math.abs(x * 10 ** MULT_DP) * 1e-12);const MONEY_REL_TOL = 1e-12; let offGridMults = 0;for (const bet of bets) { const amount = parseFloat(bet.response.amount_currency); const mult = parseFloat(bet.response.payout_multiplier); const win = parseFloat(bet.response.win_amount); if (!onGrid(mult)) { offGridMults++; failures.push(`bet ${bet.response.id} [phase ${bet.phase}]: payout_multiplier ${bet.response.payout_multiplier} is not on the ${MULT_DP}-dp grid (off by ${offGrid(mult).toExponential(2)})`); continue; } const expected = amount * mult; const diff = Math.abs(win - expected); if (!Number.isFinite(win) || diff > MONEY_REL_TOL * Math.max(Math.abs(expected), 1)) { failures.push(`bet ${bet.response.id} [phase ${bet.phase}]: win=${win} expected=${expected} diff=${diff.toExponential(2)}`); }}win_amount = amount_currency × payout_multiplier at relative 1e-12 on every bet. 0 mismatches.3.5Multiplier Table Provenance (Step 8)
plinkoConfig.json carries two multiplier sources: the compact payout_tables and the per-bracket scaling_edge[0].multipliers. They differ on 118 of 351 cells, by at most 1.49×10⁻⁶. Step 8 compares each observed payout_multiplier with both at a 1e-5 tolerance, after checking every slot lies in [0, rows] for its board. Duel pays scaling_edge[0].multipliers: on the 224 bets that landed on a cell where the two sources differ, Step 5 finds the served value equals that table exactly.
| Metric | Count |
|---|---|
| Total bets checked | 8,100 |
| Matching scaling_edge[0] (1e-5) | 8,100 |
| Matching payout_tables (1e-5) | 8,100 |
| Matching neither | 0 |
| Slots outside [0, rows] | 0 |
| Table cells paid live | 263 of 351 |
for (const bet of bets) { const { rows, risk } = bet.request; const { final_slot, payout_multiplier } = bet.response; const observed = parseFloat(payout_multiplier); const ptMult = cfg.payoutTableMultiplier(rows, risk as RiskLevel, final_slot); const seMult = cfg.scalingEdgeMultiplier(rows, risk as RiskLevel, final_slot); const ptMatch = Math.abs(observed - ptMult) <= TOLERANCE; const seMatch = Math.abs(observed - seMult) <= TOLERANCE; if (ptMatch && seMatch) { ptMatches++; seMatches++; } else if (ptMatch) { ptMatches++; ptOnly++; } else if (seMatch) { seMatches++; seOnly++; } else { neither++; if (sampleMismatches.length < 5) { sampleMismatches.push( `bet ${bet.response.id} ${rows}r/${risk} slot=${final_slot}: observed=${observed} pt=${ptMult} se=${seMult}` ); } }}scaling_edge[0].multipliers. Every live payout multiplier matches plinkoConfig.json. The 88 cells no captured bet landed in are checked structurally (Step 13) and their probabilities derived independently (Step 17).3.6Multiplier Symmetry & Floor (Step 13)
For all 27 configurations, the multiplier table is checked for symmetry: multiplier[k] = multiplier[rows − k] for every slot k. This follows from the symmetric binomial distribution: slots k and rows − k are equally likely, so their multipliers should match. Live bets also confirm their multipliers against the same table, and the 16r/high centre slot is checked against its 0.2× floor.
for (const { rows, risk } of cfg.allConfigs()) { const configBets = bets.filter(b => b.request.rows === rows && b.request.risk === risk); for (const bet of configBets) { const observed = parseFloat(bet.response.payout_multiplier); const se = cfg.scalingEdgeMultiplier(rows, risk as RiskLevel, bet.response.final_slot); if (Math.abs(observed - se) > TOLERANCE) { failures.push(`EC-12: ${rows}r/${risk} slot=${bet.response.final_slot}: diff=${Math.abs(observed - se).toExponential(2)}`); } } const slot0 = cfg.scalingEdgeMultiplier(rows, risk as RiskLevel, 0); const slotN = cfg.scalingEdgeMultiplier(rows, risk as RiskLevel, rows); if (Math.abs(slot0 - slotN) > TOLERANCE) { failures.push(`EC-10: ${rows}r/${risk}: slot0=${slot0} ≠ slotN=${slotN}`); } for (let k = 0; k <= rows; k++) { const mk = cfg.scalingEdgeMultiplier(rows, risk as RiskLevel, k); const mk_mirror = cfg.scalingEdgeMultiplier(rows, risk as RiskLevel, rows - k); if (Math.abs(mk - mk_mirror) > TOLERANCE) { failures.push(`EC-14: ${rows}r/${risk} slot ${k} vs ${rows - k}: ${mk} ≠ ${mk_mirror}`); } } if (rows === 16 && risk === 'high') { const center = cfg.scalingEdgeMultiplier(16, 'high', 8); if (center < 0.2) { failures.push(`EC-13: 16r/high center slot multiplier=${center} < 0.2 (0.2× floor violated)`); } }3.7Phase C — Bet-Size Equivalence (Step 9)
Phase C placed 200 bets at $10 on 16r/high, the same board as Phase B’s $0.01 bets, so stake is the only variable that moved. Step 9 reads both boards from the data rather than naming them. All 200 slots recompute from the revealed seeds and all 200 multipliers match the same scaling_edge[0].multipliers table. Equivalence is shown deterministically: at n = 200 a distributional test would have almost no power and add nothing.
for (const bet of phaseC) { const seedEntry = revealedMap.get(bet.response.server_seed_hashed); if (!seedEntry) { slotSkipped++; continue; } const computed = computeSlot( seedEntry.seed.serverSeed!, bet.response.client_seed, bet.response.nonce, bet.request.rows ); if (computed !== bet.response.final_slot) { failures.push(`EC-15: bet ${bet.response.id} slot mismatch: computed=${computed} actual=${bet.response.final_slot}`); } slotChecked++;}3.8Player-Verifier Parity (Step 5)
Two ProvablyFair.org verifiers a player can paste a Duel Plinko bet into are pinned by SHA-256 and executed on all 8,100 captured bets: this site’s verifier and the main-site verifier at www.provablyfair.org/verify-bets. Each must give the same slot and ordered L/R path as the audit on every bet. The main-site page also prints the commitment hash and a display-rounded multiplier, and both must agree with the capture.
| Verifier | Executed on | Slot and path | Multiplier |
|---|---|---|---|
This site’s verifier (verify-bets) | 8,100 / 8,100 | 8,100 / 8,100 | Differs from the paid value on 224 bets, by at most 1.1×10⁻⁷ |
| www.provablyfair.org/verify-bets | 8,100 / 8,100 | 8,100 / 8,100 | Display-rounded value agrees on 8,100 / 8,100 |
for (const { bet, serverSeed } of siteBets) { const p = live.printed.get(String(bet.response.id)); const { client_seed, nonce, final_slot, payout_multiplier, server_seed_hashed } = bet.response; const { rows } = bet.request; const ref = computePathFromBuffer(Buffer.from(serverSeed, 'hex'), client_seed, nonce, rows); const served = parseFloat(payout_multiplier); const shown = p?.multiplierText == null ? NaN : parseFloat(p.multiplierText); const halfUnit = p?.multiplierDecimals == null ? NaN : 0.5 * Math.pow(10, -p.multiplierDecimals); const ok = !!p && p.slotFromDirection === final_slot && p.slotFromBuckets === final_slot && ref.slot === final_slot && p.bucketCount === rows + 1 && p.path === pathString(ref.path, rows) && p.serverSeedHash === server_seed_hashed // The page prints the paytable cell rounded for display ("0.30x"); the served multiplier // must round to what it printed: |printed − served| ≤ half a unit of the printed precision. && Math.abs(shown - served) <= halfUnit + 1e-12; if (p) liveChecked++; if (!ok) { liveMismatch++; if (siteIssues.length < 10) siteIssues.push(`live-site verifier, bet ${bet.response.id}: printed ${JSON.stringify(p)}; src/rng.ts slot ${ref.slot} path ${pathString(ref.path, rows)}; served slot ${final_slot} ×${payout_multiplier}`); }}payout_tables, while Duel pays scaling_edge[0].multipliers. The gap is at most 1.1×10⁻⁷ on 224 bets across 53 cells; slot and path are unaffected. The audit requires the gap to be exactly this, so any change to either verifier shows up in Step 5.3.9Worked Example — Full Parity Verification
Real bet from Phase B — Bet ID 71644262, 16 rows, high risk, nonce 5. Verified from plinko-master-8100bets.json:
serverSeed  = 7b8c38d84c6d187c472c4e3f1e668222d64cfca099ca6127ad0e1cd198faf5b6
clientSeed  = S8Wfb9k9Uyie6M9D
nonce       = 5
rows        = 16
risk = high| Step | Process | Output |
|---|---|---|
| 1 | HMAC-SHA256(hexDecode(serverSeed), "S8Wfb9k9Uyie6M9D:5:0") through cursor 15 | 16 uint32 values |
| 2 | Each uint32 % 2 → left/right bounce | 9 right bounces |
| 3 | final_slot = 9 | Matches live game ✅ |
| 4 | Multiplier lookup: 16r/high slot 9 | 0.20186622× |
| 5 | Payout: 0.01 × 0.20186622 | 0.0020186622 ✅ |
// computeSlot("7b8c38d8...", "S8Wfb9k9Uyie6M9D", 5, 16)// 16 HMAC calls → slot = 9//// Multiplier lookup: scaling_edge["16"]["high"][0].multipliers[9]// = 0.20186622//// Payout: 0.01 × 0.20186622 = 0.0020186622// Live win_amount: 0.0020186622 ✅Technical Evidence & Verification5 evidence groups
3.10Evidence Coverage Summary9 checks
| Verification Area | Coverage | Result |
|---|---|---|
| Slot recomputation | 8,100 / 8,100 bets, full slot position | Pass |
| Payout math | 8,100 / 8,100 bets, 8-decimal grid and relative 1e-12 | Pass |
| Multiplier table provenance | 8,100 / 8,100 match scaling_edge[0]; 263 / 351 cells paid | Pass |
| Multiplier symmetry | 27 / 27 configurations, slot k = slot rows − k | Pass |
| Phase C slot recomputation | 200 / 200 at $10 | Pass |
| Phase C multiplier match | 200 / 200, same table as $0.01 | Pass |
| Player verifiers (Step 5) | Both run on 8,100 / 8,100; slot and path match | Pass |
| Config completeness | All 27 configurations, 200 Phase A bets each | Pass |
| Multi-phase coverage | A (5,400) + B (2,000) + C (200) + D (500) | Pass |
3.11Code References7 source files
| File | Purpose |
|---|---|
| tests/steps/determinism.ts | Step 5: slot recomputation and the verifier legs |
| tests/steps/payouts.ts | Steps 7–9: payout math, multiplier provenance, Phase C equivalence |
| tests/steps/dataset.ts | Steps 10–16: config completeness, epoch size, symmetry, scaling edge |
| src/rng.ts | HMAC-SHA256 slot computation |
| src/config.ts | Multiplier lookup and theoretical RTP |
| src/site-verifier.ts | Pins and runs this site’s verifier on every bet |
| src/live-site-verifier.ts | Pins and runs the www.provablyfair.org/verify-bets bundle on every bet |
3.12Datasets UsedSource artifacts
3.13Verified Invariants9 invariants
| Invariant | Result |
|---|---|
| Computed slot matches live final_slot for all 8,100 bets | Pass |
| Every payout_multiplier lies on the 8-decimal grid | Pass |
| win_amount = amount × multiplier at relative 1e-12 for all 8,100 bets | Pass |
| Every payout_multiplier matches scaling_edge[0] for its row and risk | Pass |
| Multiplier tables are symmetric for all 27 configurations | Pass |
| Phase C ($10) recomputes on the Phase B board with the same table | Pass |
| Both ProvablyFair.org verifiers give the audit’s slot and path on every bet | Pass |
| All 27 row/risk configurations present in live data | Pass |
| Phase D: 500 / 500 slots verified across 10 client seeds | Pass |
3.14Reproduction InstructionsRun locally
git clone https://github.com/ProvablyFair-org/duel-plinko.gitcd duel-plinkogit checkout v1.4.2npm cinpm test # Steps 5, 7–9, 11 and 13 cover S3S3-related steps:
[PASS] Step 5 — Slot Recomputation & Bit-Extraction Bound
[PASS] Step 7 — Payout Math
[PASS] Step 8 — Multiplier Table Provenance
[PASS] Step 9 — Phase C Code-Path Equivalence
[PASS] Step 11 — Config Completeness & Cell Coverage
[PASS] Step 13 — Multiplier Table + SymmetryRTP & Payout Logic
Is the house edge what the casino claims?
This section verifies the 0.1% house edge at the base stake tier on all 27 configurations. The theoretical RTP is derived from first principles: independently computed binomial probabilities applied to the multiplier table Duel pays, with no operator probability or RTP figure used. The RTP claim rule then holds Duel’s published 99.9% against every setting, and 27 million simulated rounds and a cherry-pick test check the implementation in practice.
Theoretical RTP is 99.9% on all 27 settings, and Duel’s published 99.9% holds on every one.

Return to Player Verification
What we verified
- Theoretical RTP from first principles: binomial P(slot) × the paid multiplier table = 99.9% on every configuration
- Duel’s published 99.9% holds on all 27 settings, inside the RTP claim rule’s ±0.1 pp band
- 27M simulated rounds are consistent with the theoretical RTP (mean 99.917%)
- Cherry-pick screening on all 162 revealed seeds finds no sign of seed pre-selection
- Bet amount does not influence the slot: confirmed at $0.01 and $10
What this means for you
- At the base stake tier, the house edge is a flat 0.1% on every board and risk level
- The RTP is derived from probabilities we compute ourselves, not from the casino’s own figure
- The casino’s seeds show no sign of being chosen to produce favourable early outcomes
- Your bet amount doesn’t affect where the ball lands
- Larger stakes move into higher tiers with a higher edge: see S4.7
- Theoretical RTP from first principles: binomial P(slot) × the paid multiplier table = 99.9% on every configuration
- Duel’s published 99.9% holds on all 27 settings, inside the RTP claim rule’s ±0.1 pp band
- 27M simulated rounds are consistent with the theoretical RTP (mean 99.917%)
- Cherry-pick screening on all 162 revealed seeds finds no sign of seed pre-selection
- Bet amount does not influence the slot: confirmed at $0.01 and $10
- At the base stake tier, the house edge is a flat 0.1% on every board and risk level
- The RTP is derived from probabilities we compute ourselves, not from the casino’s own figure
- The casino’s seeds show no sign of being chosen to produce favourable early outcomes
- Your bet amount doesn’t affect where the ball lands
- Larger stakes move into higher tiers with a higher edge: see S4.7
Anti-circularityPass
RTP claim rulePass
Simulated RTP (Pass 1)Pass
Cherry-pick screening (Pass 2)Pass
Bet-size invariancePass
PayoutsPass
scaling_edge[0].multipliers (Steps 5, 7 and 8)Stake tiersInfo
Zero Edge auditPass
effective_edge groups pay from the same table at the captured stakes (Step 10)The 99.9% theoretical RTP is derived from first principles on all 27 configurations, an exact identity rather than a statistical estimate, and Duel’s published 99.9% holds on every setting under the RTP claim rule. 27M simulated rounds are consistent with it, and the cherry-pick tests find no sign of seed selection.
RTP claim rule: Duel’s published 99.9% holds on all 27 settings (0 outside ±0.1 pp).
| Check | Result | Evidence |
|---|---|---|
| Anti-circularity | Pass | 351 probabilities equal the independent binomial; Σ P × multiplier = 99.9% on all 27 configurations; 130,816 paths walked (Step 17) |
| RTP claim rule | Pass | Published 99.9% (game settings) held against all 27 settings: 0 outside ±0.1 pp, true RTP 99.900000% on every one (Step 19) |
| Simulated RTP (Pass 1) | Pass | 27M rounds replayed from pinned seeds; mean 99.917%; 0 / 27 chi-squared fails; largest gap 1.79 standard errors (Step 19) |
| Cherry-pick screening (Pass 2) | Pass | Tests A, B and C on all 162 revealed seeds find no sign of seed pre-selection; Test C pooled z −0.554 (Step 20) |
| Bet-size invariance | Pass | Same slots and table at $0.01 and $10: 200 / 200 Phase C bets (Step 9) |
| Payouts | Pass | All 8,100 payouts exact against the paid table, scaling_edge[0].multipliers (Steps 5, 7 and 8) |
| Stake tiers | Info | 0.1% at the base stake tier, rising to 2.0% at larger stakes in the config. Explained from the config, not certified (S4.7) |
| Zero Edge audit | Pass | Both effective_edge groups pay from the same table at the captured stakes (Step 10) |
Anti-circularityPass
RTP claim rulePass
Simulated RTP (Pass 1)Pass
Cherry-pick screening (Pass 2)Pass
Bet-size invariancePass
PayoutsPass
scaling_edge[0].multipliers (Steps 5, 7 and 8)Stake tiersInfo
Zero Edge auditPass
effective_edge groups pay from the same table at the captured stakes (Step 10)The 99.9% theoretical RTP is derived from first principles on all 27 configurations, an exact identity rather than a statistical estimate, and Duel’s published 99.9% holds on every setting under the RTP claim rule. 27M simulated rounds are consistent with it, and the cherry-pick tests find no sign of seed selection.
How It Works — RTP & Payout Logic10 sections
4.1Theoretical RTP from First Principles (Step 17)
The theoretical RTP is derived from first principles, using no operator-supplied probability or RTP figure. The slot probabilities come from the binomial distribution, computed by binomProb() in src/stats.ts, which never reads the config, and again by walking every path through each board and counting where it lands. The only casino input is the multiplier table, and it is the table Duel pays. The derivation:
| Component | Formula | Source |
|---|---|---|
| Slot probability | P(slot = k) = C(rows, k) × 0.5^rows | Binomial distribution and path enumeration, not from the casino |
| Multiplier | scaling_edge[rows][risk][0].multipliers[k] | Casino-supplied: the table Duel pays (Step 8) |
| RTP computation | Σ P(k) × multiplier(k) for k = 0 … rows | Independent probability × paid multiplier |
| Result | = 0.999 on all 27 configurations | An exact identity, not a statistical estimate |
| Rows | Risk | P(slot 0) | Multiplier (slot 0) | Σ P×M | RTP |
|---|---|---|---|---|---|
| 8 | low | 0.00391 | 5.65180109× | 0.99900 | 99.9% |
| 8 | high | 0.00391 | 29.24517348× | 0.99900 | 99.9% |
| 16 | low | 0.00002 | 16.14566360× | 0.99900 | 99.9% |
| 16 | high | 0.00002 | 1009.33110594× | 0.99900 | 99.9% |
Anti-Circularity Verification:
for (const { rows, risk } of cfg.allConfigs()) { const configProbs = cfg.probabilities(rows, risk); const slotCount = rows + 1; for (let k = 0; k < slotCount; k++) { const independent = binomProb(rows, k); const fromConfig = configProbs[k]; if (fromConfig !== independent) { failures.push( `${rows}r/${risk} slot ${k}: config=${fromConfig} independent=${independent} diff=${Math.abs(fromConfig - independent).toExponential(4)}` ); } totalChecked++; }} const rtpFailures: string[] = [];for (const { rows, risk } of cfg.allConfigs()) { let independentRTP = 0; for (let k = 0; k <= rows; k++) { independentRTP += binomProb(rows, k) * cfg.scalingEdgeMultiplier(rows, risk, k); } const configRTP = cfg.theoreticalRTP(rows, risk); if (Math.abs(independentRTP - configRTP) > 1e-15) { rtpFailures.push( `${rows}r/${risk}: configRTP=${configRTP} independentRTP=${independentRTP}` ); }}Counting every path:
function enumerateBoard(rows: number): number[] { const counts = new Array<number>(rows + 1).fill(0); const total = 1 << rows; for (let path = 0; path < total; path++) { let slot = 0; for (let cursor = 0; cursor < rows; cursor++) slot += (path >> cursor) & 1; counts[slot]++; } return counts;}Why this proof is non-circular: P(slot) comes from the binomial distribution B(rows, 0.5), a property of fair coin flips, not from casino data. The multiplier table is the only casino-sourced input. Independent probabilities × the paid multipliers give 0.999 on every configuration, so the theoretical RTP is proven, not estimated. It holds for this exact, pinned table.
4.2RTP Claim Rule (Step 19)
Framework 1.1 adds the RTP claim rule (RTP-CLAIM 1.2.0): the RTP figure a casino publishes is held against the true RTP of every setting it covers. The rule looks for the claim in six places: the game page, fairness page, help page, bet panel, rules and game settings. Duel’s figure for Plinko is in its game settings: house_edge "0.001" on scaling-edge bracket 0 of the plinko config it serves, a flat claim of 99.9%.
The rule is scored on Step 19 with a ±0.1 percentage-point band. A setting more than 0.1 pp below the claim, on the house side, is a miss, and a miss makes the verdict RTP FIGURE OVERSTATED (exit 5). A miss alone never makes the verdict NOT PROVABLY FAIR, because the draws themselves would still pass.
| Property | Value |
|---|---|
| Claim | Flat 99.9% (house edge 0.1%) |
| Where published | Game settings: house_edge "0.001" on scaling-edge bracket 0 of Duel’s plinko config |
| Scored on | Step 19 |
| Band | ±0.10 pp |
| Settings | 27: rows 8–16 × low, medium, high, at the base stake tier |
| True RTP | Minimum and maximum both 99.900000% (an exact rational per setting) |
| Outside the band | 0 on the house side · 0 on the player side |
| Result | Pass · minimal fix: none |
| Setting | True RTP | Gap to claim | Result |
|---|---|---|---|
| 8 rows · low | 99.900000% | 0.000000 pp | Pass |
| 8 rows · medium | 99.900000% | 0.000000 pp | Pass |
| 8 rows · high | 99.900000% | 0.000000 pp | Pass |
| 9 rows · low | 99.900000% | 0.000000 pp | Pass |
| 9 rows · medium | 99.900000% | 0.000000 pp | Pass |
| 9 rows · high | 99.900000% | 0.000000 pp | Pass |
| 10 rows · low | 99.900000% | 0.000000 pp | Pass |
| 10 rows · medium | 99.900000% | 0.000000 pp | Pass |
| 10 rows · high | 99.900000% | 0.000000 pp | Pass |
| 11 rows · low | 99.900000% | 0.000000 pp | Pass |
| 11 rows · medium | 99.900000% | 0.000000 pp | Pass |
| 11 rows · high | 99.900000% | 0.000000 pp | Pass |
| 12 rows · low | 99.900000% | 0.000000 pp | Pass |
| 12 rows · medium | 99.900000% | 0.000000 pp | Pass |
| 12 rows · high | 99.900000% | 0.000000 pp | Pass |
| 13 rows · low | 99.900000% | 0.000000 pp | Pass |
| 13 rows · medium | 99.900000% | 0.000000 pp | Pass |
| 13 rows · high | 99.900000% | 0.000000 pp | Pass |
| 14 rows · low | 99.900000% | 0.000000 pp | Pass |
| 14 rows · medium | 99.900000% | 0.000000 pp | Pass |
| 14 rows · high | 99.900000% | 0.000000 pp | Pass |
| 15 rows · low | 99.900000% | 0.000000 pp | Pass |
| 15 rows · medium | 99.900000% | 0.000000 pp | Pass |
| 15 rows · high | 99.900000% | 0.000000 pp | Pass |
| 16 rows · low | 99.900000% | 0.000000 pp | Pass |
| 16 rows · medium | 99.900000% | 0.000000 pp | Pass |
| 16 rows · high | 99.900000% | 0.000000 pp | Pass |
export function computeRtpClaim(): RtpClaimResult { const cfg = JSON.parse(fs.readFileSync(path.join(__dirname, '..', 'plinkoConfig.json'), 'utf-8')).data; const acc = new RtpClaimAccumulator(RTP_CLAIM); for (let rows = cfg.rows.min; rows <= cfg.rows.max; rows++) { for (const risk of ['low', 'medium', 'high']) { const b0 = cfg.scaling_edge[String(rows)][risk][0]; if (b0.house_edge !== '0.001') throw new Error(`bracket 0 of ${rows}/${risk} is not the 0.001 bracket`); const mults: string[] = b0.multipliers; if (mults.length !== rows + 1) throw new Error(`${rows}/${risk}: ${mults.length} multipliers for ${rows + 1} slots`); // Σ_k C(rows,k)·m_k / 2^rows, exact over the common denominator 10^8·2^rows. let num = 0n, den = 1n; mults.forEach((m, k) => { const r = parseRational(m); num = num * r.d + binom(rows, k) * r.n * den; den = den * r.d; }); acc.add(`rows=${rows} risk=${risk}`, num, den * (1n << BigInt(rows))); } } return acc.result();}outputs/rtp-claim-table.json equals the run and matches its pin.4.3Full RTP Table — All 27 Configurations
All 27 configurations have the same theoretical RTP of 99.900% at the base stake tier. The simulated RTP varies by configuration with sampling variance, most on high-risk boards, where edge multipliers up to 1009× dominate the per-bet variance.
| Config | Theoretical RTP | Simulated RTP | Deviation |
|---|---|---|---|
| 8r/low | 99.900% | 99.894% | −0.006% |
| 8r/medium | 99.900% | 99.677% | −0.223% |
| 8r/high | 99.900% | 99.997% | +0.097% |
| 9r/low | 99.900% | 99.900% | −0.000% |
| 9r/medium | 99.900% | 99.994% | +0.094% |
| 9r/high | 99.900% | 99.566% | −0.334% |
| 10r/low | 99.900% | 99.902% | +0.002% |
| 10r/medium | 99.900% | 99.815% | −0.085% |
| 10r/high | 99.900% | 99.460% | −0.440% |
| 11r/low | 99.900% | 99.876% | −0.024% |
| 11r/medium | 99.900% | 99.921% | +0.021% |
| 11r/high | 99.900% | 100.093% | +0.193% |
| 12r/low | 99.900% | 99.916% | +0.016% |
| 12r/medium | 99.900% | 99.895% | −0.005% |
| 12r/high | 99.900% | 99.852% | −0.048% |
| 13r/low | 99.900% | 99.912% | +0.012% |
| 13r/medium | 99.900% | 99.748% | −0.152% |
| 13r/high | 99.900% | 100.361% | +0.461% |
| 14r/low | 99.900% | 99.872% | −0.028% |
| 14r/medium | 99.900% | 99.945% | +0.045% |
| 14r/high | 99.900% | 99.908% | +0.008% |
| 15r/low | 99.900% | 99.917% | +0.017% |
| 15r/medium | 99.900% | 99.923% | +0.023% |
| 15r/high | 99.900% | 100.003% | +0.103% |
| 16r/low | 99.900% | 99.881% | −0.019% |
| 16r/medium | 99.900% | 99.786% | −0.114% |
| 16r/high | 99.900% | 100.736% | +0.836% |
4.4Simulation Pass 1 — Pinned Seeds (Step 19)
Section 4.1 derives the RTP. The simulation checks the implementation in practice: 27 million rounds played with the audit’s own RNG code, one seed pair per configuration, generated once and pinned in src/sim-seeds.ts. Every npm test replays all 27M rounds and requires every slot count, the simulated RTPs and the running-RTP points to come back exactly, and every other derived figure within the reproduction tolerance.
Chi-squared test: Compares observed slot frequencies with the binomial. 0 / 27 fail at uncorrected α = 0.01, and 0 / 27 at Bonferroni α/27 ≈ 0.00037.
Serial independence: Lag-1 autocorrelation and the runs test. 0 / 27 configurations fail either test.
RTP consistency: Mean simulated RTP 99.917% against 99.900% theoretical. Each configuration is held within 5 standard errors of its theoretical RTP; the largest gap is 1.79.
Replay: 27 / 27 configurations × 1,000,000 rounds regenerated on every run: census exact, 691 derived figures within tolerance.
export function playPass1Config( rows: number, multipliers: number[], server: string, client: string, rounds: number, samples: readonly number[],): Pass1Played { const key = Buffer.from(server, 'hex'); const slotCounts = new Array(rows + 1).fill(0); const hitSequence = new Array(rounds); let totalPayout = 0; const rtpSnapshots: Array<{ roundCount: number; rtp: number }> = []; let nextSampleIdx = 0; for (let nonce = 0; nonce < rounds; nonce++) { const slot = computeSlotFromBuffer(key, client, nonce, rows); slotCounts[slot]++; hitSequence[nonce] = slot; totalPayout += multipliers[slot]; if (nextSampleIdx < samples.length && (nonce + 1) === samples[nextSampleIdx]) { rtpSnapshots.push({ roundCount: nonce + 1, rtp: (totalPayout / (nonce + 1)) * 100 }); nextSampleIdx++; } }What is a Monte Carlo simulation? Instead of relying on algebra alone, we play millions of rounds. Each round computes a slot from scratch with the same HMAC-SHA256 pipeline as the live game, and the payouts are added up. An aggregate return consistent with 99.9% shows the implementation behaves as the math says.
4.5Cherry-Pick Detection — Pass 2 (Step 20)
A commitment makes seed substitution detectable, but it does not show that seeds were chosen without bias. An operator could pre-generate seeds and deploy only those whose early nonces favour the house. Pass 2 takes every server seed Duel actually used, replays it over 10,000 nonces on the boards of its own epoch, and looks for that signature. The replay is bound to the capture: all 8,100 captured bets, re-read at their own nonce, equal the served slot.
Test A — Full range: Does any seed’s slot distribution over all 10,000 nonces depart from the binomial? A cherry-picked seed would show a significant deviation.
Test B — Early vs late window: Does any seed deviate in nonces 0–49, the window this capture played under each seed, while the later nonces do not? With about 50 nonces it detects gross selection only.
Test C — Served payouts: For each epoch, the payout sum of the 50 settings Duel actually served at nonces 0–49, standardised by the exact per-board mean and variance and ranked against a null calibrated on 10,000 fresh seeds playing the same sequence. Computed in verify, not read from an artifact.
| Test | Result |
|---|---|
| Seeds tested | 162 revealed seeds × 10,000 nonces |
| Seed × row combinations | 242 |
| Test A fails (p < 0.01) | 1 / 242 (about 2.4 expected by chance) · binomial p = 0.912 |
| Test B early-window flags | 10 / 242, below the threshold of 13 · binomial p = 0.773 |
| Multi-window analysis | 8 isolated-early, 2 multi-window (8.1 and 1.9 expected by chance) |
| Test C flagged epochs (p ≤ 0.01) | 1 / 162; the rule fails at 8 (family survival 0.8037) |
| Test C broad flags | 0 |
| Test C pooled early-window z | −0.554 (fails below −3.090) |
| Early windows below / above expectation | 98 / 64 (the calibrated null expects 99.9 below) |
| Early-window shortfall | Power per epoch | Family, 10% picked | Family, 25% picked | Family, 50% picked |
|---|---|---|---|---|
| 5% | 3.9% | 0.1% | 0.7% | 4.6% |
| 10% | 12.7% | 2.1% | 30.7% | 87.6% |
| 20% | 31.5% | 31.3% | 98.6% | > 99.9% |
// statistic per revealed epoch: the payout sum S of the 50 configurations the casino actually// served at nonces 0–49 (the captured nonce range), standardised by the EXACT per-board// mean and variance (binomial slot law × the served bracket-0 multipliers);// null Monte-Carlo calibration on PASS2_NULL_SEEDS = 10,000 fresh seeds (src/pass2-replay.ts)// playing the same served sequence at nonces 0–49; p = (1 + #null ≤ z) / (R + 1);// flag one-sided, lower tail (a window that pays the player LESS): p ≤ TEST_C_ALPHA;// family flags aggregated by Poisson-binomial survival over the per-epoch null flag// probability ⌊α(R+1)⌋/(R+1) — an upper bound on the true rate when the lattice ties;// survival < TEST_C_FAMILY_FAIL → FAIL, < TEST_C_FAMILY_FLAG → FLAG (marginal excess);// broad an epoch whose early window p ≤ TEST_C_BROAD_P AND whose reference window (nonces// 50–9,999, the same served sequence cycled) p ≤ TEST_C_BROAD_P → FAIL (a seed bad// everywhere, not a picked opening); the reference null is a bootstrap of 199 calibrated// windows per sample, 10,000 samples, from a PRNG seeded by a fixed label;// pooled z over all epochs' early windows (Σ(S−μ)/√Σσ²) below TEST_C_POOLED_Z → FAIL.const TEST_C_ALPHA = 0.01;const TEST_C_FAMILY_FAIL = 0.001;const TEST_C_FAMILY_FLAG = 0.01;const TEST_C_BROAD_P = 0.001;const TEST_C_POOLED_Z = -3.090;Tests A and B:
for (const rows of rowList) { const slotCount = rows + 1; const fullCounts = new Array(slotCount).fill(0); const earlyCounts = new Array(slotCount).fill(0); const lateCounts = new Array(slotCount).fill(0); for (let nonce = 0; nonce < NONCES_PER_SEED; nonce++) { const slot = computeSlotFromBuffer(keyBuffer, info.clientSeed, nonce, rows); fullCounts[slot]++; if (nonce < EPOCH_LENGTH) { earlyCounts[slot]++; } else { lateCounts[slot]++; } } const fullExpected = Array.from({ length: slotCount }, (_, k) => binomProb(rows, k) * NONCES_PER_SEED); const earlyExpected = Array.from({ length: slotCount }, (_, k) => binomProb(rows, k) * EPOCH_LENGTH); const lateExpected = Array.from({ length: slotCount }, (_, k) => binomProb(rows, k) * (NONCES_PER_SEED - EPOCH_LENGTH)); const testA = chiSquaredTest([...fullCounts], fullExpected); const earlyTest = chiSquaredTest([...earlyCounts], earlyExpected); const lateTest = chiSquaredTest([...lateCounts], lateExpected); // Cherry-picking signature: early deviates from binomial, late does not const cherryPickFlag = earlyTest.pValue < 0.05 && lateTest.pValue >= 0.05; if (testA.pValue < 0.01) testAFails++; if (cherryPickFlag) cherryPickFlags++;4.6Bet-Size Invariance (Step 9)
Phase C placed 200 bets at $10 on 16r/high, the same configuration as Phase B’s $0.01 bets. All 200 slots were recomputed correctly from the revealed seeds using the same HMAC-SHA256 path, and all 200 multipliers matched the same scaling_edge[0].multipliers table. Bet amount is not an input to the RNG.
| Metric | Phase B ($0.01) | Phase C ($10) |
|---|---|---|
| Bets | 2,000 | 200 |
| Config | 16r/high | 16r/high |
| Slots recomputed | 2,000/2,000 | 200/200 |
| Multiplier table | scaling_edge[0] | scaling_edge[0] |
| RNG path | HMAC-SHA256 | HMAC-SHA256 |
4.7Progressive House Edge — Stake Tiers (Step 16)
plinkoConfig.json defines a scaling_edge ladder of 191 bet-size brackets per configuration, 5,157 in all. Each bracket carries a minimum and maximum bet, a house_edge and a complete multiplier table, and the config assigns a bracket by stake. Bracket 0, the base stake tier, has an edge of 0.1%; each tier above adds 0.01%, up to 2.0%, so the table’s RTP falls from 99.9% to 98.0%. On 16r/high the edge-slot multiplier goes from 1009.33× at bracket 0 to 990.13× at the top bracket. Step 16 checks the whole ladder in the config: each declared edge above bracket 0 equals 1 − its derived RTP, multipliers are symmetric, the ladder tiles the stake axis with an edge that never decreases, and every configuration spans 0.1% to 2.0%.
This is explained from the config, not certified. Every captured bet ($0.01 and $10) was in bracket 0, so which bracket Duel’s server applies above it was not tested live, and the RTP figures in this report apply to the base stake tier only.
How it works: The config selects the bracket by amount_currency. Each bracket has its own complete multiplier table, priced at its own edge.
Where the edge rises: On 25 of the 27 configurations the top tier caps the maximum profit, stake × (top multiplier − 1), at $1.5m to the cent; on 9r/high and 8r/high the ladder ends below it. Past the stake where the maximum profit reaches $1.5m, each further 0.01% of edge adds between $0.15 (16r/high) and about $41 (8r/low) of stake, and the maximum profit stays at $1.5m. On 16r/low the config sets the edge at 0.1% at $99,000, 1.01% at $100,000 and 1.93% at $101,000, for a maximum profit of about $1.5m in each case.
Example: A $500 bet on 16r/high falls in a bracket priced at 0.15% by the config.
Audit scope: All test bets ($0.01 and $10) fall within bracket 0. Rakeback and Zero Edge sit outside the game engine and are covered in 4.8.
| Config | 0.1% up to | Max profit reaches $1.5m at | 2% tier |
|---|---|---|---|
| 16r/low | $99,038 | $99,038 (0.10%) | $101,077 – $101,088 |
| 16r/medium | $6,731 | $13,650 (0.21%) | $13,900 – $13,902 |
| 16r/high | $336 | $1,493 (0.47%) | $1,516 – $1,516 |
| 15r/low | $85,861 | $106,144 (0.13%) | $108,304 – $108,316 |
| 15r/medium | $6,006 | $17,117 (0.29%) | $17,417 – $17,419 |
| 15r/high | $404 | $2,415 (0.63%) | $2,448 – $2,449 |
| 14r/low | $143,856 | $243,526 (0.17%) | $248,798 – $248,828 |
| 14r/medium | $7,865 | $26,137 (0.34%) | $26,585 – $26,587 |
| 14r/high | $469 | $3,572 (0.81%) | $3,615 – $3,616 |
| 13r/low | $66,054 | $209,647 (0.33%) | $213,703 – $213,728 |
| 13r/medium | $7,952 | $35,514 (0.46%) | $36,082 – $36,085 |
| 13r/high | $623 | $5,795 (0.98%) | $5,855 – $5,856 |
| 12r/low | $96,130 | $165,109 (0.18%) | $168,500 – $168,520 |
| 12r/medium | $8,809 | $46,651 (0.55%) | $47,358 – $47,363 |
| 12r/high | $764 | $8,907 (1.23%) | $8,977 – $8,977 |
| 11r/low | $74,540 | $201,052 (0.28%) | $205,039 – $205,063 |
| 11r/medium | $11,736 | $64,946 (0.58%) | $65,921 – $65,928 |
| 11r/high | $863 | $12,698 (1.56%) | $12,754 – $12,756 |
| 10r/low | $52,274 | $188,552 (0.38%) | $192,045 – $192,068 |
| 10r/medium | $10,025 | $71,169 (0.75%) | $72,113 – $72,121 |
| 10r/high | $1,105 | $20,203 (1.92%) | $20,218 – $20,220 |
| 9r/low | $68,592 | $323,992 (0.49%) | $330,042 – $330,083 |
| 9r/medium | $8,939 | $88,415 (1.05%) | $89,314 – $89,323 |
| 9r/high | $1,696 | not reached | $32,567 – $32,725 |
| 8r/low | $46,899 | $324,945 (0.73%) | $330,042 – $330,083 |
| 8r/medium | $9,539 | $125,407 (1.39%) | $126,239 – $126,253 |
| 8r/high | $2,061 | not reached | $40,000 – $40,196 |
plinkoConfig.json, and the RNG is not affected. Above the stake where the maximum profit reaches $1.5m, the edge keeps rising while the maximum profit does not. The table is generated from the pinned config by node scripts/scaling-edge-table.mjs.4.8Zero Edge and effective_edge (Step 10)
The API returns effective_edge on each bet as 0.1 or 0. Both groups recompute against the same committed table: 7,563 bets carry 0.1 and 537 carry 0, with 0 multiplier mismatches in either, and both groups’ tables derive to the same 99.9% RTP.
Per Duel.com engineering, the field is the post-rakeback edge marker: every bet settles with 0.1, then an operator-side rewards queue flips it to 0 once the rakeback rebate is credited. A 20-bet re-fetch sample (5 per phase, all originally 0.1) returned 0 for 20 / 20. On the captured stakes ($0.01 and $10, bracket 0) the field has no effect on the RNG, the slot or the bet-level payout, and Zero Edge is not a separate payout table.
const edgeGroups = new Map<number, typeof bets>();for (const bet of bets) { const e = bet.response.effective_edge; if (!edgeGroups.has(e)) edgeGroups.set(e, []); edgeGroups.get(e)!.push(bet);} const failures: string[] = [];const details: Record<string, unknown> = { edgeGroups: {} };const TOLERANCE = 1e-5; for (const [edge, groupBets] of edgeGroups) { let mismatches = 0; const configSet = new Set<string>(); for (const bet of groupBets) { const { rows, risk } = bet.request; const { final_slot, payout_multiplier } = bet.response; const se = cfg.scalingEdgeMultiplier(rows, risk as RiskLevel, final_slot); if (Math.abs(parseFloat(payout_multiplier) - se) > TOLERANCE) mismatches++; configSet.add(`${rows}|${risk}`); }effective_edge groups pay from the same bracket-0 multipliers, 0 mismatches. The game-engine 0.1% house edge is set by the multiplier table itself (Step 17).4.9Informational Items (Not Scored)
These items are reported for transparency. Live bets are the evidence for determinism, parity and payout correctness; at these sample sizes they are not RTP evidence.
| Item | Value | Context |
|---|---|---|
| Phase A observed RTP | 99.303% | 5,400 bets at $0.01, within expected variance |
| Phase B observed RTP | 92.313% | 2,000 bets at $0.01 on 16r/high, high edge-slot variance |
| Phase C observed RTP | 74.993% | 200 bets at $10 on 16r/high; the 95% interval is about ±92% at n = 200 |
| Phase D observed RTP | 104.636% | 500 bets at $0.01, within expected variance |
| Live chi-squared | 26 / 27 pass at α = 0.01 | 9r/low p = 0.0013, above the Bonferroni threshold of 0.00037 |
| Live slot fit (Step 23) | Fisher p = 0.7475 | 9 board sizes; nominal p-values, scored as an informational pass |
4.10Worked Example — Payout Verification
Real bet from Phase A — Bet ID 71602647, 12 rows, medium risk, nonce 3. Verified from plinko-master-8100bets.json:
serverSeed  = a7775148ccf4ba93bbaba4605c9b055bf6d0971ca1328777d69407fa52584ff6
clientSeed  = OFsDIaHWohCPjh0t
nonce       = 3
rows        = 12
risk        = medium
Step 1 — Slot computation: computeSlot(serverSeed, clientSeed, 3, 12) → 12 HMAC calls → final_slot = 8
Step 2 — Multiplier lookup: scaling_edge["12"]["medium"][0].multipliers[8] = 1.11012046
Step 3 — Payout: 0.01 × 1.11012046 = 0.0111012046
| Step | Process | Output |
|---|---|---|
| 1 | HMAC-SHA256 × 12 rows | slot = 8 ✅ |
| 2 | Multiplier: 12r/medium slot 8 | 1.11012046× |
| 3 | RTP check: P(slot=8) × 1.11012046 | Contributes to 99.9% |
| 4 | Payout: 0.01 × 1.11012046 | 0.0111012046 ✅ |
// 12 rows, medium risk: theoretical RTP from first principles// P(slot=k) = C(12,k) × 0.5^12 for k = 0..12//// Σ binomProb(12, k) × scalingEdgeMultiplier(12, "medium", k)// = 0.999000 (99.9%)//// This is a mathematical identity, not a measurement.// Casino supplies multipliers; probabilities are independently computed.Technical Evidence & Verification5 evidence groups
4.11Evidence Coverage Summary7 checks
| Verification Area | Coverage | Result |
|---|---|---|
| Anti-circularity (Step 17) | 351 probabilities, 27 / 27 RTP cross-checks, 130,816 paths | Pass |
| RTP claim rule (Step 19) | 27 settings, 0 outside ±0.1 pp | Pass |
| Zero Edge audit (Step 10) | Both edge groups, 0 mismatches | Pass |
| Scaling edge (Step 16) | All 5,157 brackets checked in the config | Pass |
| Simulation Pass 1 (Step 19) | 27M rounds replayed; 0 / 27 chi-squared, 0 / 27 serial | Pass |
| Simulation Pass 2 (Step 20) | 162 seeds × 10,000 nonces; Tests A, B and C | Pass |
| Bet-size invariance (Step 9) | 200 / 200 Phase C at $10 | Pass |
4.12Code References9 source files
| File | Purpose |
|---|---|
| tests/steps/anti-circularity.ts | Step 17: probability independence, RTP cross-check, path enumeration |
| src/rtp-claim.ts | The framework’s RTP claim rule 1.2.0, byte-identical copy |
| src/rtp-settings.ts | The exact per-setting RTP table and the claim it is held to |
| tests/steps/dataset.ts | Steps 10 and 16: Zero Edge audit, scaling edge analysis |
| tests/steps/simulation.ts | Steps 19–20: simulation replay, cherry-pick Tests A, B and C |
| src/simulate.ts | The two-pass simulation (27M rounds; 162 seeds × 10,000 nonces) |
| src/pass2-replay.ts | Pass 2 replay and the Test C null calibration |
| src/config.ts | theoreticalRTP, scalingEdgeMultiplier, payoutTableMultiplier |
| scripts/scaling-edge-table.mjs | Generates the stake-tier table in 4.7 from the pinned config |
4.13Datasets UsedSource artifacts
4.14Verified Invariants10 invariants
| Invariant | Result |
|---|---|
| P(slot) × multiplier = 0.999 for all 27 configurations (non-circular) | Pass |
| Binomial probabilities equal plinkoConfig.json for all 351 config × slot pairs | Pass |
| house_edge "0.001" on bracket 0, and the published 99.9% holds within ±0.1 pp on all 27 settings | Pass |
| Mean simulated RTP 99.917% across 27M rounds, each configuration within 5 standard errors | Pass |
| 0 / 27 configurations reject at Bonferroni α/27 | Pass |
| 0 serial independence failures | Pass |
| No sign of seed pre-selection across 162 revealed seeds (Tests A, B and C) | Pass |
| Phase C ($10) slots follow the same algorithm and table as Phase B ($0.01) | Pass |
| Every scaling-edge bracket above bracket 0 declares an edge equal to 1 − its derived RTP | Pass |
| Both effective_edge groups use the same multiplier table | Pass |
4.15Reproduction InstructionsRun locally
git clone https://github.com/ProvablyFair-org/duel-plinko.gitcd duel-plinkogit checkout v1.4.2npm cinpm test # Steps 9, 10, 16, 17, 19 and 20 cover S4cat outputs/rtp-claim-table.jsonS4-related steps:
[PASS] Step 9 — Phase C Code-Path Equivalence
[PASS] Step 10 — Zero Edge Audit
[PASS] Step 16 — Scaling Edge Analysis
[PASS] Step 17 — Probability Independence (Anti-Circularity)
[PASS] Step 19 — Simulation Results — Pass 1 Integrity (re-derived & replayed)
[PASS] Step 20 — Simulation Results — Pass 2 Cherry-Pick Test
RTP claim rule:
rtp-claim: ENFORCED — PASS
rtp-claim: claim flat 99.900000% — source: game settings: house_edge "0.001" on scaling_edge bracket 0 of Duel's plinko config (plinkoConfig.json; E11 as fetched 2026-10-05; declaration paytable.claimedHouseEdge 0.001)
rtp-claim: band ±0.10 pp · 27 settings · true min 99.900000% (rows=10 risk=low) · true max 99.900000% (rows=9 risk=medium)
rtp-claim: house side beyond band: 0 · player-favourable beyond band: 0 · worst rows=10 risk=low at 0.000000 pp
rtp-claim: outcome PASS · minimal fix: none — the claim holds for every setting it states a figure for
rtp-claim: committed table outputs/rtp-claim-table.json: equals this run; sha256 eca16ed27d4cb5bf… matches the pinFairness Integrity Testing
Does the implementation maintain fairness under non-standard conditions?
Sections 1–4 prove the game is mathematically fair. Section 5 proves the implementation maintains integrity under non-standard conditions. We applied 15 standard fairness integrity tests covering nonce integrity, seed commitment, outcome determinism, cross-player isolation, and payout integrity. 14 tests passed and 1 is not applicable to this game type.
Adversarial tests check whether inputs, sequences or payouts can be manipulated.

Fairness Integrity Testing
What we verified
- Nonce tampering — can the sequence be forced, replayed, or skipped?
- Seed injection — can server or client seed fields be overridden via API?
- Outcome replay — can a completed bet be replayed for duplicate payouts?
- Cross-player isolation — can one player's seeds or outcomes affect another's?
- Payout tampering — can multiplier or payout values be injected client-side?
- Parameter limits — can invalid row counts or risk levels be submitted?
What this means for you
- Across the 15 tests we ran, no API path allowed outcomes to be altered, replayed, or injected — by player or casino
- Once a bet is placed, the result cannot be changed or replayed
- Each bet is cryptographically unique and isolated
- Your results are independent of every other player
- The server rejects malformed, out-of-range, and duplicate requests
- Nonce tampering — can the sequence be forced, replayed, or skipped?
- Seed injection — can server or client seed fields be overridden via API?
- Outcome replay — can a completed bet be replayed for duplicate payouts?
- Cross-player isolation — can one player's seeds or outcomes affect another's?
- Payout tampering — can multiplier or payout values be injected client-side?
- Parameter limits — can invalid row counts or risk levels be submitted?
- Across the 15 tests we ran, no API path allowed outcomes to be altered, replayed, or injected — by player or casino
- Once a bet is placed, the result cannot be changed or replayed
- Each bet is cryptographically unique and isolated
- Your results are independent of every other player
- The server rejects malformed, out-of-range, and duplicate requests
Nonce integrityPass
Seed commitment integrityPass
Outcome determinismPass
Round & player isolationPass
Payout integrityPass
15 standard fairness integrity tests: 14 pass, 1 N/A (single-step game). All API probe tests completed.
Category coverage


14 / 14 applicable tests passed · 1 test not applicable to this single-step game.

14 pass · 1 N/A · no fairness failures
| Check | Result | Evidence |
|---|---|---|
| Nonce integrity | Pass | Sequential, server-controlled, no duplicates across 162 seed pairs; two bets our capture missed were reconstructed from the revealed seeds (capture script, not Duel) |
| Seed commitment integrity | Pass | Locked at bet acceptance, unique per seed pair — 162/162 verified |
| Outcome determinism | Pass | Identical inputs produce identical outcomes — 8,100/8,100 confirmed |
| Round & player isolation | Pass | Per-user seeds, serial independence confirmed (0/27 fail in simulation) |
| Payout integrity | Pass | Parameter limits (rows 8–16, risk 1–3) enforced; client-injected payout fields ignored — server computes outcome from seeds only |
Nonce integrityPass
Seed commitment integrityPass
Outcome determinismPass
Round & player isolationPass
Payout integrityPass
15 standard fairness integrity tests: 14 pass, 1 N/A (single-step game). All API probe tests completed.
How It Works — Fairness Integrity Testing2 sections
5.1Framework Overview
Testing follows the ProvablyFair.org Fairness Integrity Framework — a structured methodology derived from real, historically observed failures in provably fair systems. Five categories target specific fairness properties. Scope boundary: S5 tests whether fairness guarantees hold under non-standard API interaction. Platform-level implementation testing falls outside standard certification.
| Category | Tests | What It Catches |
|---|---|---|
| Nonce Integrity | 4 | Sequence gaps, server-side nonce manipulation, session continuity |
| Seed Commitment | 5 | Mid-epoch seed changes, seed reuse, predictable seed generation |
| Outcome Determinism | 2 | Non-deterministic outputs, outcome replay |
| Player Isolation | 2 | Cross-round correlation, cross-user outcome dependence |
| Payout Integrity | 2 | Parameter enforcement, server-side computation verification |
5.2Severity Framework & Hard Fail Criteria
Findings are classified by severity. Hard fail criteria — any one triggers a NOT PROVABLY FAIR verdict.
| Severity | Meaning | Action |
|---|---|---|
| PASS | Test passed — no issue detected | None |
| N/A | Test not applicable to this game type | None |
| FLAG | Anomaly detected, documented for transparency | Disclosed |
| HARD FAIL | Fairness guarantee cannot be confirmed | Certification blocked until remediated |
| Condition | Consequence |
|---|---|
| Nonce gap or duplicate within epoch | Outcome sequence integrity broken |
| Server seed changed mid-epoch | Commit-reveal guarantee broken |
| Slot recomputation mismatch | Undisclosed inputs affecting outcomes |
| Client seed not used in HMAC | Player has no influence on outcomes |
15 tests · 14 pass · 1 N/A
Nonce Integrity4/4
FI-NONCE-001PassEach bet increments the nonce sequentially with no gaps, repeats, or resets — preventing the server from skipping unfavourable outcomes
FI-NONCE-002PassNonce progression is server-controlled — the client cannot inject, skip, or replay a nonce value via the API
S1, Step 4 — server controls nonce assignment. Client bet requests do not include a nonce field.
FI-NONCE-003PassSubmitting an invalid or out-of-sequence nonce does not produce a game outcome — the server rejects the request
API probe — 7 adversarial nonce values (−1, 0, 999999999, 'abc', INT32_MAX, INT32_MAX+1, 9e18) injected in request body. All 7 silently ignored; server assigned valid sequential nonces. Continuity preserved (baseline 18 → post-test 26); no stack traces leaked.
FI-NONCE-004PassNonce sequence continues correctly after disconnect/reconnect — no reset to zero mid-epoch
Seed Commitment5/5
FI-SEED-001PassEmpty, null, or invalid client seeds are handled deterministically — the server enforces input requirements
API probe — 6/7 adversarial seeds rejected with HTTP 422 (empty, null, special chars, emoji, CJK, whitespace-only). Oversized seed (>1000 chars) blocked at HTTP 400 by active-game guard before format check — correct safety behaviour. All Plinko bets after each rejection remained functional; no stack traces leaked.
FI-SEED-002PassOnce a bet is accepted, the seed pair is locked for the epoch — no mid-epoch mutation of server or client seed is possible
FI-SEED-003PassEach epoch uses a unique server seed — no seed is reused across epochs or sessions
S1, Step 1 — 162 distinct revealed server seeds, 0 reuse detected.
FI-SEED-004PassNo shared seed pool across users — each player's seeds are independently generated and isolated
API probe — 10 concurrent seed rotations on Account A and 10 on Account B. Zero hash collisions across 20 rotations; all hashes within each account distinct. Full account isolation confirmed.
FI-SEED-005PassServer seeds show no correlation with timestamps, sequential patterns, or other predictable inputs
API probe — 10 rotations spaced 5 seconds apart over ~52 seconds. All 10 server seed hashes distinct; no two shared 6+ leading hex characters. Time-correlated derivation ruled out.
Outcome Determinism2/2
FI-OUTCOME-001PassGiven identical inputs (serverSeed, clientSeed, nonce, rows), the game always produces the same slot — verified across all 8,100 live bets
S3, Step 5 — 8,100/8,100 bets independently recomputed from seeds, 0 mismatches.
FI-OUTCOME-002N/AA completed bet cannot be replayed via the API to generate a duplicate payout
Plinko auto-resolves — single-step game with no separate cashout action. Nonce increments server-side after each bet. No replay surface exists.
Player Isolation2/2
FI-ISO-001PassRNG state is fully independent across rounds — no carry-over from one bet to the next. Each nonce produces a fresh HMAC-SHA256 computation
FI-ISO-002PassOne player's seeds, nonces, and outcomes cannot be observed or influenced by another player — complete cross-user isolation
Follows from seed uniqueness (FI-SEED-003) — if each user has a unique server seed, outcomes are isolated by construction. Confirmed by FI-SEED-004 — zero hash collisions across 20 cross-account rotations.
Payout Integrity2/2
FI-PAYOUT-001PassGame parameters cannot exceed defined limits — only valid row counts (8–16) and risk levels (low, medium, high) are accepted
API probe — 6/6 invalid parameter combinations rejected with HTTP 422 (rows = −1, 0, 17, 99; risk_level = 'extreme' string, 4). All 3 control bets and recovery bet accepted. No out-of-range values silently coerced.
FI-PAYOUT-002PassMultiplier and payout fields in the API request are ignored — the server computes all values from its own formula, not from client-supplied values
API probe — 5 injected fields (payout_multiplier=1000, slot_result=0, final_slot=0, effective_edge=−99, win_amount='99999') all silently ignored. Server computed its own slot and multiplier on every bet from seeds + nonce only. noInjectionHonoured=true.
Technical Evidence & Verification4 evidence groups
5.3Coverage Summary15 checks
| Test ID | Category | Verification Source | Status |
|---|---|---|---|
| FI-NONCE-001 | Nonce | S1, Step 4 (data-driven) | Pass |
| FI-NONCE-002 | Nonce | S1, Step 4 (data-driven) | Pass |
| FI-NONCE-003 | Nonce | API probe | Pass |
| FI-NONCE-004 | Nonce | S1, Step 4 (data-driven) | Pass |
| FI-SEED-001 | Seed | API probe | Pass |
| FI-SEED-002 | Seed | S1, Steps 3 & 6 (data-driven) | Pass |
| FI-SEED-003 | Seed | S1, Step 1 (data-driven) | Pass |
| FI-SEED-004 | Seed | API probe | Pass |
| FI-SEED-005 | Seed | API probe | Pass |
| FI-OUTCOME-001 | Determinism | S3, Step 5 (data-driven) | Pass |
| FI-OUTCOME-002 | Determinism | Structural — single-step game | N/A |
| FI-ISO-001 | Isolation | S2, Step 19 (simulation) | Pass |
| FI-ISO-002 | Isolation | Structural — seed uniqueness | Pass |
| FI-PAYOUT-001 | Payout | API probe | Pass |
| FI-PAYOUT-002 | Payout | API probe | Pass |
5.4Additional Integrity Evidence (S1–S4)6 records
| Property | Source | Finding |
|---|---|---|
| 162/162 seed hashes verified | S1, Step 1 | Commit-reveal chain intact |
| 166/166 next-seed promotions | S1, Step 2 | Seed rotation chain intact |
| 8,100/8,100 exact parity | S3, Step 5 | No post-RNG conditional logic |
| Anti-circularity proven | S4, Step 17 | 0.1% house edge (bracket 0) via independent probabilities × published table |
| Tests A, B and C on 162 seeds (Test C pooled z −0.554) | S4, Step 20 | No seed pre-selection bias |
| 84.2% client seed influence | S1, Step 6 | Player entropy is genuine |
5.5Scope
This certification covers the 15 standard fairness integrity tests listed above — the minimum required to verify that the provably fair implementation holds up under non-standard conditions. This is not a penetration test. It focuses specifically on the provably fair implementation — not the operator's broader platform security.
Standard scope: The integrity matrix is largely consistent across every game we audit — the core nonce, seed, determinism, and isolation checks are identical. A small number of tests are tailored to each game (e.g. parameter ranges and payout fields specific to Plinko's rows and risk levels).
No infrastructure testing: Server security, network-level protections and operational controls fall under platform-level security, not game-level fairness, and sit outside this certification.
Point-in-time: Results apply to the game configuration and codebase at the time of audit. Post-audit changes require re-certification.
5.6Reproduction InstructionsRun locally
Data-driven tests (8 of 15): Fully reproducible from the open-source audit repo. These tests run against the captured dataset and produce deterministic results.
API probe tests (6 of 15): Live API probes against duel.com captured at audit time. Per-test evidence (requests, responses, server-assigned values, timing) is retained in our private adversarial-testing archive and summarised in the integrity test review document. The testing harness itself is kept private so it can't be reused against the game.
git clone https://github.com/ProvablyFair-org/duel-plinko.gitcd duel-plinkogit checkout v1.4.2npm cinpm testExpected output, as run at v1.4.2 (S5-related steps, mapping added):
[PASS] Step 1 — Seed Hash Integrity → FI-SEED-003
[PASS] Step 3 — Hash Consistency Within Epoch → FI-SEED-002
[FLAG:capture] Step 4 — Nonce Audit → FI-NONCE-001, 002, 004
[PASS] Step 5 — Slot Recomputation & Bit-Extraction Bound → FI-OUTCOME-001
[PASS] Step 6 — Client Seed Influence (exact null) → FI-SEED-002
[PASS] Step 19 — Simulation Results — Pass 1 Integrity (re-derived & replayed) → FI-ISO-001API Probe Tests (completed):
[PASS] FI-NONCE-003 — Invalid nonce handling → 7/7 invalid nonces ignored[PASS] FI-SEED-001 — Invalid client seed handling → 6/7 rejected (1 active-game blocked)[PASS] FI-SEED-004 — Cross-user seed pool check → 0/20 collisions across 2 accounts[PASS] FI-SEED-005 — Seed timing analysis → 10 distinct hashes, no time correlation[PASS] FI-PAYOUT-001 — Invalid parameter handling → 6/6 boundary violations rejected (HTTP 422)[PASS] FI-PAYOUT-002 — Multiplier field handling → 0 injections honouredPlayer Verification
Can a player verify their own bets without trusting anyone?
Every Plinko outcome can be reproduced from publicly disclosed inputs, with no hidden variables or private backend data. Save the commitment before you bet, rotate to reveal the seed, then check the commitment and recompute the slot. This section walks through the process and links two ProvablyFair.org verifiers, both pinned and run on all 8,100 captured bets.
Save the commitment before you bet. After rotating, check the hash and recompute the slot.
Independent Result Verification
Key principles
- Every Plinko outcome can be independently reproduced
- No hidden variables and no private backend data
- A revealed seed that matches your saved commitment shows the seed was fixed before your bet
- A matching slot shows the bet followed the published algorithm
- Duel’s Provably Fair modal and per-bet transaction view show everything you need
What you need
- Server Seed — revealed when you rotate the seed pair (casino entropy)
- Client Seed — your player-controlled seed
- Nonce — the bet’s position under the seed, counting up from 0
- Row Count — the configuration you played (8–16)
- Every Plinko outcome can be independently reproduced
- No hidden variables and no private backend data
- A revealed seed that matches your saved commitment shows the seed was fixed before your bet
- A matching slot shows the bet followed the published algorithm
- Duel’s Provably Fair modal and per-bet transaction view show everything you need
- Server Seed — revealed when you rotate the seed pair (casino entropy)
- Client Seed — your player-controlled seed
- Nonce — the bet’s position under the seed, counting up from 0
- Row Count — the configuration you played (8–16)
Player can access all required inputsPass
Commitment can be saved before bettingPass
Client seed origin transparentPass
Verification process documentedPass
Independent verifiers availablePass
Manual recomputation possiblePass
No hidden or proprietary stepsPass
Only disclosed inputs are used, and identical inputs always produce identical output. Save the commitment before you bet: your saved copy is what shows the seed was fixed before your bet.
- 1
Save the Commitment
Before your first bet under a seed, open Duel’s Provably Fair modal and copy the active server seed hash. Keep the copy. The modal also shows the next server seed’s hash: save it before you rotate and you hold your next commitment in advance.
- 2
Play, Then Rotate
Place your Plinko bets. When you rotate the seed pair, Duel retires the active server seed and reveals it, so every bet placed under it becomes checkable.
- 3
Find the Bet’s Inputs
Open Transactions and click a past Plinko round. The per-bet modal shows the revealed server seed with the bet ID, client seed and nonce.
- 4
Check and Recompute
Hash the revealed seed and compare it with the copy you saved, not with a hash read from the bet record afterwards. Then recompute the slot with a verifier below or the console checks in 6.8, and look up the payout in the base-tier table.
Verify a real bet, step by stepVerify a real bet · Swipe for all 4 steps →
Verify on provablyfair.org
The main-site verifier, pinned and run on all 8,100 captured bets: slot, path and commitment hash match on every one.
Open main-site verifier
Built-in verification
The operator’s own verification page. This tool is controlled by Duel.com.
Open Duel verifier
Visual Walkthroughstep-by-step

Open the Provably Fair modal on the game page. It shows the active client seed, the hashed server seed (the casino’s commitment) and your current nonce, plus the next pair’s commitment. Copy the hashed server seed before your first bet under it and keep it. You can also set the client seed that becomes active after rotation; “Rotate seed” retires the active pair, which reveals its server seed for your previous bets.
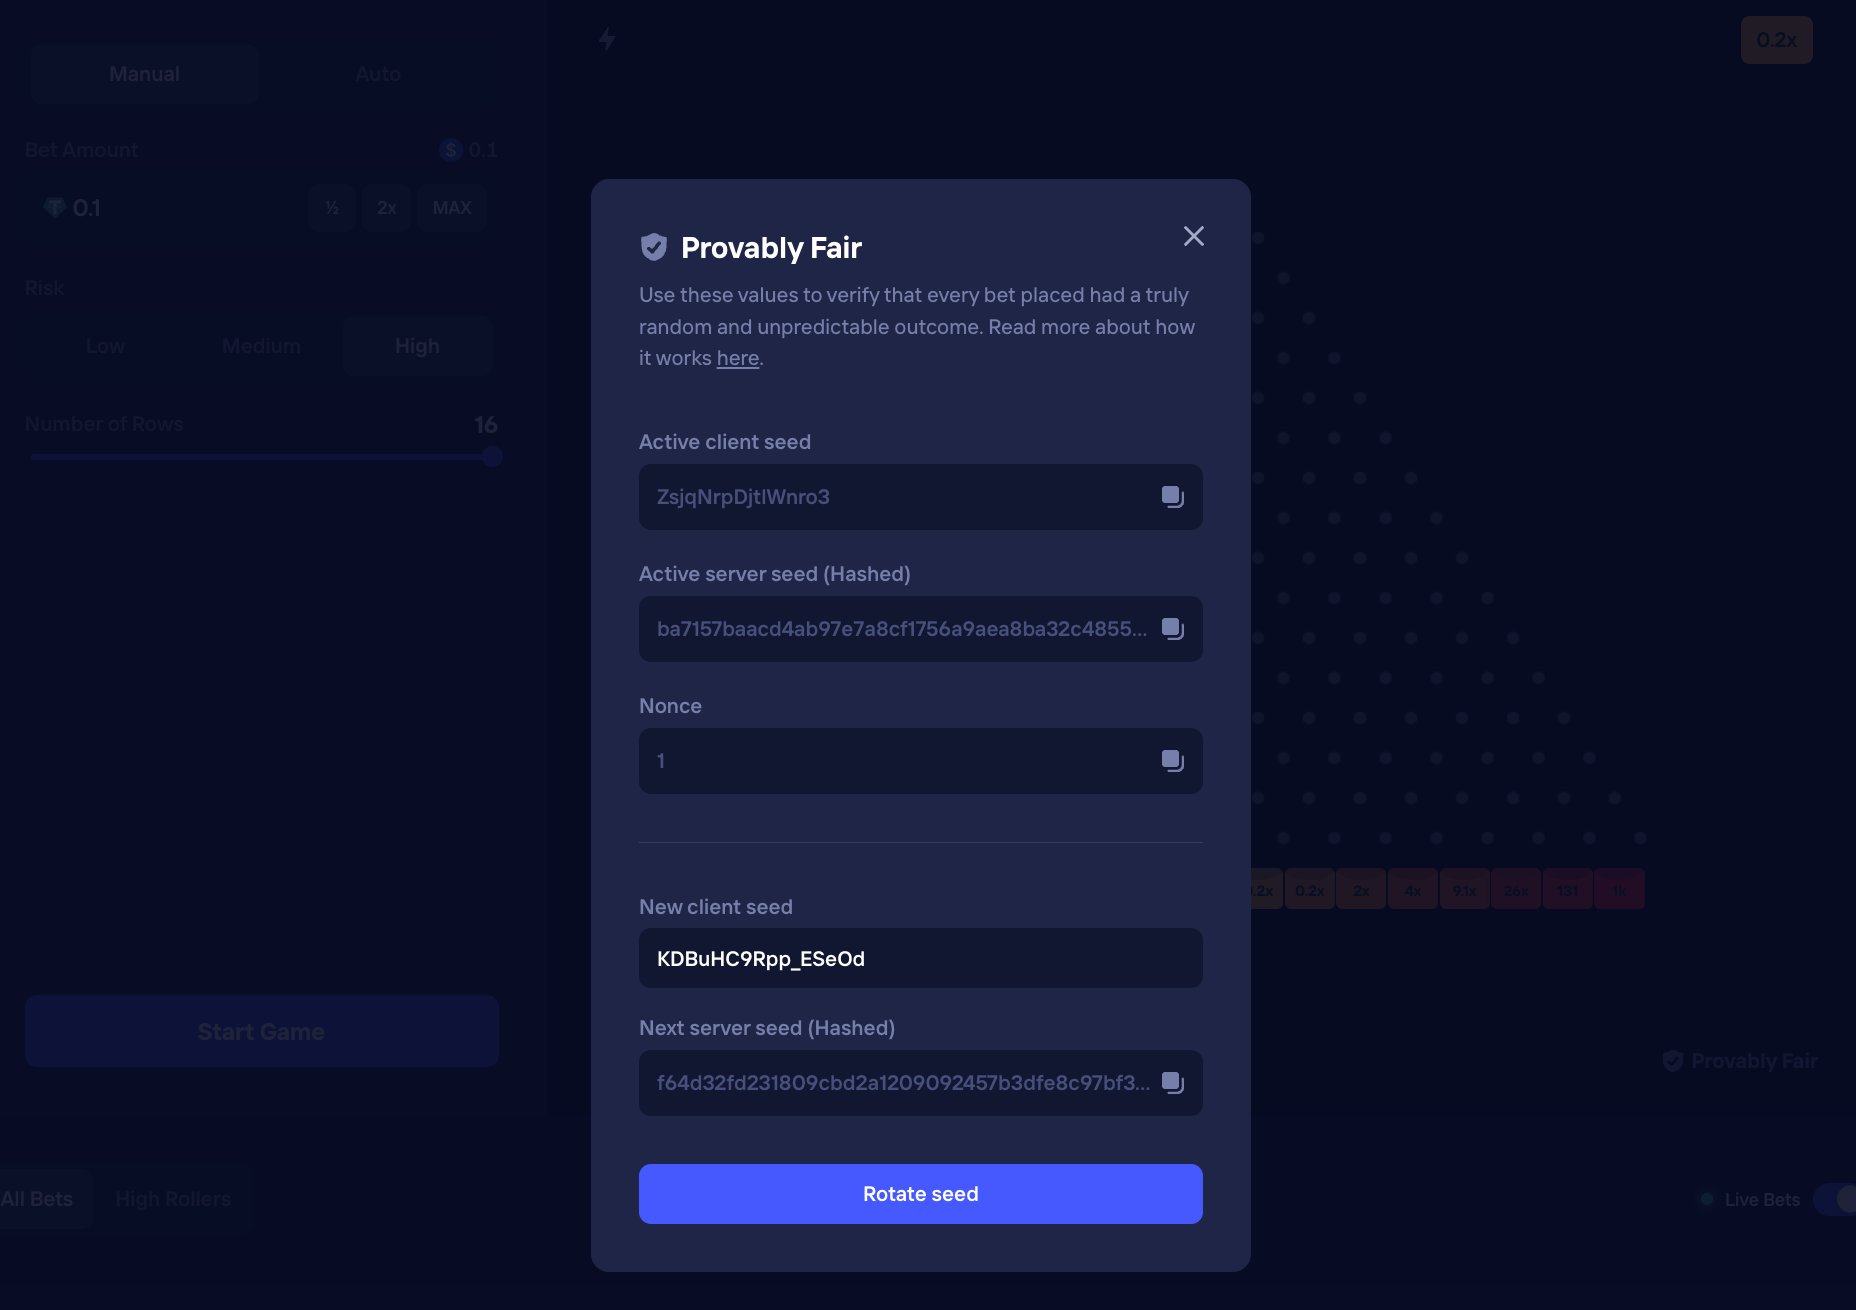
Provably Fair modal — active client seed, hashed server seed, nonce, customisable new client seed, next pair pre-commitment, and Rotate seed action.
Select your row count and risk level, then place a bet. The ball drops through the peg board and lands in the slot fixed by the committed server seed, your client seed and the nonce.
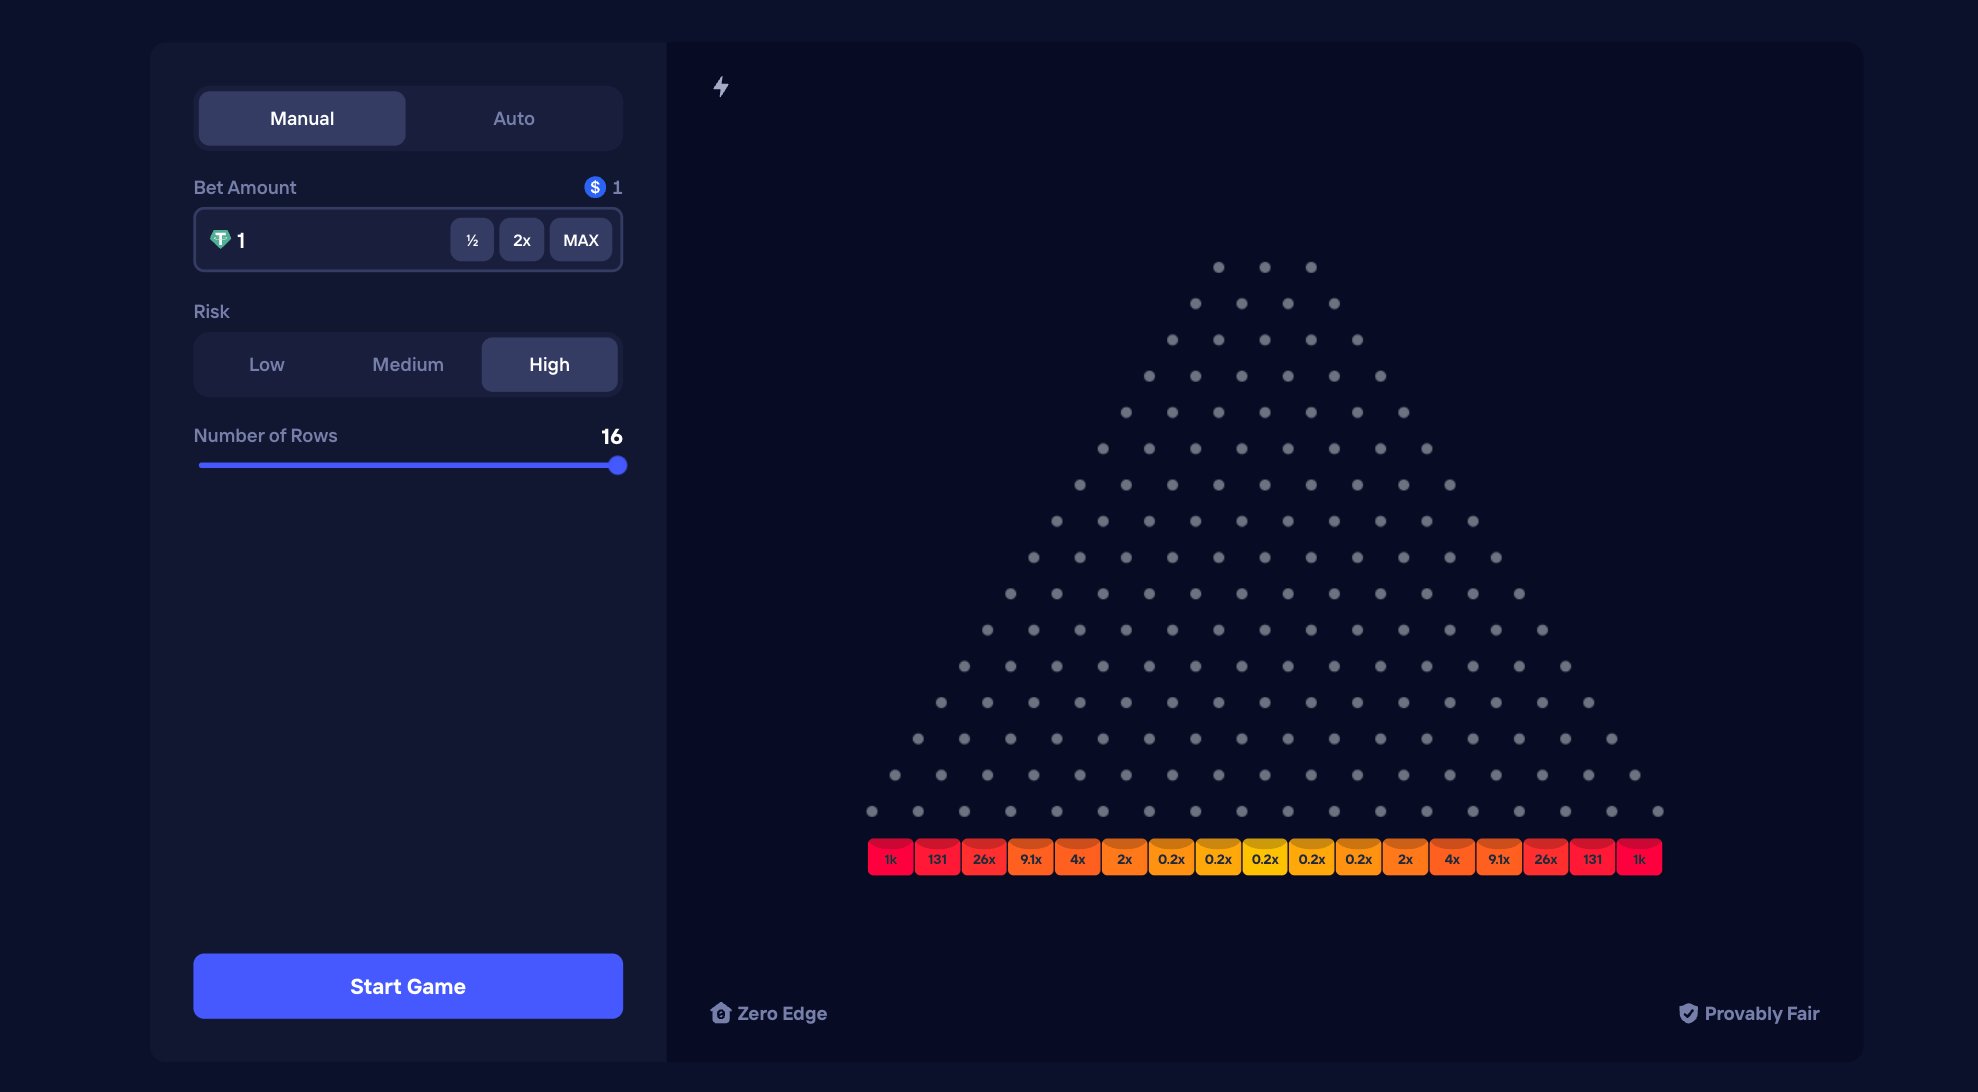
Duel.com Plinko — ball-drop game with row and risk selector.
After rotating, open Transactions and click a past Plinko round. The per-bet modal shows the revealed plaintext server seed alongside the bet ID, client seed and nonce. SHA-256 of the revealed seed must match the commitment you saved in Step 1:
Server Seed (revealed) — the plaintext value the casino committed to. Hash it and compare with your saved copy.
Client Seed — your player-controlled entropy input.
Nonce — the bet’s position under this seed pair.
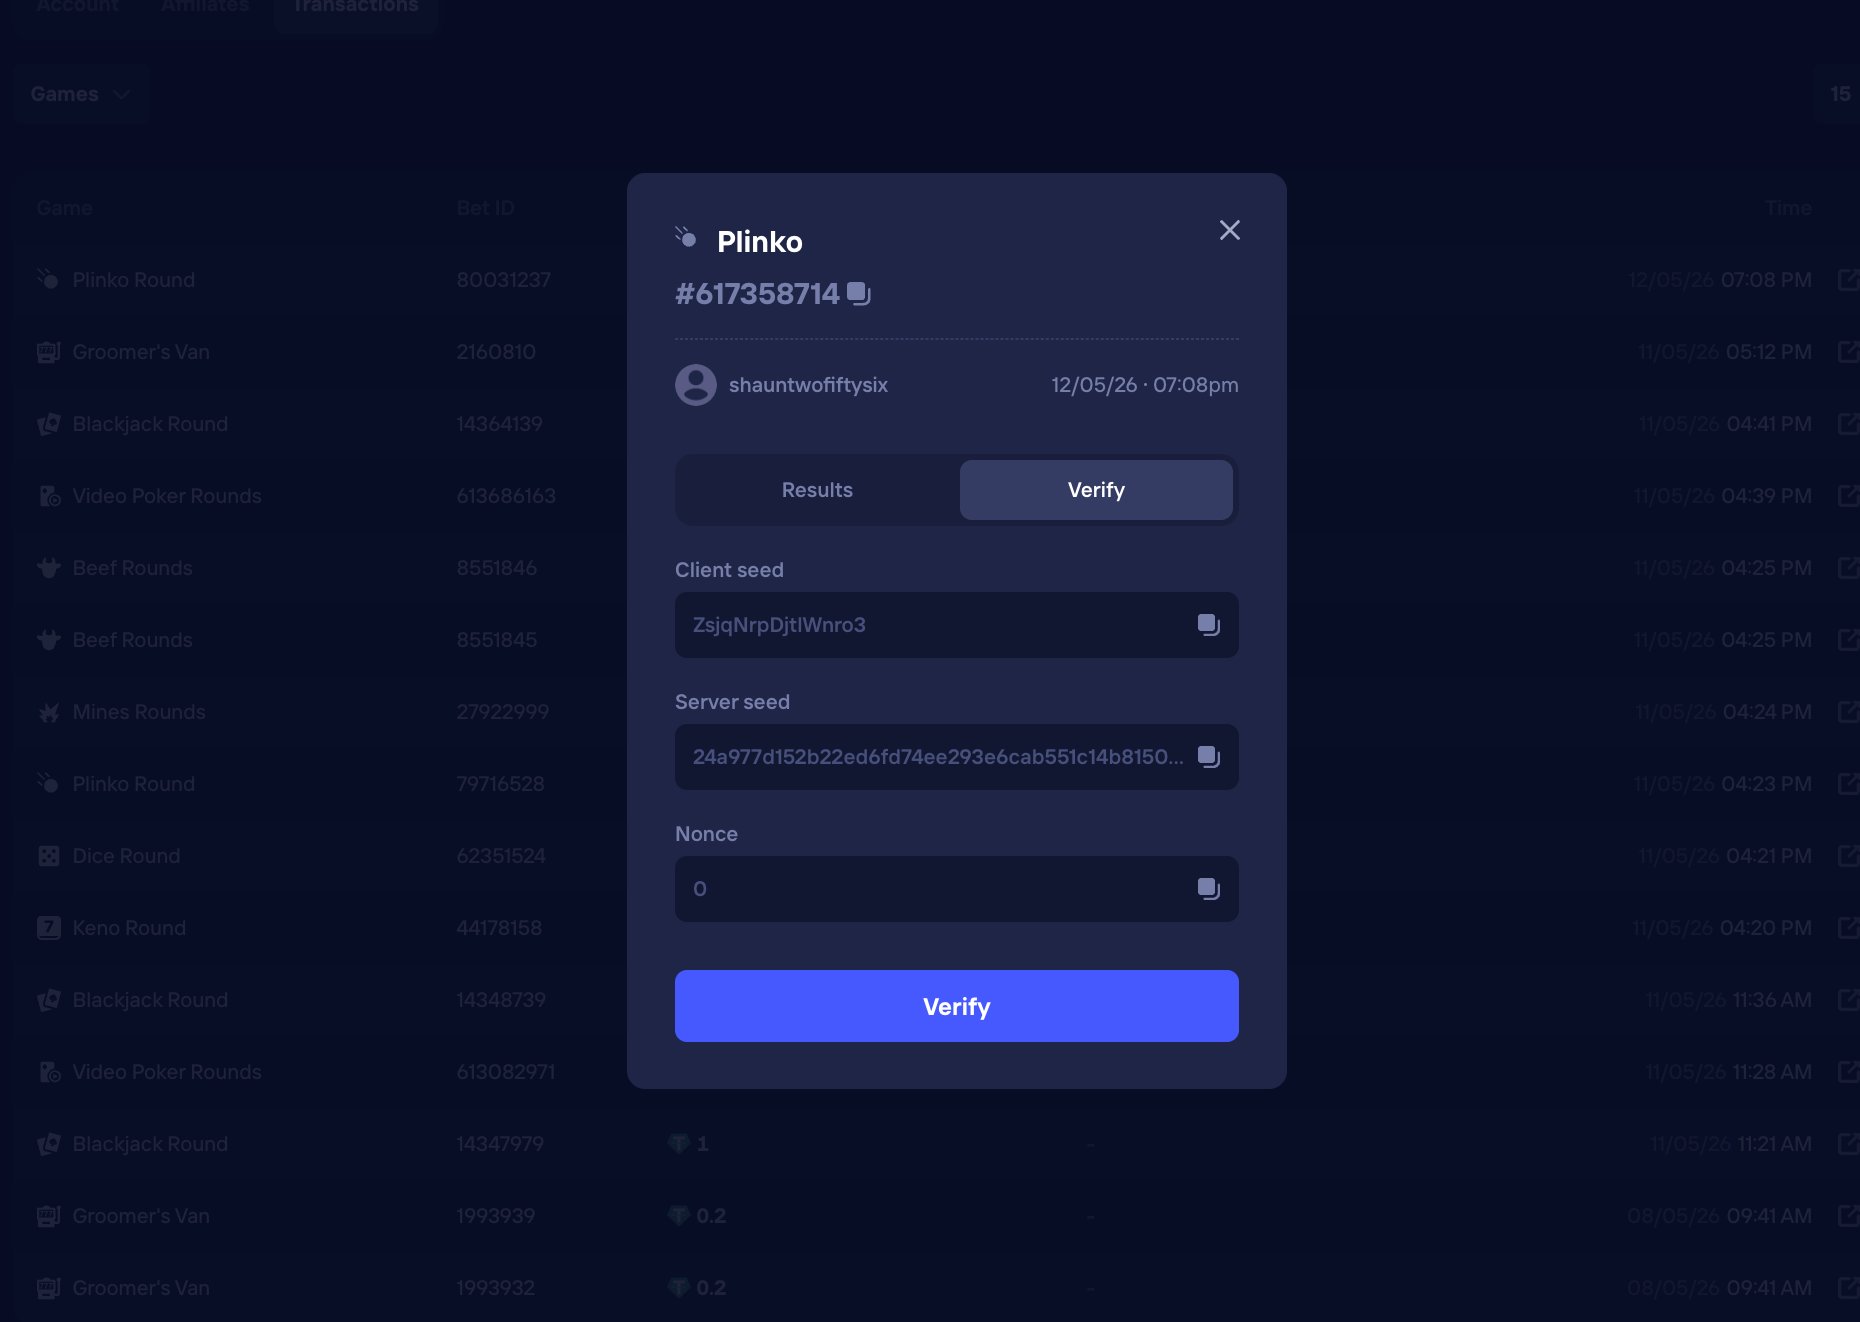
Per-bet transaction modal — revealed plaintext server seed, client seed, and nonce for the round.
Click Verify in the per-bet modal to open Duel’s Provably Fair page with the seeds filled in. The page recomputes the slot and shows the Game Result inline. If it matches your live result and the revealed seed matches the commitment you saved, the result is consistent with the published algorithm and a seed fixed before you bet. For a check that does not rely on Duel’s page, use a ProvablyFair.org verifier or the console checks in 6.8.
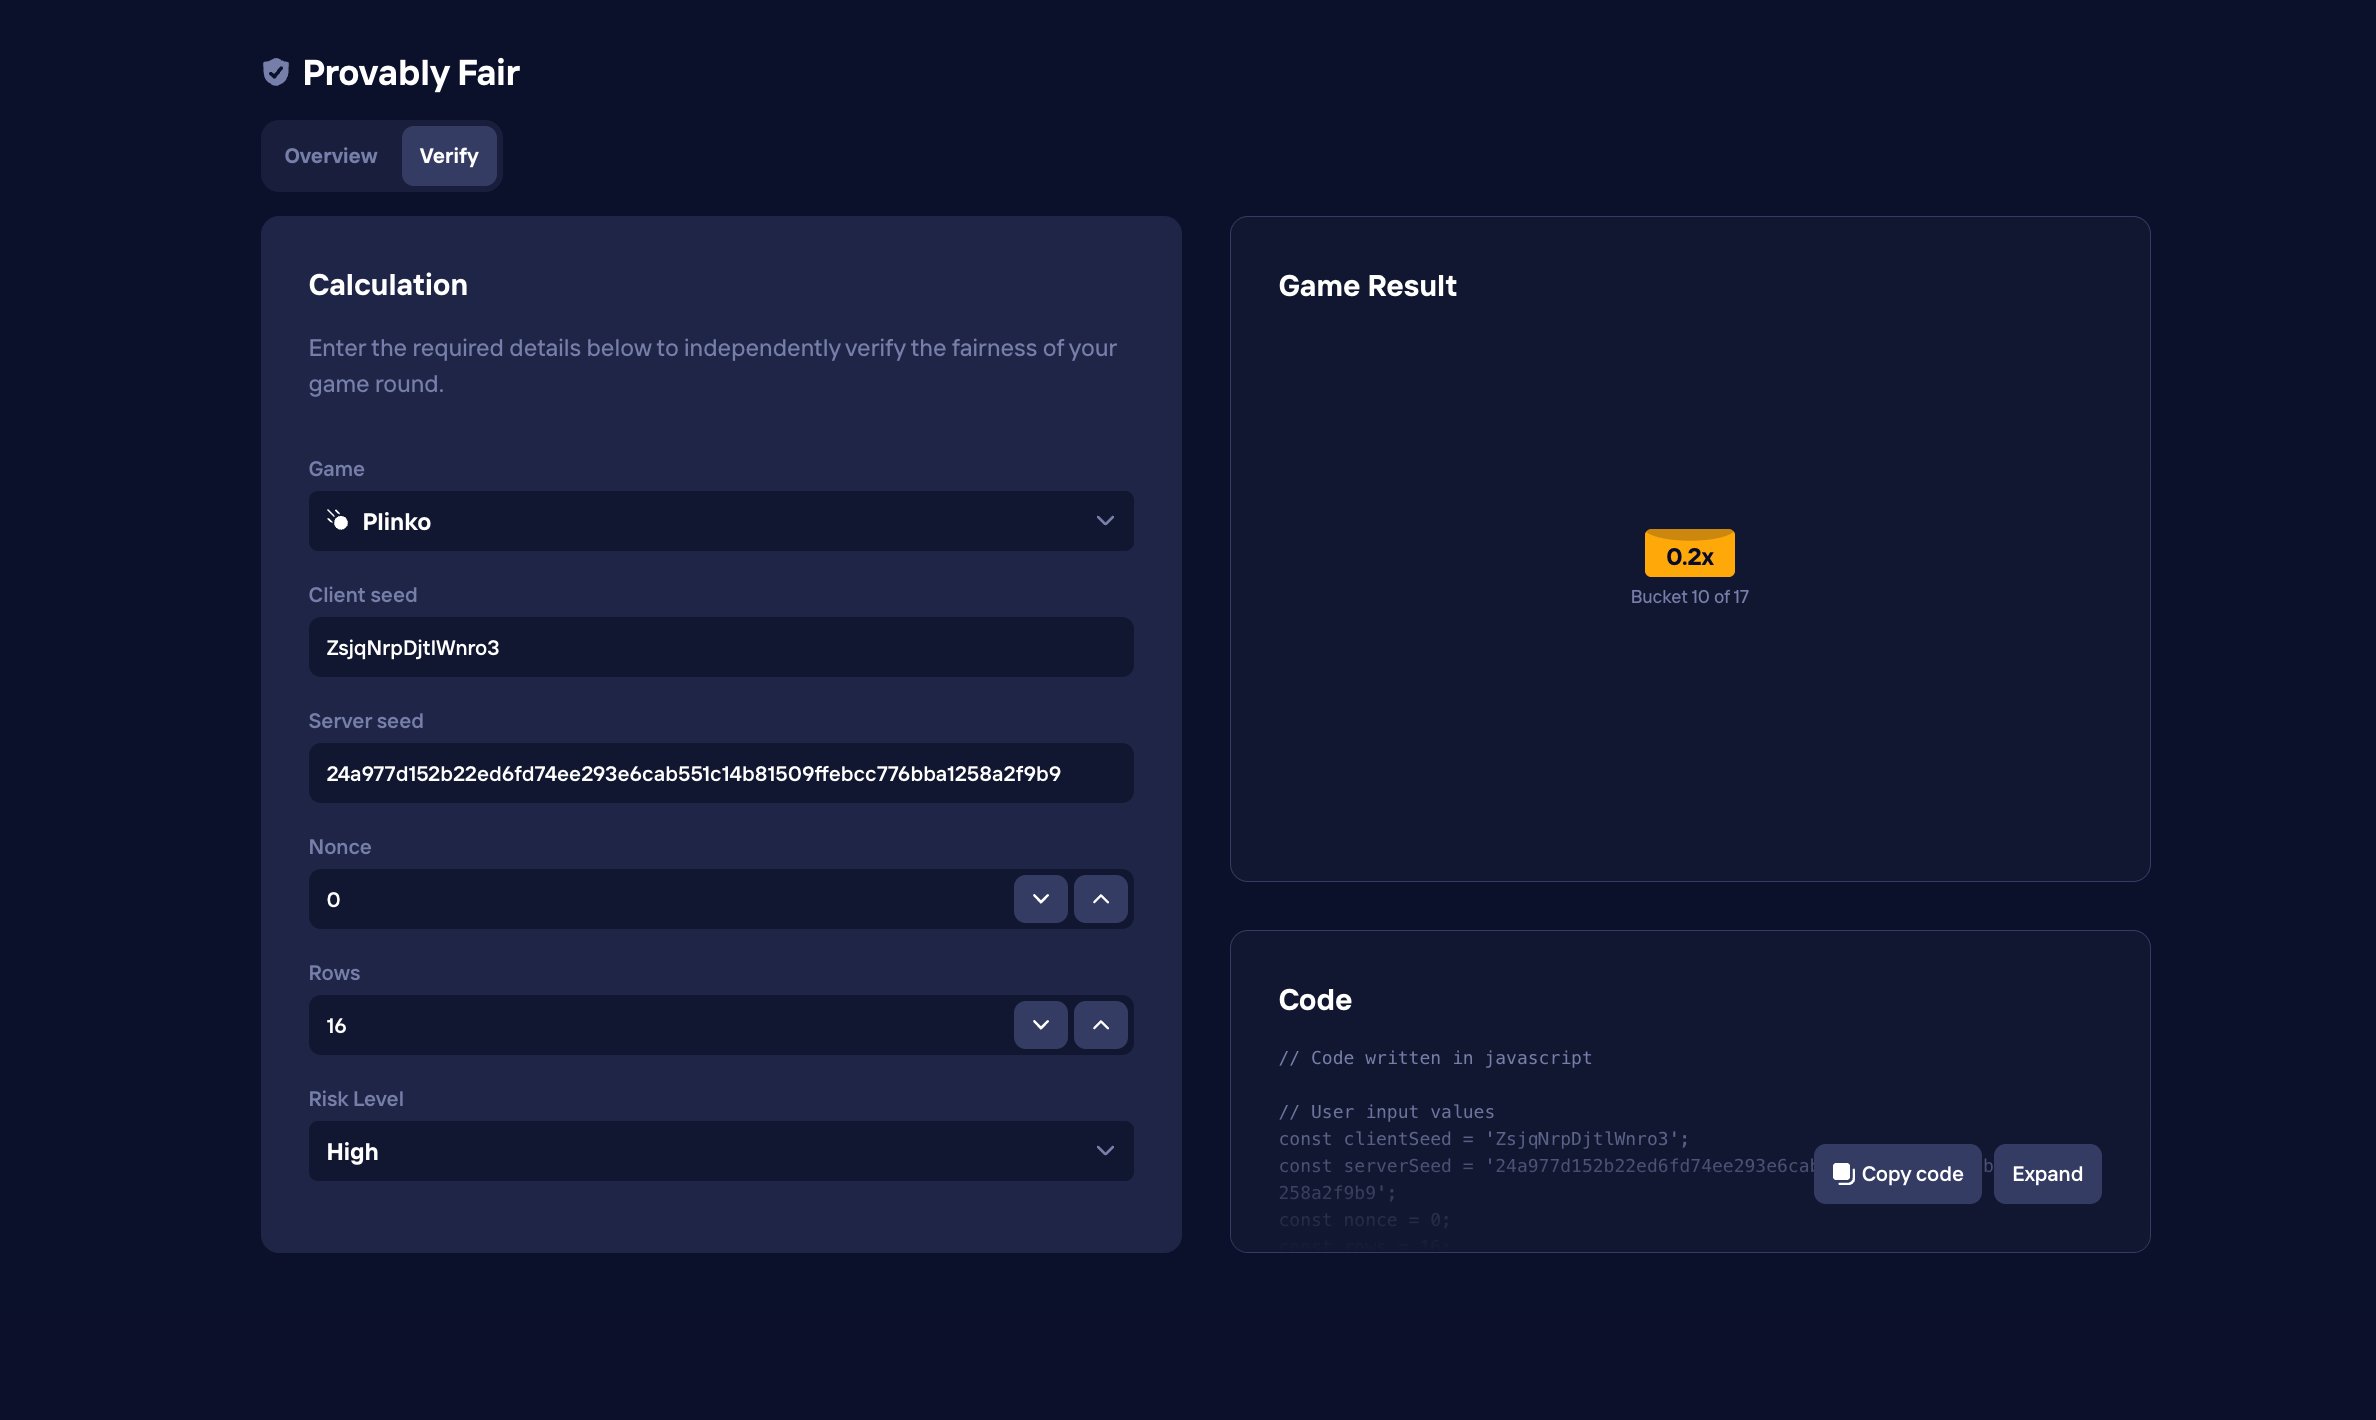
Provably Fair page — seeds populated from the per-bet modal, recomputed slot rendered inline matching the live game result.
Manual Verification (Advanced)6 sections
6.5Why Manual Verification Matters
True provably fair verification means not having to trust any casino-provided tool. Manual verification runs the calculation on your own machine, so a tampered verifier can’t mislead you, and it shows exactly how results are generated.
6.6How the Algorithm Works (Plain English)
The slot is fixed by three ingredients and the row count:
- The server’s secret seed — fixed by the commitment you can save before you bet
- Your client seed — set in your browser and an input to every row
- The nonce — a counter that makes each bet unique
These are combined with HMAC-SHA256, one call per row of the peg board. Each call gives a left or right bounce, and the final slot is the number of right-bounces. The server seed can’t change after your bet without failing to match the commitment you saved, and your client seed is your own input, so a changed one would give a different slot when you recompute.
6.7Casino Verifier vs ProvablyFair.org Verifier4 records
Three verification tools are available. All should produce the same slot; if they don’t, something has changed.
| Duel.com Verifier | This site’s verifier | Main-site verifier | |
|---|---|---|---|
| Source | Casino-controlled | ProvablyFair.org | ProvablyFair.org |
| Access | duel.com/provably-fair/verify | audit.provablyfair.org/casino/duel/tools/verify-bets | www.provablyfair.org/verify-bets/duel |
| Checked in this audit | Its published Verify-tab code, copied and run on 8,100 bets: bucket and path match | Pinned and run on 8,100 bets: slot and path match | Pinned and run on 8,100 bets: slot, path and commitment hash match |
| Trust model | Requires trusting the casino | Open-source, version-controlled | Pinned by SHA-256 in the audit |
6.8Browser Console Checks
Paste these into any browser console, no install needed. First check the commitment: run await verifyHash(serverSeed, savedServerSeedHashed) with the hash you saved before betting. A PASS against a hash read from the bet record afterwards shows consistency only.
// docs/ALGORITHM.md §1.2: commitment = lowercase hex of SHA-256 over the 32 bytes the seed's 64 hex characters encodeasync function verifyHash(serverSeed, savedServerSeedHashed) { // savedServerSeedHashed = your copy from before the bet const seedBytes = Uint8Array.from({ length: serverSeed.length / 2 }, (_, i) => Number.parseInt(serverSeed.substr(2 * i, 2), 16)); const sha = new Uint8Array(await crypto.subtle.digest('SHA-256', seedBytes)); let computed = ''; for (const byte of sha) computed += byte.toString(16).padStart(2, '0'); console.log(computed === savedServerSeedHashed.toLowerCase() ? 'PASS' : `FAIL: got ${computed}`);}final_slot on 8,100 / 8,100 captured bets, and verifyHash prints PASS for 162 / 162 revealed seeds.Then recompute the slot: run await computeSlot(serverSeed, clientSeed, nonce, rows)
// docs/ALGORITHM.md §2: one HMAC per row, bit = first 4 digest bytes (big-endian) mod 2, slot = sum of bitsasync function computeSlot(serverSeed, clientSeed, nonce, rows) { // rows = the board you played, 8 to 16 const seedBytes = Uint8Array.from({ length: serverSeed.length / 2 }, (_, i) => Number.parseInt(serverSeed.substr(2 * i, 2), 16)); const hmacKey = await crypto.subtle.importKey('raw', seedBytes, { name: 'HMAC', hash: 'SHA-256' }, false, ['sign']); const bits = []; for (let i = 0; i < rows; i++) { // Step 1: row cursor i = 0 … rows − 1 const message = new TextEncoder().encode(clientSeed + ':' + nonce + ':' + i); const digest = new DataView(await crypto.subtle.sign('HMAC', hmacKey, message)); bits.push(digest.getUint32(0, false) % 2); // Step 2: u_i big-endian, bit_i = u_i mod 2 } const slot = bits.reduce((sum, bit) => sum + bit, 0); // Step 3: slot = number of 1 bits console.log('slot', slot, 'bits', bits.join('')); return slot;}6.9Python Verification Script
The same verification in Python (standard library only):
import hashlib, hmac def compute_slot(server_seed, client_seed, nonce, rows): key = bytes.fromhex(server_seed) slot = 0 for cursor in range(rows): message = f'{client_seed}:{nonce}:{cursor}'.encode() h = hmac.new(key, message, hashlib.sha256).hexdigest() slot += int(h[:8], 16) % 2 return slot def verify_hash(server_seed, saved_server_seed_hashed): computed = hashlib.sha256(bytes.fromhex(server_seed)).hexdigest() return computed == saved_server_seed_hashed.lower() # Replace with your valuesserver_seed = 'YOUR_SERVER_SEED'saved_server_seed_hashed = 'YOUR_SAVED_SERVER_SEED_HASH' # your copy from before the betclient_seed = 'YOUR_CLIENT_SEED'nonce = 0rows = 16 print('Hash check:', 'PASS' if verify_hash(server_seed, saved_server_seed_hashed) else 'FAIL')print('Computed slot:', compute_slot(server_seed, client_seed, nonce, rows))6.10Evidence Screenshots4 records
| Evidence | Description |
|---|---|
| S08 | Fairness page overview — "What is Provably Fair?" and "How it works" sections |
| S09 | Fairness verification tool — Plinko selected, showing Rows and Risk Level inputs |
| S10 | Fairness page Plinko source code — the full validatePlinkoResult and generateHMAC_SHA256 implementation; the same code, copied as text, is run on every captured bet |
| S11 | Client seed rotation response — the server echoes the client-submitted seed and does not assign it |
Verify a real bet, step by stepVerify a real bet · Swipe for all 4 steps →
How it works
- 1
Save the Commitment
Before your first bet under a seed, open Duel’s Provably Fair modal and copy the active server seed hash. Keep the copy. The modal also shows the next server seed’s hash: save it before you rotate and you hold your next commitment in advance.
- 2
Play, Then Rotate
Place your Plinko bets. When you rotate the seed pair, Duel retires the active server seed and reveals it, so every bet placed under it becomes checkable.
- 3
Find the Bet’s Inputs
Open Transactions and click a past Plinko round. The per-bet modal shows the revealed server seed with the bet ID, client seed and nonce.
- 4
Check and Recompute
Hash the revealed seed and compare it with the copy you saved, not with a hash read from the bet record afterwards. Then recompute the slot with a verifier below or the console checks in 6.8, and look up the payout in the base-tier table.
Technical evidence
6.5Why Manual Verification Matters
True provably fair verification means not having to trust any casino-provided tool. Manual verification runs the calculation on your own machine, so a tampered verifier can’t mislead you, and it shows exactly how results are generated.
6.6How the Algorithm Works (Plain English)
The slot is fixed by three ingredients and the row count:
- The server’s secret seed — fixed by the commitment you can save before you bet
- Your client seed — set in your browser and an input to every row
- The nonce — a counter that makes each bet unique
These are combined with HMAC-SHA256, one call per row of the peg board. Each call gives a left or right bounce, and the final slot is the number of right-bounces. The server seed can’t change after your bet without failing to match the commitment you saved, and your client seed is your own input, so a changed one would give a different slot when you recompute.
6.7Casino Verifier vs ProvablyFair.org Verifier4 records
Three verification tools are available. All should produce the same slot; if they don’t, something has changed.
| Duel.com Verifier | This site’s verifier | Main-site verifier | |
|---|---|---|---|
| Source | Casino-controlled | ProvablyFair.org | ProvablyFair.org |
| Access | duel.com/provably-fair/verify | audit.provablyfair.org/casino/duel/tools/verify-bets | www.provablyfair.org/verify-bets/duel |
| Checked in this audit | Its published Verify-tab code, copied and run on 8,100 bets: bucket and path match | Pinned and run on 8,100 bets: slot and path match | Pinned and run on 8,100 bets: slot, path and commitment hash match |
| Trust model | Requires trusting the casino | Open-source, version-controlled | Pinned by SHA-256 in the audit |
6.8Browser Console Checks
Paste these into any browser console, no install needed. First check the commitment: run await verifyHash(serverSeed, savedServerSeedHashed) with the hash you saved before betting. A PASS against a hash read from the bet record afterwards shows consistency only.
// docs/ALGORITHM.md §1.2: commitment = lowercase hex of SHA-256 over the 32 bytes the seed's 64 hex characters encodeasync function verifyHash(serverSeed, savedServerSeedHashed) { // savedServerSeedHashed = your copy from before the bet const seedBytes = Uint8Array.from({ length: serverSeed.length / 2 }, (_, i) => Number.parseInt(serverSeed.substr(2 * i, 2), 16)); const sha = new Uint8Array(await crypto.subtle.digest('SHA-256', seedBytes)); let computed = ''; for (const byte of sha) computed += byte.toString(16).padStart(2, '0'); console.log(computed === savedServerSeedHashed.toLowerCase() ? 'PASS' : `FAIL: got ${computed}`);}final_slot on 8,100 / 8,100 captured bets, and verifyHash prints PASS for 162 / 162 revealed seeds.Then recompute the slot: run await computeSlot(serverSeed, clientSeed, nonce, rows)
// docs/ALGORITHM.md §2: one HMAC per row, bit = first 4 digest bytes (big-endian) mod 2, slot = sum of bitsasync function computeSlot(serverSeed, clientSeed, nonce, rows) { // rows = the board you played, 8 to 16 const seedBytes = Uint8Array.from({ length: serverSeed.length / 2 }, (_, i) => Number.parseInt(serverSeed.substr(2 * i, 2), 16)); const hmacKey = await crypto.subtle.importKey('raw', seedBytes, { name: 'HMAC', hash: 'SHA-256' }, false, ['sign']); const bits = []; for (let i = 0; i < rows; i++) { // Step 1: row cursor i = 0 … rows − 1 const message = new TextEncoder().encode(clientSeed + ':' + nonce + ':' + i); const digest = new DataView(await crypto.subtle.sign('HMAC', hmacKey, message)); bits.push(digest.getUint32(0, false) % 2); // Step 2: u_i big-endian, bit_i = u_i mod 2 } const slot = bits.reduce((sum, bit) => sum + bit, 0); // Step 3: slot = number of 1 bits console.log('slot', slot, 'bits', bits.join('')); return slot;}6.9Python Verification Script
The same verification in Python (standard library only):
import hashlib, hmac def compute_slot(server_seed, client_seed, nonce, rows): key = bytes.fromhex(server_seed) slot = 0 for cursor in range(rows): message = f'{client_seed}:{nonce}:{cursor}'.encode() h = hmac.new(key, message, hashlib.sha256).hexdigest() slot += int(h[:8], 16) % 2 return slot def verify_hash(server_seed, saved_server_seed_hashed): computed = hashlib.sha256(bytes.fromhex(server_seed)).hexdigest() return computed == saved_server_seed_hashed.lower() # Replace with your valuesserver_seed = 'YOUR_SERVER_SEED'saved_server_seed_hashed = 'YOUR_SAVED_SERVER_SEED_HASH' # your copy from before the betclient_seed = 'YOUR_CLIENT_SEED'nonce = 0rows = 16 print('Hash check:', 'PASS' if verify_hash(server_seed, saved_server_seed_hashed) else 'FAIL')print('Computed slot:', compute_slot(server_seed, client_seed, nonce, rows))6.10Evidence Screenshots4 records
| Evidence | Description |
|---|---|
| S08 | Fairness page overview — "What is Provably Fair?" and "How it works" sections |
| S09 | Fairness verification tool — Plinko selected, showing Rows and Risk Level inputs |
| S10 | Fairness page Plinko source code — the full validatePlinkoResult and generateHMAC_SHA256 implementation; the same code, copied as text, is run on every captured bet |
| S11 | Client seed rotation response — the server echoes the client-submitted seed and does not assign it |
Only disclosed inputs are used, and identical inputs always produce identical output. Save the commitment before you bet: your saved copy is what shows the seed was fixed before your bet.
Reproducibility & Artifacts
Can anyone independently reproduce every finding in this audit?
This section consolidates the open-source repository, datasets, output artifacts and reproducibility of the audit. Every scored step, statistic and verdict in the package can be reproduced by anyone with a computer and an internet connection: check out release v1.4.2, run npm test, and the run is compared with the committed results. The repository is the credential, not this report.
Check out release v1.4.2 and run npm test. The run is compared with the committed results.

Open-Source Audit Repository
Repository details
- GitHub: ProvablyFair-org/duel-plinko
- Release: v1.4.2 (Framework 1.1)
- Original audit: 5bb2cd4 (June 2026)
- Game: Plinko (duel-plinko)
- Public Verifier: provablyfair.org/verify-bets/duel
Prerequisites
- Node.js 22.x (pinned in package.json and .nvmrc)
- npm
- Git
- Up to 20 minutes on 2 cores, 6 on 12
- GitHub: ProvablyFair-org/duel-plinko
- Release: v1.4.2 (Framework 1.1)
- Original audit: 5bb2cd4 (June 2026)
- Game: Plinko (duel-plinko)
- Public Verifier: provablyfair.org/verify-bets/duel
- Node.js 22.x (pinned in package.json and .nvmrc)
- npm
- Git
- Up to 20 minutes on 2 cores, 6 on 12
 github.com/ProvablyFair-org/duel-plinko ↗
Check out the release tag, then install. Use Node 22.x, as pinned in .nvmrc and package.json. npm test runs the standalone-build check, 44 unit tests, the step-registry and S5-matrix checks, then the 23-step verifier, which replays all 27M simulated rounds. Allow 20 minutes on 2 cores and 6 on 12.
git clone https://github.com/ProvablyFair-org/duel-plinko.gitcd duel-plinkogit checkout v1.4.2npm ci # Run the entire audit end to endnpm testOur run on Node 22.22.0, 2 cores: exit 0 in 10 min 40 s. Each step prints [PASS], [FAIL] (a hard fail), [FLAG:capture] (limited by our capture, verdict-neutral) or [FLAG:operator] (verdict-affecting). The within-tolerance count and the largest gap on the last line depend on the CPU. The output is abridged: the input-hash checks, the S5-matrix check, the informational lines and the RTP claim block (shown in 4.15) are not repeated here.
npm testExpected verification output
[standalone] Source inventory, unit-test inventory and both compiled entry points match the build manifest.# tests 44# pass 44# fail 0[check-outputs] OK: 23 scored steps, ids 1..23 each once, names as tests/steps declares; summary reconciles (22 pass, 1 flag, 0 hard-fail). ══════════════════════════════════════════════════════════ PLINKO v3 AUDIT — VERIFICATION SUITE══════════════════════════════════════════════════════════ Dataset: 8100 bets | Seeds: 166 Phase A: 5400 Phase B: 2000 Phase C: 200 Phase D: 500 [PASS] Step 1 — Seed Hash Integrity [PASS] Step 2 — Next-Seed Promotion (Commitment Linkage) [PASS] Step 3 — Hash Consistency Within Epoch [FLAG:capture] Step 4 — Nonce Audit [PASS] Step 5 — Slot Recomputation & Bit-Extraction Bound [PASS] Step 6 — Client Seed Influence (exact null) [PASS] Step 7 — Payout Math [PASS] Step 8 — Multiplier Table Provenance [PASS] Step 9 — Phase C Code-Path Equivalence [PASS] Step 10 — Zero Edge Audit [PASS] Step 11 — Config Completeness & Cell Coverage [PASS] Step 12 — Epoch Size & Count [PASS] Step 13 — Multiplier Table + Symmetry [PASS] Step 14 — Population & Phase Labels [PASS] Step 15 — Dataset Hash 3cf9359d88220bc800bb32edfe04399f55b909302262928ee3a0582715635267 [PASS] Step 16 — Scaling Edge Analysis [PASS] Step 17 — Probability Independence (Anti-Circularity) [PASS] Step 18 — Phase D — Client Seed Variation [REPLAY] Pass 1: 27/27 configs × 1,000,000 rounds regenerated from the pinned seeds in 510.7 s [PASS] Step 19 — Simulation Results — Pass 1 Integrity (re-derived & replayed) 27,000,000 rounds × 27 configs; avg RTP=99.9166%. RTP, standard error, chi-squared and its p-value re-derived in verify from the committed histograms for 27/27 configs and required to agree with the artifact's own scalars; the whole experiment REPLAYED from the pinned seeds (27/27 configs × 1,000,000 rounds): census exact (0 slot-count mismatches), 691 derived figures compared, 691 within the reproduction tolerance, 0 beyond the reproduction tolerance. 0/27 configs fail at Bonferroni-corrected threshold (α/27 = 0.00037). 0/27 flag even at uncorrected α = 0.01. [REPLAY] Pass 2: 162 revealed epochs × 10,000 nonces + 10,000 calibration seeds × 50 nonces in 45.1 s; 8100 captured bets bound (0 mismatches); Tests A/B re-derived on 242 rows (0 mismatches) [TEST C] 1/162 epochs flagged at p ≤ 0.01 (family survival 0.8037, fails at ≥ 8); broad 0; pooled z -0.554; below/above expectation 98/64 (null 99.9 below); power at 10% shortfall: per-epoch 12.7%, family at 25% picked 30.7% [PASS] Step 20 — Simulation Results — Pass 2 Cherry-Pick Test Pass 2: 162 seeds × 10,000 nonces. Artifact verdicts: Test A=PASS, Test B=PASS. Early-window statistical flags: 10 of 242 (within expected false-positive range; threshold 13). Multi-window: 8 isolated-early, 2 multi-window noise. [PASS] Step 21 — Artifact Integrity (pinned artifacts of record) [PASS] Step 22 — Published-Pin Drift Scan [PASS] Step 23 — Epoch-Window Slot Fit (live drops vs binomial) ══════════════════════════════════════════════════════════ RESULTS SUMMARY══════════════════════════════════════════════════════════ Passed: 22/23 Hard fails: 0 CAPTURE-ORIGIN LIMITATIONS (disclosed, verdict-neutral): ⚑ Step 4: Nonce Audit VERDICT: PROVABLY FAIR — Full Pass Committed artifacts NOT modified. Reproduction vs the committed artifacts on Node 22.22.0: REPRODUCED (3 within tolerance, largest 1.33e-15 at steps[18].details.rederivation.perConfig[23].pValue)Runs write only to outputs/run/, which is compared with the committed results field by field: integers and strings exactly, everything else within 1e-14 absolute + 1e-12 relative. A difference beyond that exits 1. Committed artifacts are never rewritten by a run. npm run test:full also regenerates the whole simulation into outputs/run/ and diffs it.
npm testcat outputs/run/diff.jsonnode scripts/release-manifest.mjs --checkExpected verification output
Committed artifacts NOT modified.Reproduction vs the committed artifacts on Node 22.22.0: REPRODUCED (3 within tolerance, largest 1.33e-15 at steps[18].details.rederivation.perConfig[23].pValue)[release-manifest] OK: 8 artifact hashes match disk, verdict "PROVABLY FAIR — Full Pass", scored 22/23 (flags 1)The exit code is the verdict, so nothing automated can read a Conditional Pass as clean. This release exits 0.
0 PROVABLY FAIR — Full Pass, and the run reproduces the committed artifacts1 NOT PROVABLY FAIR (a hard fail), or a reproduction difference beyond tolerance2 PROVABLY FAIR — Conditional Pass (at least one verdict-affecting flag)5 RTP FIGURE OVERSTATED: no draw check failed, but a setting pays more than 0.1 pp below the published RTPAudit Reproducibility Pinning
- Release
- v1.4.2 · Framework 1.1
- Original Audit
- 5bb2cd4a0ea159af118c3000b74298a16b2f89ad · June 2026
- Signed Tag
- v1.4.2, ProvablyFair.org SSH key SHA256:gEujiJm2pRyq7lQsfYQfQ1r97H/J7GdaKHbOW8GtikY
- Node Version
- 22.x (package.json engines, .nvmrc)
- Dataset
- data/plinko-master-8100bets.json (8,100 bets, 166 seed entries)
- Dataset Hash (SHA-256)
- 3cf9359d88220bc800bb32edfe04399f55b909302262928ee3a0582715635267
- Config Hash (SHA-256)
- 78f0a39201a8c24fd1577143732e004f77e27d4d36efeedc6b3f7b93b2078fed
- verification-results.json
- ea3cce898ae6baad7965415f6926e5466dd5f73ad8754045a290ef133d18faca
- simulation-results.json
- b7744254a4d331158ab8f789581c37ecf64aeec123dcf71a651cc13859699514
- determinism-log.json
- 5d5c00c597424ea5ba692454c5998a53ec6ff21e1e314908d79553d7213859f4
- chi-squared-results.json
- c6d8f718085c388d7f9ab06d2747e98b74541d39724f214866dc6767df255d84
- rtp-claim-table.json
- eca16ed27d4cb5bf9c457b48b98fe8a73d71278eeac3a7cbb66250aca08b47cf
- rtp-convergence.html
- 57a9b8a30cee238c35dc785ed51c2333bbfc4bf25e4983436f86e2dfe7d279e9
- Mutation Battery
- 52 / 52 counterexamples rejected · 23 / 23 scored steps covered
- Runtime
- 10 min 40 s on 2 cores (Node 22.22.0) · budget 20 min on 2 cores, 6 on 12
- Audit Date
- Captured 10 April 2026 · updated October 2026
- Audit ID
- PF-2026-DL01
Audit Reproducibility Pinning
- Release
- v1.4.2 · Framework 1.1
- Original Audit
- 5bb2cd4a0ea159af118c3000b74298a16b2f89ad · June 2026
- Signed Tag
- v1.4.2, ProvablyFair.org SSH key SHA256:gEujiJm2pRyq7lQsfYQfQ1r97H/J7GdaKHbOW8GtikY
- Node Version
- 22.x (package.json engines, .nvmrc)
- Dataset
- data/plinko-master-8100bets.json (8,100 bets, 166 seed entries)
- Dataset Hash (SHA-256)
- 3cf9359d88220bc800bb32edfe04399f55b909302262928ee3a0582715635267
- Config Hash (SHA-256)
- 78f0a39201a8c24fd1577143732e004f77e27d4d36efeedc6b3f7b93b2078fed
- verification-results.json
- ea3cce898ae6baad7965415f6926e5466dd5f73ad8754045a290ef133d18faca
- simulation-results.json
- b7744254a4d331158ab8f789581c37ecf64aeec123dcf71a651cc13859699514
- determinism-log.json
- 5d5c00c597424ea5ba692454c5998a53ec6ff21e1e314908d79553d7213859f4
- chi-squared-results.json
- c6d8f718085c388d7f9ab06d2747e98b74541d39724f214866dc6767df255d84
- rtp-claim-table.json
- eca16ed27d4cb5bf9c457b48b98fe8a73d71278eeac3a7cbb66250aca08b47cf
- rtp-convergence.html
- 57a9b8a30cee238c35dc785ed51c2333bbfc4bf25e4983436f86e2dfe7d279e9
- Mutation Battery
- 52 / 52 counterexamples rejected · 23 / 23 scored steps covered
- Runtime
- 10 min 40 s on 2 cores (Node 22.22.0) · budget 20 min on 2 cores, 6 on 12
- Audit Date
- Captured 10 April 2026 · updated October 2026
- Audit ID
- PF-2026-DL01
Output Artifacts
- verification-results.json · 201 KB
- Steps 1–23 with per-step details, profile mappings and the verdict
- simulation-results.json · 162 KB
- Pass 1 (27M rounds, pinned seeds) and Pass 2 (162 casino seeds × 10,000 nonces)
- determinism-log.json · 1.4 MB
- Per-bet computed_slot vs actual_slot for all 8,100 bets
- chi-squared-results.json · 18 KB
- Per-configuration live chi-squared statistics and p-values
- rtp-claim-table.json · 5 KB
- Exact RTP of all 27 settings against the published 99.9% (RTP claim rule)
- rtp-convergence.html · 5 KB
- Self-contained RTP convergence chart (inline SVG)
Output Artifacts6 committed artifacts
| File | Contents | Size |
|---|---|---|
| verification-results.json | Steps 1–23 with per-step details, profile mappings and the verdict | 201 KB |
| simulation-results.json | Pass 1 (27M rounds, pinned seeds) and Pass 2 (162 casino seeds × 10,000 nonces) | 162 KB |
| determinism-log.json | Per-bet computed_slot vs actual_slot for all 8,100 bets | 1.4 MB |
| chi-squared-results.json | Per-configuration live chi-squared statistics and p-values | 18 KB |
| rtp-claim-table.json | Exact RTP of all 27 settings against the published 99.9% (RTP claim rule) | 5 KB |
| rtp-convergence.html | Self-contained RTP convergence chart (inline SVG) | 5 KB |
Repository Structure
duel-plinko/
├── src/
│   ├── rng.ts                  → HMAC-SHA256 RNG, rebuilt from docs/ALGORITHM.md
│   ├── config.ts               → Multiplier lookup + theoretical RTP
│   ├── simulate.ts             → Two-pass simulation (27M rounds; 162 seeds × 10,000 nonces)
│   ├── pass1.ts                → Pass 1 loop shared by the simulation and its replay
│   ├── sim-seeds.ts            → Pinned simulation seeds
│   ├── rtp-claim.ts            → RTP claim rule 1.2.0 (framework copy)
│   ├── rtp-settings.ts         → Exact per-setting RTP table and the claim
│   ├── operator-verifier.ts    → Runs Duel’s Verify-tab code as a second check
│   ├── site-verifier.ts        → Runs this site’s verifier on every bet
│   ├── live-site-verifier.ts   → Runs the main-site verifier on every bet
│   ├── diff.ts                 → Reproduction gate (run vs committed results)
│   ├── profile-map.ts          → Step → Plinko profile check mapping
│   ├── stats.ts                → Binomial, chi-squared, autocorrelation, runs test
│   └── loader.ts               → Dataset loader, pinned population and hashes
├── tests/
│   ├── verify.ts               → 23-step verification suite
│   ├── mutations.json          → 52 counterexamples for the mutation battery
│   ├── steps/
│   │   ├── commitment.ts       → Steps 1–4: commitments and nonces
│   │   ├── determinism.ts      → Steps 5–6: recomputation, verifiers, client seed
│   │   ├── payouts.ts          → Steps 7–9: payout math + Phase C
│   │   ├── dataset.ts          → Steps 10–16: dataset and config checks
│   │   ├── anti-circularity.ts → Step 17: probability independence
│   │   ├── phase-d.ts          → Step 18: client seed variation
│   │   ├── simulation.ts       → Steps 19–20: simulation replay + cherry-pick tests
│   │   ├── artifacts.ts        → Step 21: artifact integrity
│   │   ├── publication.ts      → Step 22: published-pin drift scan
│   │   └── live-fit.ts         → Step 23: epoch-window slot fit
│   └── plinko/                 → Unit tests (44, incl. the spec self-test)
├── docs/
│   ├── ALGORITHM.md            → The written RNG specification
│   └── INTERFACE.md            → Module interface for the rebuild
├── data/
│   └── plinko-master-8100bets.json → 8,100 live bets (4 phases, 166 seed entries)
├── outputs/                    → Committed artifacts of record (runs write to outputs/run/)
│   ├── verification-results.json
│   ├── simulation-results.json
│   ├── determinism-log.json
│   ├── chi-squared-results.json
│   ├── rtp-claim-table.json
│   └── rtp-convergence.html
├── verifier-parity/            → Pinned copies of the player verifiers and Duel’s runner
├── evidence/                   → Screenshots, the dated config copy, Duel’s Verify-tab code
├── capture/                    → Reference records of the capture scripts (not runnable)
├── scripts/                    → Build, check, mutation and release tooling
├── plinkoConfig.json           → Duel.com game configuration (27 configs, 191 brackets each)
├── verify.js · test.js         → Standalone builds run by npm test
├── RELEASE-MANIFEST.json       → Release identity, artifact hashes, signature
├── README.md
├── MANIFEST.md
└── package.json
Step-to-Section Cross-Reference23 scored steps mapped
| Step | Test Name | Report Section | Result |
|---|---|---|---|
| 1 | Seed Hash Integrity | S1 | Pass |
| 2 | Next-Seed Promotion (Commitment Linkage) | S1 | Pass |
| 3 | Hash Consistency Within Epoch | S1 | Pass |
| 4 | Nonce Audit | S1, S5 | Capture flag |
| 5 | Slot Recomputation & Bit-Extraction Bound | S1, S2, S3 | Pass |
| 6 | Client Seed Influence (exact null) | S1, S2 | Pass |
| 7 | Payout Math | S3, S4 | Pass |
| 8 | Multiplier Table Provenance | S3, S4 | Pass |
| 9 | Phase C Code-Path Equivalence | S3, S4 | Pass |
| 10 | Zero Edge Audit | S4 | Pass |
| 11 | Config Completeness & Cell Coverage | S3 | Pass |
| 12 | Epoch Size & Count | S1, S3 | Pass |
| 13 | Multiplier Table + Symmetry | S3 | Pass |
| 14 | Population & Phase Labels | S3 | Pass |
| 15 | Dataset Hash | S7 | Pass |
| 16 | Scaling Edge Analysis | S4 | Pass |
| 17 | Probability Independence (Anti-Circularity) | S4 | Pass |
| 18 | Phase D — Client Seed Variation | S1, S2 | Pass |
| 19 | Simulation Results — Pass 1 Integrity (re-derived & replayed) | S2, S4 | Pass |
| 20 | Simulation Results — Pass 2 Cherry-Pick Test | S4 | Pass |
| 21 | Artifact Integrity (pinned artifacts of record) | S7 | Pass |
| 22 | Published-Pin Drift Scan | S7 | Pass |
| 23 | Epoch-Window Slot Fit (live drops vs binomial) | S4 | Pass |
Game Profile CoveragePlinko profile 1.0.2 · 39 checks
Framework 1.1 requires every check in the game profile to be covered by a scored step, by a package check, or marked n/a with a reason. All 39 checks of the Plinko profile 1.0.2 are accounted for: 28 by scored steps, 9 by package checks and 2 n/a. The package marks every covered check as full coverage; none is partial.
| Profile check | Covered by | Coverage |
|---|---|---|
| PLINKO-01 | Step 1 (Seed Hash Integrity) | Full |
| PLINKO-02 | Step 2 (Next-Seed Promotion) | Full |
| PLINKO-03 | Step 3 (Hash Consistency Within Epoch) + Step 4 (Nonce Audit) | Full |
| PLINKO-04 | Step 4 (Nonce Audit) · capture flag, verdict-neutral | Full |
| PLINKO-05 | Step 12 (Epoch Size & Count) + Step 14 (Population & Phase Labels) | Full |
| PLINKO-06 | Step 6 (Client Seed Influence) + Step 18 (Phase D — Client Seed Variation) | Full |
| PLINKO-07 | Step 5 (Slot Recomputation & Bit-Extraction Bound) | Full |
| PLINKO-08 | Step 5 (Slot Recomputation & Bit-Extraction Bound) | Full |
| PLINKO-09 | Package check: RNG rebuilt from the written spec (docs/ALGORITHM.md, spec self-test); Duel’s Verify-tab code run unmodified as a second check in Step 5 | Full |
| PLINKO-10 | Step 7 (Payout Math) + Step 8 (Multiplier Table Provenance) | Full |
| PLINKO-11 | Step 7 (Payout Math) | Full |
| PLINKO-12 | Step 9 (Phase C Code-Path Equivalence) | Full |
| PLINKO-13 | Step 8 (Multiplier Table Provenance) | Full |
| PLINKO-14 | Step 13 (Multiplier Table + Symmetry) | Full |
| PLINKO-15 | Step 11 (Config Completeness & Cell Coverage) | Full |
| PLINKO-16 | n/a: no bet response in the capture carries a balance field, so there is no consecutive-bet delta to reconcile | n/a |
| PLINKO-17 | Step 10 (Zero Edge Audit) + Step 16 (Scaling Edge Analysis) | Full |
| PLINKO-18 | Step 17 (Probability Independence) | Full |
| PLINKO-19 | Step 19 (Simulation Pass 1) · RTP claim rule scored here | Full |
| PLINKO-20 | Step 19 (Simulation Pass 1) | Full |
| PLINKO-21 | Step 20 (Simulation Pass 2) | Full |
| PLINKO-22 | Step 23 (Epoch-Window Slot Fit) | Full |
| PLINKO-23 | Package check: The S5 matrix in MANIFEST.md, checked on every npm test | Full |
| PLINKO-24 | Package check: Both ProvablyFair.org player verifiers pinned and executed on every bet in Step 5 | Full |
| PLINKO-25 | Package check: The “Verify a bet” guide in MANIFEST.md, linked from the README | Full |
| PLINKO-26 | Step 15 (Dataset Hash) | Full |
| PLINKO-27 | Step 21 (Artifact Integrity) | Full |
| PLINKO-28 | Package check: npm test and the reproduction gate: runs write to outputs/run/ and are compared with the committed results | Full |
| PLINKO-29 | Package check: The mutation battery: 52 counterexamples, each rejected by a named scored step | Full |
| PLINKO-30 | Package check: The evidence register, declared limitations and load-bearing premises in MANIFEST.md | Full |
| PLINKO-31 | Step 19 (Simulation Pass 1) | Full |
| PLINKO-32 | Step 19 (Simulation Pass 1) | Full |
| PLINKO-33 | Package check: scripts/check-outputs.mjs: 23 scored steps, ids 1..23 each exactly once | Full |
| PLINKO-34 | n/a: the suite has no mode that narrows what a run attests (no sampled re-execution, no baseline re-emission) | n/a |
| PLINKO-35 | Step 22 (Published-Pin Drift Scan) | Full |
| PLINKO-36 | Step 6 (Client Seed Influence) | Full |
| PLINKO-37 | Package check: The standalone build check: verify.js and test.js match the committed sources | Full |
| PLINKO-38 | Step 20 (Simulation Pass 2) | Full |
| PLINKO-39 | Step 16 (Scaling Edge Analysis) | Full |
outputs/verification-results.json (profileCoverage and each step’s profileChecks).Release Historyv1.0.0 → v1.4.2
| Release | What changed | Verdict |
|---|---|---|
| v1.0.0 | The original audit, June 2026 (commit 5bb2cd4); the tag, set in September 2026, also carries two artifact-pinning commits | Full Pass |
| v1.1.0 | Hardening pass under Framework 1.0 | Unchanged |
| v1.1.1 | Simulation artifact serialised exactly as the generator writes it; no figure changed | Unchanged |
| v1.2.0 | Reproduction gate, exit codes and read-only committed artifacts | Unchanged |
| v1.3.0 | Conformance with the Plinko game profile under Framework 1.1: one new scored step, the RTP claim rule and a mutation battery | Unchanged |
| v1.4.0 | RNG code rebuilt from a written spec; Duel’s Verify-tab code kept as a second check | Unchanged |
| v1.4.1 | A .gitattributes file keeps a Windows clone byte-identical; no audit content changed | Unchanged |
| v1.4.2 | A source comment drops a guard-code label that no file in the package defined; no scored step, figure or verdict changed | Unchanged |
reproduce-audit.sh
# Clone the releasegit clone https://github.com/ProvablyFair-org/duel-plinko.gitcd duel-plinkogit checkout v1.4.2npm ci # Run the full audit (44 unit tests + 23 scored steps, Node 22.x)npm test # Optional: regenerate the simulation into outputs/run/ and diff itnpm run test:full # Confirm the release manifest against the files on disknode scripts/release-manifest.mjs --checkCheck out release v1.4.2 and run npm test: every result is recomputed, written to outputs/run/ and compared with the committed artifacts, and the exit code is the verdict. The dataset and config hashes pin the exact 8,100 bets and table.