Crash
Independent verification, backed by open-source code.


 Passed
- Live Bets Verified
- 1,100
- Parity Rate
- 100%
- Simulated RoundsSimulated RTP 99.872% (mean of 5 targets)
- 5M
- Simulated RTP 99.872% (mean of 5 targets)
- Proven RTP
- 99.9%
- At most 99.9% at every cash-out target
Verification pipeline
Real bets. Independently reproduced.
Placed anonymously at Duel.com. We rebuilt the game logic from scratch and matched all 1,100 recorded outcomes.
The casino result, reproduced.
- Casino outcome
- Crash at 1.35×
- Our reproduction
- Crash at 1.35×
- Recorded amountWon
- $0.010989


- Seed Hash IntegrityPass
- drand Bet TimingPass
- drand Round MonotonicityPass
- Server Seed UniquenessPass
- Outcome RecomputationPass
- Bet-Size InvariancePass
- Payout MathPass
- House Edge AuditPass
- Phase CoveragePass
- Dataset HashPass
- drand Chain FormulaPass
- Anti-CircularityPass
- Simulation Pass 1Pass
- Simulation Pass 2 (Casino Seeds)Pass
- drand API Signature VerificationPass
- Configuration CoveragePass
- Artifact IntegrityPass
- Live-Sample FitPass


The repo is the credential. Check out v1.2.1 and run npm test: 19 unit tests, then all 18 scored steps offline — both simulation passes replayed from their seeds, every pinned artifact checked, and the result compared with the committed one.

This audit verifies the Crash game operated by Duel.com under Framework 1.1. We captured 1,100 live rounds across three phases in April 2026 and reproduced every crash point by exact equality with our own implementation, written from a specification. Every round opens its own commitment, every drand beacon matches the public quicknet chain, and the theoretical RTP is between 99.899768% and 99.9% at every cash-out target. The release package v1.2.1 re-runs all 18 scored steps offline and reports PROVABLY FAIR — Full Pass.

Audit Verdict
| Check | Result | Evidence |
|---|---|---|
| Overall Status | Pass | PROVABLY FAIR — Full Pass: 18/18 scored steps passed, 0 flags, 0 hard fails (Framework 1.1, release v1.2.1) |
| Proven RTP | Pass | At most 99.9% at every cash-out target (flat 0.1% distribution edge); 99.9000% to 4 dp from 1.01× to 2,156.11×; lowest 99.899768% at 9,999.05× with Duel's stated 9,999.999× cap applied. RTP claim (RTP-CLAIM 1.2.0): the flat 99.9% on Duel's fairness page holds at all 9,999,900 targets within ±0.1 pp — PASS |
| Live ↔︎ Verifier Parity | Pass | 1,100 / 1,100 crash points reproduced by exact equality; Duel's own Verify-tab code and both ProvablyFair.org verifiers agree on all 1,100 |
| Commit-Reveal System | Pass | 1,100 / 1,100 revealed seeds hash to their own round's commitment, 1,100 distinct seeds — a consistency check. The capture kept no receipt time for each hash, so the order is taken from the game's design (S1) |
| drand Beacon | Pass | 1,100 / 1,100 signatures equal the pinned api.drand.sh records; publication times follow the quicknet chain formula; every bet accepted before its beacon published, on Duel's transaction clock (min 0.404 s) |
| Client Seed | N/A | Crash is multiplayer: one crash point per round, no client seed in the message. The drand beacon is the outside randomness |
| RNG Analysis | Pass | Our own implementation, written from the specification; Duel's Verify-tab code run unmodified as a cross-check only. 5M simulated rounds are consistent with the survival law (Fisher's p = 0.5382) |
| Payout Logic | Pass | 1,100 / 1,100 win flags follow crash ≥ target (4 ties won); 671 / 671 recorded amountWon = stake × target × 0.999; the wallet ledger credits the full stake × target on the 3 wins looked up |
| Anti-Circularity | Pass | uint32 counts from a separate per-value model equal src/rng.ts at 11 targets; every RTP at or below 99.9% in integer arithmetic; both negative controls rejected |
| Cherry-Pick Screen | Pass | 1,100 casino seeds × 10,000 beacon values find no sign of seed selection: return z 0.286, rank-sum z 0.160 against a −3.291 threshold |
| Fairness Integrity | Pass | 16 fairness integrity tests — 14 pass, 1 N/A (single-step game), 1 flag disclosed (payout input-validation gap — does not affect fairness) |
| Reproducibility | Pass | npm test re-runs all 18 steps offline and compares the result with the committed artifact: REPRODUCED, exit 0 |
| Game Profile | Pass | Crash profile 1.0.3: all 30 checks accounted for — 21 by scored steps, 6 by package checks, 3 n/a; 4 partial as the package states (Game profile coverage) |
Overall StatusPass
v1.2.1)Proven RTPPass
Live ↔︎ Verifier ParityPass
Commit-Reveal SystemPass
drand BeaconPass
Client SeedN/A
RNG AnalysisPass
Payout LogicPass
amountWon = stake × target × 0.999; the wallet ledger credits the full stake × target on the 3 wins looked upAnti-CircularityPass
src/rng.ts at 11 targets; every RTP at or below 99.9% in integer arithmetic; both negative controls rejectedCherry-Pick ScreenPass
Fairness IntegrityPass
ReproducibilityPass
npm test re-runs all 18 steps offline and compares the result with the committed artifact: REPRODUCED, exit 0Game ProfilePass

What Was Audited
✓ Audited
- The base stake tier: both captured stakes, $0.01 and $10, ran at the base 0.1% edge (
effectiveEdge0.1 on all 1,100 rounds) - Every revealed server seed hashes to its round's commitment — one fresh seed per round, 1,100 distinct
- Every crash point reproduces from
(serverSeed, drandRandomness)by exact equality — 1,100 / 1,100 - Every drand value is the public quicknet signature for its round, published on the chain's fixed schedule
- Every bet was accepted before its beacon published, measured on Duel's transaction timestamps
- The theoretical RTP is at most 99.9% at every cash-out target, derived from the algorithm alone
- The published 99.9% RTP holds at every target a player can choose, within ±0.1 percentage point
- Win flags follow crash ≥ target on every round; stake does not move the crash point or the per-unit return
- Players can check every round with public inputs and either ProvablyFair.org verifier

What Audit Excludes
- Stakes above the captured tier — the release carries no stake-tier configuration (S4.4)
- Max win
- Zero Edge rakeback and its daily cap — 99.9% is the proven RTP; the rakeback is operator-side
- Manual cash-out — every captured bet used an auto cash-out target
- Cross-account sampling
- Duel's server code and seed generation — outcomes are verified from the captured rounds, their commitments and the public drand beacon
- Infrastructure or server security
- Wallet, payments, or operational systems outside game logic
What Audit Covers

| Area | Description |
|---|---|
| Commit-Reveal System | Per-round SHA-256 commitment opened on every round; one fresh seed per round; reveal after the crash |
| External Entropy | drand quicknet beacon (chain 52db9ba7…4e971, 3-second period) — every signature bound to a pinned api.drand.sh record |
| Bet Timing | Bet accepted before its beacon published: Duel's transactions-API timestamp against the chain formula |
| RNG Analysis | Our own implementation written from the specification; Duel's Verify-tab code run unmodified as a cross-check; 5M-round simulation |
| Live Parity | Every recorded crash point recomputed, and both ProvablyFair.org verifiers executed on all 1,100 rounds |
| RTP & Payouts | Anti-circularity count, RTP claim rule over 9,999,900 targets, win rule, recorded payout field and wallet-ledger sample |
| Fairness Integrity | Standard integrity matrix — 16 tests across seed integrity, commitment timing, determinism, isolation, payout and distribution |
| Reproducibility | npm test re-runs every step offline; runs write to outputs/run/ and are compared with the committed results |
What Audit Guarantees

- Every crash point is reproducible from
(serverSeed, drandRandomness)— verified on all 1,100 rounds - Every revealed seed matches the commitment its round carried, and no seed was reused
- All 1,100 drand signatures equal the public quicknet records for their rounds
- The theoretical RTP is at most 99.9% at every cash-out target; with Duel's stated 9,999.999× cap applied, it is at least 99.899768% at every target
- The published 99.9% RTP figure is not overstated at any target (RTP-CLAIM 1.2.0, ±0.1 pp)
- The crash point does not depend on the stake — 100 / 100 rounds at $10 recompute exactly
- Pass 2 finds no sign of seed or beacon selection across the casino's 1,100 seeds, within its stated power
- 14 of 16 fairness integrity tests pass; 1 N/A (replay protection — single-step game); 1 FLAG (server-side input validation gap on auto_cashout_multiplier — disclosed to Duel.com, does not affect fairness)
References
Crash — Game Rules6 sections▶

Crash is a live multiplayer multiplier game. Each round has one crash point, shared by every player in it, computed from a server seed and a drand public randomness beacon. A multiplier rises from 1.00× until it crashes. A bet set to cash out at a target wins if the crash point reaches that target.
How to Play
1. Save the commitment — Before you bet, note the round's server seed hash (the commitment) and the time you saved it.
2. Place your bet — Enter a stake and an auto cash-out target (e.g. 1.5×, 2×, 10×).
3. The round runs — The multiplier rises from 1.00× until it reaches the crash point.
4. Outcome — If the crash point reaches your target, the bet cashes out and the wallet is credited stake × target. Otherwise the stake is lost.
5. Verify — After the crash, take the revealed server seed, the drand round and its signature, and reproduce the crash point yourself.
Win Conditions
A bet wins if and only if the crash point is at or above its cash-out target. A crash point exactly equal to the target is a win.
| Outcome | Condition | Example (stake $1, target 2×) |
|---|---|---|
| Win | Crash point ≥ target | Crash point 3.56× → credited $2.00 (stake × target) |
| Tie (win) | Crash point = target | Crash point 2.00× → credited $2.00 |
| Loss | Crash point < target | Crash point 1.99× → $0 |
| Instant crash (loss) | Crash point = 1.00× | Every bet with a target above 1.00× loses; about 1 round in 92 (1.0891%) |
amountWon field reads stake × target × 0.999; the wallet ledger credits the full stake × target on the wins looked up.Risk vs Reward
The cash-out target sets the risk. Higher targets win less often and pay more; lower targets win often and pay little.
- Low targets win often — the crash point reaches 1.5× about 66.6% of the time
- High targets pay rarely — about 10% of rounds reach 10× and about 1% reach 100×
- The edge is flat — the theoretical RTP is at most 99.9% at every target, and at least 99.899768% with Duel's stated 9,999.999× cap applied
- Short sessions swing — a few hundred rounds can return far above or below 99.9% (S4)
Parameters
| Parameter | Value | Notes |
|---|---|---|
| Minimum crash point | 1.00× | The formula is clamped at 1.00 |
| Maximum crash point | 4,290,672,328.70× | The map's own maximum, at uint32 value 0; no cap on the crash point |
| Cash-out cap | 9,999.999× | Duel's statement: every bet cashes out at 9,999.999× at most |
| Cash-out targets captured | 1.1×, 1.5×, 2×, 5×, 10× | Targets are on the 0.01 grid |
| House edge | 0.1% flat | The 0.999 factor in the crash-point formula |
| Theoretical RTP | At most 99.9% | Counted exactly from the algorithm at every 0.01 target to 100,000× |
| RNG | HMAC-SHA256 | Key: server seed bytes; message: drand signature (UTF-8, lossy) + :0 |
| External entropy | drand quicknet | 3-second period; chain 52db9ba7…4e971 |
| Round structure | Multiplayer | One crash point per round, shared by every player |
Seed Formats
Every Crash round uses two inputs: a server seed committed by the operator, and the drand quicknet beacon's signature for the round. There is no client seed and the nonce is always 0.
| Input | Format | Example (round 829099) | Purpose |
|---|---|---|---|
| Server Seed | 64 hex characters (32 bytes) | 3c9c71aa9ffa2691…8fab1d23 | Operator randomness, revealed after the crash |
| Server Seed Hashed | 64 hex characters (SHA-256) | 706bb90b571c6165…f4e151c0 | The commitment: SHA-256 of the 32 decoded seed bytes |
| Drand Round ID | Integer | 27798178 | The quicknet beacon round the game round uses |
| Drand Randomness | 96 hex characters (48-byte BLS signature) | b18fa6dc92304844…1767fd56d | The quicknet signature for that round |
:0 is the HMAC message. All 1,100 rounds recompute with this exact encoding.Multiplier Formula & Payout
Crash has no multiplier table: the crash point comes from one formula, and a win pays the cash-out target.
value      = first 4 bytes of HMAC-SHA256(serverSeed bytes, drand text + ":0"), big-endian uint32
cents      = floor(999 × 2³² / (10 × (value + 1)))        exact integer arithmetic
crashPoint = max(1.00, cents / 100)

Win  (crashPoint ≥ target): credit = stake × target
Loss (crashPoint < target): credit = 0| Target | P(crash ≥ target) | Credit on win (per $1) | Theoretical RTP |
|---|---|---|---|
| 1.5× | 66.6000% | $1.50 | 99.9000% |
| 2× | 49.9500% | $2.00 | 99.9000% |
| 5× | 19.9800% | $5.00 | 99.9000% |
| 10× | 9.9900% | $10.00 | 99.9000% |
| 50× | 1.9980% | $50.00 | 99.9000% |
P(crash ≥ x) × x is at most 0.999 at every target: the 0.999 factor is the house edge, and the floor in the uint32 count can only lower the return, by less than x / 2³².Why Provably Fair Matters▶

Traditional online casinos require players to trust that games are fair. Provably fair systems let players check outcomes for themselves. In a provably fair system:
- The casino commits to the inputs that determine a result before the player bets
- A source of randomness exists that the casino cannot predict or control
- Anyone can verify the outcome after the fact
High-Level Overview7 sections▶

Checklist Reference
The ProvablyFair.org Framework 1.1 checks covered by this audit, grouped by area.
Commitments & Seeds
| Test | Description |
|---|---|
| Seed reveal matches commitment | SHA-256(hex_decode(serverSeed)) = serverSeedHash on 1,100 / 1,100 rounds (Step 1) |
| One commitment per round | 1,100 distinct seeds and 1,100 distinct commitments (Step 4) |
| Sequence key ordered | Nonce constant 0; drand round strictly increasing over 1,099 transitions (Step 3) |
| Client seed | Not applicable — Crash is multiplayer and carries no client seed |
Beacon & Timing
| Test | Description |
|---|---|
| Beacon authenticity | Every signature equals its pinned api.drand.sh record (Step 15) |
| Publication time | Every publication time equals the quicknet chain formula (Step 11) |
| Bet before beacon | 1,100 / 1,100 bets accepted before their beacon published, on Duel's clock (Step 2) |
| Commitment before beacon | Order taken from the game's design — the capture recorded no receipt time for the commitment |
RNG & Parity
| Test | Description |
|---|---|
| Own implementation | src/rng.ts written from the specification docs/ALGORITHM.md |
| Live parity | 1,100 / 1,100 recorded crash points reproduced by exact equality (Step 5) |
| Player verifiers | Docs-site verifier and main-site verifier bundle agree on 1,100 / 1,100 (Step 5) |
| Operator cross-check | Duel's Verify-tab code, run unmodified, agrees on 1,100 / 1,100 displayed crash points |
RTP & Payouts
| Test | Description |
|---|---|
| Anti-circularity | Counts from a separate per-value model at 11 targets; RTP ≤ 99.9% (Step 12) |
| RTP claim rule | Flat 99.9% claim within ±0.1 pp at all 9,999,900 targets — PASS (Step 16) |
| Win rule & recorded payout | Win flags 1,100 / 1,100; amountWon 671 / 671 (Step 7) |
| Simulation | 5M rounds, Fisher's p = 0.5382 (Step 13); casino-seed screen z 0.286 / 0.160 (Step 14) |
High-Level Flow
A single Crash round, from commitment to verification:
1. Commitment — The server sends the round's server seed hash
2. Bet — The player bets with an auto cash-out target
3. Beacon — The drand quicknet chain publishes the beacon for the round's drand round
4. Crash point — HMAC-SHA256(seed bytes, drand text + ":0") → first 4 bytes as uint32 → floor(999 × 2³² / (10 × (v + 1))) cents, at least 1.00×
5. Settlement — A bet wins when the crash point is at or above its target; the wins looked up in the wallet ledger were credited stake × target
6. Reveal — After the crash, the server reveals the seed; the round's Provably Fair panel shows the seed, the drand round and its signature
7. Verify — Anyone can recompute the crash point and check the seed against the saved hash
Provably Fair Model
Crash combines a per-round server seed commitment with a public randomness beacon. The operator commits to the seed with a SHA-256 hash; the drand quicknet network publishes a BLS threshold signature on a fixed 3-second schedule; HMAC-SHA256 of the two gives the crash point. The protection rests on the commitment being fixed before the beacon publishes.
Commit-Reveal Model
The commit-reveal sequence for a Crash round:
Commit:
The server sends the round's serverSeedHash (captured from the crash_hashed_pf event). Only the hash is visible; the seed stays hidden.
Bet:
The player bets with a cash-out target. Every captured bet was accepted before its beacon published, on Duel's transaction clock.
Beacon:
The drand quicknet chain publishes the signature for the round's drand round. Its publication time follows the public chain formula.
Reveal:
After the crash the server reveals the seed (captured from the pending_drand event, which also names the drand round and carries its signature). Anyone can check SHA-256(hex_decode(serverSeed)) = serverSeedHash and recompute the crash point. The next round uses a fresh seed.
Why Crash Uses a Public Randomness Beacon
Client-seed games let each player supply an input the casino cannot predict. Crash is multiplayer: one crash point is shared by every player in the round, so no single player's seed can drive it. Crash uses the drand quicknet beacon instead:
- drand signatures come from a threshold of independent League of Entropy operators — no single party can forge or withhold one
- Each beacon publishes on a fixed public schedule, so anyone can compute when it appeared
- Anyone can fetch the signature from api.drand.sh and compare it with the value the round used
- Provided the commitment is fixed before the beacon publishes, the operator cannot choose a seed to suit the beacon
Why There's No Nonce or Epoch Chain
Client-seed games reuse one server seed for many bets and count them with a nonce. Crash gives every round a new server seed instead, so there is nothing to count:
- Each round has exactly one server seed — no reuse, no chain, no cursor
- The nonce is the constant
0in the HMAC message - The seed is revealed after every round, not after a rotation
- The 1,100 captured rounds carry 1,100 distinct seeds and 1,100 distinct commitments (Step 4)
Round N: serverSeed_N (new), drandRoundId_N → crashPoint_N [seed revealed after the crash] Round N+1: serverSeed_(N+1) (new), drandRoundId_(N+1) → crashPoint_(N+1) [seed revealed after the crash] Every HMAC message ends in the fixed suffix ":0".Determinism Guarantee
Given identical inputs, the output is always identical:
HMAC-SHA256(hex_decode(serverSeed), utf8(drand) + ":0") → same digestFirst 4 bytes as a big-endian uint32 → same value vfloor(999 × 2³² / (10 × (v + 1))) → same centsmax(1.00, cents / 100) → same crash pointcrashPoint ≥ target → same win or lossstake × target → same creditTechnical Glossary6 categories▶

Core Concepts
| Term | Definition |
|---|---|
| Provably Fair | A model in which the inputs to every outcome are committed before the outcome is known, and any player can verify the outcome afterwards without trusting the operator. |
| Commit-Reveal Protocol | One party publishes the hash of a secret before any dependent action and reveals the secret afterwards. In Crash, the round's server seed hash is the commitment and the seed is revealed after the crash. |
| External Entropy Source | Randomness outside the operator's control that enters the outcome. Crash uses the drand quicknet beacon. |
| Determinism | Identical inputs always produce identical outputs: one (serverSeed, drandRandomness) pair gives exactly one crash point. |
Seed System
| Term | Definition |
|---|---|
| Server Seed | 64 hex characters (32 bytes) chosen by the operator, hex-decoded for the HMAC key. Each round uses a new one. |
| Server Seed Hash | SHA-256 of the 32 decoded seed bytes — the round's commitment. A revealed seed matching it shows the seed is the committed one; your saved copy shows when you saw it. |
| drand Round ID | The number of a beacon in the drand quicknet chain. Its publication time is 1692803367 + (round − 1) × 3 seconds. |
| drand Randomness | The 96-hex-character (48-byte) BLS signature the quicknet chain publishes for a round — the API's signature field. |
| Single-Use Seed Model | Every round gets a fresh server seed; the nonce is the constant 0 in the HMAC message. |
Cryptographic Functions
| Term | Definition |
|---|---|
| HMAC-SHA256 | Keyed hash of the drand text plus :0 under the server seed bytes; its first 4 bytes give the uint32 value. |
| SHA-256 | The commitment hash: SHA-256(hex_decode(serverSeed)) = serverSeedHash is checked on every round. |
| BLS Threshold Signature | A signature that needs a threshold of independent signers; each drand beacon is one. |
| Lossy UTF-8 Decoding | The drand bytes are read as UTF-8 text and each invalid byte sequence (usually a single byte) becomes one U+FFFD. It is deterministic, so server and verifier build the same message. |
| uint32 Threshold Mapping | The uint32 value v maps to max(1.00, floor(999 × 2³² / (10 × (v + 1))) / 100). The map is monotone in v: every v gives exactly one crash point. |
Verification Terms
| Term | Definition |
|---|---|
| Verifier | An implementation of the RNG and payout rules used to recompute outcomes from captured inputs. Ours is written from the specification, not from the operator's code. |
| Parity | Our computed crash point equals the recorded one. 1,100 / 1,100 parity means zero mismatches. |
| Anti-Circularity | Deriving the RTP from the algorithm alone. For Crash, the uint32 values reaching each target are counted from a separate per-value model — no casino data is used. |
| Survival Probability | P(crash ≥ x) = floor(999 × 2³² / (10k)) / 2³² for a target x = k/100; roughly 0.999 / x. |
Game Mechanics
| Term | Definition |
|---|---|
| Crash Point | The multiplier at which a round ends; shared by every player. From 1.00× up to the map maximum of 4,290,672,328.70×. |
| Auto Cash-Out | The target at which a bet settles. If the crash point reaches it, the wallet is credited stake × target; otherwise the bet loses. |
| Instant Crash | A round at exactly 1.00×. Probability 1.0891% (46,776,872 of 2³² values). |
| Shared Round | One (serverSeed, drand beacon) pair per round, used for every player's bet in it. |
| Multi-Stream Chi-Squared | Pass 1 runs 10 independent 500,000-round streams and combines their p-values with Fisher's method, so no single stream's tail-bin variance decides the result. |
Framework 1.1
| Term | Definition |
|---|---|
| Framework 1.1 | The ProvablyFair.org audit framework version this release is certified under. It brings the RTP claim rule (RTP-CLAIM 1.2.0, exit 5), the approved Crash profile 1.0.3 and the stated S5 level. |
| RTP Claim Rule | RTP-CLAIM 1.2.0 holds every setting a player can choose to the RTP figure the casino publishes, within ±0.1 percentage point. A house-side miss ends the run RTP FIGURE OVERSTATED (exit 5); the draws themselves are scored separately. |
| Capture Flag | A gap that comes from our capture script rather than the casino. It is shown in neutral styling, explained in plain words and never counted against the operator. This audit has none on its scored steps. |
| Base Stake Tier | The stake level at the casino's base house edge, before any stake-scaled edge applies. Certification covers this tier only; both captured Crash stakes ran at the base 0.1% edge. |
Commit-Reveal & Bet Timing
Can the casino change your outcome after you bet?
Every Crash round on Duel.com comes from two inputs: a server seed committed by the operator and a drand beacon from the public quicknet chain. In this scheme the operator sends the seed's SHA-256 hash before the round and reveals the seed after the crash, so a revealed seed that matches its hash is the committed one. This section checks every commitment, the order of the beacons, and that every bet was accepted before its beacon published.

Per-Round Commitments & Beacon Timing
What we verified
- Every revealed server seed hashes to its round's commitment:
SHA-256(hex_decode(serverSeed)) = serverSeedHashon 1,100 / 1,100 rounds - 1,100 distinct seeds and 1,100 distinct commitments — one fresh seed per round, never reused
- The nonce is the constant 0; the sequence key is the drand round, strictly increasing over all 1,099 transitions
- Every bet was accepted before its beacon published, on Duel's transaction clock: min 0.404 s, median 12.251 s, max 13.779 s
- Every beacon's publication time equals the quicknet chain formula — 1,100 / 1,100
- No client seed: Crash is multiplayer, and all 1,100 rounds recompute from the seed and the beacon alone
What this means for you
- The seed revealed after the crash is the one behind the hash you were shown
- Save the hash before you bet: a match shows consistency, your saved copy shows timing
- No seed carries over between rounds — each round starts fresh
- The outside randomness is a public beacon anyone can fetch and check


- Every revealed server seed hashes to its round's commitment:
SHA-256(hex_decode(serverSeed)) = serverSeedHashon 1,100 / 1,100 rounds - 1,100 distinct seeds and 1,100 distinct commitments — one fresh seed per round, never reused
- The nonce is the constant 0; the sequence key is the drand round, strictly increasing over all 1,099 transitions
- Every bet was accepted before its beacon published, on Duel's transaction clock: min 0.404 s, median 12.251 s, max 13.779 s
- Every beacon's publication time equals the quicknet chain formula — 1,100 / 1,100
- No client seed: Crash is multiplayer, and all 1,100 rounds recompute from the seed and the beacon alone
- The seed revealed after the crash is the one behind the hash you were shown
- Save the hash before you bet: a match shows consistency, your saved copy shows timing
- No seed carries over between rounds — each round starts fresh
- The outside randomness is a public beacon anyone can fetch and check
Seed hash integrity (Step 1)Pass
SHA-256(hex_decode(serverSeed)) = serverSeedHash; 0 left unopenedServer seed uniqueness (Step 4)Pass
Nonce & sequence (Step 3)Pass
Bet before beacon (Step 2)Pass
Beacon publication time (Step 11)Pass
Commitment before beaconInfo
Client-seed influenceN/A
:0All 1,100 revealed seeds open their own round's commitment and no seed repeats, so the revealed seeds are the committed ones. Every bet was accepted before its beacon published, on Duel's own transaction timestamps, and every beacon published on the chain's schedule.
| Check | Result | Evidence |
|---|---|---|
| Seed hash integrity (Step 1) | Pass | 1,100 / 1,100 commitments opened: SHA-256(hex_decode(serverSeed)) = serverSeedHash; 0 left unopened |
| Server seed uniqueness (Step 4) | Pass | 1,100 distinct seeds and 1,100 distinct commitments, checked against the declared population |
| Nonce & sequence (Step 3) | Pass | Nonce constant 0; drand round strictly increasing on 1,099 / 1,099 transitions — no beacon reused or taken out of order |
| Bet before beacon (Step 2) | Pass | 1,100 / 1,100 bets accepted before their beacon published (min 0.404 s, mean 12.196 s, max 13.779 s), on Duel's transactions-API timestamps |
| Beacon publication time (Step 11) | Pass | 1,100 / 1,100 equal genesis + (round − 1) × 3 s on the quicknet chain |
| Commitment before beacon | Info | The capture kept no receipt time for the seed hash or the drand round, so the order is taken from the game's design; the cherry-pick screen finds no sign of seeds chosen to suit their beacons (Step 14) |
| Client-seed influence | N/A | No client seed: the HMAC message is the drand text plus :0 |
Seed hash integrity (Step 1)Pass
SHA-256(hex_decode(serverSeed)) = serverSeedHash; 0 left unopenedServer seed uniqueness (Step 4)Pass
Nonce & sequence (Step 3)Pass
Bet before beacon (Step 2)Pass
Beacon publication time (Step 11)Pass
Commitment before beaconInfo
Client-seed influenceN/A
:0All 1,100 revealed seeds open their own round's commitment and no seed repeats, so the revealed seeds are the committed ones. Every bet was accepted before its beacon published, on Duel's own transaction timestamps, and every beacon published on the chain's schedule.
How It Works — Commitments & Beacon Timing6 sections
1.1Server Seed Commitment
Each round has its own server seed: 64 hex characters (32 bytes), chosen by the operator. The commitment is SHA-256(hex_decode(serverSeed)) — the hash of the 32 decoded bytes, not of the 64-character text. In this scheme the server sends the hash before the round and reveals the seed after the crash. A revealed seed that matches the hash is the committed seed; the match shows consistency, not when the hash was sent (1.3).
/** Commitment check: SHA-256 over the hex-decoded seed bytes, not the ASCII text (§1.2). */export function verifyHash(serverSeed: string, serverSeedHash: string): boolean { const h = createHash("sha256").update(hexDecode(serverSeed)).digest("hex"); return h === serverSeedHash.toLowerCase();}Real Example from Live Data:
{ "roundId": 829099, "serverSeed": "3c9c71aa9ffa2691d29fd754cb0caf8ce1fa87d57804196967de81088fab1d23", "serverSeedHash": "706bb90b571c6165c96a484580efd2f834b4f3237e7cf0f2680b26b7f4e151c0", "drandRoundId": 27798178, "drandRandomness": "b18fa6dc92304844fc4e868d708953e6b628b3f88d4381249d32264df1bfe5bc20aa0905e57fe54063010881767fd56d", "crashPoint": 2.81}Verification:
const crypto = require('crypto'); const serverSeed = '3c9c71aa9ffa2691d29fd754cb0caf8ce1fa87d57804196967de81088fab1d23'; const serverSeedHash = crypto .createHash('sha256') .update(Buffer.from(serverSeed, 'hex')) // the 32 decoded bytes .digest('hex'); console.log(serverSeedHash);// Output: 706bb90b571c6165c96a484580efd2f834b4f3237e7cf0f2680b26b7f4e151c0 ✅1.2drand Bet Timing (Step 2)
For every round, Step 2 measures the gap between the bet and its beacon: drandPublishedAt × 1000 − betPlacedAt, in milliseconds. betPlacedAt is Duel's own timestamp_raw from the transactions API, matched by round ID. drandPublishedAt comes from the public quicknet formula, 1692803367 + (drandRoundId − 1) × 3. Anyone can recompute both. The step times the bet, on the operator's clock; when the hash was shown is covered in 1.3.
for (const r of rounds) { if (r.timing.source === EXPECTED_TIMING_SOURCE) serverTimestamped++; // … const cbd = r.timing.drandPublishedAt * 1000 - r.timing.betPlacedAt; // milliseconds // … if (cbd > 0) { positive++; // … } else { nonPositive++; // … }}Real Example — round 829099 timestamps:
{ "drandPublishedAt": 1776197898, "drandPublishedAtISO": "2026-04-14T20:18:18.000Z", "commitmentBeforeDrand": 12828, "betPlacedAt": 1776197885172, "betPlacedAtISO": "2026-04-14T20:18:05.000000Z", "source": "transactions-api"}Verification:
// betPlacedAt — Duel's transactions-API timestamp_raw (operator clock)// drandPublishedAt — public quicknet formula: genesis + (drandRoundId - 1) × 3const QUICKNET_GENESIS = 1692803367; // 2023-08-23T15:09:27Zconst QUICKNET_PERIOD = 3; // seconds const drandPublishedAt = QUICKNET_GENESIS + (27798178 - 1) * QUICKNET_PERIOD;// → 1776197898 (2026-04-14T20:18:18.000Z) ✅ const margin_ms = drandPublishedAt * 1000 - 1776197885172;// → 12828 ms — the bet came 12.828 s before the beacon published ✅1.3What the Capture Records
The capture read each round's commitment from the crash_hashed_pf socket event and its drand round from pending_drand, without storing when either arrived. So the audit shows that every bet came before its beacon, but not that every commitment did. That each commitment and each drand round were fixed before the beacon published is a premise of this audit. Step 14's rank statistic is the statistical check on beacon selection (S4).
1.4Single-Use Seeds (Step 4)
Crash has no seed rotation and no nonce cursor. Every round gets a new server seed, committed by its SHA-256 hash and revealed after the crash. Step 4 counts distinct seeds and distinct commitments against the population declared in src/loader.ts, so a shortened dataset cannot pass by agreeing with itself.
const seeds = new Set(rounds.map(r => r.result.serverSeed));const hashes = new Set(rounds.map(r => r.result.serverSeedHash));const issues: string[] = [];if (seeds.size !== rounds.length) issues.push(`${rounds.length - seeds.size} rounds reuse a server seed`);if (hashes.size !== rounds.length) issues.push(`${rounds.length - hashes.size} rounds reuse a commitment hash`);if (seeds.size !== EXPECTED_DISTINCT_SEEDS) issues.push(`distinct seeds ${seeds.size} != ${EXPECTED_DISTINCT_SEEDS}`);if (hashes.size !== EXPECTED_DISTINCT_SEEDS) issues.push(`distinct hashes ${hashes.size} != ${EXPECTED_DISTINCT_SEEDS}`);1.5Nonce & Beacon Sequence (Step 3)
The nonce is the constant 0: every HMAC message ends in :0, and all 1,100 rounds recompute with it. Order is carried by the drand round instead. Step 3 checks that it rises strictly from one captured round to the next, so no beacon was reused or taken out of order. Beacon selection is tested statistically by Step 14 (premise in 1.3).
for (let i = 1; i < rounds.length; i++) { compared++; if (rounds[i].result.drandRoundId <= rounds[i - 1].result.drandRoundId) { violations.push(`round ${rounds[i].roundId}: drand ${rounds[i].result.drandRoundId} does not exceed the previous ${rounds[i - 1].result.drandRoundId}`); }}1.6Client Seed & Determinism
Crash is multiplayer: every player in a round shares one crash point, so there is no per-player client seed. The HMAC message is the drand text plus :0, the dataset carries no client-seed field, and all 1,100 rounds recompute without one. The drand beacon is the input the operator does not choose. The same (serverSeed, drandRandomness) pair always gives the same crash point, so any player with the revealed values derives the round exactly.
Technical Evidence & Verification5 sections

1.7Evidence Coverage Summary6 checks

| Verification Area | Coverage | Result |
|---|---|---|
| Seed hash integrity (Step 1) | 1,100 / 1,100 commitments opened | Pass |
| drand bet timing (Step 2) | 1,100 / 1,100 bets before their beacon (min 0.404 s) | Pass |
| drand round monotonicity (Step 3) | 1,099 / 1,099 transitions strictly increasing | Pass |
| Server seed uniqueness (Step 4) | 1,100 distinct seeds and commitments | Pass |
| drand chain formula (Step 11) | 1,100 / 1,100 publication times | Pass |
| Commitment before beacon | No receipt time in the capture; order taken from the game's design | Info |
1.8Code References7 source files

| File | Purpose |
|---|---|
| tests/verify.ts | 18-step orchestrator and reproduction gate (Steps 1–4 and 11 cover S1) |
| tests/steps/commitment.ts | Steps 1–4: seed hash, bet timing, drand monotonicity, seed uniqueness |
| tests/steps/dataset.ts | Steps 10–12: dataset hash, chain formula, anti-circularity |
| src/rng.ts | Commitment check (verifyHash) and crash-point derivation |
| src/loader.ts | Dataset pin and the population of record |
| src/verify-drand-timing.js | npm run timing: chain formula, margins and signature re-fetch (network) |
| capture/crash-capture.reference.js | Round-capture code (reference record) |

1.9Datasets UsedSource artifacts


| Property | Value |
|---|---|
| Source | Live Crash rounds from Duel.com, one test account |
| Total records | 1,100 rounds (Phase A: 800, Phase B: 200, Phase C: 100) |
| Round IDs | 829099 → 831399 (1,095 consecutive steps, 4 capture gaps) |
| drand rounds | 27,798,178 → 27,819,827 (quicknet) |
| Capture window | 2026-04-14T20:17:12.676Z → 2026-04-15T14:21:25.365Z |
| SHA-256 | ea62337a8665842ad33341a7d1b435d0c986f9feb3b03609cb0b0c868f3ef58a |
Fields used: roundId, phase, request.amount, request.auto_cashout, result.crashPoint, result.serverSeed, result.serverSeedHash, result.drandRoundId, result.drandRandomness, result.amountWon, result.effectiveEdge, result.isWin, timing.betPlacedAt, timing.drandPublishedAt, timing.commitmentBeforeDrand, timing.source
1.10Verified Invariants7 invariants

| Invariant | Result |
|---|---|
SHA-256(hex_decode(serverSeed)) = serverSeedHash for all 1,100 rounds | Pass |
| 1,100 distinct seeds and 1,100 distinct commitments | Pass |
drandPublishedAt × 1000 − betPlacedAt > 0 for all 1,100 rounds | Pass |
timing.source = "transactions-api" on 1,100 / 1,100 rounds | Pass |
drandPublishedAt = genesis + (drandRoundId − 1) × 3 for all 1,100 rounds | Pass |
| drand round IDs strictly increasing over 1,099 transitions | Pass |
Every HMAC message ends in the constant nonce :0 | Pass |
1.11Reproduction InstructionsRun locally

Clone the release, install the pinned dependencies, and run the verifier:
git clone https://github.com/ProvablyFair-org/duel-crash.gitcd duel-crash && git checkout v1.2.1 && npm cinpm run verify# S1 steps: 1, 2, 3, 4 and 11Console lines for this section's steps, as run:
✓ Step 1: Seed Hash Integrity
✓ Step 2: drand Bet Timing (Bet Before Beacon)
✓ Step 3: drand Round Monotonicity
✓ Step 4: Server Seed Uniqueness
✓ Step 11: drand Chain FormulaRNG & Entropy Model
Is the randomness genuinely random, or could it be rigged?
Our RNG, src/rng.ts, is written from a specification and reproduces every captured crash point from two inputs: the server seed and the drand signature. Duel's own Verify-tab code, run unmodified, is a cross-check only. This section covers the derivation, the entropy sources, the drand records, the map from uint32 to crash point, and 5 million simulated rounds.
Our Own RNG, Written From the Specification
What we verified
- Our RNG,
src/rng.ts, is written from a specification by an implementer who never opened Duel's code - Only the server seed and the drand signature enter the crash point — all 1,100 rounds recompute from those two alone
- All 1,100 drand signatures equal the pinned api.drand.sh records for their rounds
- Duel's own Verify-tab code, run unmodified as a cross-check, gives the same displayed crash point on 1,100 / 1,100
- 5M simulated rounds are consistent with the survival law: Fisher's combined p = 0.5382, 0 / 10 streams below α = 0.01
- No sign of serial dependence: lag-1 z = −0.029 and runs p = 0.0436 over 5M rounds
What this means for you
- No crash point is more or less likely than the formula says, to within one uint32 value
- The outside randomness comes from a public, signed source the casino cannot forge
- No hidden inputs: what you can see is all that goes in
- Past rounds say nothing about the next one
- Our RNG,
src/rng.ts, is written from a specification by an implementer who never opened Duel's code - Only the server seed and the drand signature enter the crash point — all 1,100 rounds recompute from those two alone
- All 1,100 drand signatures equal the pinned api.drand.sh records for their rounds
- Duel's own Verify-tab code, run unmodified as a cross-check, gives the same displayed crash point on 1,100 / 1,100
- 5M simulated rounds are consistent with the survival law: Fisher's combined p = 0.5382, 0 / 10 streams below α = 0.01
- No sign of serial dependence: lag-1 z = −0.029 and runs p = 0.0436 over 5M rounds
- No crash point is more or less likely than the formula says, to within one uint32 value
- The outside randomness comes from a public, signed source the casino cannot forge
- No hidden inputs: what you can see is all that goes in
- Past rounds say nothing about the next one
RNG written from the specPass
src/rng.ts written from docs/ALGORITHM.md; reproduces 1,100 / 1,100 recorded crash pointsDisclosed inputs onlyPass
HMAC-SHA256(hex_decode(serverSeed), utf8(drand) + ":0") — all 1,100 rounds recompute from the two inputsOperator code cross-checkPass
drand authenticity (Step 15)Pass
Mapping bias (Steps 12, 16)Pass
Simulation Pass 1 (Step 13)Pass
Live-sample fit (Step 18)Pass
The crash point depends only on the server seed and the drand signature, and our own implementation, written from the specification, reproduces every round. Every beacon equals the public quicknet record. The map from uint32 to crash point carries no bias beyond one uint32 value at any target, and 5 million simulated rounds are consistent with the survival law.
| Check | Result | Evidence |
|---|---|---|
| RNG written from the spec | Pass | src/rng.ts written from docs/ALGORITHM.md; reproduces 1,100 / 1,100 recorded crash points |
| Disclosed inputs only | Pass | HMAC-SHA256(hex_decode(serverSeed), utf8(drand) + ":0") — all 1,100 rounds recompute from the two inputs |
| Operator code cross-check | Pass | Duel's Verify-tab code, run unmodified: displayed crash point equal on 1,100 / 1,100 |
| drand authenticity (Step 15) | Pass | 1,100 / 1,100 signatures bound to one pinned api.drand.sh record each; chain quicknet |
| Mapping bias (Steps 12, 16) | Pass | The map is monotone in one uint32; survival within 2⁻³² of 0.999 / x at all 9,999,900 targets to 100,000× |
| Simulation Pass 1 (Step 13) | Pass | 5M rounds replayed from their seeds; Fisher's p = 0.5382; lag-1 z −0.029; runs p 0.0436 |
| Live-sample fit (Step 18) | Pass | Informational: the 1,100 live uint32 values fit uniform on 20 bins (χ² p = 0.828); lag-1 z −0.75; runs p 0.469 |
RNG written from the specPass
src/rng.ts written from docs/ALGORITHM.md; reproduces 1,100 / 1,100 recorded crash pointsDisclosed inputs onlyPass
HMAC-SHA256(hex_decode(serverSeed), utf8(drand) + ":0") — all 1,100 rounds recompute from the two inputsOperator code cross-checkPass
drand authenticity (Step 15)Pass
Mapping bias (Steps 12, 16)Pass
Simulation Pass 1 (Step 13)Pass
Live-sample fit (Step 18)Pass
The crash point depends only on the server seed and the drand signature, and our own implementation, written from the specification, reproduces every round. Every beacon equals the public quicknet record. The map from uint32 to crash point carries no bias beyond one uint32 value at any target, and 5 million simulated rounds are consistent with the survival law.
How It Works — RNG & Entropy Model8 sections
2.1RNG Implementation
Each round's crash point comes from one HMAC-SHA256. The 32 hex-decoded seed bytes are the key. The drand signature is hex-decoded to 48 bytes and read as UTF-8 text, with each invalid byte sequence (usually a single byte) replaced by one U+FFFD; that text plus :0 is the message. The first 4 bytes of the digest, big-endian, are the uint32 u. The crash point is floor(999 × 2³² / (10 × (u + 1))) cents, at least 1.00, in exact integer arithmetic.
Our src/rng.ts implements this from the specification docs/ALGORITHM.md, which was written from Duel's public pages, the standard construction, the 1,100 live rounds and black-box readings of Duel's Verify page. Its implementer never opened Duel's code.
| Component | Detail |
|---|---|
| Hash function | HMAC-SHA256 |
| Key | hex_decode(serverSeed) — 32 bytes |
| Message | utf8(lossy_utf8(hex_decode(drand))) followed by :0 |
| Extraction | First 4 digest bytes, big-endian uint32 u |
| Mapping | floor(999 × 2³² / (10 × (u + 1))) cents, exact |
| Clamp | At least 1.00× |
| Output | One crash point per round, shared by every player |
// §2 Step 2: message = UTF-8(lossy-decode(drand bytes)) followed by the ASCII bytes ":0".function buildMessage(drandSeed: string): Buffer { const drandBytes = hexDecode(drandSeed); const text = lossyUtf8.decode(drandBytes); return Buffer.concat([Buffer.from(text, "utf8"), Buffer.from(":0", "ascii")]);} // §2 Steps 3 and 4: HMAC-SHA256 keyed by the server seed bytes, then the first four digest// bytes as an unsigned big-endian integer. No cursor, no rejection loop.function drawU(key: Buffer, drandSeed: string): number { const digest = createHmac("sha256", key).update(buildMessage(drandSeed)).digest(); return digest.readUInt32BE(0);} // §2 Step 5 in exact integer arithmetic: cents = floor(999 × 2^32 / (10 × (u + 1))).// BigInt division truncates, which equals floor for these positive operands.function centsFromU(u: number): bigint { return NUM / (10n * BigInt(u + 1));} // §2 Step 5, clamp: the displayed value is never below 1.00.function displayedFromU(u: number): number { return Math.max(1, Number(centsFromU(u)) / 100);}src/rng.ts as a unit test.2.2Entropy Sources
Two inputs and a constant enter the HMAC. The server seed is the operator's. The drand signature comes from the League of Entropy's quicknet network: a BLS threshold signature the operator can neither predict nor forge. Crash takes no player input.
| Source | Controlled By | Purpose |
|---|---|---|
| Server seed | Casino | Operator randomness, committed by its SHA-256 hash |
| drand signature | drand quicknet network | Outside randomness — BLS threshold signature (chain 52db9ba7…4e971) |
| Nonce suffix | Fixed | Always :0 — each seed is used once |
(serverSeed, drandRandomness) always gives the same crash point. 1,100 / 1,100.How we know: all 1,100 rounds recompute from these inputs alone. A hidden input that moved a crash point would break that round's recomputation; none broke.
2.3drand Chain Authenticity (Step 15)
Are the drand values real? Each round's signature is compared with the public api.drand.sh record for its drand round. The records were fetched once and pinned in outputs/drand-api-verification.json. Step 15 binds every round to exactly one record and recompares the signatures on every run, offline; npm run timing re-fetches all 1,100 from api.drand.sh.
const DRAND_CHAIN_HASH = '52db9ba70e0cc0f6eaf7803dd07447a1f5477735fd3f661792ba94600c84e971';const DRAND_API_BASE = `https://api.drand.sh/${DRAND_CHAIN_HASH}/public`; async function fetchDrandRound(round) { const resp = await fetch(`${DRAND_API_BASE}/${round}`); if (!resp.ok) throw new Error(`drand API ${resp.status} for round ${round}`); return resp.json();}// … const api = await fetchDrandRound(r.result.drandRoundId); const sigMatch = api.signature === r.result.drandRandomness;Why it matters. A signature equal to the public record is a beacon the operator relayed, not one it made up. Duel labels the field drandRandomness; it is the quicknet signature (48 bytes), not drand's separate randomness field.
2.4Uniform Mapping
The uint32 u is uniform over [0, 2³² − 1], and the crash point falls as u rises: the map is monotone. So the values reaching a target x are exactly the first count(x) values of u, with count(x) = floor(999 × 2³² / (10k)) for x = k/100. There is no modulo and no rejection loop: every u gives one crash point.
Mapping:
  u ∈ [0, 2³² − 1], uniform
  cents = floor(999 × 2³² / (10 × (u + 1)))
  crash = max(1.00, cents / 100)

Survival at target x = k/100:
  count(x)     = floor(999 × 2³² / (10k))
  P(crash ≥ x) = count(x) / 2³²

Example — x = 2.00 (k = 200):
  count = floor(4,290,672,328,704 / 2,000) = 2,145,336,164
  P     = 2,145,336,164 / 4,294,967,296     = 49.9500%
RTP = 49.9500% × 2 = 99.9000% (4 dp; at most 99.9%)P(crash ≥ x) is within one uint32 value of 0.999 / x, none above and none below by a whole value (Step 16). The counts come from a per-value model separate from the closed form (Step 12, S4).At the bottom, u ≥ 4,248,190,424 gives 1.00×: 46,776,872 values, so P(1.00) = 1.0891%. At the top, u = 0 gives the map maximum, 4,290,672,328.70×.
2.5RNG Isolation
Each round's crash point is one stateless HMAC call on that round's own seed and beacon. Nothing carries over between rounds: no cursor, no shared buffer, no counter.
(serverSeed, drandRandomness) pair repeats in the capture.2.6Monte Carlo Simulation (Step 13)
Crash has one continuous distribution, so the chi-squared test needs bins: 11 bins from [1.00, 1.01) to [100.00, ∞), aligned with the 2-dp grid, with exact expected fractions from the survival law. One long stream would be exposed to noise in the tail bins, so Pass 1 runs 10 independent streams of 500,000 rounds, seeded by the HMAC-SHA256 domains pass1-server-stream-0…9, and combines the 10 p-values with Fisher's method. Step 13 replays all 5,000,000 rounds from their seeds on every npm test and scores the replay, not the stored file.
| Metric | Value |
|---|---|
| Total rounds | 5,000,000 (10 streams × 500,000) |
| Fisher's combined statistic | T = 18.75 (df = 20) |
| Fisher's combined p-value | 0.5382 |
| Streams below α = 0.01 | 0 / 10 |
| Lag-1 autocorrelation (z) | −0.029 |
| Wald-Wolfowitz runs test (p) | 0.0436 |
| Stream | χ²(10) | p-value |
|---|---|---|
| 0 | 15.01 | 0.1318 |
| 1 | 14.86 | 0.1373 |
| 2 | 6.20 | 0.7986 |
| 3 | 8.58 | 0.5724 |
| 4 | 10.68 | 0.3833 |
| 5 | 12.07 | 0.2801 |
| 6 | 10.29 | 0.4150 |
| 7 | 11.37 | 0.3291 |
| 8 | 4.29 | 0.9335 |
| 9 | 6.75 | 0.7491 |
const PASS1_STREAMS = 10;const PASS1_ROUNDS_EACH = 500_000;const PASS1_ROUNDS_TOTAL = PASS1_STREAMS * PASS1_ROUNDS_EACH;// … for (let s = 0; s < PASS1_STREAMS; s++) { const observed = new Array(NUM_BINS).fill(0); for (let i = 0; i < PASS1_ROUNDS_EACH; i++) { const serverSeed = deterministicHex(`pass1-server-stream-${s}`, i, 32); const drandSeed = deterministicHex(`pass1-drand-stream-${s}`, i, 48); const cp = computeCrashPoint(serverSeed, drandSeed);Fisher's combined test turns K independent p-values into T = −2 Σ ln(p_i), which follows χ² with 2K degrees of freedom. A biased RNG drives most streams' p-values low and T into the rejection region; Crash's combined p = 0.5382 sits mid-range.
2.7Serial Independence
Two tests run on the combined 5M-round Pass 1 sequence, and again on the 1,100 live rounds in capture order (Step 18, informational):
Lag-1 autocorrelation (z): Correlation between consecutive values; |z| ≥ 3 would signal structure. Pass 1: z = −0.029. Live: z = −0.75.
Wald-Wolfowitz runs test (p): The number of runs above and below the median; p < 0.01 would signal structure. Pass 1: p = 0.0436. Live: p = 0.469.
export function lag1Autocorrelation(values: number[]): { r: number; z: number } { const n = values.length; if (n < 3) return { r: 0, z: 0 }; const mean = values.reduce((s, v) => s + v, 0) / n; let num = 0; let den = 0; for (let i = 0; i < n; i++) { den += (values[i] - mean) ** 2; if (i < n - 1) num += (values[i] - mean) * (values[i + 1] - mean); } const r = den === 0 ? 0 : num / den; const z = r * Math.sqrt(n); return { r, z };}2.8Worked Example — Full RNG Trace
Round 829099 — the first captured round (Phase A, $0.01, auto cash-out 1.5×). Verified from data/crash-master-1100rounds.json:
serverSeed      = 3c9c71aa9ffa2691d29fd754cb0caf8ce1fa87d57804196967de81088fab1d23
drandRoundId    = 27798178
drandRandomness = b18fa6dc92304844fc4e868d708953e6b628b3f88d4381249d32264df1bfe5bc
                  20aa0905e57fe54063010881767fd56d   (96 hex characters, 48 bytes)

Step 1 — Decode:   key        = hex_decode(serverSeed)          (32 bytes)
                   drandBytes = hex_decode(drandRandomness)     (48 bytes)
Step 2 — Message:  text       = lossy UTF-8 of drandBytes        (44 characters, 20 × U+FFFD)
                   message    = UTF-8(text) + ":0"               (87 bytes)
Step 3 — HMAC:     5ad96e3c81c2c80dc149a21020c367bbf680b781e9c9eb33525101d7f9df3b3c
Step 4 — uint32:   bytes 5a d9 6e 3c, big-endian → u = 1,524,198,972
Step 5 — Cents:    floor(999 × 2³² / (10 × 1,524,198,973)) = 281
Crash point: max(1.00, 281 / 100) = 2.81| Step | Process | Output |
|---|---|---|
| 1 | Hex-decode the seed and the drand signature | 32-byte key · 48 drand bytes |
| 2 | Read the drand bytes as UTF-8 (lossy), append :0 | 87-byte message |
| 3 | HMAC-SHA256(key, message) | 5ad96e3c…f9df3b3c |
| 4 | First 4 bytes, big-endian | u = 1,524,198,972 |
| 5 | floor(999 × 2³² / (10 × (u + 1))) | 281 cents |
| 6 | max(1.00, cents / 100) | 2.81 (crash point) |
$0.01 × 1.5).Technical Evidence & Verification5 sections
2.9Evidence Coverage Summary6 checks
| Verification Area | Coverage | Result |
|---|---|---|
| Crash-point recomputation (Step 5) | 1,100 / 1,100 exact | Pass |
| Duel's Verify-tab code (cross-check) | 1,100 / 1,100 displayed crash points | Pass |
| drand signature binding (Step 15) | 1,100 / 1,100 pinned api.drand.sh records | Pass |
| Mapping vs survival law (Step 16) | 9,999,900 targets within one uint32 value | Pass |
| Simulation Pass 1 (Step 13) | Fisher's p = 0.5382; 0 / 10 streams below α | Pass |
| Live-sample fit (Step 18) | χ² p = 0.828; lag-1 z −0.75; runs p 0.469 | Pass |
2.10Code References8 source files
| File | Purpose |
|---|---|
| src/rng.ts | Crash-point derivation, commitment check and survival law, written from the specification |
| docs/ALGORITHM.md | The written specification: every step and its source |
| src/operator-verifier.ts | Pins and runs Duel's Verify-tab code (the cross-check) |
| src/simulate.ts | Pass 1 (5M rounds) and Pass 2 (casino seeds) |
| src/stats.ts | Chi-squared, Fisher's method, lag-1 autocorrelation, runs test |
| tests/steps/simulation.ts | Steps 13–15: both simulation passes and drand binding |
| tests/steps/live-fit.ts | Step 18: live-sample fit |
| tests/crash/RngSpecTests.ts | The specification's own checks against src/rng.ts |
2.11Verified Invariants8 invariants
| Invariant | Result |
|---|---|
| The key is the 32 hex-decoded seed bytes; the 64-character text gives different output | Pass |
The message is the lossy UTF-8 text of the drand bytes followed by :0 | Pass |
The drand value is the quicknet signature for its round (1,100 / 1,100) | Pass |
| First 4 digest bytes, big-endian; no cursor, no rejection loop | Pass |
Crash point in exact integers: floor(999 × 2³² / (10(u + 1))) cents, at least 1.00 | Pass |
| Duel's Verify-tab code gives the same displayed crash point on 1,100 / 1,100 | Pass |
| Fisher's combined p ≥ 0.01 (observed 0.5382); 0 / 10 streams below α = 0.01 | Pass |
|lag-1 z| < 3 and runs p ≥ 0.01 on 5M rounds (−0.029, 0.0436) | Pass |
2.12Datasets UsedSource artifacts
2.13Reproduction InstructionsRun locally
Clone the release, install the pinned dependencies, and run the verifier:
git clone https://github.com/ProvablyFair-org/duel-crash.gitcd duel-crash && git checkout v1.2.1 && npm cinpm run verify# S2 steps: 5, 12, 13, 15, 16 and 18Console lines for this section's steps, as run:
✓ Step 5: Outcome Recomputation
✓ Step 12: Anti-Circularity
✓ Step 13: Simulation Pass 1
✓ Step 15: drand API Signature Verification
✓ Step 16: Configuration Coverage (auto-cash-out target)
✓ Step 18: Live-Sample Fit (informational)Verifier Parity
Does the live game actually follow its own rules?
This section checks that the live game follows its own rules. Every recorded crash point recomputes exactly, both ProvablyFair.org verifiers agree, every win flag follows the cash-out rule, and the recorded payout field follows one rule on every win. A single mismatch would break verification.

Live ↔︎ Verifier Parity
What we verified
- Every recorded crash point recomputed from
(serverSeed, drandRandomness)by exact equality — 1,100 / 1,100 - Both ProvablyFair.org verifiers — this site's verifier and the main-site verify-bets bundle — agree on all 1,100 rounds
- Win flags follow crash ≥ target on 1,100 / 1,100 rounds; 4 ties settled as wins
- The recorded
amountWonfollows one rule on all 671 wins: stake × target × 0.999 - Stake does not move the crash point: 100 / 100 rounds at $10 recompute exactly
What this means for you
- Our verifier gives the same crash point as the live game
- Anyone with the revealed values can recompute a round
- Your stake and target don't change the crash point
- A win is credited stake × target on the wins we looked up
- Every recorded crash point recomputed from
(serverSeed, drandRandomness)by exact equality — 1,100 / 1,100 - Both ProvablyFair.org verifiers — this site's verifier and the main-site verify-bets bundle — agree on all 1,100 rounds
- Win flags follow crash ≥ target on 1,100 / 1,100 rounds; 4 ties settled as wins
- The recorded
amountWonfollows one rule on all 671 wins: stake × target × 0.999 - Stake does not move the crash point: 100 / 100 rounds at $10 recompute exactly
- Our verifier gives the same crash point as the live game
- Anyone with the revealed values can recompute a round
- Your stake and target don't change the crash point
- A win is credited stake × target on the wins we looked up
Crash-point recomputation (Step 5)Pass
ProvablyFair.org verifiers (Step 5)Pass
Win rule (Step 7)Pass
isWin = crash ≥ target; 4 ties won, 4 rounds one hundredth below lostRecorded payout field (Step 7)Pass
amountWon = stake × target × 0.999 exactly; 429 / 429 losses record 0; effectiveEdge 0.1 on 1,100 / 1,100Wallet credit (sample)Pass
Bet-size invariance (Step 6)Pass
Phase coverage (Step 9)Pass
src/loader.tsAll 1,100 recorded crash points match our recomputation exactly, and both ProvablyFair.org verifiers agree on every round. Every win flag follows the cash-out rule. The recorded payout field follows one rule on every win, and the wallet ledger credits the full stake × target on the wins looked up.
| Check | Result | Evidence |
|---|---|---|
| Crash-point recomputation (Step 5) | Pass | 1,100 / 1,100 exact; every recorded crash point a whole number of hundredths at or above 1.00 |
| ProvablyFair.org verifiers (Step 5) | Pass | This site's verifier (2 / 2 pins) and the main-site bundle (4 / 4 pins) agree on 1,100 / 1,100; the bundle prints the served commitment on every round |
| Win rule (Step 7) | Pass | 1,100 / 1,100 isWin = crash ≥ target; 4 ties won, 4 rounds one hundredth below lost |
| Recorded payout field (Step 7) | Pass | 671 / 671 amountWon = stake × target × 0.999 exactly; 429 / 429 losses record 0; effectiveEdge 0.1 on 1,100 / 1,100 |
| Wallet credit (sample) | Pass | 3 / 3 wins looked up credited the full stake × target; 3 / 3 losses have no payout leg |
| Bet-size invariance (Step 6) | Pass | 100 / 100 Phase C ($10) rounds recompute; 49 elevated-stake and 24 base-stake wins at 2× settle at one per-unit return |
| Phase coverage (Step 9) | Pass | A 800, B 200, C 100 — as declared in src/loader.ts |
Crash-point recomputation (Step 5)Pass
ProvablyFair.org verifiers (Step 5)Pass
Win rule (Step 7)Pass
isWin = crash ≥ target; 4 ties won, 4 rounds one hundredth below lostRecorded payout field (Step 7)Pass
amountWon = stake × target × 0.999 exactly; 429 / 429 losses record 0; effectiveEdge 0.1 on 1,100 / 1,100Wallet credit (sample)Pass
Bet-size invariance (Step 6)Pass
Phase coverage (Step 9)Pass
src/loader.tsAll 1,100 recorded crash points match our recomputation exactly, and both ProvablyFair.org verifiers agree on every round. Every win flag follows the cash-out rule. The recorded payout field follows one rule on every win, and the wallet ledger credits the full stake × target on the wins looked up.
How It Works — Verifier Parity8 sections
3.1Why Parity Matters
If the verifier and the live game disagree, a player cannot rely on verification at all. Parity has to be exact: a single discrepancy would mean a bug in the verifier, an inconsistent implementation, or manipulation in the live game. A player must be able to take the revealed seed, fetch the beacon from the public chain, and get exactly the crash point they played.
3.2Three-Phase Collection Design
The rounds were captured in three phases, each aimed at one property: a large single-target baseline, several cash-out targets, and a stake 1,000× the base.
| Phase | Rounds | Cash-out Target | Stake | Purpose |
|---|---|---|---|---|
| A — Baseline | 800 | 1.5× | $0.01 | Statistical coverage at one common target |
| B — Varied targets | 200 | 1.1× / 2× / 5× / 10× | $0.01 | Multi-target payout check — 51 rounds at 1.1×, 49 at 2×, 50 at 5×, 50 at 10× |
| C — Bet-size invariance | 100 | 2× | $10.00 | Stake as the only variable: 1,000× the base stake, on the 2× target 49 base-stake rounds also played |
3.3Crash-Point Recomputation (Step 5)
For every round, Step 5 recomputes the crash point with computeCrashPoint(serverSeed, drandRandomness) and compares it with the recorded value by exact equality — no tolerance. The matched count is bound to the declared population, so a skipped or shortened dataset fails.
for (const r of rounds) { const computed = computeCrashPoint(r.result.serverSeed, r.result.drandRandomness); if (computed === r.result.crashPoint) { match++; } else { mismatch++; // … }}3.4Player Verifiers & Duel's Code (Step 5)
Step 5 also runs the two ProvablyFair.org player verifiers from pinned bytes: this site's Crash verifier (games/crash/derive.js and lib/hmac-sha256.js) and the three www.provablyfair.org/verify-bets chunks the Duel path needs, with a runner. Duel's own Verify-tab code, saved verbatim and run unmodified with only its two input values filled in, is the cross-check from the operator's side.
| Verifier | Pinned bytes | Result |
|---|---|---|
| This site's Crash verifier | derive.js + hmac-sha256.js (2 / 2 SHA-256 pins match) | 1,100 / 1,100 crash points |
| Main-site verify-bets bundle | 3 chunks + runner (4 / 4 pins match), fetched 25 September 2026 | 1,100 / 1,100 crash points; served commitment printed on every round |
| Duel's Verify-tab code | Saved 26 September 2026, SHA-256 c699cd54… | 1,100 / 1,100 displayed crash points |
3.5Win-Condition Logic (Step 7)
A bet wins if and only if crashPoint ≥ target. Step 7 checks the recorded isWin flag against that on every round, and counts the boundary cases so the rule is witnessed rather than assumed: rounds whose crash point equals the target, and rounds one hundredth below it.
| Observation | Value |
|---|---|
| Rounds checked | 1,100 |
isWin = crash ≥ target | 1,100 |
| Ties (crash = target) | 4, all won |
| One hundredth below the target | 4, all lost |
| Overall win rate (informational) | 671 / 1,100 (61.00%) |
| Phase A win rate (1.5×) | 543 / 800 (67.88%) |
| Phase C win rate (2×) | 49 / 100 (49.00%) |
for (const r of rounds) { const shouldBeWin = r.result.crashPoint >= r.request.auto_cashout; if (r.result.isWin === shouldBeWin) isWinCorrect++; const cp = Math.round(r.result.crashPoint * 100), tg = Math.round(r.request.auto_cashout * 100); if (cp === tg) { ties++; if (r.result.isWin) tiesWon++; } if (cp === tg - 1) { justBelow++; if (!r.result.isWin) justBelowLost++; }}≥, not >.3.6Recorded Payout & Wallet Credit (Step 7)
Step 7 scores the dataset's amountWon field. On all 671 wins it equals stake × target × (1 − 0.1%) exactly on the 6-dp money grid, with the edge the declared constant — the served effectiveEdge, 0.1 on every round, is compared, never used. That field is not the credit. The wallet ledger, looked up read-only for six captured bets, credits the full stake × target on all three wins. The house edge is in the crash point, not a second time in the credit.
| Bet looked up | Stake × target | Recorded amountWon | Wallet credit |
|---|---|---|---|
| Round 829099 (Phase A) | $0.01 × 1.5 | 0.014985 | +0.015 |
| Round 830182 (Phase B) | $0.01 × 10 | 0.0999 | +0.1 |
| Round 831301 (Phase C) | $10 × 2 | 19.98 | +20 |
const stake = units6(r.request.amount);const wonU = units6(r.result.amountWon);const cents = BigInt(Math.round(r.request.auto_cashout * 100));// …if (r.result.isWin) { won++; if (wonU * 100n === stake * cents) fullBetModel++; if (wonU * 100n * 1000n === stake * cents * (1000n - edgeMilli)) wonOk++; // …stake × target. The three losses looked up have no payout leg.3.7Phase C — Bet-Size Invariance (Step 6)
The stake is not an input to the crash point — not the key, not the message. Phase C placed 100 bets at $10, 1,000× the base stake, on the same 2× target that 49 base-stake bets played, so the stake is the only variable. All 100 recompute exactly, and all 49 elevated-stake and 24 base-stake wins settle at one per-unit return, compared as exact integers on the 6-dp grid.
amountWon on $1,000.00 wagered (49 wins, 97.90%). At 100 bets that is variance, not an RTP measurement; the RTP is derived in S4.3.8Worked Example — Full Parity Verification
Round 831301 — Phase C, $10 stake, auto cash-out 2×; one of the six bets looked up in the wallet ledger. Verified from data/crash-master-1100rounds.json:
roundId          = 831301
serverSeed       = 56cdfbd1a38c4795f92e0007dd2d2a70fe71209d66faed1ad439789b077eb449
serverSeedHash   = 9da3c9e1c90e3d7380279aed9206d9e1a4c95a8b054812c359f2faa9aaf527ee
drandRoundId     = 27818855
drandRandomness  = 952204b3b00da671baebedf8e9f5817de20ba50060b071d140b80d9cbb6233ec
                   30c6c67347c15fc0669266c1863b6ca4   (96 hex characters, 48 bytes)
stake            = $10.00
auto_cashout     = 2.00×
effectiveEdge = 0.1 (served; compared, not used)| Step | Process | Output |
|---|---|---|
| 1 | computeCrashPoint(serverSeed, drandRandomness) | 10.08 (crash point) |
| 2 | crashPoint >= auto_cashout | 10.08 >= 2 → true |
| 3 | stake × target × 0.999 (recorded field) | 19.98 |
| 4 | Wallet ledger payout leg | +20 (stake × target) |
// Step 1: crash point from (serverSeed, drandRandomness)// HMAC-SHA256 = 195ef0cc78821a5f745fc86f757afd229f24eb87734e020cb41a19213bd804e9// u = 0x195ef0cc = 425,652,428// cents = floor(999 × 2^32 / (10 × 425,652,429)) = 1008// crashPoint = 10.08 ✅ (matches the dataset) // Step 2: win rule// 10.08 >= 2.00 → isWin = true ✅ // Step 3: payout// recorded amountWon = 10 × 2 × 0.999 = 19.98 ✅ (matches the dataset)// wallet credit = 10 × 2 = +20 ✅ (wallet ledger)amountWon match exactly, and the wallet ledger shows the full $10 × 2 credited.Technical Evidence & Verification5 sections
3.9Evidence Coverage Summary6 checks
| Verification Area | Coverage | Result |
|---|---|---|
| Crash-point recomputation (Step 5) | 1,100 / 1,100 exact | Pass |
| Player verifiers (Step 5) | 2 verifiers × 1,100 rounds, pins matched | Pass |
| Win rule (Step 7) | 1,100 / 1,100 flags; boundary witnessed | Pass |
| Recorded payout field (Step 7) | 671 / 671 wins, 429 / 429 losses | Pass |
| Bet-size invariance (Step 6) | 100 / 100 at $10; one per-unit return | Pass |
| Phase coverage (Step 9) | A 800 · B 200 · C 100 | Pass |
3.10Code References6 source files
| File | Purpose |
|---|---|
| tests/steps/determinism.ts | Steps 5–6: recomputation, player verifiers, bet-size invariance |
| tests/steps/payouts.ts | Steps 7–9: payout field, win rule, house edge, phase coverage |
| src/site-verifier.ts | Pins and runs this site's Crash verifier |
| src/live-site-verifier.ts | Pins and runs the main-site verify-bets bundle |
| src/operator-verifier.ts | Pins and runs Duel's Verify-tab code |
| src/loader.ts | Population of record: rounds, phases, stakes, targets |
3.11Datasets UsedSource artifacts
3.12Verified Invariants8 invariants
| Invariant | Result |
|---|---|
| Recorded crash point = our recomputation on 1,100 rounds | Pass |
| Every recorded crash point is a whole number of hundredths ≥ 1.00 | Pass |
isWin ⇔ crash ≥ target on 1,100 rounds; ties win | Pass |
amountWon = stake × target × 0.999 on 671 wins, exact on the 6-dp grid | Pass |
amountWon = 0 on 429 losses | Pass |
effectiveEdge = 0.1 on 1,100 rounds, compared with the declared constant | Pass |
| Wallet credit = stake × target on 3 / 3 wins looked up | Pass |
| 100 / 100 Phase C rounds recompute; one per-unit return across stakes | Pass |
3.13Reproduction InstructionsRun locally
Clone the release, install the pinned dependencies, and run the verifier:
git clone https://github.com/ProvablyFair-org/duel-crash.gitcd duel-crash && git checkout v1.2.1 && npm cinpm run verify# S3 steps: 5, 6, 7 and 9Console lines for this section's steps, as run:
✓ Step 5: Outcome Recomputation
✓ Step 6: Bet-Size Invariance
✓ Step 7: Payout Math
✓ Step 9: Phase CoverageRTP & Payout Logic
Is the house edge what the casino claims?
This section derives the theoretical RTP from the algorithm alone, by counting uint32 values in exact integers, with no casino-supplied probabilities. It then holds Duel's published 99.9% to every cash-out target under the RTP claim rule, checks the payouts, and backs the count with 5 million simulated rounds and a screen of the casino's 1,100 seeds.

Return to Player Verification
What we verified
- Theoretical RTP derived from the algorithm alone: at most 99.9% at every cash-out target, counted in exact integers
- 99.9000% (4 dp) at every target from 1.01× to 2,156.11×; with Duel's stated 9,999.999× cap applied, the lowest of any target is 99.899768% (9,999.05×)
- RTP claim rule: the flat 99.9% on Duel's fairness page holds at all 9,999,900 targets within ±0.1 pp — PASS
- A win pays the cash-out target: the wallet credited
stake × targeton the wins looked up - 5M simulated rounds: RTP within 5σ of the formula at all 5 tracked targets
- Pass 2 finds no sign of seed selection across the casino's 1,100 seeds (return z 0.286, rank-sum z 0.160)
What this means for you
- The 0.1% house edge sits in the crash point and is the same at every target
- With Duel's stated 9,999.999× cap applied, every cash-out target returns between 99.899768% and 99.9%
- Duel's published 99.9% is not overstated
- Short sessions swing widely; RTP is a long-run figure
- Theoretical RTP derived from the algorithm alone: at most 99.9% at every cash-out target, counted in exact integers
- 99.9000% (4 dp) at every target from 1.01× to 2,156.11×; with Duel's stated 9,999.999× cap applied, the lowest of any target is 99.899768% (9,999.05×)
- RTP claim rule: the flat 99.9% on Duel's fairness page holds at all 9,999,900 targets within ±0.1 pp — PASS
- A win pays the cash-out target: the wallet credited
stake × targeton the wins looked up - 5M simulated rounds: RTP within 5σ of the formula at all 5 tracked targets
- Pass 2 finds no sign of seed selection across the casino's 1,100 seeds (return z 0.286, rank-sum z 0.160)
- The 0.1% house edge sits in the crash point and is the same at every target
- With Duel's stated 9,999.999× cap applied, every cash-out target returns between 99.899768% and 99.9%
- Duel's published 99.9% is not overstated
- Short sessions swing widely; RTP is a long-run figure
Anti-circularity (Step 12)Pass
src/rng.ts at all 11 targets, every RTP ≤ 0.999 in integers; both negative controls rejectedHouse edge (Step 8)Pass
RTP claim — RTP-CLAIM 1.2.0 (Step 16)Pass
Stake tiersInfo
Payout rule (Step 7)Pass
amountWon = stake × target × 0.999 on 671 / 671 wins; the wallet ledger credits the full stake × target on the 3 wins looked upSimulation Pass 1 (Step 13)Pass
Cherry-pick screen — Pass 2 (Step 14)Pass
Target coverage (Step 16)Pass
The theoretical RTP is derived from the algorithm alone, by counting uint32 values in exact integers: at most 99.9% at every cash-out target. With Duel's stated 9,999.999× cap applied, the lowest is 99.899768%, and Duel's flat 99.9% holds at all 9,999,900 targets within the ±0.1 pp band. The 3 wins looked up were credited the full stake × target, so the edge sits in the crash point. Simulation is consistent with the formula, and Pass 2 finds no sign of seed selection.
Lowest of any target, with Duel’s stated 9,999.999× cap applied: 99.899768% (9,999.05×).
| Check | Result | Evidence |
|---|---|---|
| Anti-circularity (Step 12) | Pass | uint32 values counted from a per-value model separate from the closed form: equal to src/rng.ts at all 11 targets, every RTP ≤ 0.999 in integers; both negative controls rejected |
| House edge (Step 8) | Pass | RTP at 2×, 10× and 100× at or below 0.999 in integer arithmetic; P(1.00) = 1.0891% |
| RTP claim — RTP-CLAIM 1.2.0 (Step 16) | Pass | Flat 99.9% on Duel's fairness page; 9,999,900 targets, Duel's stated cap applied: lowest 99.899768%, highest 99.900000%; 0 beyond the ±0.1 pp band |
| Stake tiers | Info | No stake-tier configuration in the crash package; both captured stakes ran at the base 0.1% edge. Certified for the base stake tier only |
| Payout rule (Step 7) | Pass | Recorded amountWon = stake × target × 0.999 on 671 / 671 wins; the wallet ledger credits the full stake × target on the 3 wins looked up |
| Simulation Pass 1 (Step 13) | Pass | 5M rounds: simulated RTP within 5σ of the formula at 1.5×, 2×, 5×, 10× and 50× (largest |z| 0.80) |
| Cherry-pick screen — Pass 2 (Step 14) | Pass | 1,100 casino seeds × 10,000 beacon values: return z 0.286, rank-sum z 0.160 against −3.291 |
| Target coverage (Step 16) | Pass | 5 targets played, each above the 45-round floor (1.1×: 51, 1.5×: 800, 2×: 149, 5×: 50, 10×: 50); every 0.01 target to 100,000× counted |
Anti-circularity (Step 12)Pass
src/rng.ts at all 11 targets, every RTP ≤ 0.999 in integers; both negative controls rejectedHouse edge (Step 8)Pass
RTP claim — RTP-CLAIM 1.2.0 (Step 16)Pass
Stake tiersInfo
Payout rule (Step 7)Pass
amountWon = stake × target × 0.999 on 671 / 671 wins; the wallet ledger credits the full stake × target on the 3 wins looked upSimulation Pass 1 (Step 13)Pass
Cherry-pick screen — Pass 2 (Step 14)Pass
Target coverage (Step 16)Pass
The theoretical RTP is derived from the algorithm alone, by counting uint32 values in exact integers: at most 99.9% at every cash-out target. With Duel's stated 9,999.999× cap applied, the lowest is 99.899768%, and Duel's flat 99.9% holds at all 9,999,900 targets within the ±0.1 pp band. The 3 wins looked up were credited the full stake × target, so the edge sits in the crash point. Simulation is consistent with the formula, and Pass 2 finds no sign of seed selection.
How It Works — RTP & Payout Logic9 sections
4.1Anti-Circularity — RTP From First Principles (Step 12)
The theoretical RTP is derived without any casino-supplied probability or multiplier table; Crash has none. Step 12 does not re-type the closed form either. It takes the per-value map from the specification, checks that it reproduces all 1,100 live crash points with its own HMAC call, then counts the uint32 values whose crash point reaches each of 11 targets. The count is an integer, so it is compared with src/rng.ts exactly, and each RTP is held to the 0.999 ceiling in integer arithmetic — no tolerance.
| Component | Formula | Source |
|---|---|---|
| Per-value map | cents(v) = floor(100 × 999 × 2³² / (1000 × (v + 1))), crash = max(1.00, cents / 100) | The specification, docs/ALGORITHM.md §2 — bound to 1,100 live rounds |
| Survival count | count(x) = number of uint32 values v with crash(v) ≥ x | Counted by bisection — the map is monotone in v |
| Payout multiplier | x — a win pays the cash-out target | Wallet ledger (3 / 3 wins looked up) |
| RTP | count(x) × x / 2³² ≤ 0.999 | Decided in integers: count × cents × 1000 ≤ 2³² × 999 × 100 |
| Target | uint32 count | P(crash ≥ target) | Theoretical RTP |
|---|---|---|---|
| 1.01× | 4,248,190,424 | 98.9109% | 99.9000% |
| 1.1× | 3,900,611,207 | 90.8182% | 99.9000% |
| 1.5× | 2,860,448,219 | 66.6000% | 99.9000% |
| 2× | 2,145,336,164 | 49.9500% | 99.9000% |
| 3× | 1,430,224,109 | 33.3000% | 99.9000% |
| 5× | 858,134,465 | 19.9800% | 99.9000% |
| 10× | 429,067,232 | 9.9900% | 99.9000% |
| 20× | 214,533,616 | 4.9950% | 99.9000% |
| 50× | 85,813,446 | 1.9980% | 99.9000% |
| 100× | 42,906,723 | 0.9990% | 99.9000% |
| 1000× | 4,290,672 | 0.0999% | 99.9000% |
// (a) bind the independent mapping to the live populationfor (const r of rounds) { const cp = crashFromValue(valueFromRound(r.result.serverSeed, r.result.drandRandomness)); if (cp === r.result.crashPoint) liveBound++; // …} // (b) counted survival vs src/rng.ts, exact; (c) RTP vs the 0.999 ceiling, exactfor (const t of targets) { const counted = countAtOrAbove(t); const rngCount = survivalProbability(t) * TWO32; if (!Number.isInteger(rngCount) || rngCount !== counted) { countMismatches++; // … } const { deficit } = rtpDeficitUnits(counted, t); if (deficit < 0n) { aboveCeiling++; // … } // …}src/rng.ts exactly and every RTP is at or below 0.999: 99.900000% to six decimals at eight targets, 99.899999% at 50× and 100×, 99.899992% at 1000×. The shortfall is the floor in the count.Negative controls. A comparison that cannot fail proves nothing, so Step 12 shows both of its comparisons failing on purpose: every live crash point moved by one hundredth is rejected (1,100 / 1,100), and a map wired to an edge factor of 0.998 disagrees with src/rng.ts at 11 / 11 targets.
Why it is non-circular. The counts come from the specification's per-value map, bound to the live rounds, not from the closed form or from casino data. The payout multiplier is the cash-out target itself, so the RTP at a target is its survival probability times the target.
4.2House Edge (Step 8)
Step 8 computes the RTP from the uint32 threshold at three spot targets and decides the 0.999 ceiling in integers. The edge is the 0.999 factor in the crash-point formula: flat, with no per-target scaling, and below the ceiling only by the floor in the count, by less than x / 2³² at target x.
| Quantity | Value |
|---|---|
| RTP at 2× | 99.9000% (0.9989999998) |
| RTP at 10× | 99.9000% (0.9989999980) |
| RTP at 100× | 99.9000% (0.9989999933) |
| P(crash = 1.00) | 1.0891% — 46,776,872 of 2³² values |
4.3RTP Claim Rule (RTP-CLAIM 1.2.0)
Framework 1.1 holds the RTP a casino publishes to the game's real figures. A figure counts as published on the game page, the fairness page, the help page, the bet panel, the rules or the game settings. Every setting a player can choose must sit within ±0.1 percentage point of the figure; a figure that overstates the RTP beyond the band on any setting ends the run RTP FIGURE OVERSTATED (exit 5). The draws are scored separately, so a miss is never "not provably fair". A player-favourable gap never fails.
The claim. A flat 99.9%: Duel's fairness page shows houseEdge = 0.001 in the code panel of the Provably Fair → Verify tab (E16), and every captured round carries effectiveEdge 0.1. Scored on Step 16, over every 0.01 cash-out target from 1.01× to 100,000× — 9,999,900 settings. Targets from 10,000.00× up are scored at Duel's stated 9,999.999× cap.
| Cash-out targets | Settings | Lowest RTP | Highest RTP | Beyond band |
|---|---|---|---|---|
| 1.01× – 1.99× | 99 | 99.900000% | 99.900000% | 0 |
| 2.00× – 9.99× | 800 | 99.900000% | 99.900000% | 0 |
| 10.00× – 99.99× | 9,000 | 99.899998% | 99.900000% | 0 |
| 100.00× – 999.99× | 90,000 | 99.899977% | 99.900000% | 0 |
| 1,000.00× – 9,999.99× | 900,000 | 99.899768% | 99.900000% | 0 |
| 10,000.00× – 100,000.00× (at the cap) | 9,000,001 | 99.899936% | 99.899936% | 0 |
outputs/rtp-claim-table.json records the extremes and the per-decade results, pinned by SHA-256.4.4Stake Tiers & Other Lines
Certification covers the base stake tier. The crash package carries no stake-tier configuration and Duel publishes no per-stake edge tier on the pages read, so any edge that scales with stake above the base tier is outside this audit. Both captured stakes, $0.01 and $10, ran at the base 0.1% edge on every round (effectiveEdge 0.1 on 1,100 / 1,100).
| Line | What it is | Status |
|---|---|---|
| Cash-out cap | Duel's statement: every bet cashes out at 9,999.999× at most. At and above the cap the return is 99.899936%; no captured bet reached it | Noted, not tested |
| Zero Edge rakeback | A 0.001 × stake record on each of the six bets looked up. If it is paid, the net return is 99.999768% – 100.000000% (99.999936% at and above the cap) | Noted, not tested |
| Zero Edge daily cap | Not exercised by the capture | Noted, not tested |
| Profit and max-win caps | Outside our testing | Not tested |
4.5Payouts (Step 7)
A bet that reaches its target pays stake × target; a bet that does not pays 0. The dataset's amountWon field records stake × target × 0.999 on every win, exactly on the 6-dp money grid, so Step 7 scores that field as recorded; the wallet credit is covered in S3 (3.6).
| Target | P(win) | Credit per $1 staked | Recorded amountWon per $1 |
|---|---|---|---|
| 1.1× | 90.8182% | $1.10 | $1.0989 |
| 1.5× | 66.6000% | $1.50 | $1.4985 |
| 2× | 49.9500% | $2.00 | $1.998 |
| 5× | 19.9800% | $5.00 | $4.995 |
| 10× | 9.9900% | $10.00 | $9.99 |
4.6Simulation Pass 1 — RTP by Target (Step 13)
Pass 1 replays 5,000,000 rounds on HMAC-derived seeds (10 streams × 500,000) and tracks the return at five cash-out targets. Every simulated RTP is within 5σ of the formula; the distribution test is in S2.
| Target | Simulated RTP | Theoretical RTP | z |
|---|---|---|---|
| 1.5× | 99.8863% | 99.9000% | −0.43 |
| 2× | 99.8643% | 99.9000% | −0.80 |
| 5× | 99.8948% | 99.9000% | −0.06 |
| 10× | 99.9334% | 99.9000% | +0.25 |
| 50× | 99.7810% | 99.9000% | −0.38 |
4.7Cherry-Pick Screen — Pass 2 (Step 14)
Pass 2 asks two questions of the casino's 1,100 revealed seeds, each paired with 10,000 reference beacon values at the cash-out target its captured round was played at: 11,000,000 replayed rounds. Does the seed population pay the exact law's return? And was each captured beacon an ordinary draw for its seed? Under no cherry-picking, a captured round is exchangeable with its seed's reference draws, so its rank is uniform.
| Statistic | Value |
|---|---|
| Seeds × beacon values | 1,100 × 10,000 = 11,000,000 rounds |
| Return of the played targets | 10,989,992.10 vs exact mean 10,988,999.998 (RTP 99.9090% vs 99.9000%) |
| Return z | 0.286 |
| Rank-sum z (exact permutation null) | 0.160 |
| Captured wins | 671 vs 668.53 expected |
| Captured rounds reproduced from their real beacon | 1,100 / 1,100 |
| Fail threshold (pre-registered) | z < −3.291 on either test (one-sided α 0.0005 each, family 0.001) |
const rp = replayPass2(firstRounds.map(r => ({ serverSeed: r.result.serverSeed, drandRandomness: r.result.drandRandomness, crashPoint: r.result.crashPoint, target: r.request.auto_cashout,})));// …const returnOk = rp.returnZ >= PASS2_Z_CRIT;const rankOk = rp.rankSumZ >= PASS2_Z_CRIT;const pass = returnOk && rankOk && rp.capturedReplayMismatches === 0 && disagree.length === 0 && popOk;4.8Informational Items (Not Scored)
Live-sample figures at n = 1,100 are far too noisy to measure a 0.1% edge. They are shown for context; the count and the simulation are the RTP evidence. Returns use the recorded amountWon field.
| Item | Value |
|---|---|
| Instant crashes | 8 / 1,100 (0.73%) vs about 12.0 expected (1.09%); 95% binomial interval about [5, 19] |
| Live RTP at 1.1× (n = 51) | 94.81% |
| Live RTP at 1.5× (n = 800) | 101.71% |
| Live RTP at 2× (n = 149) | 97.90% |
| Live RTP at 5× (n = 50) | 69.93% |
| Live RTP at 10× (n = 50) | 79.92% |
| Overall win rate | 671 / 1,100 (61.00%) |
| Crash points | min 1.00×, median 1.96×, max 13,664.99× |
4.9Worked Example — RTP & Payout
Round 830182 — Phase B, $0.01 stake, auto cash-out 10×; one of the six bets looked up in the wallet ledger. Verified from data/crash-master-1100rounds.json:
serverSeed      = 2df69d3868ea015643180e2d7afb39dfa116bc75afa7a7db05bb278b472d0c54
drandRoundId    = 27808385
drandRandomness = ab6bf01d168311b5824e4f9b0a6e6f31ff21583b64df1250de35b03fa3cb9a6f
                  43aa1bece7e800a2328034dc3e8a7af0   (96 hex characters, 48 bytes)

HMAC-SHA256  = 07cf652186987d450654d50f1ae861009a2c3f974c6f1e060d73b8901f28cff1
u            = 0x07cf6521 = 131,032,353
cents        = floor(999 × 2³² / (10 × 131,032,354)) = 3274
crashPoint = 32.74 → 32.74 ≥ 10 → win| Quantity | Value |
|---|---|
| Theoretical RTP at 10× | 429,067,232 × 10 / 2³² = 99.9000% (0.9989999980) |
| Wallet credit | $0.01 × 10 = +0.1 (wallet ledger) |
Recorded amountWon | $0.01 × 10 × 0.999 = 0.0999 |
$0.01 × 10 credited.Technical Evidence & Verification5 sections
4.10Evidence Coverage Summary8 checks
| Verification Area | Coverage | Result |
|---|---|---|
| Anti-circularity (Step 12) | 11 targets counted; 1,100 live rounds bound; 2 negative controls | Pass |
| House edge (Step 8) | RTP at 2×, 10×, 100× in integers | Pass |
| RTP claim (Step 16) | 9,999,900 targets within ±0.1 pp of 99.9% | Pass |
| Payout field (Step 7) | 671 / 671 wins, 429 / 429 losses | Pass |
| Simulation Pass 1 (Step 13) | 5M rounds; 5 targets within 5σ | Pass |
| Simulation Pass 2 (Step 14) | 11M rounds; z 0.286 / 0.160 | Pass |
| Target coverage (Step 16) | 5 targets above the 45-round floor | Pass |
| Stake tiers | Base stake tier only | Info |
4.11Code References8 source files
| File | Purpose |
|---|---|
| tests/steps/crash-model.ts | The per-value model Steps 12 and 16 count from — separate from the closed form |
| tests/steps/dataset.ts | Step 12: anti-circularity and its negative controls |
| tests/steps/payouts.ts | Steps 7–8: payout field, win rule, house edge |
| tests/steps/coverage.ts | Step 16: target coverage, the 9,999,900-target count and the RTP claim |
| src/rtp-claim.ts | The RTP-CLAIM 1.2.0 rule |
| src/rtp-settings.ts | Generates and pins outputs/rtp-claim-table.json |
| tests/steps/sim-replay.ts | Replays both simulation passes from their seeds (Steps 13–14) |
| src/simulate.ts | Writes the simulation artifact and the convergence chart |
4.12Datasets UsedSource artifacts
4.13Verified Invariants6 invariants
| Invariant | Result |
|---|---|
| Per-value model reproduces 1,100 / 1,100 live crash points | Pass |
Counted survival = src/rng.ts survival × 2³² at 11 targets, exactly | Pass |
count × cents × 1000 ≤ 2³² × 999 × 100 at every target (RTP ≤ 0.999) | Pass |
0 ≤ 0.999 − RTP(x) < x / 2³² at all 9,999,900 targets to 100,000× | Pass |
| Every target within ±0.1 pp of the published 99.9% (RTP-CLAIM 1.2.0) | Pass |
| Simulated RTP within 5σ at 5 targets; Pass 2 z above −3.291 on both tests | Pass |
4.14Reproduction InstructionsRun locally
Clone the release, install the pinned dependencies, and run the verifier:
git clone https://github.com/ProvablyFair-org/duel-crash.gitcd duel-crash && git checkout v1.2.1 && npm cinpm run verify# S4 steps: 7, 8, 12, 13, 14 and 16Console lines for this section's steps, as run:
✓ Step 7: Payout Math
✓ Step 8: House Edge Audit
✓ Step 12: Anti-Circularity
✓ Step 13: Simulation Pass 1
✓ Step 14: Simulation Pass 2 (Casino Seeds)
✓ Step 16: Configuration Coverage (auto-cash-out target)
rtp-claim: ENFORCED — PASS
rtp-claim: claim flat 99.900000% — source: fairness page: houseEdge = 0.001 in the code panel of the Verify tab on Duel's Provably Fair page (Provably Fair → Verify, game Crash; evidence/verify-tab/duel-verify-tab-crash-2026-09-26.js L63, E16, pasted 2026-09-26), and effectiveEdge 0.1 served on all 1,100 rounds (Step 7; MANIFEST.md#payouts-and-rtp; declaration gameModel.edge.claimed 0.001)
rtp-claim: band ±0.10 pp · 9,999,900 settings · true min 99.899768% (cashout=9999.05) · true max 99.900000% (cashout=1.03)
rtp-claim: house side beyond band: 0 · player-favourable beyond band: 0 · worst cashout=9999.05 at -0.000232 pp
rtp-claim: outcome PASS · minimal fix: none — the claim holds for every setting it states a figure for
rtp-claim: committed table outputs/rtp-claim-table.json: equals this run; sha256 a80f359c34cd0dab… matches the pinFairness Integrity Testing
Does the implementation maintain fairness under non-standard conditions?
Sections 1–4 prove the game is mathematically fair. Section 5 proves the implementation maintains integrity under non-standard conditions. We applied 16 standard fairness integrity tests covering seed integrity, commitment timing, outcome determinism, cross-player isolation, payout integrity, and house-edge / distribution integrity. For Crash, the framework is adapted from the pan-game matrix to reflect the dual-entropy (server seed + drand) architecture: there is no client seed to test, no nonce sequence per player, and the commit-reveal chain is anchored against an external public beacon rather than a per-player seed pair.

Fairness Integrity Testing
What we verified
- Seed commitment — server seed hash published before drand beacon emits (1,100 / 1,100 verified)
- drand authenticity — every beacon value matches the public drand chain byte-for-byte (1,100 / 1,100)
- Bet timing — bet placed before drand publication for every round (min margin 0.404s)
- Outcome determinism — identical inputs produce identical crash points (1,100 / 1,100 recomputed)
- Cross-player isolation — all players see the same crash point per round (global outcome model)
- Distribution integrity — crash-point distribution matches uint32 survival formula (Fisher's
p = 0.5382)
What this means for you
- No one — not the player, not the casino — can alter the crash point through the API
- The casino commits to each round's outcome before the external entropy is even known
- Every round is cryptographically isolated from every other — no state leakage
- The external entropy comes from a public beacon the casino cannot forge or withhold
- The server rejects malformed bet parameters and ignores injected outcome fields
- Seed commitment — server seed hash published before drand beacon emits (1,100 / 1,100 verified)
- drand authenticity — every beacon value matches the public drand chain byte-for-byte (1,100 / 1,100)
- Bet timing — bet placed before drand publication for every round (min margin 0.404s)
- Outcome determinism — identical inputs produce identical crash points (1,100 / 1,100 recomputed)
- Cross-player isolation — all players see the same crash point per round (global outcome model)
- Distribution integrity — crash-point distribution matches uint32 survival formula (Fisher's
p = 0.5382)
- No one — not the player, not the casino — can alter the crash point through the API
- The casino commits to each round's outcome before the external entropy is even known
- Every round is cryptographically isolated from every other — no state leakage
- The external entropy comes from a public beacon the casino cannot forge or withhold
- The server rejects malformed bet parameters and ignores injected outcome fields
Seed integrityPass
Bet timingPass
Outcome determinismPass
Cross-player isolationPass
Payout integrityFlag
House edge & distributionPass
16 fairness integrity tests: 14 pass, 1 N/A (replay protection — single-step game), 1 FLAG (server-side input validation gap on auto_cashout_multiplier — does not break fairness). Disclosed to Duel.com.
Category Coverage


| Check | Result | Evidence |
|---|---|---|
| Seed integrity | Pass | 5 tests — all four SEED-001..004 pass + new SEED-005 statistical quality (χ² p = 0.7413, H = 7.995 bits/byte) |
| Bet timing | Pass | Bet placed before drand in 1,100 / 1,100 rounds (min margin 0.404s); drand round IDs strictly increasing |
| Outcome determinism | Pass | Identical inputs produce identical crash points — 1,100 / 1,100 confirmed. Replay protection: architecturally N/A |
| Cross-player isolation | Pass | RNG state independent (lag1Z = −0.029, runsP = 0.0436); global outcome model — all players see same crash point |
| Payout integrity | Flag | Field injection probed (3 betting-phase + 3 running-phase) — server computed crash point and multiplier from seed chain; no injected field reflected. Boundary re-run (FI-PAYOUT-001): the server accepted two auto_cashout_multiplier values above the theoretical maximum crash point (~4,290,672,328.70×) instead of rejecting them; on Duel's statement that every bet cashes out at 9,999.999× at most, such a bet is settled as a 9,999.999× cash-out. Server-side input-validation gap — disclosed to Duel.com (see FI-PAYOUT-001 in matrix). |
| House edge & distribution | Pass | Anti-circularity proved 99.9% RTP for 11 targets; Fisher's combined p = 0.5382 across 10 × 500K streams |
Seed integrityPass
Bet timingPass
Outcome determinismPass
Cross-player isolationPass
Payout integrityFlag
House edge & distributionPass
16 fairness integrity tests: 14 pass, 1 N/A (replay protection — single-step game), 1 FLAG (server-side input validation gap on auto_cashout_multiplier — does not break fairness). Disclosed to Duel.com.
How It Works — Fairness Integrity Testing2 sections
5.1Framework Overview
Testing follows the ProvablyFair.org Fairness Integrity Framework — a structured methodology derived from real, historically observed failures in provably fair systems. For Crash, the framework is adapted to the dual-entropy model: seed integrity now includes bet timing against a public external beacon (drand) rather than just hash commitment, and the "Nonce Integrity" category standard in client-seed games is replaced by "Commitment Timing" because drand round IDs serve as Crash's global sequence. Scope boundary: S5 tests whether fairness guarantees hold under non-standard API interaction. Platform-level implementation testing falls outside standard certification.
| Category | Tests | What It Catches |
|---|---|---|
| Seed Integrity | 5 | Hash mismatches, drand forgery, seed reuse, non-determinism, non-uniform seed generation |
| Bet Timing | 2 | Late-commitment attacks, round shopping, post-hoc drand selection |
| Determinism | 3 | Non-deterministic outputs, bet-size influence on outcome, replay-for-duplicate-payout |
| Isolation | 2 | Cross-round state leakage, cross-player outcome dependence |
| Payout Integrity | 2 | Parameter enforcement, server-side computation verification |
| House Edge & Distribution | 2 | Hidden scaling edge, biased crash-point distribution |
5.2Severity Framework & Hard Fail Criteria
Findings are classified by severity. Hard fail criteria — any one triggers a NOT PROVABLY FAIR verdict.
| Severity | Meaning | Action |
|---|---|---|
| PASS | Test passed — no issue detected | None |
| N/A | Test not applicable to this game type | None |
| FLAG | Anomaly detected, documented for transparency | Disclosed |
| HARD FAIL | Fairness guarantee cannot be confirmed | Certification blocked until remediated |
| Condition | Consequence |
|---|---|
| Negative commitment margin (bet placed after drand published) | Pre-commitment guarantee broken — operator could have seen beacon first |
drand signature mismatch against api.drand.sh | External entropy forged — no independent randomness source |
| drand round ID non-monotonic (round shopping) | Operator cherry-picking favourable beacons post-hoc |
| Crash-point recomputation mismatch | Undisclosed inputs affecting outcomes |
| Server seed reuse across rounds | Commit-reveal guarantee broken |
| Per-player crash-point divergence in the same round | Cross-player isolation broken / hidden per-user seed |
16 tests · 14 pass · 1 flag · 1 N/A
Seed Integrity5/5
FI-CRASH-SEED-001PassServer seed is committed (hashed) before the round's drand beacon is known
S1, Step 1 — 1,100/1,100 hashes verified. SHA-256(serverSeed_bytes) === serverSeedHash published pre-drand.
FI-CRASH-SEED-002Passdrand beacon is authentic and externally verifiable against the public drand chain
S2, Step 15 — 1,100/1,100 drand signatures cross-verified against api.drand.sh (chain 52db9ba7…4e971). 0 forgeries.
FI-CRASH-SEED-003PassServer seed is unique per round — no reuse across the captured sample
S1, Step 4 — 1,100 unique seeds and 1,100 unique hashes across 1,100 rounds.
FI-CRASH-SEED-004PassCrash point is deterministic from (serverSeed, drandRandomness) — no hidden entropy
S2, Step 5 — 1,100/1,100 crash points independently recomputed via HMAC-SHA256. 0 mismatches. API-probe confirmation: 10 complete pre/post pairs collected via WebSocket — crash_hashed_pf event captured before drand round, server_seed revealed post-round. SHA-256(server_seed) matched the pre-committed hash in 10/10 rounds. matchCount=10, mismatchCount=0.
FI-CRASH-SEED-005PassCaptured server seeds show no statistical patterns — uniform byte distribution, high entropy, no round-order correlation
Statistical quality check on 35,200 bytes (1,100 seeds × 32 bytes): byte-value χ² p = 0.7413; Shannon entropy H = 7.99506 bits/byte; round-order × first-byte Spearman ρ = −0.0003 (p = 0.9929). All three sub-tests within thresholds.
Bet Timing2/2
FI-CRASH-TIMING-001PassBet placement precedes drand beacon publication for every round — operator commits to the seed before external entropy is known
S1, Step 2 — 1,100/1,100 rounds with positive commitment margin (min 0.404s, mean 12.196s, max 13.779s). Single negative margin = hard fail.
FI-CRASH-TIMING-002Passdrand round IDs strictly increase across the capture window — monotonic, no replays or reordering
S1, Step 3 — 1,100 rounds, drand round IDs strictly increasing across range 27,798,178 → 27,819,827. No gaps, no backward jumps.
Determinism3/3
FI-OUTCOME-001PassGiven identical inputs (serverSeed, drandRandomness), the game always produces the same crash point
S2, Step 5 — 1,100/1,100 crash points independently recomputed from the two inputs, zero mismatches.
FI-OUTCOME-002N/AA completed round cannot be replayed via the API to generate a duplicate payout
Crash auto-resolves — single-step game with no separate cashout action. auto_cashout target is fixed at bet time; crash point and payout are auto-computed from (serverSeed, drandRandomness) alone. No separate cashout-action request exists for a completed round to replay.
FI-CRASH-DETERMINISM-003PassCrash point cannot be influenced by player actions or bet size — outcome is invariant under stake changes
S3, Step 6 — all 100 Phase C ($10) rounds verify under the identical RNG code path as the $0.01 rounds. Bet amount is not an input to the HMAC key or message.
Isolation2/2
FI-ISO-001PassRNG state is fully independent across rounds — no carry-over from one round to the next
S2, Step 13 — serial independence tested on combined 5M-round sequence: lag1Z = −0.029 (within |Z|<3), runsP = 0.0436 (above 0.01 threshold).
FI-ISO-002PassAll players see the same crash point per round — single global outcome model, no per-user seed, no cross-user dependence
Architectural — computeCrashPoint(serverSeed, drandRandomness) takes no per-user input. RNG code path confirmed in S2 (2.1 Implementation).
Payout Integrity1/2
FI-PAYOUT-001FlagBet parameters cannot exceed defined limits — invalid amounts and out-of-range auto_cashout values are rejected server-side
API probe (re-run) — the server accepts auto_cashout_multiplier values above the theoretical maximum crash point. The theoretical maximum crash point is 4,290,672,328.70× — the ceiling of the published formula floor(2³² ÷ (value + 1) × 0.999 × 100) ÷ 100 at its smallest input (uint32 value = 0). Four bets were sent over the WebSocket place-bet event to probe the boundary. Two control bets within range — multiplier=2 and multiplier=1,000,000,000 — were correctly accepted, as expected. Two boundary bets above the theoretical maximum were also accepted: multiplier=4,300,000,000 (just above the real max; bet id 1680011, round 971971) and multiplier=1,000,000,000,000,000 (bet id 1680017, round 971972). This is a server-side input-validation gap: no round can reach a target above 4,290,672,328.70×, yet the server stored it instead of rejecting it. Duel states that every bet cashes out at 9,999.999× at most, whatever target is set; on that statement such a bet is settled as a 9,999.999× cash-out, which wins only if the round reaches it. The server must reject any auto_cashout_multiplier that exceeds the theoretical maximum crash point (~4,290,672,328.70×). The fairness guarantees of the commit-reveal model are unaffected: the crash point is still derived deterministically from the server seed and drand beacon and no injected field overrides it (see FI-PAYOUT-002); any payout remains bounded by the platform's max-win cap. Disclosed to Duel.com.
FI-PAYOUT-002PassPayout and crash-point fields cannot be injected into the bet request — server computes outcome only from canonical inputs
API probe — 3 betting-phase + 3 running-phase WebSocket bets each carrying an injected field (crash_point=1000, payout_multiplier=999, cashout_at=999). The accepted betting-phase bet (id 1476259, round 883890) returned auto_cashout_multiplier=2 with no injected field reflected in the response. The crash point is computed server-side from server_seed + drand beacon; no client-supplied field could override it. injectedFieldsLeaked=false.
House Edge & Distribution2/2
FI-CRASH-EDGE-001PassHouse edge is 0.1% as per published formula — no scaling edge, no per-target variation, analytically proven
S4, Step 12 — anti-circularity: P(crash ≥ x) × x ≤ 0.999 for 11 cashout targets (1.01× → 1000×). Independently derived from uint32 survival formula. Step 16 extends the count to all 9,999,900 targets; with Duel's stated 9,999.999× cap applied, the lowest is 99.899768% (9,999.05×).
FI-CRASH-STAT-001PassCrash-point distribution matches theoretical expectations across 5M simulated rounds — no mapping bias, no serial correlation
S4, Steps 13–14 — Pass 1: Fisher's combined p = 0.5382 across 10 × 500K streams; 0/10 streams below α = 0.01. Pass 2: 1,100 casino seeds × 10,000 beacon values — return z 0.286, rank-sum z 0.160 against −3.291.
Technical Evidence & Verification4 sections
5.3Coverage Summary16 checks
| Test ID | Category | Verification Source | Status |
|---|---|---|---|
| FI-CRASH-SEED-001 | Seed | S1, Step 1 (data-driven) | Pass |
| FI-CRASH-SEED-002 | Seed | S2, Step 15 (data-driven) | Pass |
| FI-CRASH-SEED-003 | Seed | S1, Step 4 (data-driven) | Pass |
| FI-CRASH-SEED-004 | Seed | S2, Step 5 (data-driven) | Pass |
| FI-CRASH-SEED-005 | Seed | Statistical analysis (data-driven) | Pass |
| FI-CRASH-TIMING-001 | Timing | S1, Step 2 (data-driven) | Pass |
| FI-CRASH-TIMING-002 | Timing | S1, Step 3 (data-driven) | Pass |
| FI-OUTCOME-001 | Determinism | S2, Step 5 (data-driven) | Pass |
| FI-OUTCOME-002 | Determinism | Structural — single-step game | N/A |
| FI-CRASH-DETERMINISM-003 | Determinism | S3, Step 6 (data-driven) | Pass |
| FI-ISO-001 | Isolation | S2, Step 13 (simulation) | Pass |
| FI-ISO-002 | Isolation | Structural — global outcome model | Pass |
| FI-PAYOUT-001 | Payout | API probe | Flag |
| FI-PAYOUT-002 | Payout | API probe | Pass |
| FI-CRASH-EDGE-001 | House Edge | S4, Step 12 (analytical) | Pass |
| FI-CRASH-STAT-001 | Distribution | S4, Steps 13–14 (simulation) | Pass |
5.4Additional Integrity Evidence (S1–S4)7 records
| Property | Source | Finding |
|---|---|---|
| 1,100 / 1,100 seed hashes verified | S1, Step 1 | Commit-reveal chain intact |
| 1,100 / 1,100 positive commitment margins | S1, Step 2 | Pre-commitment guarantee holds (min 0.404s) |
| 1,100 / 1,100 drand signatures match public chain | S2, Step 15 | External entropy verifiably authentic |
| 1,100 / 1,100 exact crash-point parity | S2, Step 5 | No post-RNG conditional logic, no hidden entropy |
| Anti-circularity proven for 11 cashout targets | S4, Step 12 | 0.1% distribution edge from first principles |
| Pass 2: return z 0.286, rank-sum z 0.160 (against −3.291) | S4, Step 14 | No seed pre-selection bias |
| Fisher's combined p = 0.5382 across 10 × 500K streams | S4, Step 13 | Distribution matches theoretical at scale |
5.5Scope
This certification covers the 16 standard fairness integrity tests listed above — the minimum required to verify that the provably fair implementation holds up under non-standard conditions, adapted to Crash's dual-entropy architecture. This is not a penetration test. It focuses specifically on the provably fair implementation — not the operator's broader platform security.
Standard scope: The 16 tests above are our standard Crash fairness integrity matrix. The base list is applied to every game we audit, with per-game adaptations where a test does not apply (e.g. replay protection is N/A for single-step games) or where the architecture requires different probes (Crash uses a dual-entropy model — server seed + drand beacon — and a WebSocket transport, so client-seed and REST tests are replaced with WebSocket-event tests and bet-timing tests against the drand beacon).
Single-account scope: Tests were conducted from a single auditor account. Cross-player consistency (all users seeing the same crash point per round) is verified architecturally via RNG code path, not empirically through multi-account capture.
No infrastructure testing: Server security, network-level protections and operational controls fall under platform-level security, not game-level fairness, and sit outside this certification.
Point-in-time: Results apply to the game configuration and codebase at the time of audit. Post-audit changes require re-certification.
5.6Reproduction InstructionsRun locally
Data-driven tests (13 of 16): Fully reproducible from the open-source repo. These tests run against the captured 1,100-round dataset and produce deterministic results.
API probe tests (2 of 16): Verified by issuing live adversarial bets via the WebSocket transport against the running game. Per-test evidence (WebSocket events, server-assigned bet IDs, round IDs, accepted/dropped status, stored auto_cashout_multiplier, injected-field-leak flags, drand round IDs) is retained in our private adversarial-testing archive and summarised in the integrity test review document. The testing harness itself is kept private so it can't be reused against the game.
git clone https://github.com/ProvablyFair-org/duel-crash.gitcd duel-crash && git checkout v1.2.1 && npm cinpm run verifyConsole lines for the S5-related steps, as run (→ the tests they decide):
✓ Step 1: Seed Hash Integrity → FI-CRASH-SEED-001
✓ Step 2: drand Bet Timing (Bet Before Beacon) → FI-CRASH-TIMING-001
✓ Step 3: drand Round Monotonicity → FI-CRASH-TIMING-002
✓ Step 4: Server Seed Uniqueness → FI-CRASH-SEED-003
✓ Step 5: Outcome Recomputation → FI-CRASH-SEED-004, FI-OUTCOME-001
✓ Step 6: Bet-Size Invariance → FI-CRASH-DETERMINISM-003
✓ Step 12: Anti-Circularity → FI-CRASH-EDGE-001
✓ Step 13: Simulation Pass 1 → FI-ISO-001, FI-CRASH-STAT-001
✓ Step 14: Simulation Pass 2 (Casino Seeds) → FI-CRASH-STAT-001
✓ Step 15: drand API Signature Verification → FI-CRASH-SEED-002
✓ Step 16: Configuration Coverage (auto-cash-out target) → FI-CRASH-EDGE-001Statistical Quality Test (FI-CRASH-SEED-005):
// FI-CRASH-SEED-005: Server-seed byte distribution quality// Runs on the 1,100 revealed server seeds from data/crash-master-1100rounds.json//// Three sub-checks (all PASS thresholds):// 1. Byte-value chi² across 256 buckets — pass if p ≥ 0.01// 2. Shannon entropy (bits/byte) — pass if H > 7.9// 3. Round-order × first-byte Spearman — pass if |ρ| < 0.1 AND p ≥ 0.01//// Observed:// 1. χ² = 240.0145, p = 0.7413 ✓// 2. H = 7.99506 bits/byte ✓// 3. ρ = −0.0003, p = 0.9929 ✓//// Overall: PASSAPI Probe Tests (completed):
[PASS] FI-CRASH-SEED-004 — Commit-reveal hash chain → 10/10 SHA-256(server_seed) matched committed hash[FLAG] FI-PAYOUT-001 — Auto-cashout upper bound → 2/2 controls OK; 2/2 above-max (>4.29B×) accepted — no upper bound — disclosed[PASS] FI-PAYOUT-002 — Field injection handling → 0 injected fields reflected; auto_cashout_multiplier stored correctlyPlayer Verification
Can a player verify their own bets without trusting anyone?
Every Crash round can be reproduced from the inputs in its Provably Fair panel: the revealed server seed, the drand round and its signature. Save the round's server seed hash before you bet; after the crash, check it, the beacon and the crash point. This section walks through the steps and gives scripts that run on your own machine.
Independent Round Verification
Key principles
- Every Crash round reproduces from public inputs — no private backend data
- Save the round's server seed hash before you bet: a match shows consistency, your saved copy shows timing
- The drand beacon can be checked against the public quicknet chain at api.drand.sh
- Duel's Verify tab and the ProvablyFair.org verifier both recompute the crash point
What you need
- Server Seed Hashed — save it before you bet
- Server Seed — revealed after the round ends
- Drand Round ID — the quicknet beacon round the game round used
- Drand Randomness — the beacon's BLS signature, public at api.drand.sh
- Every Crash round reproduces from public inputs — no private backend data
- Save the round's server seed hash before you bet: a match shows consistency, your saved copy shows timing
- The drand beacon can be checked against the public quicknet chain at api.drand.sh
- Duel's Verify tab and the ProvablyFair.org verifier both recompute the crash point
- Server Seed Hashed — save it before you bet
- Server Seed — revealed after the round ends
- Drand Round ID — the quicknet beacon round the game round used
- Drand Randomness — the beacon's BLS signature, public at api.drand.sh
Player can access every inputPass
External entropy verifiablePass
Verification steps documentedPass
Independent verifierPass
Manual recomputationPass
No hidden stepsPass
Every input is shown in the round's Provably Fair panel, and the beacon can be checked against the public chain. The crash point recomputes from those inputs alone. Save the hash before you bet: a match then shows the seed is the one you were committed to.
- 1
Save the Hash Before You Bet
Before you bet, save the Server Seed Hashed for the round you are about to play, with the time you saved it: a screenshot or a copied note. Our capture did not record whether or when Duel shows it before the round starts. Your saved copy is what shows the commitment came before your bet; the panel after the crash cannot show that.
- 2
Copy the Values After the Crash
Open the round's Provably Fair panel (the shield icon on the Crash screen). Copy the Round ID, Server Seed Hashed, Server Seed, Drand Round ID and Drand Randomness, and note when you placed your bet.
- 3
Check the Hash
SHA-256(hex_decode(serverSeed))must equal the hash you saved before betting. Hash the 32 decoded bytes, not the 64-character text. A match shows the revealed seed is the one behind your saved commitment. - 4
Check the drand Beacon
Open
api.drand.sh/v2/beacons/quicknet/rounds/{Drand Round ID}. Itssignaturemust equal the Drand Randomness, and the beacon published at1692803367 + (round − 1) × 3seconds — after your bet. - 5
Recompute & Match
Recompute the crash point with the ProvablyFair.org verifier, Duel's Verify tab or the scripts below. Your bet wins if the crash point is at or above your target; the wins looked up in the wallet ledger were credited
stake × target.
Verify a real bet, step by stepVerify a real bet · Swipe for all 4 steps →
Verify with ProvablyFair.org
Recompute any Crash round from its revealed seed and drand beacon, independently of the casino. The audit package pins this verifier and runs it on all 1,100 captured rounds.
Open independent verifier
Built-in verification
The operator’s own verification page. This tool is controlled by Duel.com.
Open Duel verifier
Visual Walkthroughstep-by-step

Save the round's Server Seed Hashed before you bet (step 1 above). Then set your stake and auto cash-out target and place the bet. The crash point comes from the committed seed and a drand beacon published after your bet.
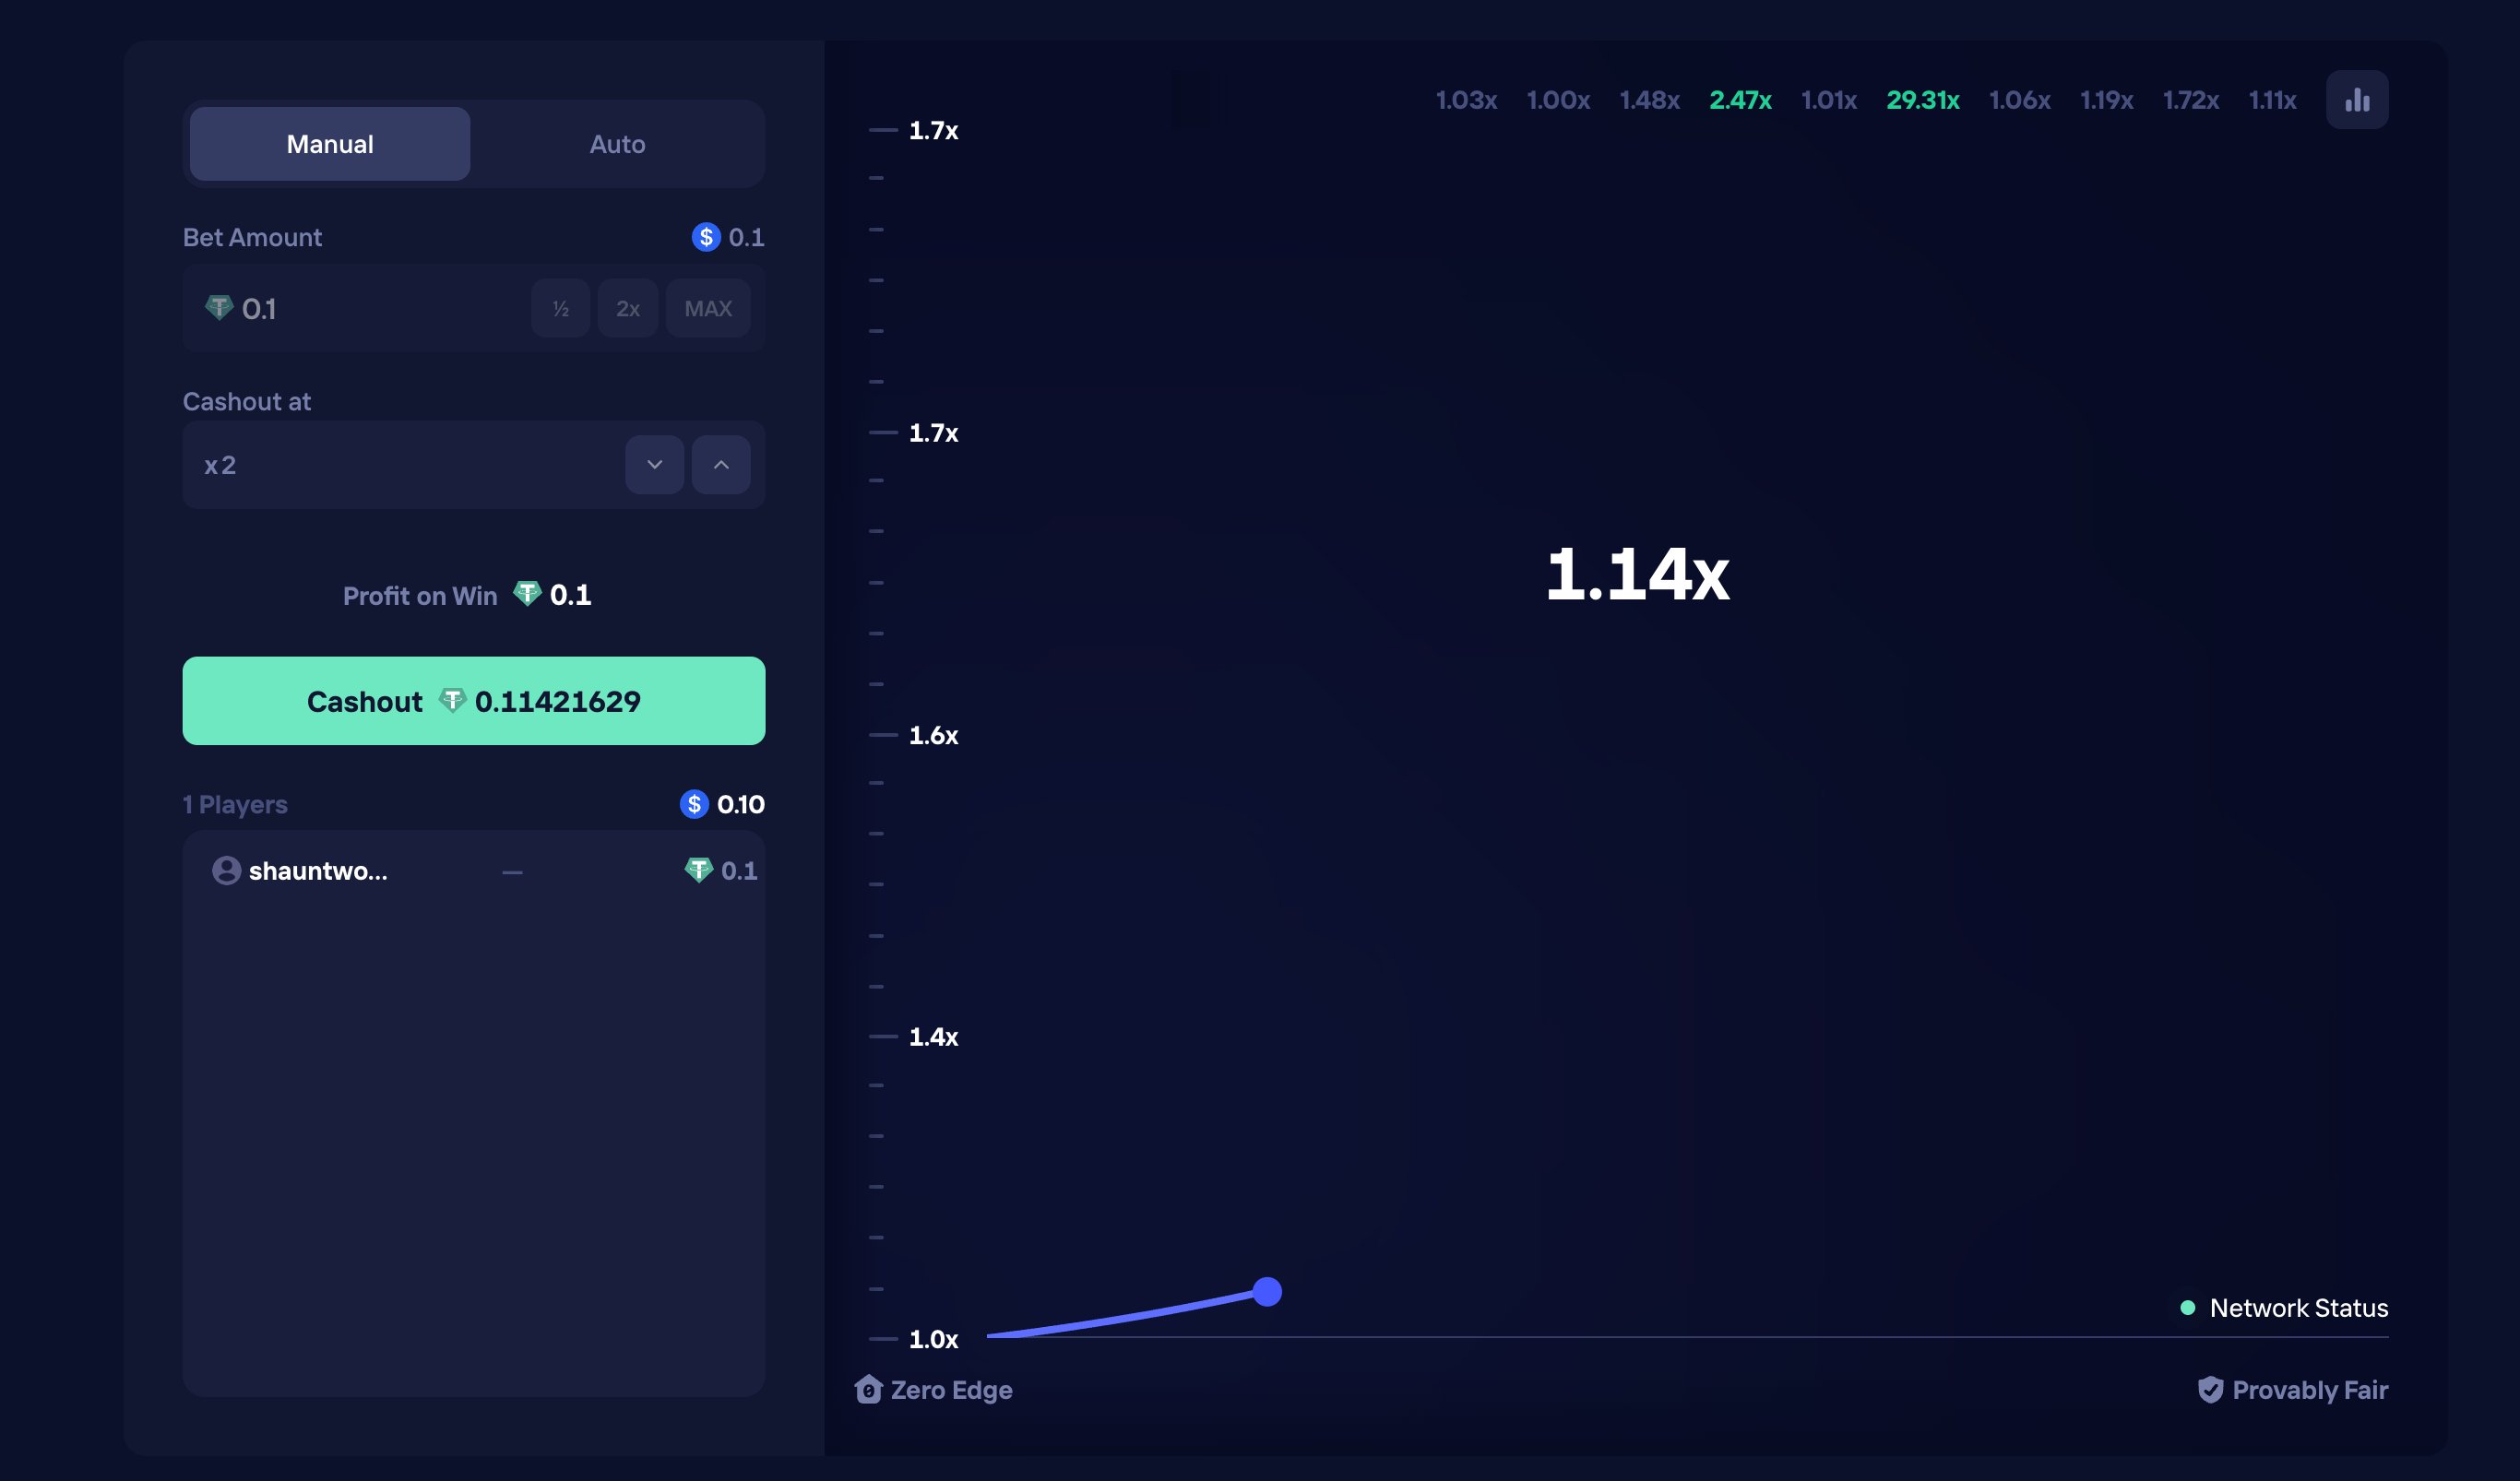
Duel.com Crash: bet amount, cash-out target and the multiplayer player list, with the Provably Fair link at the bottom right.
After the round crashes, open its Provably Fair panel. It shows every input the crash point needs. Every player in the round verifies against the same pair of server seed and beacon.
Server Seed Hashed — SHA-256 of the 32 decoded seed bytes: the commitment. Compare it with the copy you saved before betting.
Server Seed — the revealed seed. Hash it to check it against the commitment.
Drand Round ID — the quicknet beacon round the game round used.
Drand Randomness — the beacon's 48-byte BLS signature (96 hex characters), published by the drand chain on its fixed schedule.
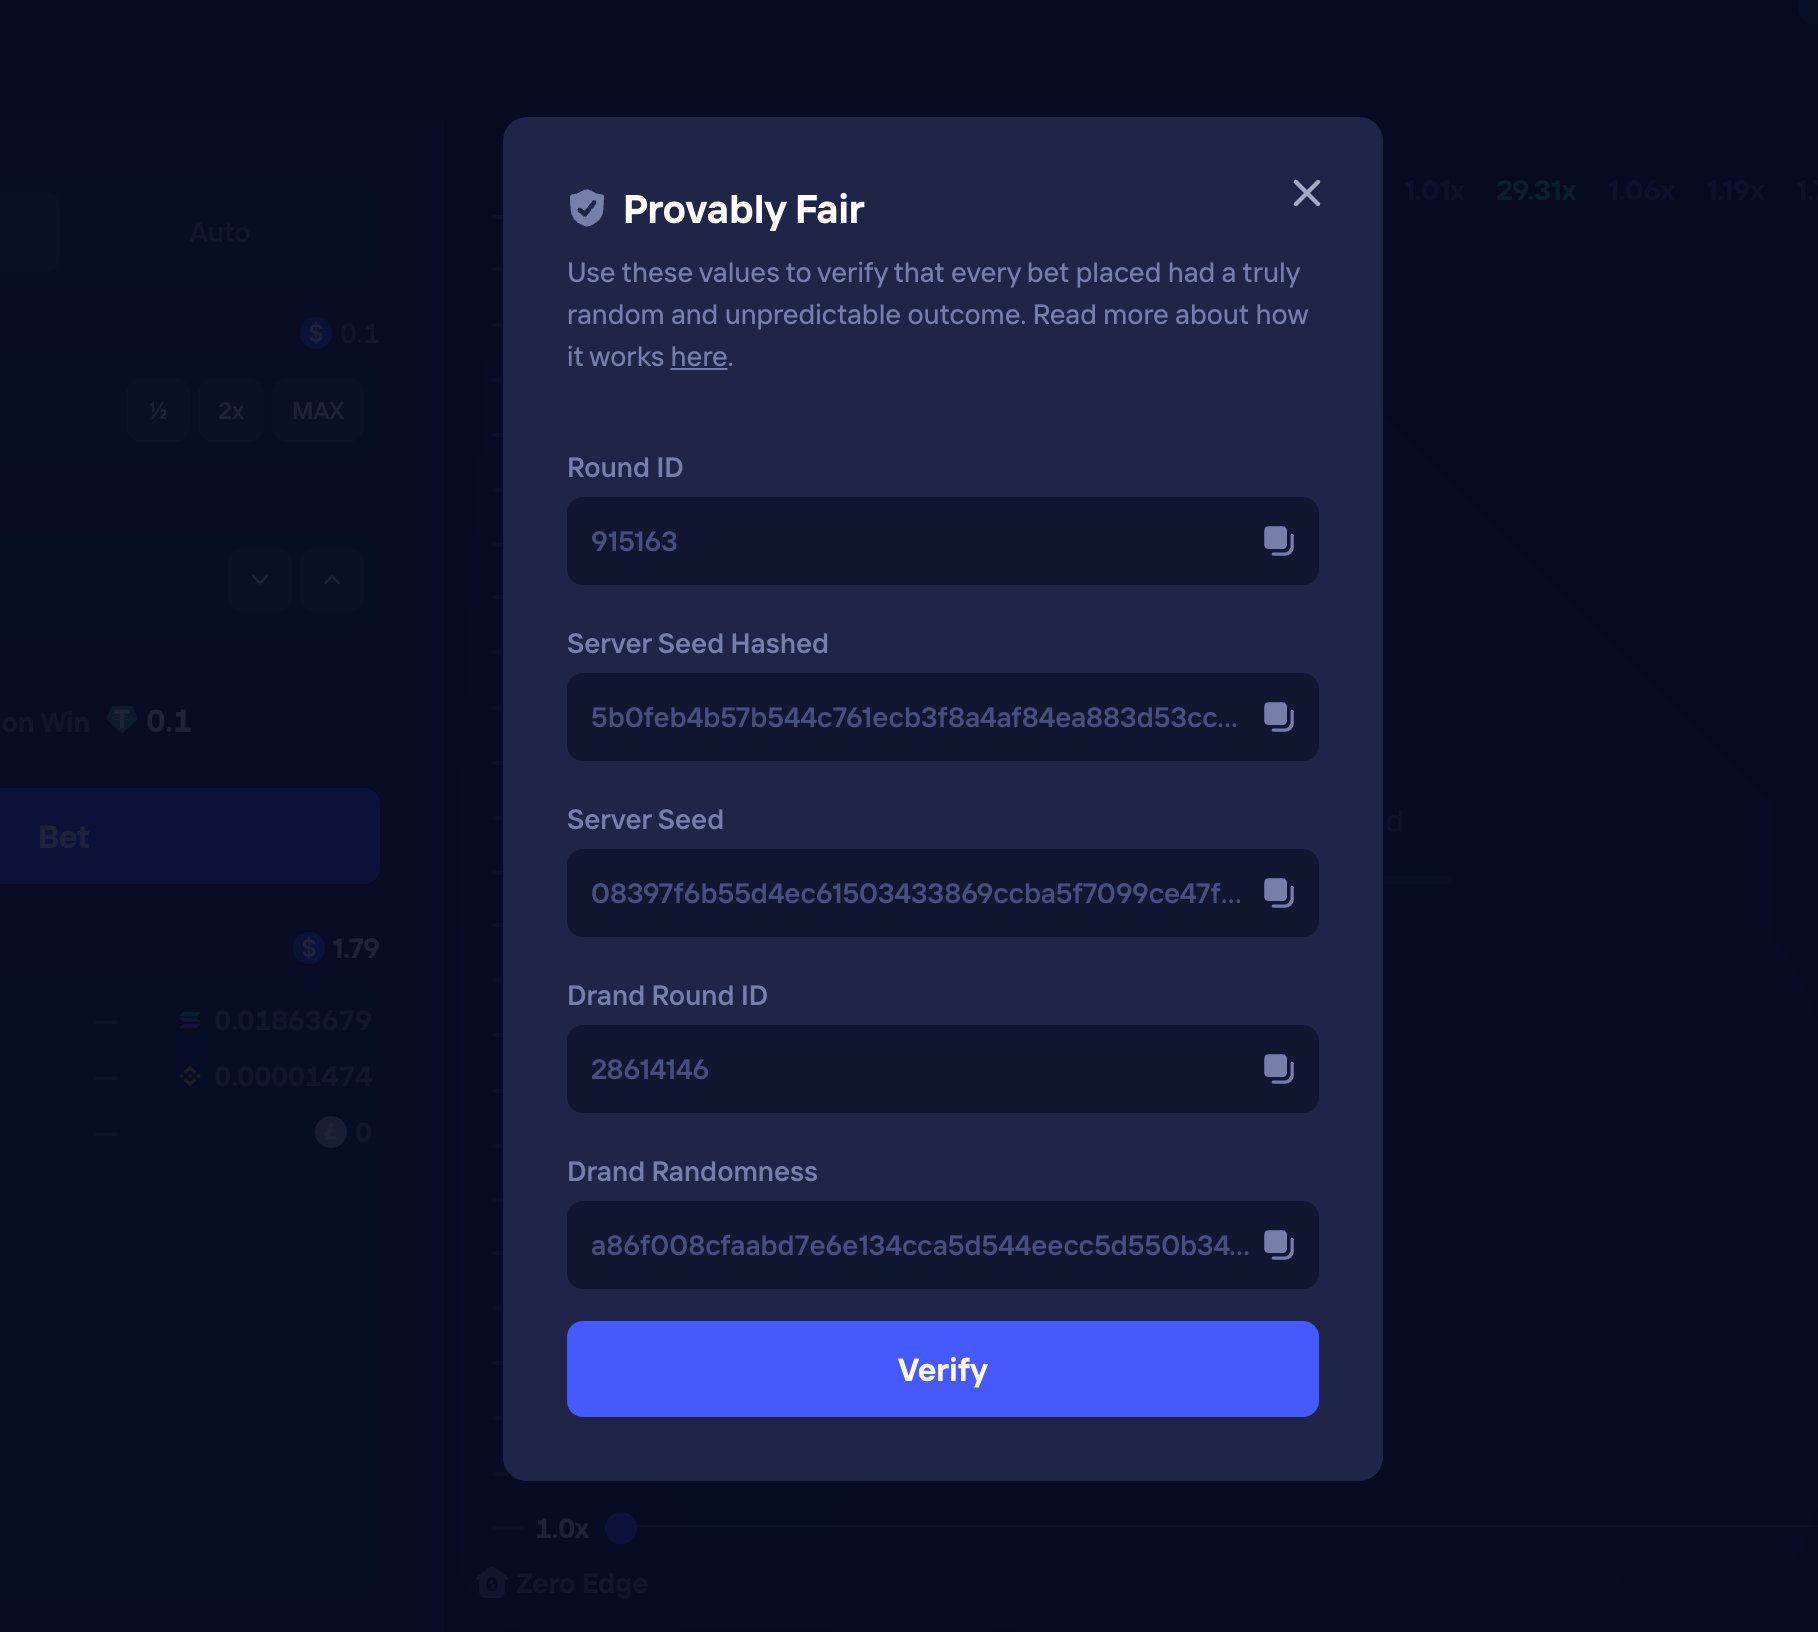
Crash Provably Fair panel: Round ID, Server Seed Hashed, Server Seed, Drand Round ID, Drand Randomness and the Verify button.
Click Verify in the panel to open the Provably Fair page with the drand seed and server seed filled in. The page recomputes the crash point and shows it as the Game Result. A result equal to your round's crash point, with a revealed seed that matches your saved hash, shows the round is consistent with its commitment. Duel's Verify-tab code agreed with every captured round; the ProvablyFair.org verifier gives an independent check.
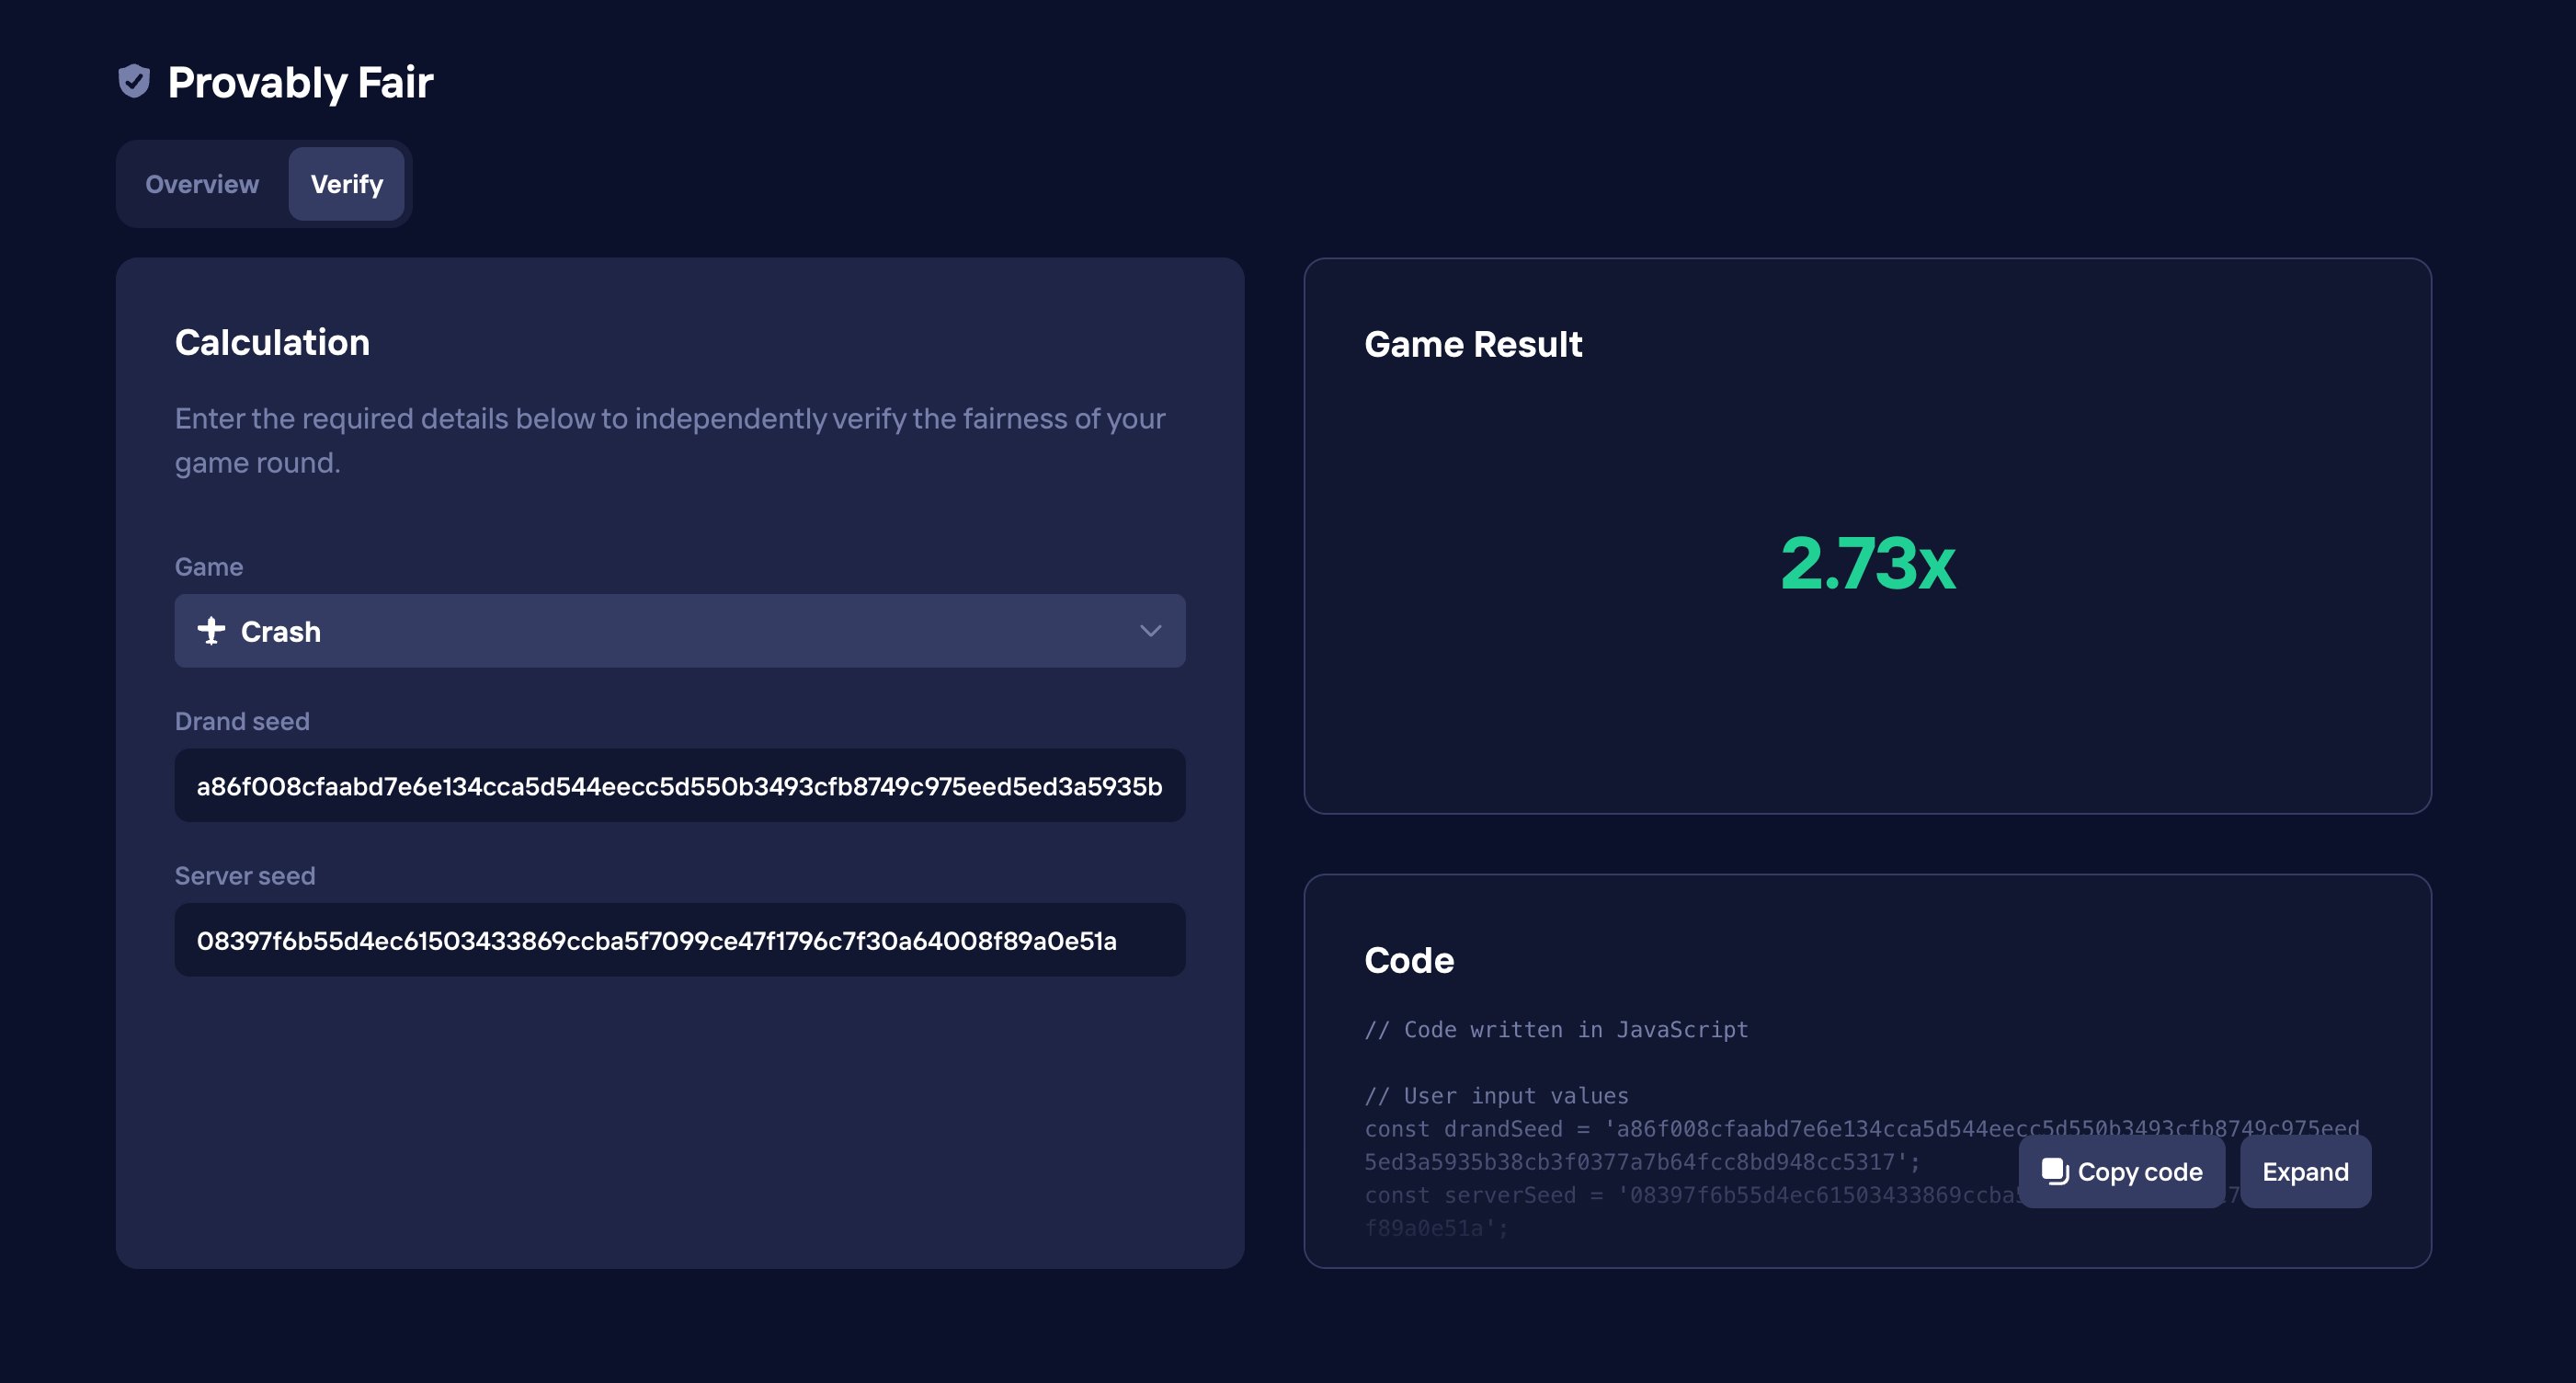
Duel's Provably Fair page, Verify tab: Game Crash, drand seed and server seed filled in, the Game Result, and the code panel.
Open https://api.drand.sh/v2/beacons/quicknet/rounds/{drandRoundId}, using the Drand Round ID from the panel. The signature in the response must equal the Drand Randomness exactly. drand is a public beacon run by an independent network; its publication time, 1692803367 + (round − 1) × 3 seconds, should be after your bet.
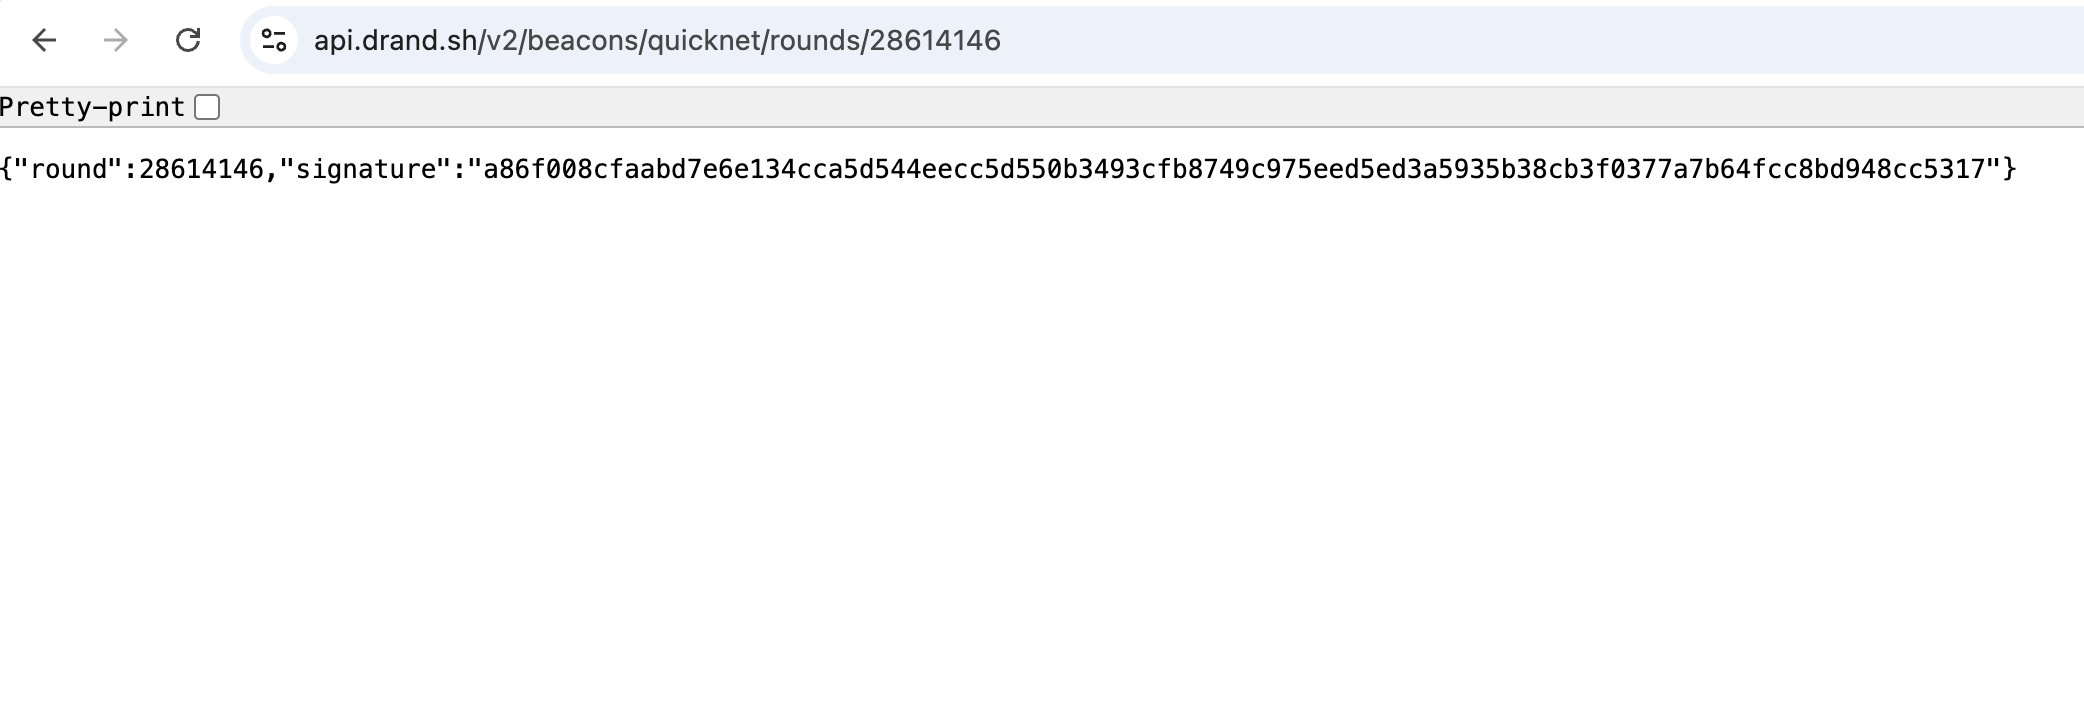
Public drand API response: the round number and its BLS signature, fetched directly from api.drand.sh.
Manual Verification (Advanced)6 sections
6.5Why Manual Verification Matters
Manual verification means you don't rely on any casino-provided tool. You run the calculation on your own machine, rule out a tampered verifier, and see exactly how the result is produced.
6.6How the Algorithm Works (Plain English)
Each round's crash point comes from two inputs:
- The server seed — chosen by the casino, committed by its hash, revealed after the crash
- The drand signature — published by the drand quicknet network for the round's drand round
HMAC-SHA256 combines them: the seed bytes are the key, and the drand bytes read as UTF-8 text plus :0 are the message. The first 4 bytes of the result are a number v from 0 to 4,294,967,295, and the crash point is floor(999 × 2³² / (10 × (v + 1))) hundredths, at least 1.00. The casino does not choose the beacon's value, and a seed that matches the hash you saved before betting is the seed you were committed to.
6.7Casino Verifier vs ProvablyFair.org Verifier4 records
Two verification tools are available. Both should give identical results; if they don't, something has changed.
| Duel.com Verify tab | ProvablyFair.org Verifier | |
|---|---|---|
| Source | Casino-controlled | Independent, open source |
| Access | duel.com/provably-fair/verify | provablyfair.org/verify-bets/duel |
| Audit check | Its code, saved 26 September 2026, run unmodified on all 1,100 rounds | Pinned by SHA-256 and run on all 1,100 rounds |
| Change detection | None | A changed file no longer matches its pin |
6.8JavaScript Verification Script
Run with Node.js; no packages needed. The example values are round 829099 — replace them with your round's:
const crypto = require('crypto'); // Commitment: SHA-256 of the 32 decoded seed bytes, not of the 64-character text.function verifyHash(serverSeed, serverSeedHash) { const h = crypto.createHash('sha256').update(Buffer.from(serverSeed, 'hex')).digest('hex'); return h === serverSeedHash.toLowerCase();} // Crash point in exact integers (docs/ALGORITHM.md §2).function crashPoint(serverSeed, drandRandomness) { const key = Buffer.from(serverSeed, 'hex'); // 32 bytes const text = new TextDecoder('utf-8', { ignoreBOM: true }) .decode(Buffer.from(drandRandomness, 'hex')); // 48 bytes, lossy UTF-8 const message = Buffer.concat([Buffer.from(text, 'utf8'), Buffer.from(':0')]); const v = crypto.createHmac('sha256', key).update(message).digest().readUInt32BE(0); const cents = (999n * 2n ** 32n) / (10n * BigInt(v + 1)); // floor, exact return Math.max(1, Number(cents) / 100);} // drand quicknet: when a beacon round was published (Unix seconds).const publishedAt = round => 1692803367 + (round - 1) * 3; // Replace with your round's values (example: round 829099, auto cash-out 1.5×)const savedHash = '706bb90b571c6165c96a484580efd2f834b4f3237e7cf0f2680b26b7f4e151c0';const serverSeed = '3c9c71aa9ffa2691d29fd754cb0caf8ce1fa87d57804196967de81088fab1d23';const drandRoundId = 27798178;const drandRandomness = 'b18fa6dc92304844fc4e868d708953e6b628b3f88d4381249d32264df1bfe5bc20aa0905e57fe54063010881767fd56d';const target = 1.5; const cp = crashPoint(serverSeed, drandRandomness);console.log('Commitment:', verifyHash(serverSeed, savedHash) ? 'MATCH' : 'NO MATCH');console.log('Beacon published:', new Date(publishedAt(drandRoundId) * 1000).toISOString());console.log('Crash point:', cp.toFixed(2) + '×');console.log('Bet:', cp >= target ? `WIN — credited stake × ${target}` : 'LOSS');Output for the example round:
Commitment: MATCH
Beacon published: 2026-04-14T20:18:18.000Z
Crash point: 2.81×
Bet: WIN — credited stake × 1.56.9Python Verification Script
The same check in Python 3, standard library only:
import hashlib, hmacfrom datetime import datetime, timezone # Commitment: SHA-256 of the 32 decoded seed bytes, not of the 64-character text.def verify_hash(server_seed, server_seed_hash): return hashlib.sha256(bytes.fromhex(server_seed)).hexdigest() == server_seed_hash.lower() # Crash point in exact integers (docs/ALGORITHM.md §2).def crash_point(server_seed, drand_randomness): key = bytes.fromhex(server_seed) # 32 bytes text = bytes.fromhex(drand_randomness).decode('utf-8', errors='replace') # 48 bytes, lossy UTF-8 message = text.encode('utf-8') + b':0' v = int.from_bytes(hmac.new(key, message, hashlib.sha256).digest()[:4], 'big') cents = (999 * 2**32) // (10 * (v + 1)) # floor, exact return max(100, cents) / 100 # drand quicknet: when a beacon round was published.def published_at(round_id): return datetime.fromtimestamp(1692803367 + (round_id - 1) * 3, timezone.utc) # Replace with your round's values (example: round 829099, auto cash-out 1.5×)saved_hash = '706bb90b571c6165c96a484580efd2f834b4f3237e7cf0f2680b26b7f4e151c0'server_seed = '3c9c71aa9ffa2691d29fd754cb0caf8ce1fa87d57804196967de81088fab1d23'drand_round_id = 27798178drand_randomness = 'b18fa6dc92304844fc4e868d708953e6b628b3f88d4381249d32264df1bfe5bc20aa0905e57fe54063010881767fd56d'target = 1.5 cp = crash_point(server_seed, drand_randomness)print('Commitment:', 'MATCH' if verify_hash(server_seed, saved_hash) else 'NO MATCH')print('Beacon published:', published_at(drand_round_id).isoformat())print(f'Crash point: {cp:.2f}×')print('Bet:', f'WIN — credited stake × {target}' if cp >= target else 'LOSS')Output for the example round:
Commitment: MATCH
Beacon published: 2026-04-14T20:18:18+00:00
Crash point: 2.81×
Bet: WIN — credited stake × 1.56.10Evidence Screenshots5 records
The package's exhibits. Screenshots illustrate interface states; the recorded rounds are the evidence.
| Exhibit | Description |
|---|---|
| E08 | Crash game UI: bet controls, crash chart, round history bar and multiplayer player list |
| E09 | Duel.com Provably Fair overview page |
| E10 | Provably Fair page, Verify tab: the calculation form |
| E11 | Crash Provably Fair panel: Round ID, Server Seed Hashed, Server Seed, Drand Round ID and Drand Randomness |
| E16 | Duel's Crash Verify-tab code, saved verbatim on 26 September 2026 (SHA-256 c699cd54…) |
Verify a real bet, step by stepVerify a real bet · Swipe for all 4 steps →
How it works
- 1
Save the Hash Before You Bet
Before you bet, save the Server Seed Hashed for the round you are about to play, with the time you saved it: a screenshot or a copied note. Our capture did not record whether or when Duel shows it before the round starts. Your saved copy is what shows the commitment came before your bet; the panel after the crash cannot show that.
- 2
Copy the Values After the Crash
Open the round's Provably Fair panel (the shield icon on the Crash screen). Copy the Round ID, Server Seed Hashed, Server Seed, Drand Round ID and Drand Randomness, and note when you placed your bet.
- 3
Check the Hash
SHA-256(hex_decode(serverSeed))must equal the hash you saved before betting. Hash the 32 decoded bytes, not the 64-character text. A match shows the revealed seed is the one behind your saved commitment. - 4
Check the drand Beacon
Open
api.drand.sh/v2/beacons/quicknet/rounds/{Drand Round ID}. Itssignaturemust equal the Drand Randomness, and the beacon published at1692803367 + (round − 1) × 3seconds — after your bet. - 5
Recompute & Match
Recompute the crash point with the ProvablyFair.org verifier, Duel's Verify tab or the scripts below. Your bet wins if the crash point is at or above your target; the wins looked up in the wallet ledger were credited
stake × target.
Visual Walkthroughstep-by-step
Save the round's Server Seed Hashed before you bet (step 1 above). Then set your stake and auto cash-out target and place the bet. The crash point comes from the committed seed and a drand beacon published after your bet.
Duel.com Crash: bet amount, cash-out target and the multiplayer player list, with the Provably Fair link at the bottom right.
After the round crashes, open its Provably Fair panel. It shows every input the crash point needs. Every player in the round verifies against the same pair of server seed and beacon.
Server Seed Hashed — SHA-256 of the 32 decoded seed bytes: the commitment. Compare it with the copy you saved before betting.
Server Seed — the revealed seed. Hash it to check it against the commitment.
Drand Round ID — the quicknet beacon round the game round used.
Drand Randomness — the beacon's 48-byte BLS signature (96 hex characters), published by the drand chain on its fixed schedule.
Crash Provably Fair panel: Round ID, Server Seed Hashed, Server Seed, Drand Round ID, Drand Randomness and the Verify button.
Click Verify in the panel to open the Provably Fair page with the drand seed and server seed filled in. The page recomputes the crash point and shows it as the Game Result. A result equal to your round's crash point, with a revealed seed that matches your saved hash, shows the round is consistent with its commitment. Duel's Verify-tab code agreed with every captured round; the ProvablyFair.org verifier gives an independent check.
Duel's Provably Fair page, Verify tab: Game Crash, drand seed and server seed filled in, the Game Result, and the code panel.
Open https://api.drand.sh/v2/beacons/quicknet/rounds/{drandRoundId}, using the Drand Round ID from the panel. The signature in the response must equal the Drand Randomness exactly. drand is a public beacon run by an independent network; its publication time, 1692803367 + (round − 1) × 3 seconds, should be after your bet.
Public drand API response: the round number and its BLS signature, fetched directly from api.drand.sh.
Technical evidence
6.5Why Manual Verification Matters
Manual verification means you don't rely on any casino-provided tool. You run the calculation on your own machine, rule out a tampered verifier, and see exactly how the result is produced.
6.6How the Algorithm Works (Plain English)
Each round's crash point comes from two inputs:
- The server seed — chosen by the casino, committed by its hash, revealed after the crash
- The drand signature — published by the drand quicknet network for the round's drand round
HMAC-SHA256 combines them: the seed bytes are the key, and the drand bytes read as UTF-8 text plus :0 are the message. The first 4 bytes of the result are a number v from 0 to 4,294,967,295, and the crash point is floor(999 × 2³² / (10 × (v + 1))) hundredths, at least 1.00. The casino does not choose the beacon's value, and a seed that matches the hash you saved before betting is the seed you were committed to.
6.7Casino Verifier vs ProvablyFair.org Verifier4 records
Two verification tools are available. Both should give identical results; if they don't, something has changed.
| Duel.com Verify tab | ProvablyFair.org Verifier | |
|---|---|---|
| Source | Casino-controlled | Independent, open source |
| Access | duel.com/provably-fair/verify | provablyfair.org/verify-bets/duel |
| Audit check | Its code, saved 26 September 2026, run unmodified on all 1,100 rounds | Pinned by SHA-256 and run on all 1,100 rounds |
| Change detection | None | A changed file no longer matches its pin |
6.8JavaScript Verification Script
Run with Node.js; no packages needed. The example values are round 829099 — replace them with your round's:
const crypto = require('crypto'); // Commitment: SHA-256 of the 32 decoded seed bytes, not of the 64-character text.function verifyHash(serverSeed, serverSeedHash) { const h = crypto.createHash('sha256').update(Buffer.from(serverSeed, 'hex')).digest('hex'); return h === serverSeedHash.toLowerCase();} // Crash point in exact integers (docs/ALGORITHM.md §2).function crashPoint(serverSeed, drandRandomness) { const key = Buffer.from(serverSeed, 'hex'); // 32 bytes const text = new TextDecoder('utf-8', { ignoreBOM: true }) .decode(Buffer.from(drandRandomness, 'hex')); // 48 bytes, lossy UTF-8 const message = Buffer.concat([Buffer.from(text, 'utf8'), Buffer.from(':0')]); const v = crypto.createHmac('sha256', key).update(message).digest().readUInt32BE(0); const cents = (999n * 2n ** 32n) / (10n * BigInt(v + 1)); // floor, exact return Math.max(1, Number(cents) / 100);} // drand quicknet: when a beacon round was published (Unix seconds).const publishedAt = round => 1692803367 + (round - 1) * 3; // Replace with your round's values (example: round 829099, auto cash-out 1.5×)const savedHash = '706bb90b571c6165c96a484580efd2f834b4f3237e7cf0f2680b26b7f4e151c0';const serverSeed = '3c9c71aa9ffa2691d29fd754cb0caf8ce1fa87d57804196967de81088fab1d23';const drandRoundId = 27798178;const drandRandomness = 'b18fa6dc92304844fc4e868d708953e6b628b3f88d4381249d32264df1bfe5bc20aa0905e57fe54063010881767fd56d';const target = 1.5; const cp = crashPoint(serverSeed, drandRandomness);console.log('Commitment:', verifyHash(serverSeed, savedHash) ? 'MATCH' : 'NO MATCH');console.log('Beacon published:', new Date(publishedAt(drandRoundId) * 1000).toISOString());console.log('Crash point:', cp.toFixed(2) + '×');console.log('Bet:', cp >= target ? `WIN — credited stake × ${target}` : 'LOSS');Output for the example round:
Commitment: MATCH
Beacon published: 2026-04-14T20:18:18.000Z
Crash point: 2.81×
Bet: WIN — credited stake × 1.56.9Python Verification Script
The same check in Python 3, standard library only:
import hashlib, hmacfrom datetime import datetime, timezone # Commitment: SHA-256 of the 32 decoded seed bytes, not of the 64-character text.def verify_hash(server_seed, server_seed_hash): return hashlib.sha256(bytes.fromhex(server_seed)).hexdigest() == server_seed_hash.lower() # Crash point in exact integers (docs/ALGORITHM.md §2).def crash_point(server_seed, drand_randomness): key = bytes.fromhex(server_seed) # 32 bytes text = bytes.fromhex(drand_randomness).decode('utf-8', errors='replace') # 48 bytes, lossy UTF-8 message = text.encode('utf-8') + b':0' v = int.from_bytes(hmac.new(key, message, hashlib.sha256).digest()[:4], 'big') cents = (999 * 2**32) // (10 * (v + 1)) # floor, exact return max(100, cents) / 100 # drand quicknet: when a beacon round was published.def published_at(round_id): return datetime.fromtimestamp(1692803367 + (round_id - 1) * 3, timezone.utc) # Replace with your round's values (example: round 829099, auto cash-out 1.5×)saved_hash = '706bb90b571c6165c96a484580efd2f834b4f3237e7cf0f2680b26b7f4e151c0'server_seed = '3c9c71aa9ffa2691d29fd754cb0caf8ce1fa87d57804196967de81088fab1d23'drand_round_id = 27798178drand_randomness = 'b18fa6dc92304844fc4e868d708953e6b628b3f88d4381249d32264df1bfe5bc20aa0905e57fe54063010881767fd56d'target = 1.5 cp = crash_point(server_seed, drand_randomness)print('Commitment:', 'MATCH' if verify_hash(server_seed, saved_hash) else 'NO MATCH')print('Beacon published:', published_at(drand_round_id).isoformat())print(f'Crash point: {cp:.2f}×')print('Bet:', f'WIN — credited stake × {target}' if cp >= target else 'LOSS')Output for the example round:
Commitment: MATCH
Beacon published: 2026-04-14T20:18:18+00:00
Crash point: 2.81×
Bet: WIN — credited stake × 1.56.10Evidence Screenshots5 records
The package's exhibits. Screenshots illustrate interface states; the recorded rounds are the evidence.
| Exhibit | Description |
|---|---|
| E08 | Crash game UI: bet controls, crash chart, round history bar and multiplayer player list |
| E09 | Duel.com Provably Fair overview page |
| E10 | Provably Fair page, Verify tab: the calculation form |
| E11 | Crash Provably Fair panel: Round ID, Server Seed Hashed, Server Seed, Drand Round ID and Drand Randomness |
| E16 | Duel's Crash Verify-tab code, saved verbatim on 26 September 2026 (SHA-256 c699cd54…) |
Every input is shown in the round's Provably Fair panel, and the beacon can be checked against the public chain. The crash point recomputes from those inputs alone. Save the hash before you bet: a match then shows the seed is the one you were committed to.
Reproducibility & Artifacts
Can anyone independently reproduce every finding in this audit?
Everything in this audit reproduces from the open-source release v1.2.1. Check it out and run npm test: every step re-runs offline and is compared with the committed results. The repository is the credential, not this report.

Open-Source Audit Repository
Repository Details
- GitHub: ProvablyFair-org/duel-crash
- Release: v1.2.1 (Framework 1.1)
- Original audit: commit f97d5b8, 4 June 2026
- Public Verifier: provablyfair.org/verify-bets/duel
Prerequisites
- Node.js 22.x (pinned by
.nvmrc) - npm 9 or later
- Git
- Network only for
npm ciandnpm run timing
- GitHub: ProvablyFair-org/duel-crash
- Release: v1.2.1 (Framework 1.1)
- Original audit: commit f97d5b8, 4 June 2026
- Public Verifier: provablyfair.org/verify-bets/duel
- Node.js 22.x (pinned by
.nvmrc) - npm 9 or later
- Git
- Network only for
npm ciandnpm run timing
Check out v1.2.1 and run npm test: every step re-runs offline and the result is compared with the committed one. The dataset hash pins the 1,100 rounds, and all six files of record are hashed in RELEASE-MANIFEST.json.

Commands to Reproduce
Check out the release tag and install the pinned dependencies (Node 22.x).
git clone https://github.com/ProvablyFair-org/duel-crash.gitcd duel-crashgit checkout v1.2.1npm ci19 unit tests, then the 18 scored steps offline, with both simulation passes replayed from their seeds. The run writes to outputs/run/, is compared with the committed results, and exits 0. Each step also prints a one-line finding, omitted below; the findings are in outputs/run/verification-results.json.
npm test> duel-crash-audit@1.2.1 test> mocha && npm run verify Crash RNG ✔ should compute crash points for 5 known test vectors ✔ should produce raw crash >= 1.0 ✔ computeCrashPoint should floor to 2 decimal places Hash Verification ✔ should verify SHA-256(hex_bytes(serverSeed)) === serverSeedHash ✔ should reject wrong hash Survival Probability & RTP ✔ P(crash >= 1.0) should be 1.0 ✔ P(crash >= 2.0) should be ~0.4995 ✔ P(crash >= 100.0) should be ~0.00999 ✔ RTP for cashout target 2x should be ~0.999 ✔ RTP for any target should be <= 0.999 ✔ instant crash probability is exactly 46,776,872 / 2^32 (1.0891%) Statistics ✔ chi-squared p-value for known values ✔ regularized gamma P(1, 1) ≈ 0.6321 ✔ chi-squared test with pooling ✔ lag-1 autocorrelation on independent data near zero Second check — Duel's own Crash Verify-tab code, executed with only its inputs filled in (pasted 2026-09-26) ✔ the vendored operator file and its runner hash to their pins, the code ran, and as shipped it printed only its empty-input message ✔ fixed vectors: the operator code's displayed crash point equals the known crash point and src/rng.ts computeCrashPoint ✔ every captured round: the operator code's displayed crash point equals the served crash point and src/rng.ts computeCrashPoint (1,100/1,100) Spec self-test — docs/ALGORITHM.md against src/rng.ts (clean-room, 20 Oct 2026) NOTE spec §2 Step 3 labels: spec says seed=ab/drand=00 -> 3.21; seed-as-key gives 7.15 ✔ all 87 spec checks pass 19 passing (4s) > duel-crash-audit@1.2.1 verify> ts-node tests/verify.ts Dataset hash check: Expected: ea62337a8665842ad33341a7d1b435d0c986f9feb3b03609cb0b0c868f3ef58a Actual: ea62337a8665842ad33341a7d1b435d0c986f9feb3b03609cb0b0c868f3ef58a Status: MATCH ✓ ══════════════════════════════════════════════════════════ CRASH AUDIT — VERIFICATION SUITE══════════════════════════════════════════════════════════ Dataset: 1100 rounds | 2026-04-14T20:17:12.676Z → 2026-04-15T14:21:25.365Z Phase A: 800 Phase B: 200 Phase C: 100 ── Scored Steps ── ✓ Step 1: Seed Hash Integrity ✓ Step 2: drand Bet Timing (Bet Before Beacon) ✓ Step 3: drand Round Monotonicity ✓ Step 4: Server Seed Uniqueness ✓ Step 5: Outcome Recomputation ✓ Step 6: Bet-Size Invariance ✓ Step 7: Payout Math ✓ Step 8: House Edge Audit ✓ Step 9: Phase Coverage ✓ Step 10: Dataset Hash ✓ Step 11: drand Chain Formula ✓ Step 12: Anti-Circularity ✓ Step 13: Simulation Pass 1 ✓ Step 14: Simulation Pass 2 (Casino Seeds) ✓ Step 15: drand API Signature Verification ✓ Step 16: Configuration Coverage (auto-cash-out target) ✓ Step 17: Artifact Integrity (pinned artifacts of record) ✓ Step 18: Live-Sample Fit (informational) ── Informational Context (live-bet stats — not scored) ── ┌─────────────────────────────────────────────────────────────┐ │ Instant crash rate │ 8/1100 (0.73%) — expected ~12.0 (1.09%) │ Live RTP @ 1.1x (n=51) │ 94.81% — informational only (simulation is authoritative) │ Live RTP @ 1.5x (n=800) │ 101.71% — informational only (simulation is authoritative) │ Live RTP @ 2x (n=149) │ 97.90% — informational only (simulation is authoritative) │ Live RTP @ 5x (n=50) │ 69.93% — informational only (simulation is authoritative) │ Live RTP @ 10x (n=50) │ 79.92% — informational only (simulation is authoritative) │ Overall win rate │ 671/1100 (61.00%) │ Crash point range │ min=1, median=1.96, max=13664.99 └─────────────────────────────────────────────────────────────┘ rtp-claim: ENFORCED — PASS rtp-claim: claim flat 99.900000% — source: fairness page: houseEdge = 0.001 in the code panel of the Verify tab on Duel's Provably Fair page (Provably Fair → Verify, game Crash; evidence/verify-tab/duel-verify-tab-crash-2026-09-26.js L63, E16, pasted 2026-09-26), and effectiveEdge 0.1 served on all 1,100 rounds (Step 7; MANIFEST.md#payouts-and-rtp; declaration gameModel.edge.claimed 0.001) rtp-claim: band ±0.10 pp · 9,999,900 settings · true min 99.899768% (cashout=9999.05) · true max 99.900000% (cashout=1.03) rtp-claim: house side beyond band: 0 · player-favourable beyond band: 0 · worst cashout=9999.05 at -0.000232 pp rtp-claim: outcome PASS · minimal fix: none — the claim holds for every setting it states a figure for rtp-claim: committed table outputs/rtp-claim-table.json: equals this run; sha256 a80f359c34cd0dab… matches the pin══════════════════════════════════════════════════════════ Passed: 18/18 VERDICT: PROVABLY FAIR — Full Pass══════════════════════════════════════════════════════════ → outputs/run/verification-results.json written Committed artifact NOT modified. Reproduction vs the committed artifact on Node 22.22.0: REPRODUCED Diff written to: outputs/run/diff.jsonRegenerates the simulation into outputs/run/, then verifies and diffs it against the pinned artifact.
npm run test:fullRe-checks the chain formula and margins, and re-fetches all 1,100 signatures from api.drand.sh into outputs/run/.
npm run timingChecks every artifact hash in RELEASE-MANIFEST.json, and the dataset hash on its own.
node scripts/release-manifest.mjs --checkshasum -a 256 data/crash-master-1100rounds.json# ea62337a8665842ad33341a7d1b435d0c986f9feb3b03609cb0b0c868f3ef58aAudit Reproducibility Pinning
- Release
v1.2.1· Framework 1.1- Original Audit
f97d5b8baf234a61ca8ca9441cb6220fbf6647c7· 4 June 2026- Node Version
- 22.x (
.nvmrc,engines) - Dataset
- data/crash-master-1100rounds.json (1,100 rounds, 3 phases)
- Dataset Hash (SHA-256)
- ea62337a8665842ad33341a7d1b435d0c986f9feb3b03609cb0b0c868f3ef58a
- Runtime
npm test: 78 s on an Apple M2 Max (Node 22.23.1)- Mutation Battery
- 43 / 43 mutations killed; every scored step has one that kills it
- Release Signature
- SHA256:gEujiJm2pRyq7lQsfYQfQ1r97H/J7GdaKHbOW8GtikY
- Audit Date
- April 2026 (capture 14–15 April 2026)
- Audit ID
- PF-2026-DL05
Output Artifacts6 files of record
| File | Contents | SHA-256 |
|---|---|---|
| data/crash-master-1100rounds.json | 1,100 live rounds, phases A–C | ea62337a8665842ad33341a7d1b435d0c986f9feb3b03609cb0b0c868f3ef58a |
| outputs/verification-results.json | All 18 step results, the verdict and the profile labels; every run is compared with it | 2ded53b275fe2086324a8d4b6583d16927d906f71e141e527bb578010252c504 |
| outputs/rtp-claim-table.json | RTP claim table: extremes and per-decade results, every 0.01 target to 100,000× | a80f359c34cd0dab42ea1ecef8ce3f3eebae8b4dfc1e49d95ead8059fea20ca1 |
| outputs/simulation-results.json | Pass 1 (5M rounds) and Pass 2 (11M rounds) | d78d38a7e2e98da89dd0781bfd03dba459049d0ebcf94e1614c9b48afff9d555 |
| outputs/drand-api-verification.json | 1,100 api.drand.sh records, one per round | 6de7a635b429b9412de25999e1501a3ad8209a23cbdd0830ea89656df3c48d1c |
| outputs/rtp-convergence.html | RTP convergence chart, self-contained | ea242a6bf421341beb0096f37edfaa962e5b377cb3090a3600d9cb10380e261b |
Exit Codes4 codes
The exit code is the verdict.
| Exit | Meaning |
|---|---|
| 0 | PROVABLY FAIR — Full Pass, and the run reproduces the committed results |
| 1 | NOT PROVABLY FAIR (at least one hard fail), or a reproduction difference beyond tolerance |
| 2 | PROVABLY FAIR — Conditional Pass (at least one flag) |
| 5 | RTP FIGURE OVERSTATED — the draws pass, but a published RTP figure is above the game's real RTP beyond the ±0.1 pp band |
Reproduction Gateoutputs/run/
npm run verify, npm run simulate and npm run timing write only to outputs/run/; only a deliberate PF_EMIT=1 run rewrites the files of record. A run cannot replace the evidence it scores.
| Rule | Detail |
|---|---|
| Where runs write | outputs/run/ — results, re-simulated artifacts and diff.json |
| What is compared | The run against the committed outputs/verification-results.json, field by field |
| Tolerance | 1e-14 absolute + 1e-12 relative; two different integers never agree |
| Dataset guard | The SHA-256 pin is checked before any step runs and is never rewritten to make a run agree |
| Refreshing evidence | Only deliberately, with PF_EMIT=1, re-pinning the artifact in the same commit |
Release Historyv1.0.0 – v1.2.1
| Release | What changed | Verdict |
|---|---|---|
| Original audit | Published 4 June 2026 (commit f97d5b8) | PROVABLY FAIR — Full Pass |
| v1.0.0 | Tagged 17 September 2026 on 7350abd: the original audit plus pinned artifacts of record; dataset unchanged | Unchanged |
| v1.1.0 | Framework 1.1: 18 scored steps, the RTP claim table, the money model from the wallet ledger | Unchanged |
| v1.2.0 | RNG built from a written specification, with Duel's code kept as a cross-check; Duel's 9,999.999× cash-out cap applied to the RTP table | Unchanged |
| v1.2.1 | Adds .gitattributes so every file clones byte-identical on any platform; no audit content changed | Unchanged |
Repository Structure
duel-crash/
├── README.md · MANIFEST.md        → Results, scope, premises and limitations
├── RELEASE-MANIFEST.json          → Release record: verdict, artifact hashes, signature
├── docs/ALGORITHM.md              → The written specification src/rng.ts is built from
├── src/
│   ├── rng.ts                     → Crash-point derivation and commitment check
│   ├── loader.ts                  → Dataset pin and the population of record
│   ├── simulate.ts · stats.ts     → Two-pass simulation and statistics
│   ├── rtp-claim.ts · rtp-settings.ts → RTP-CLAIM 1.2.0 and the RTP claim table
│   ├── site-verifier.ts · live-site-verifier.ts · operator-verifier.ts
│   │                              → Pin and run both ProvablyFair.org verifiers and Duel's code
│   ├── artifact-pins.ts · domains.ts · diff.ts → Pins, value domains, reproduction diff
│   ├── profile-map.ts             → Crash profile 1.0.3 labels per step
│   └── verify-drand-timing.js     → npm run timing: re-fetch drand signatures
├── tests/
│   ├── verify.ts                  → 18 scored steps and the reproduction gate
│   ├── steps/                     → One module per step group
│   ├── crash/                     → 19 Mocha unit tests
│   └── mutations.json             → Mutation battery (43 entries)
├── data/crash-master-1100rounds.json → 1,100 live rounds (SHA-256 pinned)
├── outputs/                       → Artifacts of record; runs write to outputs/run/
├── evidence/                      → Screenshots, Duel's Verify-tab code, wallet ledger
├── verifier-parity/               → Pinned verifier bytes and runners
├── capture/crash-capture.reference.js → Capture method (reference record)
└── scripts/                       → Mutation runner, verifier re-checks, release manifest
Step-to-Section Cross-Reference18 verification steps mapped
| Step | Test Name | Report Section |
|---|---|---|
| 1 | Seed Hash Integrity | S1, S5 |
| 2 | drand Bet Timing (Bet Before Beacon) | S1, S5 |
| 3 | drand Round Monotonicity | S1, S5 |
| 4 | Server Seed Uniqueness | S1, S5 |
| 5 | Outcome Recomputation | S2, S3, S5 |
| 6 | Bet-Size Invariance | S3, S5 |
| 7 | Payout Math | S3, S4 |
| 8 | House Edge Audit | S4 |
| 9 | Phase Coverage | S3 |
| 10 | Dataset Hash | S7 |
| 11 | drand Chain Formula | S1 |
| 12 | Anti-Circularity | S2, S4, S5 |
| 13 | Simulation Pass 1 | S2, S4, S5 |
| 14 | Simulation Pass 2 (Casino Seeds) | S4, S5 |
| 15 | drand API Signature Verification | S2, S5 |
| 16 | Configuration Coverage (auto-cash-out target) | S2, S4, S5 |
| 17 | Artifact Integrity (pinned artifacts of record) | S7 |
| 18 | Live-Sample Fit (informational) | S2 |
reproduce-audit.sh
# Clone the release (Node 22.x)git clone https://github.com/ProvablyFair-org/duel-crash.gitcd duel-crashgit checkout v1.2.1npm ci # 19 unit tests, then the 18 scored steps (offline)npm test # Optionalnpm run test:full # regenerate the simulation into outputs/run/, then verifynpm run timing # network: re-fetch every drand signature into outputs/run/node scripts/release-manifest.mjs --checkoutputs/run/ and leave the evidence of record untouched; the run is compared with the committed results field by field.Check out v1.2.1 and run npm test: every step re-runs offline and the result is compared with the committed one. The dataset hash pins the 1,100 rounds, and all six files of record are hashed in RELEASE-MANIFEST.json.
Game Profile Coverage
Is every check in the Crash profile accounted for?
The ProvablyFair.org Crash profile 1.0.3 lists 30 checks. Each is covered by a scored step, by a package check, or marked n/a with a reason. Partial means the package states that part of a check is not established; the note says which part.
| Check | What it covers | Covered by | Status |
|---|---|---|---|
| CRASH-01 | Every round's commitment opens | Step 1 | Full |
| CRASH-02 | Seed chain links and folds | n/a: Crash commits one fresh seed per round, so there is no chain | N/A |
| CRASH-03 | One commitment per round, none reused | Step 4 | Full |
| CRASH-04 | Sequence key strictly ordered; constant nonce 0 | Step 3 | Full |
| CRASH-05 | Rounds and phases match the declared plan | Step 9 | Full |
| CRASH-06 | Client seed in the message | n/a: Crash is multiplayer and the message carries no client seed | N/A |
| CRASH-07 | Every served crash point recomputed exactly | Step 5 | Full |
| CRASH-08 | No mapping bias at any cash-out point | Step 16 | Full |
| CRASH-09 | RNG from a written specification; operator code as a cross-check | Package check: docs/ALGORITHM.md, spec self-test, Duel's code run by Step 5 | Full |
| CRASH-10 | Crash-point grid, floor, win rule and instant-crash probability | Steps 5, 7, 12 | Partial |
| CRASH-11 | Settlement rule | Step 7 | Partial |
| CRASH-12 | Stake does not move the outcome or the per-unit return | Step 6 | Full |
| CRASH-13 | Edge source declared; served edge field compared, never used | Step 7 | Full |
| CRASH-14 | Crash-point cap and target bounds | Step 5 | Partial |
| CRASH-15 | Every declared target exercised | Step 16 | Full |
| CRASH-16 | Balance field reconciles | n/a: no round record carries a balance; six wallet legs were looked up separately | N/A |
| CRASH-17 | Beacon timing, order, publication time and source | Steps 2, 3, 11, 15 | Partial |
| CRASH-18 | Anti-circularity with negative controls | Step 12 | Full |
| CRASH-19 | RTP at the claimed edge; RTP claim rule | Steps 8, 16 | Full |
| CRASH-20 | Simulation on pinned seeds, replayed | Step 13 | Full |
| CRASH-21 | Casino-seed cherry-pick screen | Step 14 | Full |
| CRASH-22 | Live-sample fit (informational) | Step 18 | Full |
| CRASH-23 | The package’s standard S5 matrix | Package check: MANIFEST verification results | Full |
| CRASH-24 | Both ProvablyFair.org verifiers, hash-matched and run | Step 5 | Full |
| CRASH-25 | Player verification steps | Package check: MANIFEST "Verify a bet" | Full |
| CRASH-26 | Dataset hash pinned | Step 10 | Full |
| CRASH-27 | Artifacts pinned; value domains declared | Step 17 | Full |
| CRASH-28 | Reproduction: offline run, gate and tolerance | Package check: package.json, tests/verify.ts | Full |
| CRASH-29 | Mutation battery | Package check: tests/mutations.json | Full |
| CRASH-30 | Limitations register and premises | Package check: MANIFEST limitations and evidence | Full |
- CRASH-10 (partial): our capture script stored the served multiplier floored to 2 dp, so the grid half of Step 5 cannot fail on this dataset and does not show what the server sends. The floor, the win rule and P(1.00) are fully covered
- CRASH-11 (partial): Step 7 scores the recorded
amountWonfield, which is not the credit. The credit, the fullstake × target, is witnessed on the 3 wins looked up in the wallet ledger - CRASH-14 (partial): no cap on the crash point is declared or observed, and no served crash point exceeds the map maximum. Duel publishes no minimum or maximum cash-out target to check against; its stated 9,999.999× cash-out cap limits the payout, not the crash point
- CRASH-17 (partial): the capture recorded no receipt time for the commitment, and the bet-before-beacon margin uses Duel's own bet timestamp
21 checks are covered by scored steps, 6 by package checks and 3 are n/a with a reason. Four are partial, each for a reason the package states.